

The devOpsSec Dilemma: Effective Strategies for Social Networking
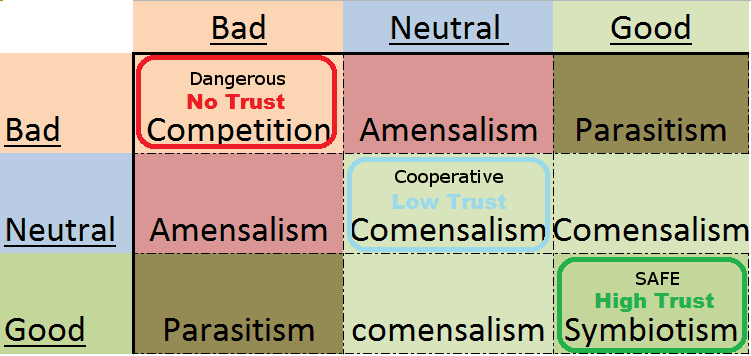
I was sad to hear of the passing of John Nash and his wife Alicia this weekend. May they rest in peace. As a game theorist I am familiar with his work and it just so happens that Nash Equilibriums have been in the center of what I’ve been working with lately. It’s an honor […]
DevOps Connect: Rugged DevOps @Infosecurity Europe
We have assembled another top flight list of speakers for our DevOps Connect event @Infosecurity Europe. While pre-registration is sold out, if you are one of the 15,000+ attendees of Infosecurity Europe, you can still come to DevOps Connect on a first come, first serve basis. Details and schedule are below: When: Thursday 4th June, […]
What is Adaptive Security?
72 days after the fact AdultFriendFinder.com, a “very mature” dating site, realized they had been hacked. The VERY personal information of 3 million registrants has been held hostage. By now, it should be clear that in the modern software development world, old-style static security just won’t work. Of course, there are times when the static security […]
The #1 trick DevOps shops use to reduce vulnerabilities
A new report out this week highlights how important it is to find ways to fold in vulnerability assessment information into the software development lifecycle. Released by WhiteHat Security, the Website Statistics Report 2015 offers a smorgasboard of interesting data around web application security. Amid all of the statistics, though, DevOps shops should perhaps home […]
DevOps Leadership Series: Security at Velocity
If it does not fit, it does not get done. For many DevOps practices, application security falls into the “does not get done” bucket. That’s because for many DevOps-centric organizations, application security has historically been done somewhere else, by someone else, who is slow. Go faster. Shift left. Remove complexity. Reduce rework. All mantras of […]
The DevOps and Security Manifesto
Early in Illumio’s history, I saw the future of DevOps security. The CISO of an electronics manufacturer brought us in to help secure a new support service that was built entirely in the cloud. After meeting with the security team, we were introduced to the application development team who cast a cold eye on our […]
DevOps Leadership Series: Software Supply Chains
We kicked off this series on Monday with Gene Kim (@RealGeneKim) sharing his views on the big theme for DevOps in 2015: proving that DevOps is applicable for large organizations. Another theme that arose often during our recent “DevOps: Wine-ing, Not Whining” event was the importance of software supply chains. Every software development organization has a software […]
It’s time security pros shake their DevOps fear, uncertainly, and doubt
There’s been considerable discussion recently about how to make certain good security practices remain integrated within DevOps-driven environments. To get the scoop from a security pro who is experienced working on delivering security programs in development environments, I turned to Andrew Storms for some insight. Storms has been leading IT, security and compliance teams for […]

Swim in the DevOps pool or drown in security problems
There has been a significant shift recently in security. Most security vendors and organizations recognize that the traditional model of keeping the bad guys out by detecting malicious exploits is flawed at best. The reality is that the bad guys are already inside the network using authorized credentials to bypass security controls and exfiltrate sensitive […]
A True Story: DevOps(Sec) Manages Out Elective Risks
A True Story There are over 2000 developers in Bill’s organization. He is a C-level executive for one of the largest insurance companies in North America. Bill boosted developer productivity by 15% last year after taking a closer look at the company’s software supply chain. And this approach isn’t unique to Bill’s organization. Many high performance IT […]
Welcome to the ADC (After DevOps Connect) era of DevOps and Security
I was speaking with Britta Glade of RSA Conference after our DevOps Connect conference at RSA Conference Monday. She congratulated us on putting together a great day of tracks and sessions (kudos to Gene Kim and Josh Corman). But then she said something else that really struck me to my core. She said after today […]
Illumio Hopes To Cater Security To Continuous Delivery And DevOps Shops
Since coming out of two years of stealth development back in October, the data center security gurus at Illumio have been building momentum in the drive to break out of the confines of the traditional network-centric security model to make it easier to secure IT in the face of distributed computing, continuous delivery and DevOps […]
Live Blogging DevOps Connect @RSAC
We will be live blogging the DevOps Connect: SecDevOps event from RSA Conference on Monday, April 20th. Stay tuned for updates Alan Shimel
DevOps Security Talks At RSA USA 2015 Conference
DevOps and security. Its a muddled mix of waters made even more confusing by the wet ink still on the concept of DevOps. There is no denying the popularity of DevOps and there is a lot of talk on how the DevOps movement functions alongside security teams. The annual USA RSA conference is just around […]
Continuous is the new Black
We have gone from the city that never sleeps to a world that is continuous. That’s right, it seems along with the world shrinking, it is always on, someone is always watching or doing. Continuous has become the new black. Nowhere is this more true than in IT. We have Continuous Delivery, Continuous Integration, Continuous […]
Complete speakers & schedule for DevOps Connect: SecDevOps @RSAC
The line up for DevOps Connect: SecDevOps @ RSAC is complete. What a great job Gene Kim and Josh Corman did lining up a power-packed schedule. Here is what the day is shaping up to be include: 8:50 to 9:00am Alan Shimel and Mark Miller – Opening remarks and welcome 9:00 to 9:50am […]
April is Rugged DevOps Month
Some of you may be aware that we have published a full blown media kit including an editorial calendar for the rest of 2015. For the month of April our focus is Rugged DevOps. It started yesterday with a great post by David Geer, Rugged DevOps: From Idea to Automation to Impact. It will continue all […]
Automated Security Testing in a Continuous Delivery Pipeline
Automated unit, integration and acceptance tests are essential quality controls in running a reliable continuous integration or continuous delivery pipeline. Too often, security tests are left out of this process because of the erroneous belief that security testing is solely the domain of leather-jacket-wearing security experts. Security testing does not need special treatment We’ve made […]
One Secure OS for the Cloud – The Rise of Unikernels
In the last few years, a number of open source projects have started to build interesting new technologies to create faster and more secure and scalable cloud applications. The name: unikernels. The goal: develop a new breed of applications (or port existing ones) for the cloud that significantly improve security, performance and scalability by reducing […]
Rugged DevOps Breakfast @RSAC
In April DevOps.com will highlight the intersection of DevOps and Security. We will be hosting DevOps Connect: SecDevOps @ RSA Conference on Monday, April 20 with Gene Kim, Josh Corman, Jez Humble and others scheduled to speak. We are also releasing the DevOps.com authored EBook, Rugged DevOps. The EBook will look at what role security […]
DevOps Connect: SecDevOps, how to register if you already registered for RSA Conference
Several people have written asking us how to pre-register for the DevOps Connect: SecDevOps conference on the Monday of RSA Week at the Moscone Center. All registrations are handled by RSA. The event is free to anyone who has any RSA badge. So you can go register for an RSA expo pass and still attend […]
Dev and Ops Coming Together To Combat the Weakest Security Link – BYOD
Traditionally, security threats have taken the form of intentional acts by remote attackers: somebody on the outside working covertly to get to the inside. This is the classic scenario that most people associate with IT security, and it’s what most network operators are best prepared for. But these classic threats are eroding rapidly in the […]
First wave of sessions and speakers announced for DevOps Connect: SecDevOps @ RSA Conference
As we previously announced there will be a DevOps Connect: SecDevOps @ RSA Conference this year at the Moscone Center. The event takes place Monday of RSA Conference week at the Moscone Center. The program committee for the event is headed up by Gene Kim and Josh Corman. Gene and Josh will be delivering the […]