

ControlMonkey Extends IaC Automation Reach to Restore Network Services
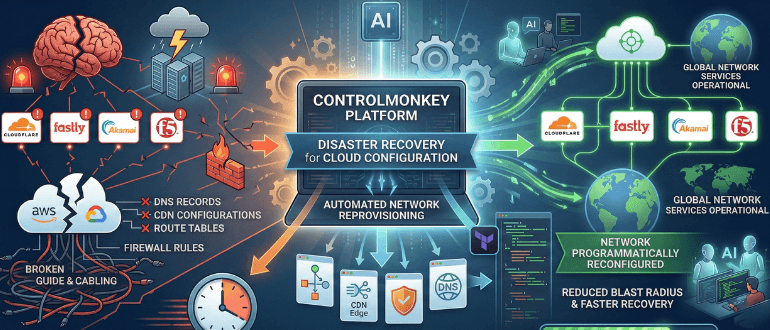
ControlMonkey has extended its platform for automating infrastructure-as-code (IaC) to add an ability to reprovision network services following a disruption in service. Company CEO Aharon Twizer said this extension to the Cloud Configuration Disaster Recovery platform, which the company launched last year, makes it possible to use Terraform code to programmatically reconfigure networking services among others […]
I Learned Traffic Optimization Before I Learned Cloud Computing. It Turns Out the Lessons Were the Same.
I wanted to be a race car driver before I knew what a data center was. I started in traffic, not in the cloud. This was not a childhood dream driven by glamour. It was more practical than that. I grew up in India, and I was always late for school. Not entirely my fault. […]
The Future of AI in Software Quality: How Autonomous Platforms are Transforming DevOps
Agentic AI is transforming DevOps by embedding autonomous quality checks into CI/CD pipelines, improving code security, coverage and speed.
How OPA Changed Our Go-No-Go Forever
Learn how Open Policy Agent (OPA) transformed go/no-go releases from subjective meetings into automated, auditable, policy-driven decisions embedded directly in the CI/CD pipeline.
The Great Infrastructure Migration: Why Teams are Moving From Manual Provisioning to Autonomous Platforms
Autonomous infrastructure platforms replace manual provisioning, accelerating delivery, improving compliance and freeing platform teams to focus on strategic work.
Test Automation Strategy for Growing Software Teams
Build a scalable test automation strategy that improves release speed, reduces defects, and supports growing software teams.
Secrets Management Failures in CI/CD Pipelines
Explore the critical role of secrets management in CI/CD pipelines and its impact on cybersecurity. This article highlights the risks of credential exposure, the importance of implementing strong security practices, and how organizations can ensure robust defenses against breaches and supply chain attacks.
Secure DevOps at Scale: Integrating SRE, DevSecOps and Compliance
Enterprises developing SaaS products face the challenge of balancing innovation, security, and compliance. By adopting Secure DevOps practices—integrating security into every stage of development—and implementing site reliability engineering (SRE), organizations can enhance agility while ensuring resilience and adherence to regulatory standards. Automating compliance within DevOps pipelines allows teams to maintain high-speed execution without compromising security, creating a robust framework for scalable and secure cloud-native applications.
Veracode Extends Package Firewall Reach to Microsoft Artifacts
Veracode has extended the reach of a Package Firewall that applies policies that limit what types of code can be downloaded from a repository to Azure Artifacts from Microsoft. Additionally, DevSecOps teams can now define custom policies based on package risk profiles, vulnerability thresholds, or a specific security requirement their organization has adopted. Tim Jarrett, […]
Why Data Contracts Need Apache Kafka and Apache Flink
Data contracts prevent breaking schema changes in data pipelines. Learn how Kafka and Flink help specify, implement and enforce them.

The Problem’s Not Your Monitoring Tools, It’s Your Workflow
The real cost of poor observability isn’t just downtime; it’s lost trust, wasted engineering hours, and the strain of constant firefighting. But most teams are still working across fragmented monitoring tools, juggling endless alerts, dashboards, and escalation systems that barely talk to one another, which acts like chaos disguised as control. The result is alert […]
‘PackageGate’ Vulnerabilities Can Let Attackers Bypass Shai-Hulud Defenses
In the wake of the massive Shai-Hulud supply chain attack that ripped through npm late last year and compromised more than 700 packages and exposed 25,000 repositories, developers in the JavaScript world embraced a two-part defense strategy. The widely adopted playbook called for disabling lifecycle scripts and using lockfiles. “It became the standard advice everywhere […]
Harness Adds AI Agent to Help Investigate Incidents
Harness today added an artificial intelligence (AI) agent to its portfolio that has been specifically trained to help DevOps teams investigate events that occurred prior to an incident. Tina Huang, vice president of product and engineering for AI SRE at Harness, said the Harness Human-Aware Change Agent leverages large language models (LLMs) to analyze comments […]
Snowflake Plans $1B Acquisition of Observe to Expand AI-Powered Observability
Snowflake has signed an agreement to acquire observability startup Observe, moving to fold AI-driven telemetry analysis directly into its AI Data Cloud as enterprises grapple with the operational complexity created by large-scale AI systems. Financial terms were not disclosed, though multiple reports estimate the transaction at roughly $1 billion, which would make it the largest […]
Survey Sees Growing Interest in Switching Observability Platforms
A survey of 100 VP+ IT decision-makers published today finds 62% plan to increase spending on observability initiatives over the next 12 to 24 months, with only 4% planning to decrease spending. Conducted by LogicMonitor, a provider of a monitoring and observability platform, the survey also finds more than two-thirds (67%) are very likely or […]
7 Cybersecurity Tips for 2026 No One Will Tell You About
Nothing about 2026 feels stable anymore, especially in security. Attacks move faster than your monitoring stack, AI tools leak data behind your back and everyday convenience apps quietly turn into intrusion points. The biggest threats aren’t the ones trending in conference talks but the subtle, boring habits that have crept into your workflow without anyone noticing. Once you start paying […]
Best of 2025: How AI Agents are Reshaping the Developer Experience
AI agents are helping to shift developers’ focus from long hours of manual coding to high-value problem-solving, architecture and decision-making processes.
Best of 2025: GitLab Extends Scope and Reach of Core CI/CD Platform
GitLab Inc. has updated its core continuous integration/continuous delivery (CI/CD) platform to natively provide more artificial intelligence (AI) capabilities, along with built-in software artifact management capabilities and more robust security tools.
Best of 2025: CloudBees Moves to Unify Management of Multiple DevOps Platforms
CloudBees today launched a software-as-a-service (SaaS) platform for centralizing the management of multiple DevOps environments, including GitHub, GitLab and the open source Jenkins continuous integration/continuous delivery (CI/CD) platforms.
Best of 2025: GitHub Action Compromise Risks Data Leaks for 23,000 Repositories
The attacker introduced malicious Python code that would expose secrets like authentication credentials in public repositories.
Best of 2025: Integrating Generative AI Into DevOps Pipelines
Generative AI, a subset of AI, is a new technology that can create content in different forms, such as text, images and videos. Integrating generative AI into DevOps practices can benefit an organization’s business processes. This article addresses the advantages, obstacles and opportunities concerning blending and integrating generative AI with DevOps. Understanding the Problem Organizations […]
Best of 2025: The DevOps Bottleneck: Why IaC Orchestration is the Missing Piece
If you work in DevOps, you’ve heard it a thousand times: “Do more with less.” More automation, more security, more reliability—but with the same (or fewer) people. Meanwhile, your development teams keep growing, pushing out new features at breakneck speed. Yet somehow, the infrastructure team is supposed to scale magically to keep up. Let’s be […]
Best of 2025: Survey: AI Tools are Increasing Amount of Bad Code Needing to be Fixed
Survey findings include respondents noted that AI tools are increasing the blast radius of the amount of bad code that needs to be debugged.