

When AI Goes Really, Really Wrong: How PocketOS Lost All Its Data
You can’t make this crap up. You just wish you could. Jer Crane, founder of the small vertical software company, PocketOS, reported on X that the AI Cursor coding agent and a Railway backup misconfiguration combined to briefly wipe out the company’s car‑rental customer production data. Not some of the data. All of it. That’s […]
Sophisticated Supply Chain Attack Targeting Trivy Expands to Checkmarx, LiteLLM
The supply chain attack that compromised Aqua Security’s Trivy open source security vulnerability scanner and its associated GitHub Actions earlier this month continues to expand, with software development tools from Checkmarx and LiteLLM being the latest victims of the sophisticated campaign. The threat group behind it, TeamPCP, is using the attacks to create persistence and […]
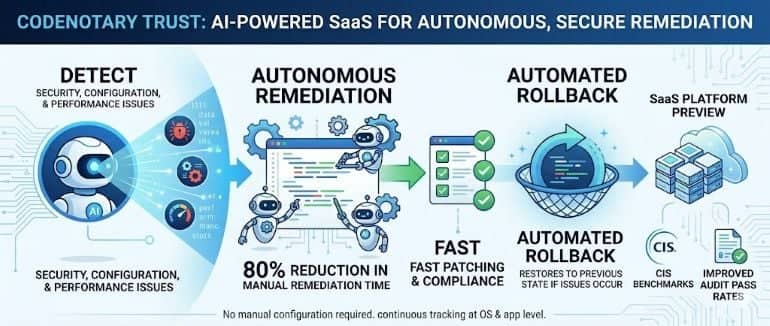
Codenotary Previews AI Platform to Autonomously Detect and Remediate IT Issues
Codenotary is previewing a software-as–a-service (SaaS) platform that enables artificial intelligence (AI) agents it has developed to autonomously detect, prioritize, and fix security, configuration, and performance issues. Company CEO Moshe Bar said the Codenotary Trust platform also enables continuous vulnerability tracking at both the Linux operating system and application level. Once an issue is detected, […]
N. Korean Famous Chollima Hackers Use Malicious npm Packages to Steal Data
A group of more than two dozen malicious npm packages used to steal secrets and credentials from software developers has all the hallmarks – from infrastructure to operations – of Famous Chollima, the North Korean nation-state actor linked to the ongoing high-profile Contagious Interview scam. Threat researchers with Socket and Kieran Miyamoto of the DPRK […]
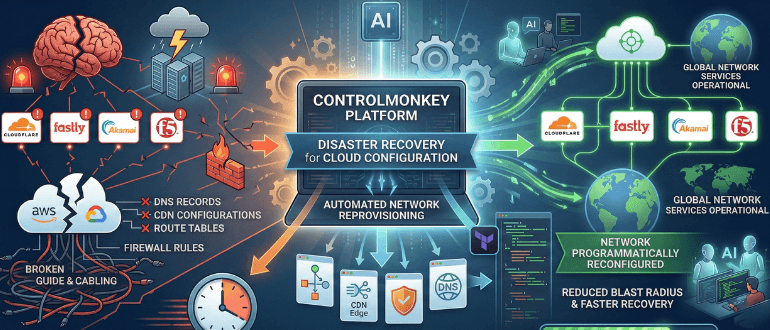
ControlMonkey Extends IaC Automation Reach to Restore Network Services
ControlMonkey has extended its platform for automating infrastructure-as-code (IaC) to add an ability to reprovision network services following a disruption in service. Company CEO Aharon Twizer said this extension to the Cloud Configuration Disaster Recovery platform, which the company launched last year, makes it possible to use Terraform code to programmatically reconfigure networking services among others […]
‘PackageGate’ Vulnerabilities Can Let Attackers Bypass Shai-Hulud Defenses
In the wake of the massive Shai-Hulud supply chain attack that ripped through npm late last year and compromised more than 700 packages and exposed 25,000 repositories, developers in the JavaScript world embraced a two-part defense strategy. The widely adopted playbook called for disabling lifecycle scripts and using lockfiles. “It became the standard advice everywhere […]
From Reactive to Predictive: Capacity Planning Systems That Actually Work
I used to think capacity planning was about setting up CloudWatch alarms and hoping they’d fire before things broke. Spoiler: that’s not capacity planning—that’s just reactive firefighting with extra steps. Real capacity planning means knowing you’ll need more database capacity three weeks from now, not three minutes after your site starts timing out. It means […]
Attackers Testing New Strain of Shai-Hulud on npm: Aikido
Threat actors behind the virulent Shai-Hulud worm that wreaked havoc in open npm repositories toward the end of 2025 apparently are trying out a new strain that comes with slight modifications. Security researchers with Aikido Security, who have been tracking Shai-Hulud for months, wrote in a report that was updated January 2 that there doesn’t […]
Observability, SRE and Uptime in Telehealth Platforms: A DevOps Playbook
Virtual care went from nice to have to must have during the COVID-19 pandemic and while in-person visits are starting to pick up again, telemedicine is here to stay. Its growth will continue: health-tech companies are predicting the telemedicine market will be $143.49 billion by 2025 (it will be $167.74 billion in 2025 and $584.99 […]
Crates.io Removes Malicious Rust Package Targeting Web3 Developers
A malicious Rust package that was found to be downloading payloads aimed at stealing cryptocurrency was removed from the crates.io Rust package registry, along with another package by the same author that appeared benign but was dependent on the first. The crates.io team removed both packages this week after security researchers with Socket alerted it […]
System Initiative Extends Reach of IT Infrastructure Automation Platform
System Initiative today revealed it is now extending the reach of its digital twin platform for automating the management of IT infrastructure to any cloud computing environment, including now out-of-the-box support for Microsoft Azure, Digital Ocean and Hetzner services, along with existing support for Amazon Web Services (AWS). Nick Stinemates, vice president of business development […]
Massive VS Code Secrets Leak Puts Focus on Extensions, AI: Wiz
Researchers with cybersecurity firm Wiz earlier this year discovered, almost by chance, a significant supply chain risk and massive secrets leak in the Visual Studio Code and OpenVSX marketplaces that they said put a focus on the ongoing security issues presented by extensions and plugins. In their months-long investigation with Microsoft, the researchers found that […]
The Leadership Mindset for Sustainable DevOps Cost Optimization
From seeing costs as an external burden imposed by finance to recognizing them as an integral signal of engineering health.
Spacelift Adds On-Premises Edition of Infrastructure Management Platform
Spacelift has made available an on-premises edition of a platform for automating the provisioning and management of IT infrastructure that previously was only accessible via a software-as-a-service application. Company CEO Pawel Hytry said the on-premises edition of the platform satisfies both the requirements of highly regulated industries and the emergence of sovereign cloud requirements that […]
Typosquat Supply Chain Attack Targets Go Developers
A backdoor that impersonates a widely used database module in the popular Go programming language can give hackers control of infected systems, according to a senior threat intelligence analyst with developer-focused platform provider Socket. The malicious package, which the threat actor first published in November 2021 and remains in the Go Module Proxy, typosquats the […]
CISA Pushes Steps to Better Secure Software and Product Designs
The country’s top cybersecurity agency is urging developers to take steps to ensure the software they’re building and the products they roll out are secure and protect end users. The Cybersecurity and Infrastructure Security Agency (CISA) this week rolled out a series of recommendations that it wants businesses and critical infrastructure organizations to adopt to […]
Operations as Code: Transforming Operational Excellence
The push toward digital transformation and cloud-native infrastructure is inevitable. This shift brings the need to manage operations with the same rigor and automation we apply to infrastructure or security. Many organizations have embraced the ideas of everything in a pipeline and all things as code. While platform engineering and other teams have created answers […]
AWS Cloud Migration Strategy
Migrating your project means moving your data from the on-premises data center to the cloud. Migration is a big task and AWS facilitates migration in phases.
CISA: Critical Jenkins Flaw Exploited in Ransomware Attacks
The security vulnerability in the popular open-source development tool helps threat actors gain initial access into victims’ systems.
White House to Spend $11 Million to Study Open Source Software Use
Hardening the security around open source software has been a key part of the White House’s larger cybersecurity efforts since President Biden released his executive order for improving the United States’ security posture in May 2021, only months after taking office. Now the Biden Administration and the Department of Homeland Security (DHS) are putting $11 […]
ZEST Security Brings Generative AI to Cloud Infrastructure Security
ZEST Security has launched a platform that leverages generative artificial intelligence (AI) to remediate code created using infrastructure-as-code (IaC) tools.
Quali Bakes Generative AI into Environment as Code Platform
Quali has added a generative artificial intelligence (AI) capability to its Torque platform for managing infrastructure-as-code that enables DevOps teams to use natural language to describe a template, that is then automatically created and implemented.
Scaling with Terraform: How to Manage Infrastructure at Scale
These key points can help you effectively manage Terraform infrastructure at scale, ensuring your systems are resilient, scalable and compliant with organizational policies and industry standards.