

RIP CentOS. Hello AlmaLinux Rocky Linux, CentOS Stream or RHEL
CentOS 7’s official end of life is June 30th. What should a DevOps team do? We help you consider your choices.
AlmaLinux Introduces Engineering Steering Committee to Enhance Community Collaboration
AlmaLinux is keeping its Linux community in the technology loop.
Defining DevSecOps for IoT
By embedding security practices at every stage of the IoT development lifecycle, from design through deployment, organizations can significantly enhance the security and integrity of their IoT ecosystems.
Security, Automation and Developer Experience: The Top DevOps Trends of 2024
If you want to know what’s truly changing in the world of DevOps – as opposed to which conversations are most hype-worthy – these are the places to look.
Does More Money Improve Open Source Security?
It sounds simple: If you pay developers more money they’ll improve the quality and security of their code. The evidence isn’t so clear.
Mind the Shift: Answering Common Questions About OpenTofu
A lead contributor to OpenTofu answers the (truly) frequently asked questions about the open source project.
OpenSSF warns of Open Source Social Engineering Threats
Linux dodged a bullet. If the XZ exploit had gone undiscovered for only a few more weeks, millions of Linux systems would have been compromised with a backdoor. We were lucky. But can we stay lucky? The Open Source Security Foundation (OpenSF) and the OpenJS Foundation revealed that a similar hackling attempt had targeted several […]
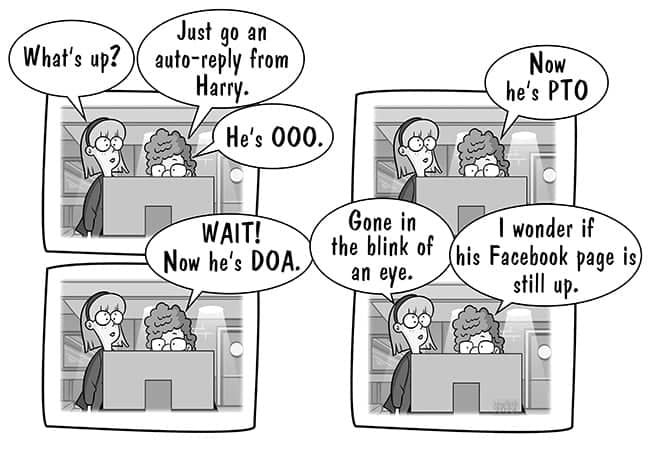
Auto Reply
We’re going to send email messages that say, “Hope this finds you in a well” and see if anybody notices.
Tools for Sustainability in Cloud Computing
You’re probably sold on the environmental benefits of moving to the cloud. These tools can help you get there faster by measuring your applications’ carbon emissions.
Securing Open Source Software, the Cyber Resilience Act Way
The Eclipse Foundation is spearheading an effort to create a unified framework for secure software development.

Grafana Labs Makes Observability More Accessible
The updates promise to make it easier to invoke the capabilities of a Grafana Cloud platform based on open source software.
Your AI Might be Lying to You
Simple tests can demonstrate whether a code generator is actually doing what you ask.
Modern Application Management Requires Deeper Internet Visibility
Most IT teams regularly employ a range of tools to monitor application performance. But in an era where applications are running everywhere from the cloud to the network edge, the visibility being provided is limited. The metrics and analysis being surfaced are roughly akin to only being able to see a few yards ahead when […]
Bringing DevOps Automation to Legacy Systems
A critical step toward adopting automation for legacy applications is to change your organization’s mindset about legacy systems.
Survey Sees AI Playing Larger Role in Test Automation
A Tricentis survey found organizations could see massive costs savings by fully automating mobile application testing.
Time to Extend DevOps Visibility to the Network Edge
Any comprehensive approach to observability needs to include an analysis of the internet services upon which organizations depend.
Edge Computing Requires DevOps at Scale
The rise of edge computing will drive a long-overdue convergence of DevOps, data engineering, security, networking, OT and MLOps best practices.
Controlling Cloud Costs With Efficient Ramp Plans
Ramp plans are becoming a vital tool for containing cloud resources as companies try to control cloud sprawl and spending.
The IaC Weight on DevOps’ Shoulders
It’s often challenging to adopt modern DevOps practices around infrastructure-as-code (IaC). Here’s how to make the journey smoother.
Leveraging eBPF for DevSecOps
The applications for enhancing security observability with eBPF are vast, and it’s increasingly valuable for DevSecOps use cases.
appCD Launches Platform to Securely Provision Cloud Infrastructure
appCD’s platform analyzes an application about to be deployed and automatically generates the code to provision the required infrastructure.
Permiso Makes Open Source Tool to Identify Cloud Threats Available
Permiso today launched an open source tool dubbed CloudGrappler that surfaces indicators of compromise in cloud computing environments.
AISecOps: Expanding DevSecOps to Secure AI and ML
AISecOps, the application of DevSecOps principles to AI/ML and generative AI, means integrating security into models’ life cycles.