

Waterfall 2.0: Controlling LLM-Driven Software Development with Stage-Gated Discipline
Waterfall 2.0 reimagines classic stage-gated software development for the LLM era, combining fast AI generation with structured validation, cheap backtracking and a shared knowledge corpus.
Why API Test Generation Is a Judgment Problem, Not a Code Generation Problem
When we started using large language models for API test generation at KushoAI, the results were impressive on the surface. Tests appeared in seconds. Coverage breadth went up. The team was excited. Then we looked more carefully at what was being produced. On one endpoint, the model generated 26 tests where a senior QA engineer […]
Why Cryptographic Inventory Is the First Step Toward Quantum Readiness
Post-quantum readiness starts with visibility. DevOps teams need a continuous cryptographic inventory to map algorithms, keys, certificates, libraries, infrastructure and third-party dependencies before PQC migration begins.
npm v12 Shuts Down a Popular Malware Trick — But the Threat Isn’t Going Away
For years, one of the easiest ways to sneak malware onto a developer’s machine has been to hide in plain sight. Install a package from npm, and any lifecycle script bundled with it runs automatically — no review, no approval, no second look. Attackers have known this for a long time, and they’ve used it […]
AI Agents Are Writing Code Faster Than Anyone Can Review It. Tessl Is Betting On Standards To Close That Gap
Every team that has turned coding agents loose on real work has run into the same wall. The agents write fast. They write a lot. And somewhere between the tenth and twentieth pull request of the day, the humans responsible for reviewing that code start falling behind. That’s not a hypothetical. It’s the operating reality […]
Critical Flaw in isolated-vm Can Lead to Sandbox Escape, RCE Threat
Developers for years have been using vm2, an open-source Node.js library, to run untrusted JavaScript inside a secure and isolated sandbox environment. It uses Node.js’s built-in modules and JavaScript Proxies and lets developers whitelist particular built-in Node modules or limit what the script can access. During that time, vm2 has been the default for safely […]
UiPath Test Cloud: Robots Handle Repetition, Agents Adapt and Humans Lead
Most companies don’t actually struggle to ship software anymore. AI made that part fast. What they struggle with is releasing what they built with any real confidence in it. That gap between shipping fast and trusting what you shipped is what I’ve been calling quality debt at conferences all year, and it’s the same gap […]
GitHub Sharpens CodeQL’s Eye on Actions Workflows and Modern JavaScript
GitHub Actions pipelines have become one of the quieter attack surfaces in software development. They pull in third-party actions, cache dependencies, and pass secrets between jobs, often without anyone reviewing the workflow file as closely as they’d review application code. That gap is exactly where cache-poisoning and output-clobbering attacks live, and it’s why GitHub keeps […]
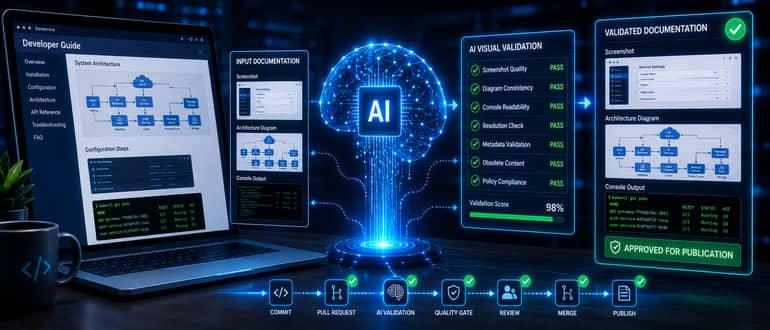
Elevating Technical Documentation: Using Predictive AI to Standardize Visual Knowledge Bases
Every release changes documentation alongside the code. Developers depend on that documentation during implementation, maintenance and troubleshooting. A diagram becomes misleading once services are renamed or integrations change without a corresponding documentation update. Keeping documentation updated becomes increasingly difficult as repositories, products and release cycles grow. Outdated or inconsistent images eventually find their way into […]
How to Avoid Repeating the “Automate Everything” Mistake Due to AI FOMO
The DevOps community has already experienced technological extremes. You might recall the time when automation was thought of as a panacea for all possible engineering issues, and the slogan “Automate Everything” was ringing out everywhere. Over time, the industry came to an important conclusion: Automation should not become the end goal. Along with faster software […]
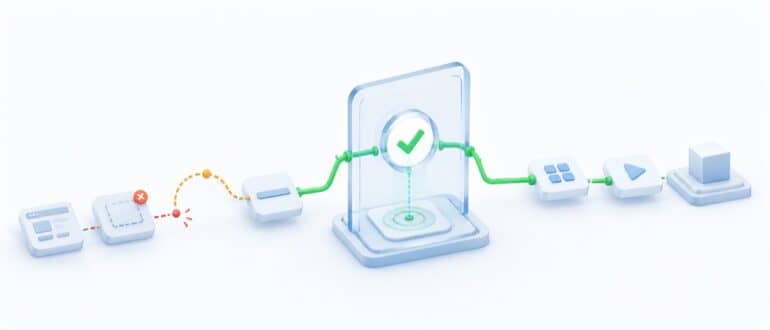
Why Self-Healing Tests Need a Deployment Gate
When an end-to-end test fails after a front-end change, the repair often looks routine. A class name changed. A button moved. A selector that used to be unique now matches two elements. A self-healing system inspects the page, proposes a new locator, reruns the test, and gets a green result. That green result is useful, […]
Cursor Launches Origin Code Hosting Platform as GitHub Rival
AI coding provider Cursor has launched Origin, a code hosting platform that puts source code and AI coding agents inside the Cursor development environment. The new coding platform expands the company into a market long dominated by GitHub. The rollout arrived as GitHub suffered a major outage lasting more than six hours, disrupting pull requests, […]
LangChain’s dcode Isn’t New. Its Governance Play for Sensitive Code Is
Enterprises are running into the same wall with AI coding agents: the tools that write code fastest are usually the ones IT trusts least with sensitive codebases. Legacy modernization projects — COBOL migrations, .NET upgrades, decade-old frameworks nobody wants to touch by hand — are exactly where agentic coding tools could help most, and exactly […]
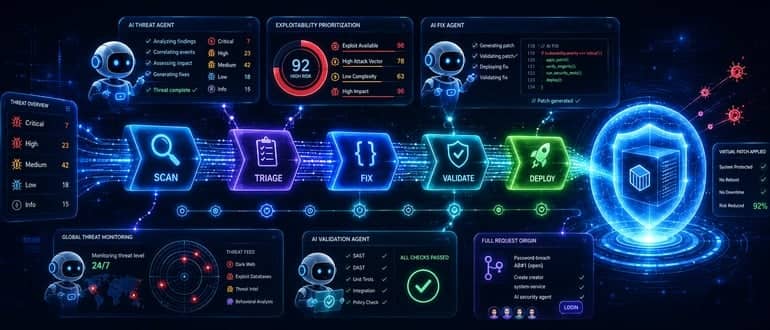
Harness Adds AI Agents to Automate DevSecOps Workflows at Machine Speed
Harness today added multiple artificial intelligence (AI) agents and a virtual patching capability to its portfolio to automate DevSecOps workflows at a time when the number of vulnerabilities being discovered in code continues to exponentially increase. The AI agents include one that has been added to the static application security testing (SAST) tool that Harness […]
Claude Code’s Temporary Usage Boost Expires Tonight. Here’s What Actually Changes
Anthropic’s temporary 50% increase to Claude Code weekly usage limits expires August 19, reducing available capacity for developers and DevOps teams without lowering subscription prices.
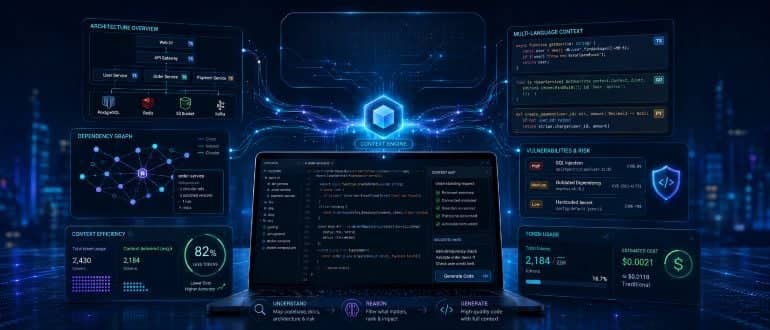
Adronite Unveils AI Coding Tool Based on Embedded Context Engine
Adronite launches Codistry, an AI coding tool that uses a context engine to map codebases, reduce token usage and generate more production-ready code.
Are LLMs Equally Good (or Bad) at Building Secure Software?
An SCW study finds a large variance in how frontier and budget LLMs perform across different frameworks, and explains the striking cost variance.
What the Microservices Era Can Teach Us About AI
AI agents are not just microservices with LLMs attached. Their long-running, non-deterministic workflows demand durable execution, per-step identity, governance and observability.
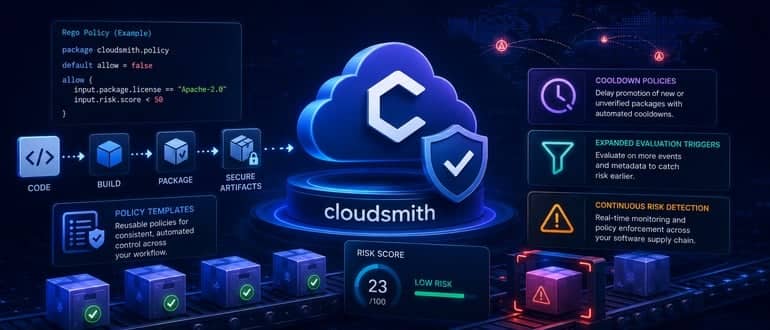
Cloudsmith Extends Policies and Controls to Secure Application Binaries
Cloudsmith this week revealed it has expanded the policy management and continuous risk detection capabilities it makes available within its software artifact management platform to now include policy templates, cooldown policies, and expanded evaluation triggers. Alison Sickelka, vice president of product for Cloudsmith, said these additions to the platform will make it simpler to prevent […]
Deterministic Robots, Agentic Reasoning: Balancing Reliability and Flexibility in Software Test Automation
Summary: Scott Robohn explores how UiPath Test Cloud mitigates the “release gap” caused by rapid, AI-driven development by offering a platform that blends a combination of deterministic automation, AI agents, and human oversight. By distinguishing between deterministic “robots” for efficient, cost-effective regression and flexible “agents” for complex reasoning, the platform empowers quality engineers to use […]
Microsoft’s GitHub Hit by Major Outage as AI-Driven Demand Strains Infrastructure
GitHub, the Microsoft Corp.-owned code hosting platform serving more than 180 million developers, is still reeling from a widespread outage on Monday that severely disrupted software development pipelines globally. The hours-long incident was the latest in a relentless series of reliability failures for a service struggling to keep pace with an unprecedented surge in artificial […]
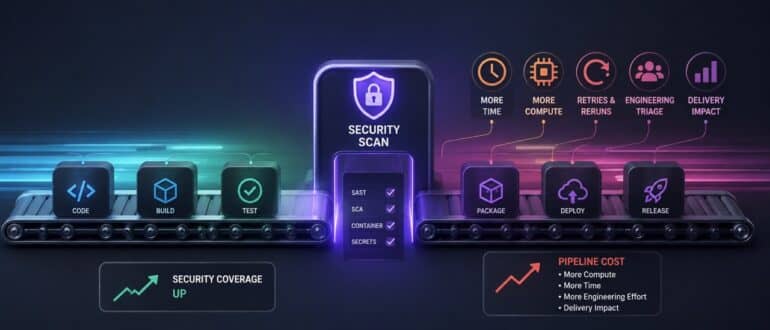
Is Your New DevSecOps Tooling Reducing Work Or Just Adding to It?
Security belongs in the software delivery pipeline. The harder question is where, how often and at what cost. Many pipeline teams eventually add security scanning to CI/CD, and relatively few go back afterward to measure what it actually cost the delivery process. Security coverage went up. Something else changed too, and it is rarely measured […]
GitHub Hit by Widespread Outage, Halting Work for Global Developers
A major technical outage struck GitHub on Monday morning, disrupting workflows for millions of developers worldwide for several hours as critical services, automated testing pipelines, and artificial intelligence (AI) coding tools suffered high error rates. The hosting platform — a subsidiary of Microsoft Corp. that supports roughly 180 million users — first reported performance issues […]