

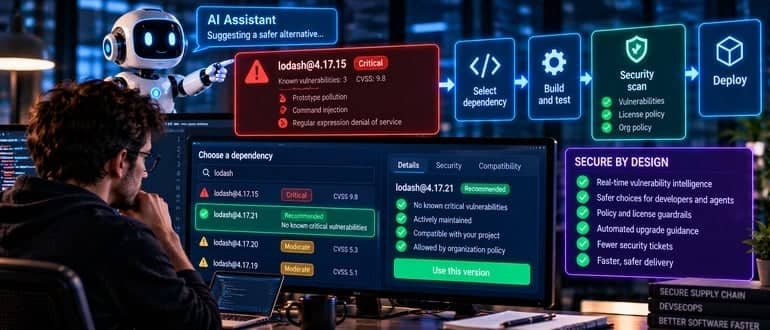
Security Teams Are Fixing Vulnerabilities Faster Than Ever. So Why Is Software Getting Riskier?
AI is speeding up dependency decisions, making point-of-selection security essential for reducing vulnerable components, downstream tickets and avoidable rework.
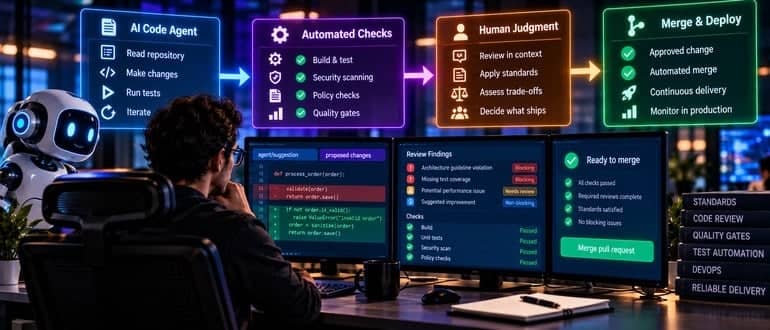
Taste, Discernment, and Judgment Have Become Must-Have Engineering Skills
AI coding agents make code generation cheap, shifting engineering value toward standards, deterministic quality gates, contextual review and human judgment about what should ship.
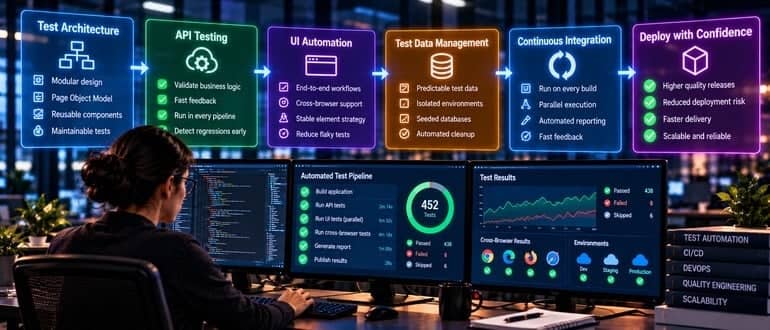
QA Automation Frameworks for Enterprise Applications
Modern enterprise applications demand testing strategies that can keep pace with continuous delivery, distributed architectures, and increasingly complex deployment pipelines. Traditional manual testing approaches often become a bottleneck as engineering teams scale their applications and release software more frequently. This article explores the essential building blocks of an enterprise-grade QA automation framework, focusing on maintainability, […]
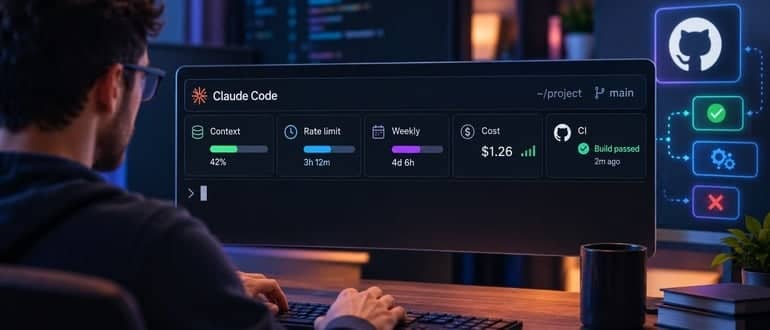
Open Source Mod Brings Rate Limits, Costs and CI Status Into View for Claude Code Users
Claude Statuspane gives developers real-time visibility into Claude Code context use, rate limits, costs and CI status, highlighting a growing need for agent observability.
DevOps Dozen 2026 Nominations Are Open: Recognizing the People and Technology Moving DevOps Forward
When we launched the DevOps Dozen in 2015, we wanted to recognize the people, projects and companies helping this community move forward. We saw the work happening across DevOps every day at DevOps.com. The awards gave our readers a chance to tell us who deserved recognition. Eleven years later, there is a lot more ground […]
Survey Surfaces Sharp Increase in Amount of Code Written by AI
A global survey of 705 developers and IT leaders finds 42% of respondents reporting that artificial intelligence (AI) now writes at least half their code, with only 21% of developers now spending more than half their week writing new code from scratch. Conducted by BairesDev, a provider of software development services, the survey also finds […]
Git 2.56 Takes Aim at Messy Merges, Slow Diffs and Branch Sprawl
Git 2.56 improves merge safety, speeds up large-repository operations and adds cleanup tools that could prove especially useful for AI coding agents and busy DevOps teams.
Leaked GitLab Email Tokens Can Reach Code, Secrets and CI/CD Pipelines
Security researchers have uncovered a GitLab behavior that could let attackers use a leaked project email address to push code, trigger CI/CD jobs and reach other repositories accessible to the address owner. Aikido Security researcher Joe Leon detailed the attack path this week in a blog post after reporting it to GitLab earlier this year. […]
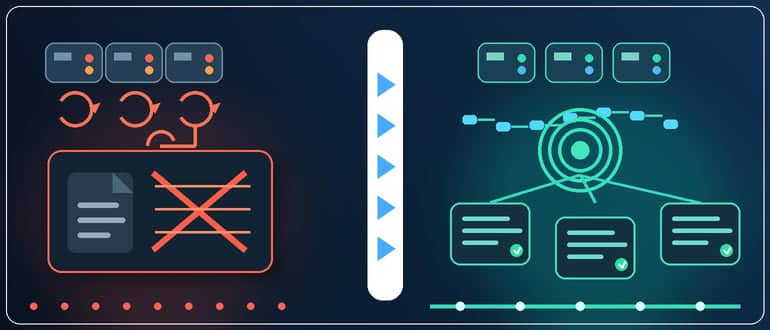
Dependency Mocking Approach That Gets More Accurate as Your Services Deploy More Often
Traffic-based dependency mocking turns frequent upstream deployments into opportunities to refresh mocks from real behavior and reduce integration test drift.
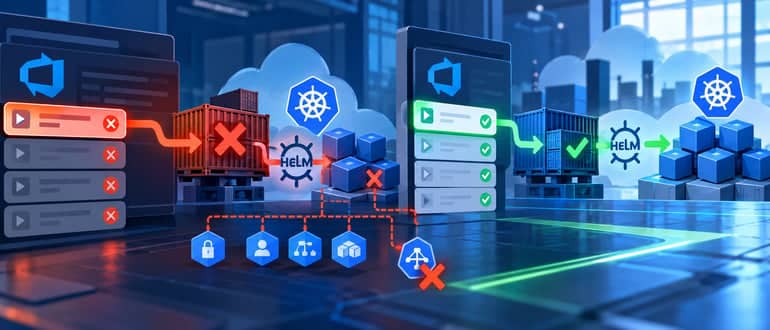
Why Old Azure DevOps Releases Survive a Pipeline Cutover
Old Azure DevOps Classic releases can retain retired deployment tasks, Helm names, image paths and variables long after a pipeline cutover, leaving stale redeploy paths active.
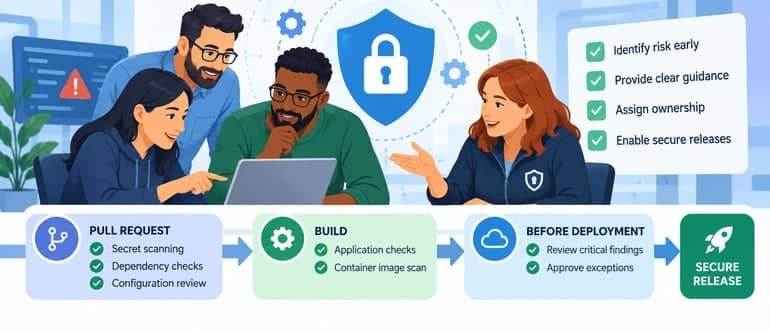
DevSecOps Teams as Partners in Secure Software Delivery
DevSecOps teams can reduce last-minute release delays by shifting security decisions earlier, improving guardrails, clarifying ownership and making findings actionable.
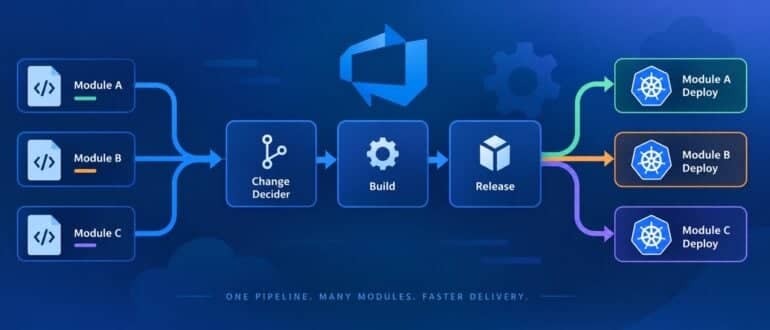
How I Consolidated Duplicate Delivery Pipelines With Parameters and Build Tags
Two modules in a repository had near-identical Azure DevOps build and release definitions. A third would have required another pair. The delivery chain used five definitions: one change decider, two builds, and two releases. I consolidated it into one decider, one generic build, and one release with a deployment stage for each onboarded module. The […]
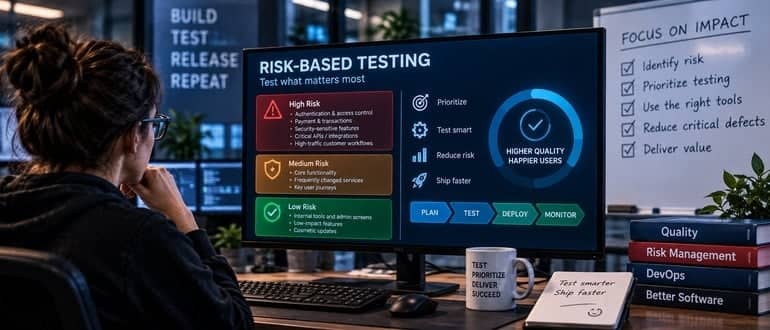
Stop Chasing 100% Test Coverage: Why DevOps Teams Need to Test Smarter, Not More
Every software team eventually runs into the same question: How much testing is enough? For years, the default answer has been “more.” More automated tests. More regression suites. More environments. More devices. But as applications become more complex and release cycles continue to accelerate, testing everything simply isn’t realistic, even with the support of AI. […]
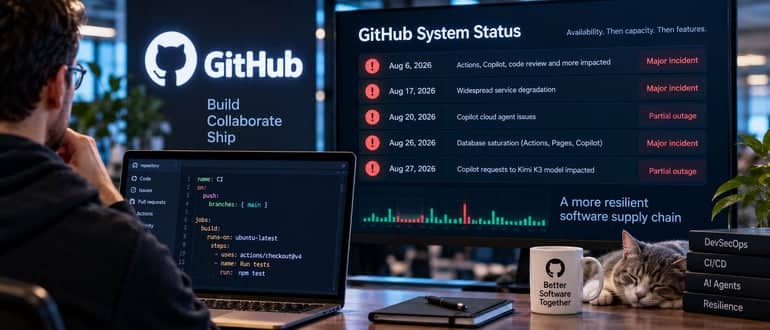
GitHub’s August Outages Show Growth Is Outpacing Infrastructure
GitHub’s August 2026 report details five outages tied to Actions and Copilot growth outpacing infrastructure. Here’s what platform teams should know.
GitHub Workflows Strain Under AI Agent Development
Coder CEO Rob Whiteley joins Mike Vizard to explain why GitHub workflows, CI/CD pipelines and developer platforms are showing strain under agentic development — and what a policy-aware redesign of the DevOps stack should look like.
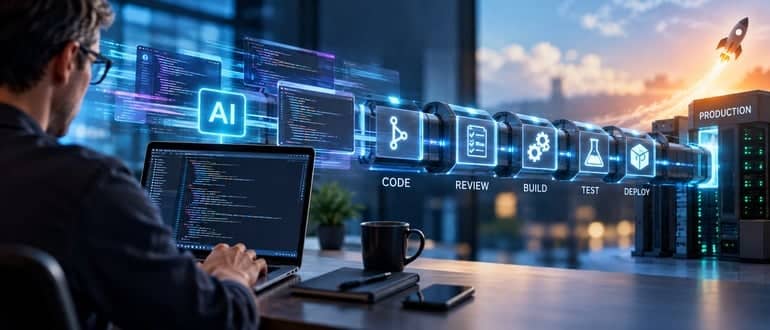
AI Has Turned Verification Into the New DevOps Bottleneck
The next DevOps challenge is not generating more software. It is proving, quickly and repeatedly, that a growing volume of machine-generated change is fit to ship.
Your DevOps Pipeline Is Already a Sustainability Program
During my doctoral research on modern engineering practices and operational efficiency, one pattern kept surfacing that I did not expect to find. The engineering teams making the most measurable progress on sustainability were not the ones that had appointed green committees. They were the ones running tight DevOps discipline: right-sized fleets, lean pipelines, tuned alerting, […]
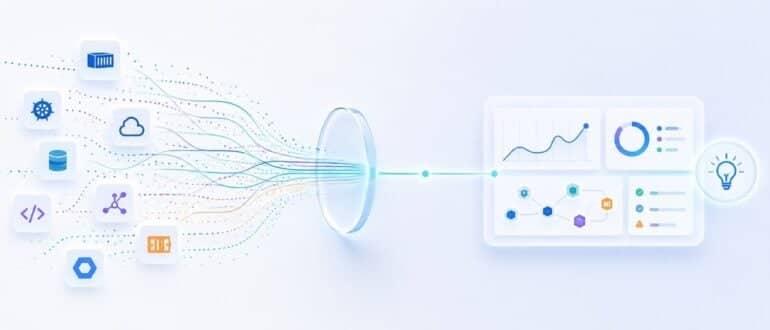
Observability 2.0: Why DevOps Teams Are Moving From Monitoring to Intelligent System Understanding
For a long time, monitoring just meant staring at dashboards and waiting for something to flash red. Engineers tracked things like CPU usage, memory, response times, error rates, and uptime. If a number crossed a certain line, you’d get an alert. Then, someone dived in to figure out what was wrong. That basic approach isn’t […]
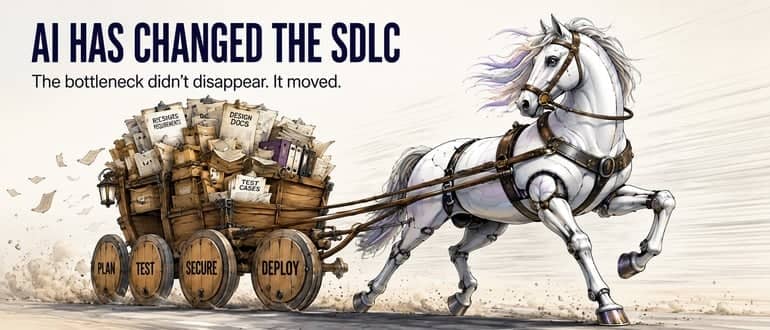
From the Horse’s Mouth: Anthropic Says AI Has Changed the SDLC
Anthropic’s AI-native SDLC playbook argues that faster coding is shifting the bottleneck to planning, testing, governance, deployment and operations.
GitOps in 2026: Why Pull Requests Are Taking Over Cloud Operations
For years, cloud infrastructure changes were mostly a mystery. An engineer would log into a dashboard, tweak a setting, run a few scripts, and that was it. Nobody worried until something broke. Suddenly, everyone wanted answers. Who changed this? Was it tested? Can we fix it? How did production end up out of sync with […]
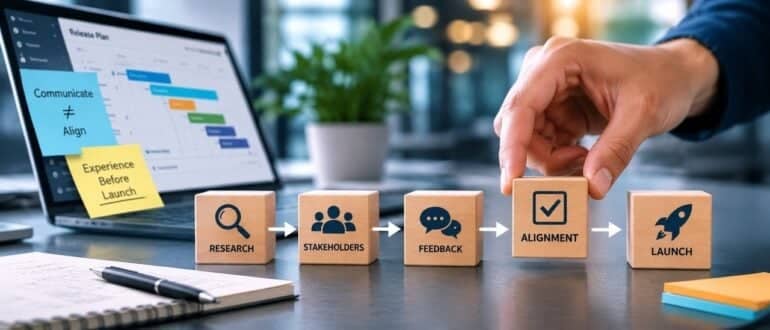
Informing Stakeholders Isn’t the Same as Aligning Them
The first sign of trouble was a screenshot. We’d just switched on the A/B test via our feature management platform. Within the hour, a senior stakeholder landed in the variant feature flag, opened the app on their own phone, and sent us an image of it. The message, more or less: “Why is there a […]
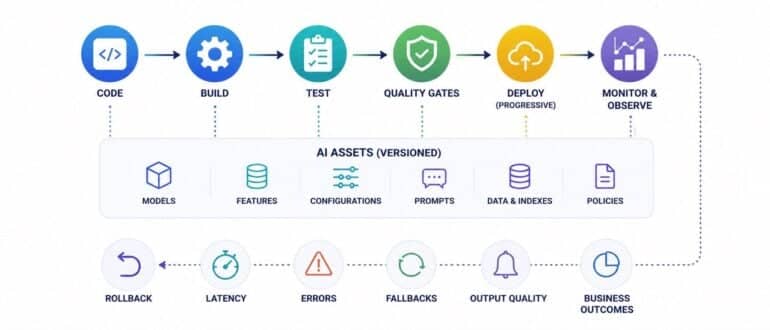
CI/CD for AI-Enabled Applications: Why Traditional Deployment Pipelines Need to Evolve
Traditional CI/CD pipelines are optimized around a familiar assumption: source code changes, automated tests validate the change, a build artifact is produced, and the application is promoted through environments. AI-enabled applications complicate that model because production behavior can change even when application code does not. A new model version, feature transformation, prompt configuration, retrieval index […]
The AI Agent Race Is On. But Are We Watching the Right Race?
Claude Code, OpenAI Codex, GitHub Copilot, Cursor and a growing field of challengers are competing to define the future of software development. A new Techstrong special report examines who is ahead, how the race should be measured and what enterprises need to consider before placing their bets. Which AI coding agent is winning? It sounds […]