

Why Self-Healing Tests Need a Deployment Gate
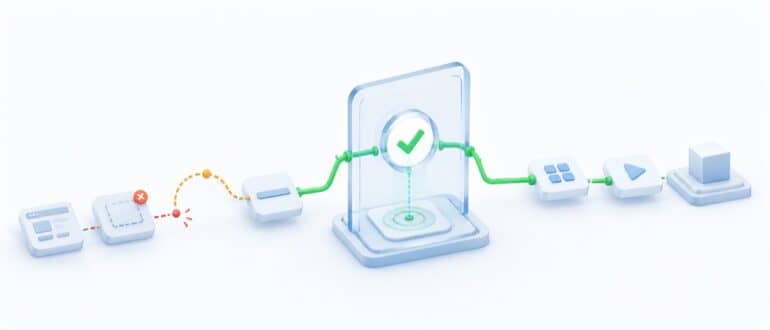
When an end-to-end test fails after a front-end change, the repair often looks routine. A class name changed. A button moved. A selector that used to be unique now matches two elements. A self-healing system inspects the page, proposes a new locator, reruns the test, and gets a green result. That green result is useful, […]
Is Your New DevSecOps Tooling Reducing Work Or Just Adding to It?
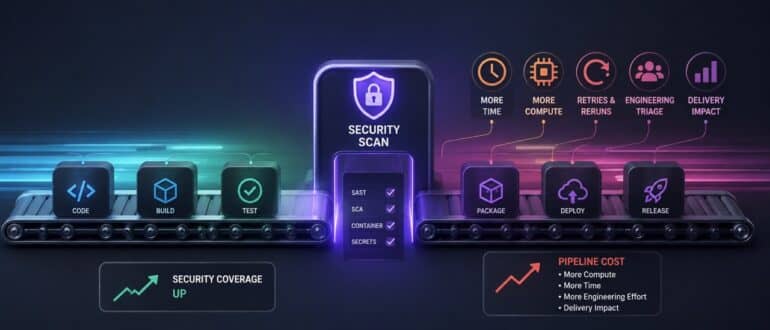
Security belongs in the software delivery pipeline. The harder question is where, how often and at what cost. Many pipeline teams eventually add security scanning to CI/CD, and relatively few go back afterward to measure what it actually cost the delivery process. Security coverage went up. Something else changed too, and it is rarely measured […]
Treat Business Workflow Changes Like Deployments
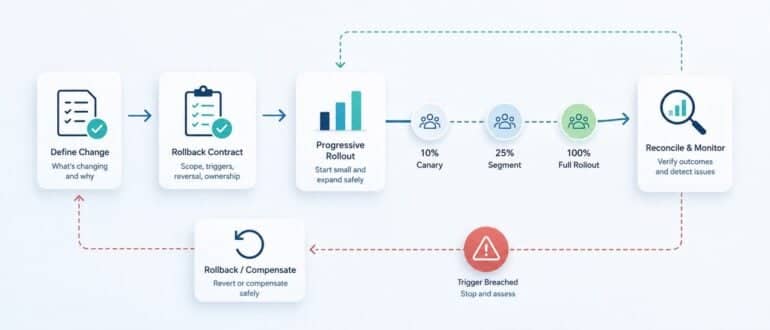
Business automation often reaches production without the release discipline applied to application code. A routing rule changes, an approval threshold moves, or an integration starts writing to a new system. The edit may happen in a visual builder instead of a repository, but its blast radius is still real: orders can duplicate, customers can receive […]
Software Deployment Strategies for Enterprise Teams: A Scenario-Based Guide to Choosing the Right Approach
Choosing the right software deployment strategy depends on the scenario. Get a practical decision framework for enterprise teams.
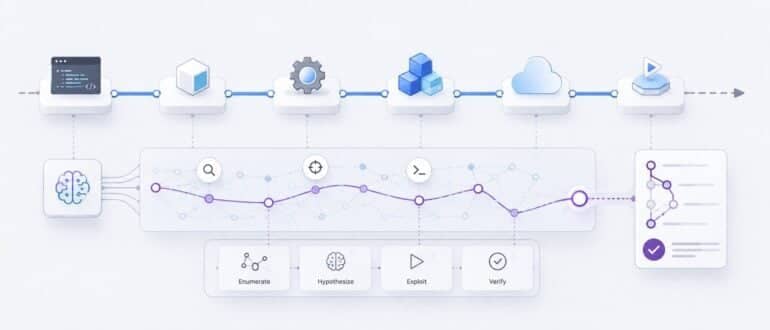
Why CI/CD Security Testing Is Going Autonomous (and Why It Should Stay Local)
Continuous integration and delivery changed the tempo of software. Teams merge dozens of times a day, infrastructure is redefined on every commit, and a new build can reach production in minutes. Security testing never caught up with that tempo. It still lives in two modes that both fight the pipeline instead of moving with it. […]
How Test Management Tools Give Engineering Teams the Visibility They Need to Ship With Confidence
Test management tools do more than track results. Learn how they give engineering teams the coverage visibility needed to ship with confidence.
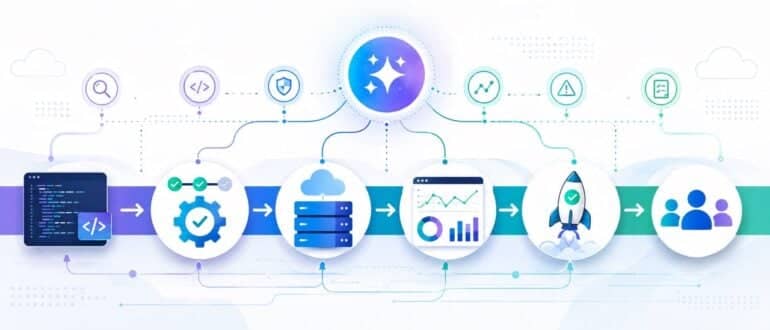
The Rise of AI-Native DevOps: How AI Is Reshaping Software Delivery in 2026
For years, DevOps had a pretty straightforward mission: help teams ship reliable software faster by getting development and operations folks working together. Tools like automation, continuous integration, continuous delivery, infrastructure as code, and better observability have all been key pieces of the puzzle. But now, things are shifting again. This time, artificial intelligence is changing […]
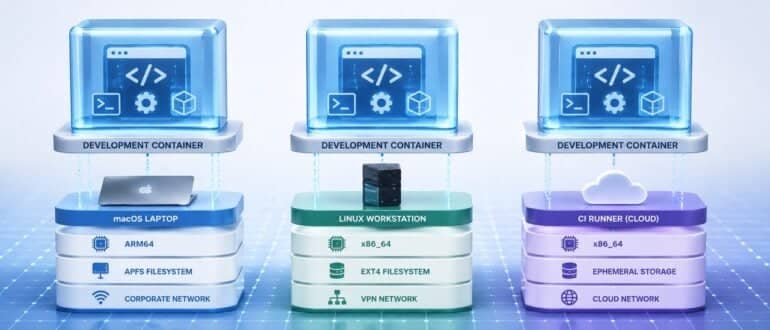
Why Standardized Developer Environments Still Break DevOps Workflows
Standardized developer environments promise to eliminate one of software engineering’s oldest explanations: “It works on my machine.” By packaging approved runtimes, dependencies and tools into containers, virtual machines or cloud workspaces, organizations expect every developer to start from the same foundation. The approach delivers clear benefits. It reduces onboarding time, minimizes dependency conflicts and makes […]
Why Reliability Guardrails Are Needed in Every AI Coding Pipeline
We’re in the middle of a reliability reckoning. Thanks to AI, companies are shipping code much faster than before. But if there’s anything to learn from the surge in high-profile outages over the last couple of years, it’s that with more code comes more reliability risks. And when those risks do lead to an outage, […]
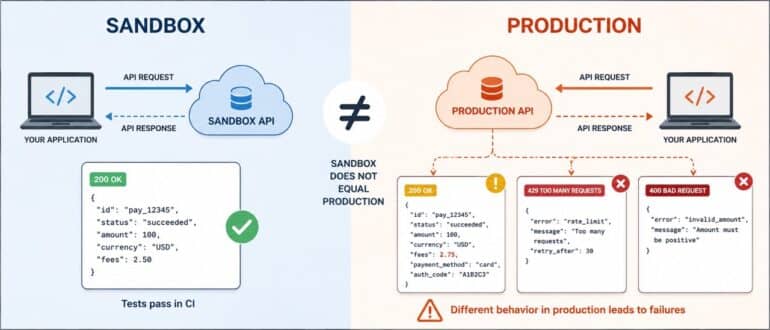
Sandbox Testing for API-Heavy Systems: What Changes When You Don’t Own the Dependency
Sandbox testing works well when your team controls both sides of the integration. You define the service, you define the mock, you know exactly what the sandbox should return. That setup holds up fine for internal microservices and first-party APIs. It starts to break down when you don’t own the dependency. Payment processors, identity providers, […]
RapidFort Extends Open Source Software Security Reach to Runtime Environments
RapidFort today at the Black Hat USA conference announced it has extended its ability to secure open source software to the runtimes that DevOps teams deploy in production environments. Michael Wood, chief marketing officer for RapidFort, said the RapidFort Runtime platform makes it possible to now monitor open source software deployed within a container image […]
GitHub Brings Stacked Pull Requests Out of the Shadows
GitHub introduces native stacked pull requests, helping development teams break large changes into smaller, dependency-ordered PRs that are faster and easier to review.
Adoption and Fragmentation of AI in CI/CD—and Operational Readiness
In today’s enterprise software delivery environment, AI has moved from a distant possibility to an active area of experimentation across the CI/CD pipeline. The conversation around AI in software delivery often runs ahead of the underlying reality, and most organizations are still working through what it takes to operationalize AI inside delivery architectures that were […]
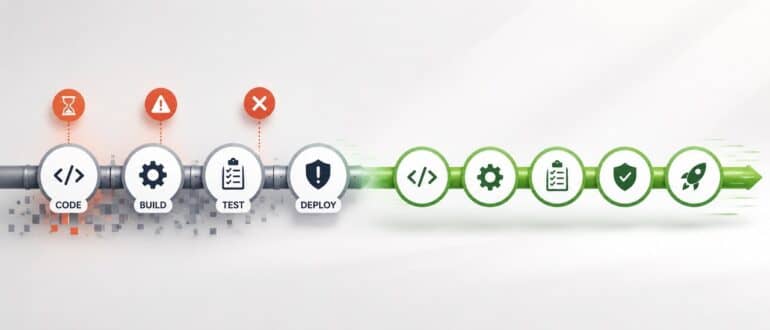
These are 10 CI/CD Pipeline Mistakes That Slow Down Engineering Teams
Continuous software delivery in the digital age has come to depend on CI/CD pipelines. They enable engineering teams to rapidly develop, test, and deploy code while keeping it highly usable and consistent across environments. CI/CD pipelines, however, can themselves become a source of friction as systems start at a small scale and become more complex. […]
Harness Extends DevOps Reach to the Realm of AI Agents
Harness today extended the reach of its core continuous integration/continuous delivery (CI/CD) platform to enable DevOps teams to build and deploy artificial intelligence (AI) agents. At the core of that capability are five additions to the Harness portfolio, including an AI Asset Catalog that automatically discovers every agent, skill, and plugin that exists within repositories […]
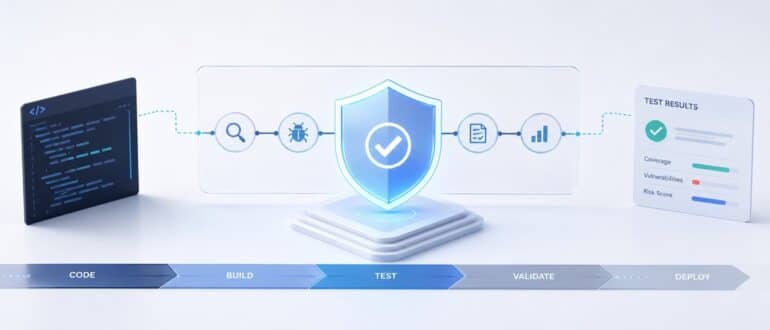
Why You Need AI Agent Security Validation in Software Testing
Engineering teams have been racing for the last two years to deploy AI agents that can find bugs faster than any QA team ever could. Autonomous testing agents can crawl through codebases, identify vulnerabilities, and generate test coverage reports while developers finally get to take a breath. The irony is that while development teams enjoy […]
How to Build a DevSecOps CI/CD Pipeline on Azure With GitHub Actions
Fix security problems when they’re cheap to fix, which is before the code is deployed. A pipeline that enforces this automatically is what makes that principle real.
Shadow Mode Continuous Integration: The Missing Test Layer for AI Agents
Autonomous agents require CI/CD pipelines that evaluate behavior, not just artifacts. Containerized shadow mode gives platform teams a practical control point: Run the agent in an isolated Docker environment, replay realistic workflows, capture structured traces and evaluate behavior against statistical and policy baselines.
Building CI/CD Pipelines for On-Prem Azure DevOps: What the Cloud Docs Don’t Tell You
The engineering that makes on-prem CI/CD reliable is invisible when it works. When it does not work, the failures are subtle and the documentation is thin.
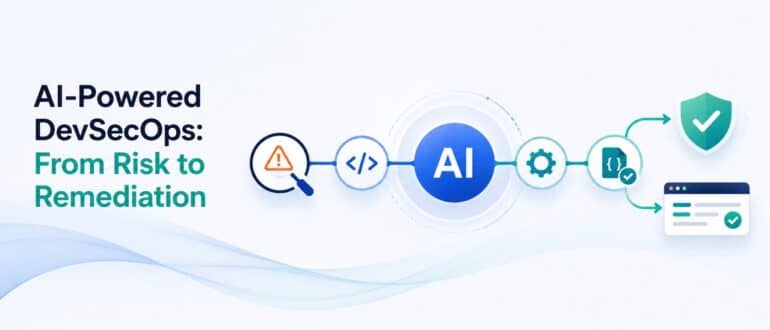
How AI is Revamping DevSecOps Processes
Artificial Intelligence is pushing DevSecOps into a new phase where security is no longer just about detecting vulnerabilities, but increasingly about resolving them automatically within the flow of software delivery. As many organizations are discovering, DevSecOps historically gave teams visibility into risk. AI is now turning that visibility into automated remediation. This evolution has taken […]
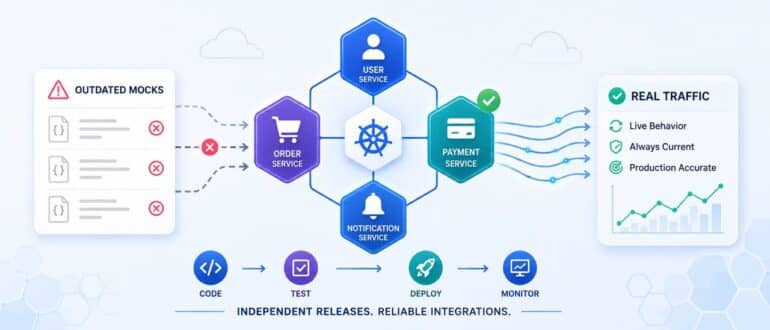
How Independent Service Deployments Expose the Limits of Conventional Regression Testing Tools
The architectural shift to independently deployable services was supposed to make software delivery faster and less risky. In many aspects, it has. Teams can ship a change to one service without coordinating a release across the entire system. A bug fix in the payment service does not require a synchronized deployment with the notification service, […]
A Beginner’s Guide to CI/CD and CI/CD Pipelines
Modern software development moves at a pace that would have been unthinkable a decade ago. Organizations push updates on demand, respond to vulnerabilities within minutes, and integrate new features at a relentless pace. This acceleration is driven by continuous integration and continuous delivery (CI/CD). To understand how CI/CD reshapes the security posture of modern organizations, […]
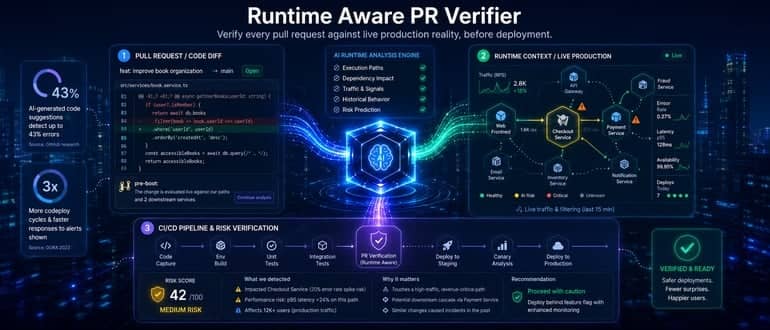
Lightrun Adds Ability to Assess Impact Pull Request Will Have in Production
Lightrun is providing early access to an ability to verify whether a pull request (PR) will actually run in a production environment as part of its artificial intelligence (AI) platform for automating site reliability engineering (SRE) workflows. Company CTO Leonid Blouvshtein said the Runtime Aware PR Verifier enables DevOps teams to assess the impact a […]