



Federal Agencies Share DevSecOps Guidelines
The National Security Agency (NSA), Cybersecurity and Infrastructure Security Agency (CISA), and the Office of the Director of National Intelligence (ODNI) have published a set of DevSecOps best practices based on the Enduring Security Framework (ESF). Developed by a public-private cross-sector working group led by NSA and CISA, the ESF framework was created in the wake […]
Contrast Security Adds API Support to Security Platform
Contrast Security has fully extended its vulnerability scanning and runtime application self-protection (RASP) platform to now include application programming interfaces (APIs). Company CTO Jeff Williams said the Contrast Secure Code Platform embeds agents directly into code to detect vulnerabilities using a combination of integrated static and dynamic application security testing tools. That approach makes it […]

One Year Out: What Biden’s EO Means for Software Devs
It has been just over a year since president Biden issued executive order 14028 (EO) to improve the nation’s cybersecurity posture. Despite the Log4j vulnerability and a worldwide increase in ransomware attacks, this EO signaled a major step in improving software security at federal agencies and establishing cybersecurity as a priority for the U.S. government. […]
TechStrong Con 2022: Exploring What’s Next in Tech
We have become increasingly reliant on technology and it’s hard to imagine life without all the great tech inventions we use in our daily lives. As technology keeps progressing, more is expected of IT teams, and security is a top priority. While we are still trying to get used to the new normal, the IT […]
Why is Security Still in the Way? A Look at DevSecOps Right Now
According to industry trend reports for 2022, DevSecOps is now considered to be one of the most effective approaches to building software quickly and securely. This effort, of course, means development, security and operations teams commit to addressing security as early as possible in the software development life cycle (SDLC). The goal of the shift […]
How Work-From-Anywhere Impacts DevOps
Brian Lavallée from Ciena talks with Mike Vizard about how the work-from-anywhere movement has impacted DevOps, networking and security. The video is below, followed by a transcript of the conversation. Mike Vizard: Hey, guys. Thanks for the throw. We’re here with Brian Lavallée who is senior director for solutions marketing at Ciena. Brian, welcome to […]

How the Cybersecurity EO Impacts DevOps Teams
Eric Greenwald, general counsel for Finite State, talks with Mike Vizard about how the executive order for securing software supply chains issued by president Biden will impact DevOps teams. The video is below, followed by a transcript of the conversation. Announcer: This is Digital Anarchist. Mike Vizard: Hey, guys. Thanks for the throw again. We’re […]
2022 Will Be the Year of the Cyber ‘Shift Show’
As ransomware continues to plague organizations across industries, remote work continues and innovation brings with it new threat vectors for bad actors to exploit, 2022 is poised to be another messy year in cybersecurity. In July 2021 alone, organizations lost $45 million to ransomware. What’s more, ransomware costs are projected to reach $265 billion by […]

Infrastructure Access Management a Growing DevOps Priority
Organizations plan to address access management over the next 12 months, as the need to secure and streamline infrastructure-wide access controls serves as a prerequisite to other initiatives, like zero-trust. This was one of the key findings of a survey of 600 DevOps professionals conducted by Pollfish and sponsored by strongDM. The report also found […]
Predict 2022: Back to the Future
After a year of innovation, rapid digital transformation efforts, new challenges and settling into a new normal, it is time to look back at all the lessons learned and look forward to the future. What does 2022 has in store for us? Will 2022 be a breakthrough year in terms of progress and opportunity? At […]
Best of 2021 – Torvalds’ Bug Warning is a Lesson for Linux Users
As we close out 2021, we at DevOps.com wanted to highlight the most popular articles of the year. Following is the third in our series of the Best of 2021. Linux does, occasionally, raise security concerns. While many users see it as the most secure, robust and versatile operating system available — that’s this writer’s […]
Datadog Cloud Security Platform Advances DevSecOps
Datadog has launched a Datadog Cloud Security Platform that promises to advance DevSecOps by identifying potential threats using the same agent software many DevOps teams already rely on to instrument applications. Renaud Boutet, senior vice president of product for Datadog, said organizations that rely on the Datadog software-as-a-service (SaaS) platform can now more easily invoke […]
The Shopify Breach: Why Authz Exploits Slip by Most Security Defenses
What Happened As part of a bug bounty, the security researcher Uzsunny found a critical vulnerability on the Shopify platform. The vulnerability allowed the attacker to assign himself as a “collaborator” to any store on Shopify without approval from the store’s manager. Collaborators have full access to perform any action on the store, including reading […]
Best Practices for Cloud Incident Response
Cloud computing is now mainstream, with almost all organizations running at least some resources in the public cloud—whether software-as-a-service (SaaS), platform-as-a-service (PaaS) or infrastructure-as-a-service (IaaS). Security teams have been scrambling to adapt to cloud environments, and with the growing adoption of DevSecOps, they are working together with DevOps teams to secure cloud systems from the […]
What Biden’s Cybersecurity EO Means for DevOps Teams
On May 12, 2021 President Biden issued Executive Order 14028, also known as the Executive Order on Improving the Nation’s Cybersecurity. This EO covers a lot of ground, and like all executive orders, it instructs agencies of the U.S. Federal Government to perform specific actions. What it doesn’t do is appropriate funding or create industry […]
WhiteHat Security Allies With Bit Discovery on Vulnerability Intelligence
WhiteHat Security, a subsidiary of NTT, has announced an integration with Bit Discovery to make it easier for developers and cybersecurity teams to discover the extent to which the attack surface they need to defend might be impacted by a vulnerability. Bit Discovery maintains a database made up of more than 5 billion internet-connected assets […]
Vulcan Cyber Research Reveals Most Enterprise Cybersecurity Teams Lack the Ability to Remediate Risk
Benchmark study finds most cybersecurity organizations lack the tooling and resources to deliver enterprise cyber hygiene TEL AVIV, Israel — May 12, 2021 — Vulcan Cyber®, developers of the industry’s only risk and vulnerability remediation platform, today released the results of its latest vulnerability remediation maturity research project. A survey of more than 100 enterprise security executives across […]
Trend Micro Allies With Snyk to Advance DevSecOps
Trend Micro and Snyk unveiled today a software-as-a-service (SaaS) platform the two companies have jointly developed to identify vulnerabilities in open source code. The Trend Micro Cloud One – Open Source Security by Snyk platform enables DevOps teams to both identify vulnerabilities and licensing issues to better monitor, prioritize and share information about risk and […]
The Basics of DevSecOps Adoption
Embracing DevOps is essential, but keeping the software delivery and deployment pipeline safe has become more critical than ever. While attackers are keen on getting into your Docker containers or Kubernetes clusters, securing your images, pods and clusters can deter attackers. Securing your artifacts, deployment workloads and production environments remains critical today. While we have […]
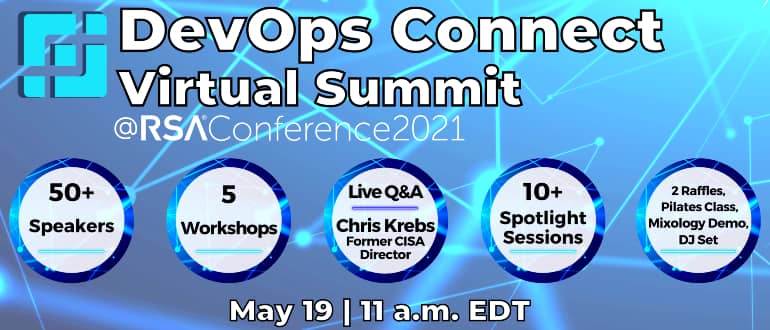
DevOps Connect at RSAC 2021: Insightful Talks, Live Q&A, Workshops, Pilates and More
We are excited to announce the return of DevOps Connect: DevSecOps Virtual Summit on May 19, as part of the RSA Conference 2021. This year, internationally recognized speakers will take a deep dive into “Securing the Cloud Native World.” DevOps Connect is a full-day event, featuring four different content tracks, with more than 50 speakers, […]
The Time for Collaborative Security Is Now
As Bruce Schneier famously said, “security is a process, not a product.” We commonly see companies pour millions of dollars into cybersecurity products and tools to protect against vulnerabilities and lower risks, and yet, more often than not these ample funds are not enough to defend against attacks. Within the span of two decades, we […]
How to Bring DevOps and Security Teams Closer Together
More often than not, there seems to be friction between DevOps and security teams. Despite having the same end goals of creating the most secure code and preventing any potential security pitfalls, these groups of professionals often lack the unity needed to accomplish these end goals effectively and efficiently. In the interview below, Naomi Buckwalter, […]
Live Fireside Chat with Christopher Krebs: How to Combat Disinformation
We live in a digital world where most information is now found online. This makes it increasingly difficult to verify the veracity of information. Threat actors have been taking advantage of the digital landscape to spread disinformation, propaganda and conspiracy theories to manipulate the public and sow doubt, discord and chaos. How can we distinguish […]