


Navigating the Next Wave of Cybersecurity Legislation With a Supercharged Security Culture
CISOs at the forefront of implementing developer-driven security programs choose upskilling solutions that allow for precision measurement, in addition to customization that is reflective of scenarios they are most likely to encounter in the course of their work.

DryRun Security Defines Application Security Policies Using Natural Language
DryRun Security today added an ability to use natural language to define and enforce application security policies as application developers build software.
CISA Pushes Steps to Better Secure Software and Product Designs
The country’s top cybersecurity agency is urging developers to take steps to ensure the software they’re building and the products they roll out are secure and protect end users. The Cybersecurity and Infrastructure Security Agency (CISA) this week rolled out a series of recommendations that it wants businesses and critical infrastructure organizations to adopt to […]
Automating Web Application Security Testing to Combat Cyber Threats
Despite the hundreds of exposed web applications and APIs in our attack surfaces, many assets remain dangerously untested and vulnerable to cyberattacks.
The Software Extinction Event That Wasn’t
The world may have just avoided a cybersecurity disaster, with potential impact of CrowdStrike x1000. Imagine if the world’s most pervasive programming language, used in the majority of organizations, services, websites and infrastructure today, was itself made to be malicious? Cybersecurity researchers from JFrog recently discovered a GitHub Personal Access Token in a public Docker […]
The Risks of the Cloud Oligopoly
The cloud oligopoly, insofar as it stifles competition, represents a potentially overlooked area in which businesses must assess their supply chain commitments.
Techstrong Group Announces Rebranding of Security Bloggers Network to Security Creators Network
BOCA RATON, FL, April 9, 2024 — Techstrong Group, the power source for people and technology, is excited to announce the rebranding of the renowned Security Bloggers Network to the Security Creators Network. With over 350 security-focused content creators, the network has been a staple in the cybersecurity community for the past two decades. The […]
DevSecOps: 5 Tips for Developing Better, Safer Apps
DevSecOps requires teams to collaborate and enable the organization to deliver safer applications to customers without compromising security.

Avoiding Mistakes in Multi-Cloud Configurations
Knowing how to configure multiple clouds mistake-free is essential to keep the promise of multi-cloud alive.
Synopsys Taps NowSecure and Secure Code Warrior to Improve DevSecOps
Synopsys has partnered with NowSecure and Secure Code Warrior to help organizations improve DevSecOps best practices.
Communicating Common Web App Security Threats to Developers
Shift left involves providing developers with the context they need to prioritize and remediate threats appropriately.
Bionic Extends Application Security Posture Management Platform
Bionic this week added a pair of tools to its application security posture management (ASPM) platform that make it simpler to triage threats based on severity and attach a risk score. Josh Cho, senior director of global systems engineering at Bionic, said the Bionic Signals and Business Risk Scoring tools ingest data from third-party security […]

How to Empower DevSecOps in a Complex Multi-Cloud Landscape
Organizations are embracing cloud-based application delivery for speed of delivery and scale. However, the proliferation of multi-cloud systems to access and maximize the cloud’s capabilities is driving complexity in IT environments. Many organizations do not consider how multi-cloud adoption is expanding their attack surface—and the risk is growing: The 2023 CrowdStrike Global Threat Report found […]
GitLab Adds More AI and Cybersecurity Capabilities to CI/CD Platform
GitLab this week delivered an update to its continuous integration/continuous delivery (CI/CD) platform that adds additional generative artificial intelligence (AI) and cybersecurity capabilities. The GitLab 16 release included cybersecurity capabilities such as centralized policy management, expanded compliance reports and controls, compliance dashboards and default Level 3 attestation for the supply-chain levels for software artifacts (SLSA) […]

Four Trends Defining the Observability Market in 2023
Observability is a market that has grown exponentially over the past few years. It started as a buzzword in late 2015 and early 2016, and since then we’ve seen dozens of insurgent companies rush in, eager to stake their claim in a new (albeit loosely defined) market. Incumbent companies also rebranded their wares, hoping to […]
Technical Debt is a Major Threat to Innovation
A survey published today suggested that technical debt is starting to take a heavier toll as IT environments continue to become more complex to manage. The survey of 400 IT leaders at organizations with 1,500 employees was conducted by Foundry, the market research arm of International Data Group (IDG) on behalf of Insight Enterprises, a […]
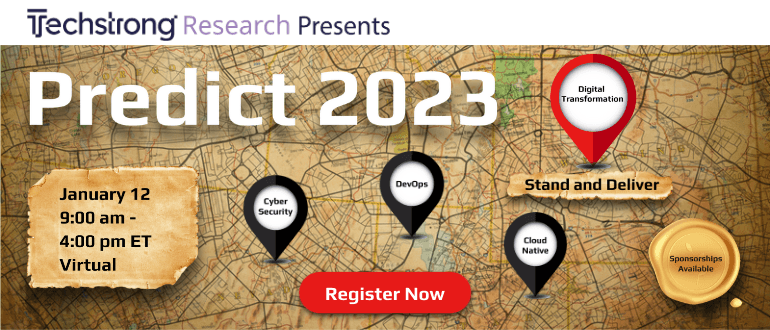
Predict 2023: Stand and Deliver
It’s that time of year again—the New Year’s ritual: Time to predict the big trends in your world for the new year. By now you have probably seen dozens of headlines, articles, videos and interviews telling you what big trends will shape the coming year. Here at Techstrong Group, our Predict virtual event is built […]
Best of 2022: Measuring Technical Debt
As we close out 2022, we at DevOps.com wanted to highlight the most popular articles of the year. Following is the latest in our series of the Best of 2022. What is enterprise technical debt? Technical debt slows down organizations and hampers their ability to deliver. Studies show that technical debt can triple the cost […]
Why Backups and Compliance Go Hand-in-Hand
It’s hard to run a business. Besides the numerous challenges you have to deal with daily, ensuring the security of your business and customer information is essential for operating smoothly. In order to mitigate information security risks that would affect companies and their users, a number of security regulations have been created, including a set […]
Implementing Shift Left Security in the Cloud
While ransomware has been the leading concern for enterprise security teams over the few past years, software vulnerabilities are nipping at its heels. The boom in cloud-based apps and services and increased digitization of work have been a boon for hackers, who are taking advantage of developers’ and DevOps teams’ attempts to work faster and […]
Palo Alto Networks Buys Cider Security to Lock Down Pipelines
Palo Alto Networks this week extended its efforts to secure application environments by agreeing to acquire Cider Security, a provider of a platform for securing continuous integration/continuous delivery (CI/CD) platforms, for approximately $195 million in cash. The acquisition of Cider Security, scheduled to close this quarter, will extend the reach of the company’s Prisma Cloud […]
5 Tips for Securing DevOps: What You Wish You Knew Sooner
Foundations and frameworks, concrete and steel—not exciting. But that’s the foundation and framing of pretty much every modern building. Everything else that is part of a building–flooring, wiring, lighting, room placement and so on—is made possible by the foundation and the framework. If you want DevOps to succeed in your organization, you have to start […]
Aqua Security Claims Compliance With Biden’s Executive Order
Aqua Security this week claimed it is the first software supply chain security platform provider to meet the attestation requirements as defined by an executive order issued to federal agencies last year by the Biden administration. A supplementary memo issued by the Biden administration required federal agencies to collect compliance attestation letters for all software […]