

Legit Security AI Tool Uses Threat Feed to Identify Risks to Software Supply Chain
Legit Security this week added a threat feed that DevSecOps teams can use to instantly determine if a newly discovered vulnerability impacts their software supply chain. Built using the Legit VibeGuard tool, the threat feed added to the company’s application security posture management (ASPM) platform also enables DevSecOps teams to take advantage of “vibecoding” techniques […]
DevSecOps In Digital Banking: Balancing Fast Releases With Regulatory Compliance
In the digital banking sector, fast releases of new features and security patches have become the norm. Unfortunately, many institutions lack the organization or the processes necessary to make the speed of necessary releases coincide with the need to follow strict regulatory guidelines. A failure to accurately test and ensure compliance can lead to critical […]
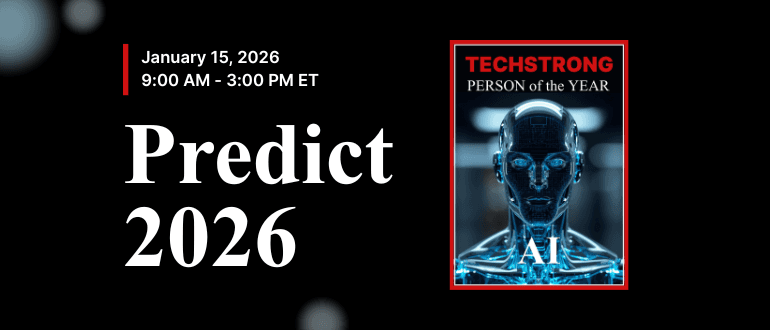
Predict 2026: Why AI Will Force DevOps to Reinvent Itself
Join us at Predict 2026 to explore how AI is transforming the DevOps landscape, enhancing software delivery, and redefining operational strategies.
Cursor Allies with 1Password to Secure AI Coding Secrets
Cursor has partnered with 1Password to better protect secrets as applications are developed using an artificial intelligence (AI) coding tool. Nancy Wang, senior vice president and head of engineering for 1Password, said a Hooks Script provides application developers with a secure, just-in-time way to ensure only required secrets are made available to Cursor AI agents […]
Importance of Observability in the DevSecOps Pipeline: Enhancing Security, Compliance, and Collaboration
In today’s rapidly developing software world, security cannot be an afterthought. DevSecOps, the integration of security practices into every phase of DevOps, requires continuous monitoring and actionable insights to detect and mitigate threats effectively. Observability plays an essential role in this ecosystem by providing deep visibility into the security posture of the development process, enabling […]
Best of 2025: GitLab Extends Scope and Reach of Core CI/CD Platform
GitLab Inc. has updated its core continuous integration/continuous delivery (CI/CD) platform to natively provide more artificial intelligence (AI) capabilities, along with built-in software artifact management capabilities and more robust security tools.
Best of 2025: Five Trends That Will Drive Software Development in 2025
In 2025, developers will broaden the scope of how they use AI with promising new applications for reducing technical debt and improving security.
Surprise! Everybody Uses AI Tools for Software Development, Few Do So Securely
AI is generating code faster than teams can secure it, widening software supply chain risk and exposing major gaps in AppSec and governance.
Checkmarx Acquisition of Tromzo Accelerates Plan to Apply AI to Application Security
Checkmarx accelerates its AI-driven DevSecOps strategy after acquiring Tromzo, integrating AI agents to automate application security across the software development lifecycle.
DevOps for GenAI Toronto Edition Hackathon: Unlocking New Opportunities
This week in Toronto, at the DevOps for GenAI Hackathon, something remarkable occurred: Industry professionals, academic leaders and learners representing top academic institutions, fintech, technology firms, and consulting companies came together in a high-intensity innovation sprint that blurred the lines between academia and enterprise. Across four banking teams (including winners from Scotiabank), three technology and […]
Why Privacy-Safe Logging Remains One of the Hardest Problems in DevOps
As cloud-native architectures scale and regulatory pressure intensifies, organizations are finally recognizing that their logging pipelines contain sensitive. Logs fuel observability, debugging, compliance investigations, and incident response, yet they also remain one of the least governed data streams in the enterprise. Despite years of progress in DevSecOps, true privacy-safe logging, logs that remain operationally useful […]
It’s Time to Rethink Access Control for Modern Development Environments
As development environments evolve at breakneck speed, our approach to securing them remains stuck in the past. I’ve watched countless organizations implement robust Identity and Access Management (IAM) solutions, deploy Identity Governance and Administration (IGA) tools, and then breathe a collective sigh of relief, believing they’ve solved their access control challenges. But have they? An […]
How Open Source Tools Simplify DevOps for Startups
In recent years, software development has made big strides. Tools like GitHub Copilot, ChatGPT, and other AI helpers have given developers the power to churn out code, tests, and documentation faster than ever. However, for solo founders and small startup teams, getting things written is only half the battle. Real challenges lie in getting it […]
What I’m Thankful for in DevOps This Year: Living Through Interesting Times
Alan reflects on a chaotic yet inspiring year in DevOps, highlighting the rise of AI in engineering, the maturation of DevSecOps, the evolution of hybrid work culture, the surge of platform engineering and IDPs, and the continued strength and inclusivity of the DevOps community — while acknowledging the talent crunch, tool sprawl and security theater that still challenge the industry.
The Future of DevOps Still Has a Pulse
Over the last few years, we have watched our industry get swept up in the promise of AI agents. The pitch is compelling: tell a system “Deploy this workflow and roll back if things don’t go as expected,” and watch it handle everything else. No more YAML troubleshooting and pipeline debugging. We’ve all been there, […]
What Fuels AI Code Risks and How DevSecOps Can Secure Pipelines
Modern development teams are under constant pressure to deliver fast, innovate continuously, and stay clear of security threats; all at the same time. Every new feature, every accelerated release, carries the hidden risk of introducing vulnerabilities that can slip past traditional check points. Even the most seasoned developers can unknowingly leave gaps that put applications […]
How to Escape the Talent Valley
Across the tech industry a disconcerting trend is emerging, job losses at the hand of a seemingly more efficient and cost-effective employee, artificial intelligence (AI). Software developers in particular have felt the full force of automation’s iron fist, with layoffs widespread. Since May, Microsoft alone has let go of approximately 15,000 employees, with software engineers […]
Endor Labs Adds AI SAST Tool to Discover Vulnerabilities in Code
Endor Labs launches an agentic AI-powered SAST tool that drastically reduces false positives, identifies deeper code flaws and helps DevSecOps teams secure AI-generated code across 40+ languages.
The Future of DevSecOps: From Shifting Left to Shifting Smart
For the better part of a decade, a revolutionary idea has reshaped enterprise security: the “shift left” movement. This mantra taught us to view the software development lifecycle (SDLC) not as a finish line for security, but as its starting point. By embedding security checks at the earliest possible stage, we made incredible strides in […]

Vibe Coding: The Double-Edged Sword in Modern Software Development
In the fast-paced world of software development, new methodologies and trends emerge constantly. One method gaining traction, particularly among younger developers, is vibe coding. While it promises increased productivity and a more fluid development experience, it also introduces a unique set of cybersecurity risks that both developers and their leadership need to understand. What is […]
Observability is the Next Frontier of DevOps and Cloud Security
In today’s cloud-native, hybrid-multi-cloud world, DevOps teams face a new paradox. They can deploy code faster than ever, but their visibility often lags. Traditional monitoring tools might reveal that something broke, but not why it happened, when it started, or how it affects the business. For organizations that value resilience, agility, and trust, observability can […]
JFrog Adds Ability to Track Usage of AI Coding Tools
JFrog introduces AI-Generated Code Detection and Shadow AI Detection tools to identify AI-created code, track model usage, and enhance DevSecOps governance across software supply chains.
DevSecOps in Practice: Closing the Gap Between Development Speed and Security Assurance
In the world of modern software development, speed is king. Teams are under constant pressure to release features, fix bugs and stay ahead of competitors. Yet, as development velocity increases, so does the risk of introducing vulnerabilities — an inconvenient truth that security teams have been sounding alarms about for years. This tension between speed and […]