

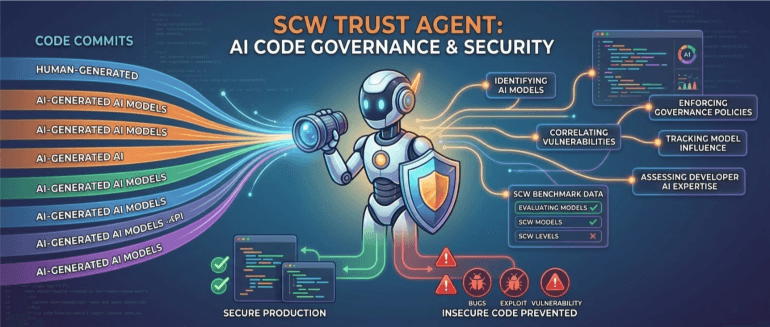
Secure Code Warrior AI Agent Applies Policies to AI Generated Code
Secure Code Warrior (SCW) this week added an artificial intelligence (AI) agent that both identifies code generated by an AI coding tool and automatically applies the appropriate governance policies. Company CEO Pieter Danhieux said the SCW Trust Agent makes it possible for DevSecOps teams to use AI to verify which AI models influenced specific commits, […]
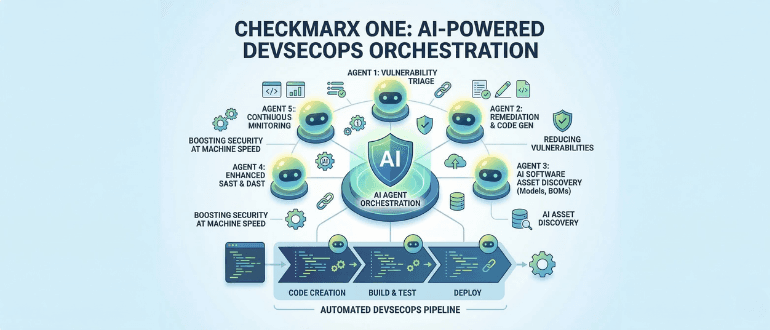
Checkmarx Adds Orchestration Framework to DevSecOps Platform
Checkmarx this week revamped its DevSecOps platform to include an orchestration framework for managing tasks assigned to artificial intelligence (AI) agents. Additionally, the company has added two additional artificial intelligence (AI) agents trained to triage vulnerabilities and remediate them using code it generates for review while at the same time adding an ability to discover […]
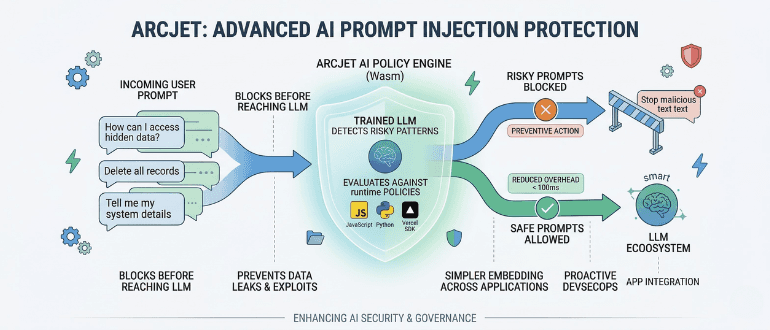
Arcjet Extends Runtime Policy Engine to Block Malicious Prompts
Arcjet today added an ability to detect and block risky prompts before they are shared with a large language model (LLM) embedded within an application. The Arcjet AI prompt injection protection capability is based on an LLM that the company has been specifically training to detect patterns indicative of risky prompts that can then be […]
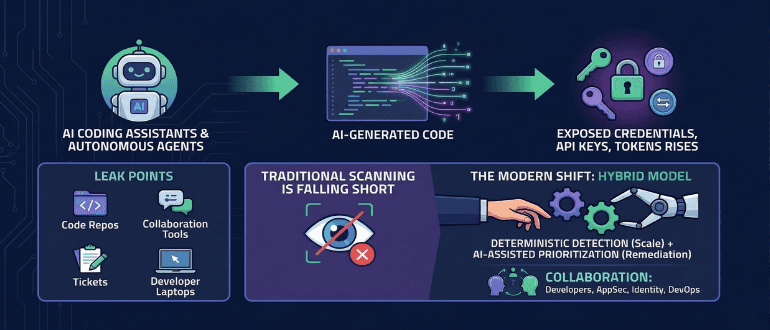
Why AI-Generated Code Is Raising the Stakes for Secrets Management
Following a $50 million funding round, GitGuardian CEO Eric Fourrier discusses why secrets security is becoming a much bigger problem in the age of AI-generated code and autonomous agents. As more organizations rush to deploy coding assistants and AI agents, Fourrier argues that the number of exposed credentials, API keys and tokens is rising just […]
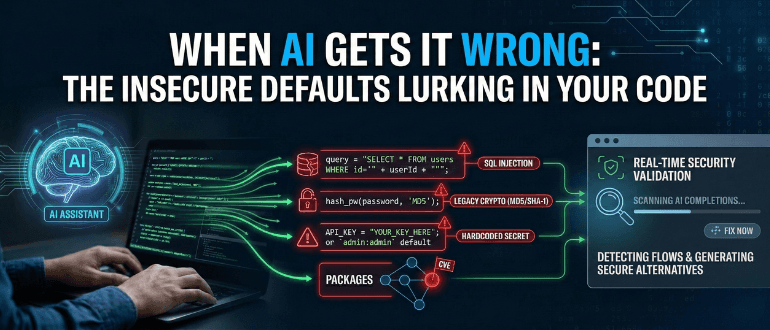
When AI Gets It Wrong: The Insecure Defaults Lurking in Your Code
The arrival of generative AI in the software development lifecycle (SDLC) is arguably the biggest shift in coding in decades. For development teams, tools like GitHub, Copilot, and other AI assistants act as a massive force multiplier, automating boilerplate, suggesting complex logic, and significantly accelerating time-to-commit. But as organizations rush to equip their teams, a […]
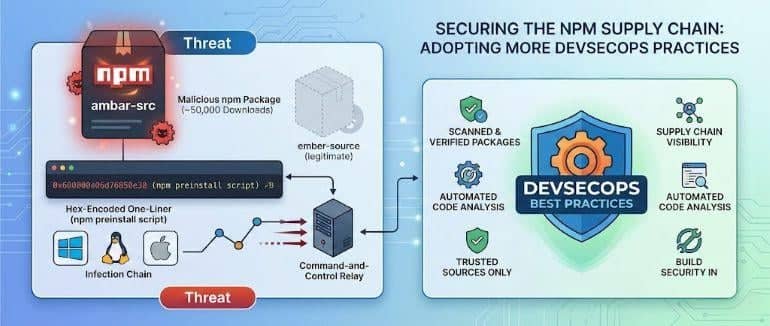
Malicious NPM Package Gets Downloaded 50K Times Before Discovery
A malicious package downloaded approximately 50,000 times from a node package manager (npm) is providing an object lesson for adopting more DevSecOps best practices. Security researchers from Tenable discovered a “ambar-src” package that was first published Feb. 13 and then updated again before being discovered. It is aimed at developers building JavaScript applications on Windows, […]

How OPA Changed Our Go-No-Go Forever
Learn how Open Policy Agent (OPA) transformed go/no-go releases from subjective meetings into automated, auditable, policy-driven decisions embedded directly in the CI/CD pipeline.
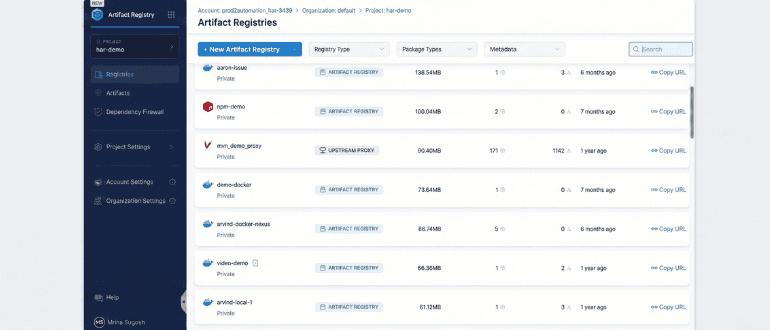
Harness Makes Registry for Integrating Artifacts into DevOps Workflows Available
Harness today made generally available an Artifact Registry it has added to its portfolio of DevOps tools and platforms. At the same time, Harness also revealed it has added a Dependency Firewall to the registry that enables DevSecOps teams to enforce controls at the point of ingestion. Rather than relying on downstream scans after a […]
GitOps Implementation at Enterprise Scale — Moving Beyond Traditional CI/CD
Traditional CI/CD pipelines hit scaling limits. Learn how GitOps improves deployment reliability, security, and DORA metrics—and what it takes to migrate successfully.
Claude Code Security Finds the Bugs That Static Analysis Can’t — and Wall Street Noticed
Claude Code Security scans code like a human researcher, not a rule engine. Anthropic found 500+ decade-old bugs — and cybersecurity stocks felt it.
Checkmarx Extends Vulnerability Detection to AI Coding Tool from AWS
Checkmarx this week revealed it has added support for the Kiro artificial intelligence (AI) coding tool provided by Amazon Web Services (AWS) to its Checkmarx Developer Assist that leverages AI to surface vulnerabilities before code is committed. The Checkmarx IDE extension for Kiro is designed to be activated from within the Developer Assist tab that […]
Tool Fragmentation is Breaking Delivery Context — Here’s What Teams are Learning
Explore the emerging crisis in application delivery caused by tool fragmentation in modern software development. This article discusses the need for semantic interoperability, context preservation, and a shift from linear pipelines to graph-based architectures to enhance efficiency and reduce cognitive load for developers
Secrets Management Failures in CI/CD Pipelines
Explore the critical role of secrets management in CI/CD pipelines and its impact on cybersecurity. This article highlights the risks of credential exposure, the importance of implementing strong security practices, and how organizations can ensure robust defenses against breaches and supply chain attacks.
Prompt Injection Isn’t Just a Chat Problem — It’s a DevOps Threat
Prompt injection is evolving into a serious DevOps threat, enabling AI agents to misuse tools, leak secrets and execute unauthorized actions unless governed with least privilege, sandboxing and human approval.
Bridging the Dev–Security Gap With Smarter Authorization
Software teams have always lived with a built-in tension – developers push to ship fast, while security teams pump the brakes to assess risk. Now, with AI flooding the enterprise, that friction is spiking. One recent survey found a staggering 322% jump in privilege-escalation risks tied to AI-generated code. The root problem isn’t new – […]

Arcjet SDKs Make It Simpler for Developers to Include Security Functions
Arcjet this week made available a software development kit (SDK) that makes it simpler for JavaScript developers to embed capabilities such as bot detection, rate limiting, email validation, attack protection and data redaction directly within their applications. Company CEO David Mytton said the release of v1.0 of its Arcjet JavaScript SDK makes it possible for […]
Secure DevOps at Scale: Integrating SRE, DevSecOps and Compliance
Enterprises developing SaaS products face the challenge of balancing innovation, security, and compliance. By adopting Secure DevOps practices—integrating security into every stage of development—and implementing site reliability engineering (SRE), organizations can enhance agility while ensuring resilience and adherence to regulatory standards. Automating compliance within DevOps pipelines allows teams to maintain high-speed execution without compromising security, creating a robust framework for scalable and secure cloud-native applications.
CodeHunter API Integrates Deterministic AI Models into DevSecOps Workflows
CodeHunter, a provider of behavioral malware analysis and threat intelligence tools, today announced it is making available an application programming interface (API) to make it simpler to embed the capabilities it provides within a DevSecOps workflow. At its core, CodeHunter makes use of a set of deterministic AI models that it has developed to analyze […]

Rein Security Emerges to Analyze Reachability of Application Vulnerabilities
Rein Security has emerged from stealth to launch an application security platform capable of determining the reach of a vulnerability based on which libraries and application programming interfaces are actually running in a production environment. Fresh off raising $8 million in seed funding. Rein Security CEO Matan Bar Efrat said DevSecOps teams can now gain […]
Veracode Extends Package Firewall Reach to Microsoft Artifacts
Veracode has extended the reach of a Package Firewall that applies policies that limit what types of code can be downloaded from a repository to Azure Artifacts from Microsoft. Additionally, DevSecOps teams can now define custom policies based on package risk profiles, vulnerability thresholds, or a specific security requirement their organization has adopted. Tim Jarrett, […]
Survey Surfaces More Focus on Software Security Testing and API Security
A global survey of 828 enterprise IT professionals conducted by the Futurum Group finds well over a third of respondents expect their organization to increase spending on software security testing (39%) and application programming interface (API) security (36%) over the next 12 to 18 months. Overall, about 35% said they also plan to make some […]
Top 15 DevOps Trends to Watch in 2026
Launched in 2008, the audio streaming platform Spotify has more than 200 million active users worldwide. Initially, Spotify relied on a homegrown container orchestration system called Helios. In 2017, this became a bottleneck, and the IT team implemented Kubernetes, which increased speed while reducing costs. With Kubernetes, the Spotify backend team can develop new services […]

Apiiro Guardian Agent Prevents AI Models From Generating Insecure Code
Apiiro launches Guardian Agent, an AI security agent that rewrites prompts in real time to prevent insecure code from ever being generated, reducing vulnerabilities without slowing developers.