

Oasis Security Identifies Security Weakness in Cursor AI Coding Tool
Oasis Security this week warned application developers of a security flaw in the Cursor artificial intelligence (AI) code editor developed by Anysphere, Inc. that potentially could be used to allow a maliciously crafted code repository to execute code as soon as it’s opened using Cursor. Erez Schwartz, threat research engineer at Oasis Security, said that […]
What Makes Vulnerability Scanning Effective in Fast-Moving DevSecOps Pipelines Today?
Traditional vulnerability scanning can’t keep pace with CI/CD. Learn how real-time, context-aware scanning reduces noise, speeds fixes, and enables secure DevSecOps at scale.
Nominations Are Open: DevOps Dozen 2025
The DevOps Dozen 2025 awards are open. Celebrate community leaders and tools shaping DevOps, from AI to platform engineering and supply chain security.
Survey Surfaces Raft of AI Coding Issues Involving Embedded Systems
A new survey of 785 development and security professionals reveals that 89% of organizations are using AI coding assistants for embedded systems, but concerns over security, licensing risks, and governance remain. Python leads as the top programming language, while SBOM adoption and SCA scans rise across industries.
Coding at the Speed of AI: Innovation, Vulnerability, and the GenAI Paradox
Generative AI accelerates software delivery but also reintroduces vulnerabilities, making secure coding practices, oversight, and developer training essential for safe adoption.
Qwiet AI Extends Microsoft Support in Platform for Fixing Vulnerabilities
Qwiet AI extends its AI-driven application security platform with deeper Microsoft DevOps integrations, enhanced automation, and expanded AutoFix capabilities to proactively remediate code vulnerabilities.
The EU’s Cyber Resilience Act: Redefining Secure Software Development
The European Union’s Cyber Resilience Act (CRA) marks a turning point for anyone building, selling, or maintaining digital products. Whether it’s enterprise software, consumer apps, IoT devices, or embedded systems, the CRA sets rigorous cybersecurity requirements that apply throughout a product’s entire lifecycle, from design and development to deployment, maintenance, and secure decommissioning. At its […]
John Willis: The True North of DevOps and DevSecOps
Over the last 14-plus years of my journey through DevOps, I’ve had the good fortune to meet some of the smartest, most generous, most forward-thinking people in our industry. It’s one of the things I’m most thankful for—the friendships and shared learning that come from being part of a community that is always pushing boundaries. […]
Tackling the DevSecOps Gap in Software Understanding
When I first read the recent article from CISA titled “Tackling the National Gap in Software Understanding,” I had the same reaction I imagine many of you did: Well, of course this is necessary. Who in their right mind doesn’t want better visibility into the software used in our most mission-critical systems? But then I […]
White Paper: The Future of DevSecOps in a Fully Autonomous CI/CD Pipeline
Abstract The growing complexity of modern software development and the increasing speed at which organizations need to deliver software have led to the widespread adoption of DevOps practices, particularly continuous integration/continuous deployment (CI/CD) pipelines. These pipelines enable rapid development and deployment cycles; however, they also introduce significant security risks that must be addressed continuously. The […]
HoundDog.ai Code Scanner Shifts Data Privacy Responsibility Left
HoundDog.ai today made generally available a namesake static code scanner that enables security and privacy teams to enforce guardrails on sensitive data embedded in large language model (LLM) prompts or exposed artificial intelligence (AI) data sinks, such as logs and temporary files, before any code is pushed to production. Company CEO Amjad Afanah said the […]

Minimus Adds VEX Support to Managed Hardened Images Service
Minimus has extended its managed service for providing application developers with hardened images to include support for the Vulnerability Exploittability eXchange (VEX) format used to share data across multiple application security tools and platforms along with hardened Helm charts for securely deploying applications on Kubernetes clusters. Additionally, Minimus has added compliance dashboards and views, and […]

“Shove Left” – Dumping Downstream Tasks Onto Developers – A Recipe for Failure
Beware the “Shove Left” anti-pattern. Simply dumping downstream tasks onto developers without changing the system is a recipe for burnout, inefficiency and failure.

Emerging DevOps Trends: Security, Scalability and Sustainability
As DevOps continues to grow, rapid changes such as security, scalability and sustainability are at the forefront of these changes.
When AI Assistants Turn Against You: The Amazon Q Security Wake-Up Call
Amazon Q coding assistant was compromised with malicious prompts designed to wipe AWS accounts. What this near-miss teaches us about AI security.
Veracode Allies with Wiz to Bring More Context to DevSecOps Workflows
Veracode today revealed an alliance through which it will integrate its application security posture management (ASPM) platform with the cloud native application protection platform from Wiz.
Kusari Adds AI Security Tool to Inspect Code as Pull Requests Are Made
Kusari has added an artificial intelligence (AI) tool that runs a security risk assessment every time an application developer makes a pull request. Company CTO Mike Lieberman said Kusari Inspector is designed to make it simpler for security to be shifted left toward application developers in a way that doesn’t impinge productivity. Most application developers […]
Why DevSecOps Isn’t a Thing Yet
One of the biggest obstacles to DevSecOps adoption is the cultural gap between development, security, and operations teams.
AWS Extends Cloud Security Reach to Include DevSecOps Tools to Scan Code
Amazon Web Services (AWS) this week made Amazon Inspector, a code scanning tool for surfacing vulnerabilities that is designed to be natively integrated with GitHub and GitLab platforms, generally available. Announced at the AWS re:Inforce 2025 conference, Amazon Inspector combines a static application security testing (SAST) tool for analyzing application source-code with a software composition […]
Merging Business Logic and DevOps
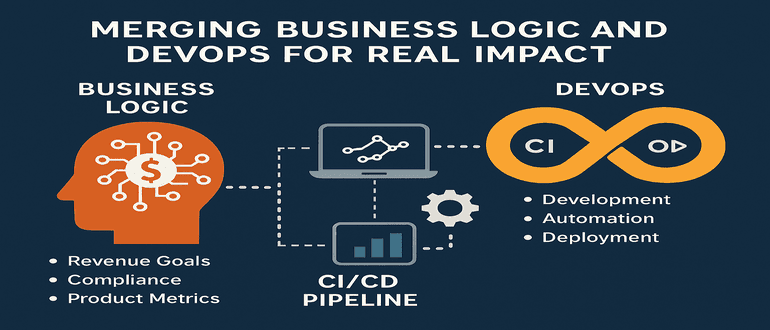
Bridging the gap between DevOps and business logic means product and application owners should map out business outcomes and then embed them in DevOps pipelines.

How to Embed Security Into Enterprise DevOps Pipelines
DevOps without security is just speed with risk. Now is the time to shift left, automate smart and build security into everything.
JFrog Extends Alliance With NVIDIA to Secure AI Software Supply Chain
JFrog and NVIDIA today announced they have expanded the integrations between their software development platforms to now include the Enterprise AI Factory, a set of frameworks and blueprints for building artificial intelligence (AI) applications. As a result, software artifacts created using the NVIDIA Enterprise AI Factory can be housed in the JFrog Software Supply Chain […]
DevEx Got You This Far: What’s Next for True DevSecOps Maturity?
The journey toward integrating security into the fast-paced world of DevOps has seen significant strides, largely thanks to a much-needed focus on the developer experience (DevEx). Collectively, the AppSec community and industry have moved mountains in making security tools less intrusive, integrating them into developer workflows, and acknowledging that developers need security as a help, […]