

Salt Security Unveils Platform to Secure APIs
Salt Security, fresh off raising an additional $10 million in funding, announced a platform that promises to advance the state of DevSecOps by making it possible to detect when application programming interfaces (APIs) are being probed by cybercriminals looking for weaknesses to exploit. Salt Security CEO Roey Eliyahu said the Salt Security API Protection Platform employs […]
IoT, Not People, Now the Weakest Link in Security
Do a quick search on “people weakest link” and you’ll see a raft of articles in which cybersecurity experts and computer scientists point to employees or end users as the biggest vulnerability. No doubt, people do silly (or outright abusive) stuff and open the door for a variety of enterprise security problems. Spoiler alert: There’s […]
How to Turn Your DevSecOps Shift into Your ‘Pixar Moment’
If you have worked in security as long as I have, you have seen that vulnerabilities persist, despite years of attempts to fix them without changing how the organization operates. One of my all-time favorite leadership quotes comes from the first stockholder meeting after Robert Iger, the CEO of Disney, bought Pixar. “The riskiest thing […]
DevOps Chat: Identity Management with ForgeRock’s Peter Barker
Two megatrends for 2019 and beyond is scale and automation. The identity management space is a perfect example. Considering all of the IP-enabled devices (machines) coming online and the billions of people and their identities, managing these billions and billions takes systems that will redefine scale and, almost by definition, have to be automated. Enter […]
Blame Replaces Strategy: Enterprise IT War Rooms Causing Incalculable Losses
The concept of a “war room” is time-honored. One of the early examples is the Churchill War Rooms, an underground bunker that allowed Britain’s leaders to plot the allied route to victory during World War II. British Prime Minister Winston Churchill, as plain-speaking and self-assured as ever, said, “This is the room from which I […]
Building Amazing Apps, Part 1: Optimizing the Front End
There are millions of apps available today, and it’s incredibly easy for any user to download and install any of them with just a few taps on a screen or click of a mouse. If you want to build and deliver an app that will amaze users, you need to be able to differentiate from […]
Best of 2018: 5 Open Source SIEM Tools Worth Checking Out
As we close out 2018, we at devopsy.kinsta.cloud wanted to highlight the five most popular articles of the year. Following is the second in our weeklong series of the Best of 2018. Security information and event management (SIEM) is the cornerstone of IT security. All other network solutions are merely data flows that feed […]
What It Really Takes to Build Compliant Apps
If you search online for “software compliance,” you’ll be met with a seemingly endless lineup of blog posts, how-tos and explainer articles promising to tell you everything you need to know about writing and deploying software in a compliance-friendly manner. Some of those are good resources, especially the ones that delve into meeting specific compliance […]
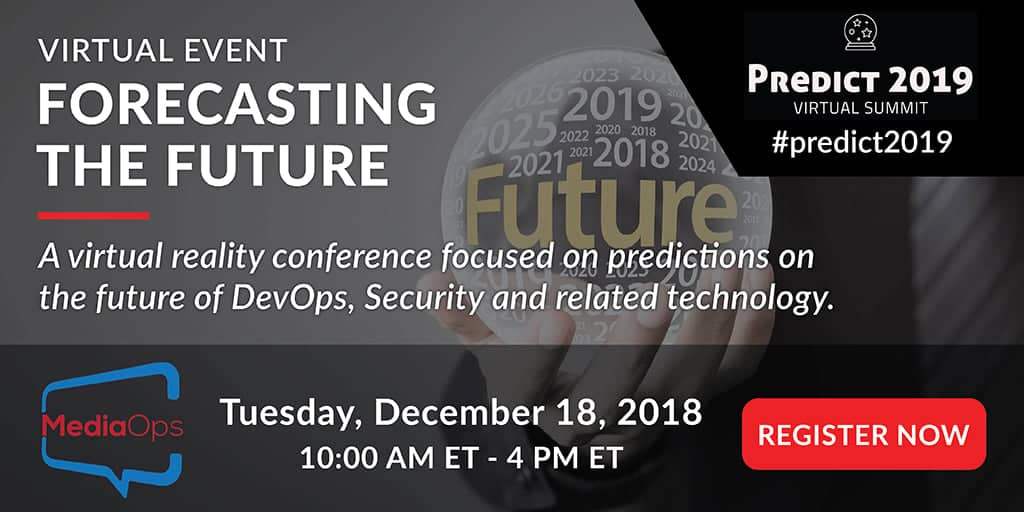
Today: Predict 2019 Virtual Summit
Predict 2019 Virtual Summit is finally here! The summit is happening today, Tuesday, Dec. 18 at 10 a.m. Eastern. Don’t miss the opportunity to hear from Mirco Herring, Rich Mogull, John Willis, Chenxi Wang and other industry luminaries as they offer their DevOps and security predictions for 2019. If you have already registered, then go here […]
How to Become a DevSecOps Engineer
The popularity and success of DevOps means it’s now an increasingly common feature in IT job descriptions. One of the most important roles within DevOps, however, is the Security Engineer or DevSecOps Engineer. This deeply rewarding career requires a specific technical skill set, current knowledge of cybersecurity trends and a decent amount of experience. Perhaps […]
DevOps Chat: Promoting Innovation at the RSA Conference
RSA Conference is where the world comes to meet Security. For the last 14 years, the Innovation Sandbox Contest was where you could find out what the up and coming companies in security were up to. This year RSAC is doing something else in addition. The Launch Pad is where to come to if you […]
DevOps Chat: DevSecOps with Signal Sciences’ James Wickett
James Wickett is the man to go to for DevSecOps. The founder of the Rugged DevOps movement, which has merged into the DevSecOps group, James is one of the most knowledgeable people on the subject of DevSecOps. In this DevOps Chat, James shares his views on what’s on the horizon for DevSecOps and the most […]
The State of Web and Mobile DevSecOps
As the leaders in coverage of the DevOps world, the reporters here at devopsy.kinsta.cloud are constantly pressed upon to convey the true state of DevSecOps at any given moment in time. We try to dig up the state of the union by asking important questions of IT executives, DevOps champions, security leaders and other pundits. […]
5 Questions to Ask When Choosing a Cloud-Native Security Platform for DevOps
If you work in DevOps, you’ve likely heard the mantra that DevOps success is all about the right people, tools and processes. Below, we take a look at how you can address the “tools” part of that equation when it comes to security. Specifically, we’ll discuss which questions to ask and what features DevOps teams […]
How Secure is Open Source for DevOps? 5 Considerations
Open source libraries and frameworks have important roles to play in a DevOps culture that emphasizes shorter development life cycles, collaboration and innovation. However, it’s vital not to neglect the security of these open source components. This article discusses the use of open source in DevOps and gives you five things to consider in terms […]
DevOps and Security: Focus on Importance
Why have I written “DevOps and Security” and not DevSecOps or one of the other names that floats around? Because this post is aimed to apply to everyone—not just those far enough along to have melded some of their security practices into DevOps. Note: After I wrote this article but before I posted it, Bill […]
3 Tips to Build A DevSecOps Organization
For organizations undergoing digital transformation today, modernizing the existing environment can present serious challenges when it comes to security. Whether you’re dealing with a transition from legacy to cloud or hybrid models, or shifting from ITIL and waterfall methodologies to DevOps, the increasing number of technologies and complexity mean you need to rethink your security […]
Are Developers Your First Line of Security Risk or Defense?
Every organization on the planet, whether public or commercial, is facing an ongoing challenge: to exist in an increasingly digital space. Past products must transform to meet the digital expectations of their customers, and new products must be built with “digital-first” frameworks in mind. After all, if they fail to meet these expectations, there’s almost […]
DevOps Chat: Managing Apple Devices with Fleetsmith
Managing Macs, iPhones, iPads and other Apple devices at scale is not something really native to iOS or OSX. Enter Fleetsmith. In sort of a Puppet-meets-Apple environment, the Fleetsmith team automates configuration, management and security of your Apple devices. In this DevOps Chat we sit down with Fleetsmith co-founder and CEO Zack Blum and company […]
How DevSecOps Can Help Avoid Catastrophic Breaches
Earlier this year, Tesla’s Cloud was hijacked and used to mine cryptocurrency, exploiting a vulnerability in the company’s Kubernetes cluster. A mountain of FedEx data was recently exposed, affecting 119,000 individuals. The Equifax breach garnered international attention after an estimated 145.5 million Americans were jeopardized. In other news, we’ve reported on how the Vine Docker […]
Twistlock Releases Cloud Discovery Open Source Tool for Cloud Native Services
A simple, powerful way for audit and security practitioners to discover all ‘unknown unknowns’ across cloud environments PORTLAND, Ore., Nov. 13, 2018 /PRNewswire/ — Twistlock, the leader in container and cloud native cyber security, today announced the release of the open source Cloud Discovery tool. Cloud Discovery gives enterprise infrastructure, operations, and security teams the ability to easily understand and […]
DH2i Launches DxOdyssey for Zero Trust Hybrid/Multi-Cloud Security
DH2i’s DxOdyssey Set to Disrupt the Multi-Billion Dollar Cloud VPN Market DH2i to Demonstrate New DxOdyssey Software at PASS Summit 2018 FORT COLLINS, Co. – November 6, 2018 – DH2i®, the leading provider of multi-platform Software Defined Perimeter and Smart Availability™ software for Windows and Linux, today announced the launch of DxOdyssey™, its new network security software […]
DevOps Chat: The State of Software Security with Veracode’s Chris Eng
Every year CA Veracode publishes its “State of Software Security” report, chock full of research about how well software is being secured during development and beyond. It’s eye-opening stuff and definitely worth a read for anyone even remotely interested in helping make software more secure. In this DevOps Chat, Chris Eng, VP of research at […]