

Why Is Security Missing in Many DevOps Implementations?
The exceptional and ground-breaking, technology-driven opportunities in today’s digitized age come with significant competitive pressures to transform promptly. Specific demands increase due to continuous repeating in response to customer preferences becomes the more deep-seated expectation. To overcome this issue, organizations are shifting toward DevOps as a medium to deliver innovations quickly. DevOps also promotes innovation […]
DevSecOps Adoption and the Web Security Myth
As DevOps practices have become widespread in the tech community, many people have begun proclaiming the virtues of DevSecOps. As the name implies, DevSecOps is the addition of security into DevOps. Just as DevOps promises better-quality production in less time, DevSecOps promises better security with less time required to achieve and maintain it. DevSecOps has […]
The Road Ahead for Security, DevOps Transformation
Qualys hosted its Qualys Security Conference 19 this week in Las Vegas. Hundreds of attendees from around the world have gathered at the Bellagio hotel to learn more about the current state of cybersecurity and what the future has in store. As you might expect, given the technology landscape today, many of the sessions and […]
Three Ways Developers Can Worry Less About Security
Over the past 10 years, developers have risen in organizational importance. They’ve acquired more tools, power, responsibility and autonomy. As part of that evolution, many developers today want to touch all of the layers of code and have their hands in every tool that’s being built. Known as “mechanical sympathy,” developers are taking increased initiative […]
DevOps Chat: Holistic Kubernetes and Cloud-Native App Security, With StackRox
More than ever, application security is a top priority. Beyond secure coding practices, a holistic app security strategy addresses the full application and infrastructure stack. This includes containers, microservices, orchestration, infrastructure software and the cloud. Bolting on the next security tool may not be the answer. Kamal Shah, StackRox CEO, joins us on this DevOps […]
WhiteSource Extends DevSecOps Reach
WhiteSource has extended its platform that enables developers to more easily address application security issues to provide integrations with GitLab Core and integrated development environments (IDEs) based on the open source Eclipse project. David Habusha, vice president of product for WhiteSource, said these latest extensions extend the reach of the company’s platform for addressing DevSecOps […]
ESG Survey Sees Long DevSecOps Road Ahead
A study published by Enterprise Strategy Group (ESG) in collaboration with Data Theorem, a provider of tools for securing application programming interfaces (APIs) and mobile applications, finds that while a lot of progress has been made in terms of adopting DevSecOps, most organizations still have a very long road ahead before they can claim DevSecOps […]
DevOps Deeper Dive: VMware Transformed
At the VMworld 2019 conference this week, VMware in no uncertain teams made it clear it wants to become a major DevOps force. Following the acquisition of sister company Pivotal Software last week, VMware is moving to build out an application development framework for building and deploying cloud-native applications based on Kubernetes. That effort coincides […]
Why Modernizing Security is Like Visiting a Fast-Food Restaurant
Fast casual restaurants are taking over the food industry. Today’s consumers want quality and speed, and the brick-and-mortar model offering immediate service paired with quality ingredients perfectly fits the bill. It’s the new, modernized dining experience. You can also argue that the same modernization taking the food industry by storm is happening in the security […]
Helping Developers Win in the Shift-Left Revolution
The shift-left revolution is upon us. Just because it’s a cliche, doesn’t mean it’s not true. As software development organizations continue to implement DevOps culture, processes, and tools, developers are adopting the practice of testing and ensuring the security of their applications as early as possible in the DevOps pipeline. This is quite a change […]
GitLab Survey Surfaces Major DevSecOps Challenges Ahead
A report based on a survey of 4,071 software professionals published this week by GitLab, a provider of a continuous integration and continuous deployment (CI/CD) platform, found that while appreciation of the potential value of DevSecOps best practices is high, the ability to implement those practices is uneven at best. According to the survey, half […]
DevSecOps Survey Finds Failure to Communicate
While it’s generally agreed that shifting more cybersecurity responsibility onto the shoulders of developers is a good idea, a failure to communicate across application development and cybersecurity teams has contributed to little progress in achieving DevSecOps. A survey of 1,310 IT decision-makers conducted by the market research firm Vanson Bourne on behalf of Trend Micro […]
5 Ways DevSecOps Can Manage Software Supply Chains
The unbridled use of open source components within the software supply chain is on a major uptick, according to new research. Even as this surge in open source dependencies fuels faster innovation, the study shows that it comes with high cybersecurity costs, as the number of breaches related to these components is similarly on the […]
Why Workload Security Is Not Just for IT Anymore
Once upon a time, workload security (which means making sure an application and its environment are configured and deployed securely) was something that developers didn’t have to think much about. Developers’ only real security responsibility was to write secure code. After they passed the code off for building, testing and deploying, it was someone else’s […]
What is Cloud-Native Workload Protection?
We’re living in a cloud-native age. That means that many of the paradigms that worked in the days of on-premises hosting no longer suffice. Chief among them is security. To thrive in today’s cloud-native world, organizations need to rethink their approach to workload protection and bring it up to speed with cloud-native environments. In this […]
Open Innovation Labs: How Lockheed Brought Better Security to Fighter Jets
How Red Hat’s Open Innovation Labs have helped accelerate Lockheed’s software development for the F-22 Raptor As the key government contractor charged with helping the U.S. Air Force keep its F-22 Raptor jets in fighting trim, Lockheed Martin Aeronautics increasingly values software delivery speed as much as engine speed. So much of the continued evolution […]
4 Steps to Introduce DevSecOps to Database Development
Although DevOps was implemented within application development, there is a growing awareness that including the database within DevOps processes is vital to success. We live in a data-driven world and many front-end applications use a database at the back end to collect, process and store customer and user data. The faster development of applications that […]
Survey Finds Mixed Progress on DevSecOps
A survey of 5,558 IT professionals published today by Sonatype in collaboration with CloudBees, Carnegie Mellon’s Software Engineering Institute, Signal Sciences, 9th Bit and Twistlock finds 27 percent of organizations have mature DevOps practices in place, while another 48 percent are still working on improving them. Despite the DevOps works that remains to be accomplished, […]
DevOps Chat: AppSec and DevSecOps with Contrast Security’s Jeff Williams
I have known of Jeff Williams in the security industry for more than several years. He is a well-respected thought leader in AppSec and OWASP. I finally got a chance to catch up with Jeff and talk with him about Contrast Security, the company he co-founded and how it is helping. In this DevOps Chat, […]
DevOps Chat: Repos and Nexus Firewall Access, with Sonatype
There are really only two repositories of any scale for software components today: the Nexus repo managed by Sonatype and the Artifactory artifact repo managed by JFrog. Up until now they were separate and apart, and working with one was independent of another. In a big move toward keeping DevOps open and secure, the Sonatype […]
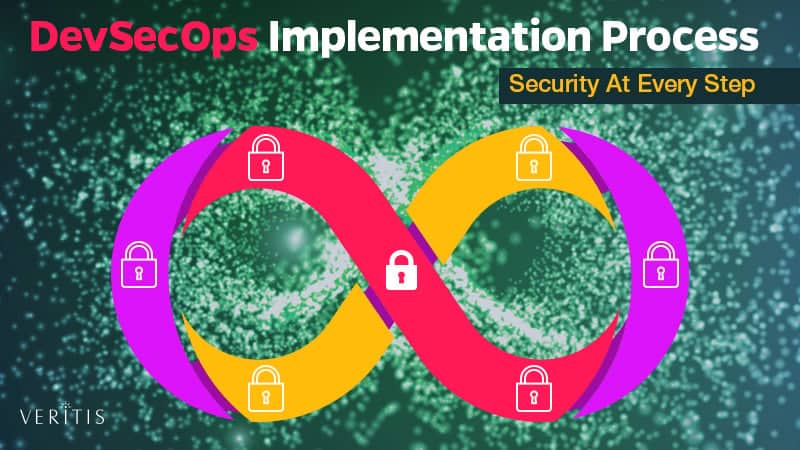
DevSecOps Implementation Process and Road Map – Security at Every Step
DevSecOps is changing our perspective toward security and is equipping us to deal with its challenges in an intelligible manner. The systematic approach of DevSecOps helps us add value to our business processes while ensuring security. Here’s a summary of the key inputs and a recipe for a successful software development project. Implementing DevSecOps with […]
Fail Fast: How Shifting Security Left Speeds Development
How DevSecOps can help organizations increase security, move faster and save money With developers under constant pressure to create more software in less time, the last thing you need is for your code to fail at the end of the development lifecycle. No developer wants to create inoperable or insecure code. We know that most […]
How Software Outsourcing Can Empower Digital Transformation
Businesses are constantly readjusting themselves to become more agile and innovative while maximizing their opportunity in today’s digital economy. This is especially true for up-and-coming businesses with limited budgets that need to think ahead of the curve to find additional resources to fuel their digital transformation. Software outsourcing is no longer perceived as a choice […]