

Adopting Shift Left Testing in Software QA
I am often asked to recommend best practices for building software testing programs. The problem is that it depends on your definition of “best.” What works for an innovative startup developing software and deploying agile development sprints is not necessarily going to suit an established public company launching a new web product. The software development […]
Where Does Your Data Go?
One of the most interesting developments in security and compliance in recent years is the ability to follow a piece of data through an application from input to consumption and see each bit that touches it. For me, the reason this is so interesting is that it allows postmortems to actually determine exactly what was […]

ShiftLeft Appoints Prevention-First, Cybersecurity Visionary and Artificial Intelligence/Machine Learning Pioneer Stuart McClure as Chief Executive Officer
Serial Entrepreneur, Cybersecurity Leader and Industry Veteran joins ShiftLeft to Drive Growth and AI/ML Innovation Globally Santa Clara, CA, August 2, 2022 — ShiftLeft, a disruptor and innovator in the world of DevSecOps and NextGen SAST and SCA, today named Stuart McClure as CEO. With more than 30 years in security, vulnerabilities and prevention technology, […]

ShiftLeft Report Reveals State of Application Security
A report published today by automated application security testing platform ShiftLeft found only one in three applications has an attackable vulnerability. The report also found organizations that prioritized their remediation efforts based on the level of actual threat are fixing 76% of those vulnerabilities within two sprints lasting 12 days, on average. Based on millions […]
What the New OWASP Top 10 Changes Mean to Devs
The open web application security project (OWASP) recently updated its top 10 list of the most critical security risks to web applications after four years. It represents the most radical shake-up since the list was introduced in 2003. The changes will undoubtedly have a big impact on how businesses address application security going forward and […]

At Some Point, We’ve Shifted Too Far Left
Those of us involved in DevOps have a tendency to see the world with blinders on. It is rather easy to fall into the “If all you have is a hammer, everything looks like a nail” trap. We have used the phrase “shift left” with the attitude that this is the solution to every problem […]

Threat Modeling as a DevSecOps Practice
Software engineers are always under pressure to build more software, faster. At the same time, there is increasing regulatory and market pressure for secure software that meets users’ and regulators’ requirements for data privacy. This dynamic often puts software engineers at odds with application security or product security teams. In fact, 81% of developer teams […]
ShiftLeft Announces Strategic Investment from and Go-to-Market Partnership with Wipro
Funding from Wipro Ventures is part of a go-to-market partnership to drive ShiftLeft into new markets and verticals Santa Clara, CA, June 16, 2022 — ShiftLeft, an innovator in automated application security testing, announced an investment from and go-to-market partnership with Wipro Ventures, the strategic investment arm of Wipro Limited (NYSE: WIT, BSE: 507685, NSE: WIPRO). […]
Competing Priorities Prevent Devs From Creating Secure Code
The recently released Secure Code Warrior State of Developer-Driven Security Survey revealed that developers continue to wrestle with secure coding practices in a working environment that has long prioritized features and functionality and speed at the expense of security. Of the more than 1,200 developers who took part in the survey, only 14% named security […]

SRE Vs. DevOps: The Wrong Question?
The age-old question about the competition between DevOps and SRE sets up a false dichotomy. DevOps is a methodology while SRE is a team within operations. Although the two are often pitted against one another, developers also embody the skills and the capabilities to implement fixes. Traditionally, application changes were reactive. The process of SRE […]
Shift Left is Only Part of Secure Software Delivery
We’re living in the age of accelerated consumption and delivery. You can get a seemingly infinite selection of products delivered to your door within two days, for free, from thousands of miles away. You can access an endless variety of services online within mere seconds: Movies, music, games, education and even health care. These modern […]
Embedded Connectivity Solves the Right (and Left) Problem
In Steven Bellovin’s book, “Thinking Security: Stopping Next Year’s Hackers,” (2015) he wrote: “Companies are spending a great deal on security, but we read of massive computer-related attacks. Clearly, something is wrong. The root of the problem is two-fold: We’re protecting (and spending money on protecting) the wrong things, and we’re hurting productivity in the […]
Improving Software Security in 2022
The recent Log4j vulnerability showed just how quickly a security bug could disrupt not just an industry, but the entire world. Organizations, especially federal agencies, will always find themselves at some level of risk, but they can also do more to mitigate those challenges. In November 2021, the Biden administration issued a directive through the […]
2022 Will Be the Year of the Cyber ‘Shift Show’
As ransomware continues to plague organizations across industries, remote work continues and innovation brings with it new threat vectors for bad actors to exploit, 2022 is poised to be another messy year in cybersecurity. In July 2021 alone, organizations lost $45 million to ransomware. What’s more, ransomware costs are projected to reach $265 billion by […]
Shift Left: Right or Wrong?
The term DevOps emerged into mainstream software development communities roughly 10 years ago. It represented a combination of tools and techniques which helped solve many pertinent issues of the time, namely responsibility for code in production and lack of a positive feedback loop. As of today, DevOps is a massive movement. It is considered the […]
Secure Software Summit: Exploring Secure Coding Best Practices
In an era where software is dominating the world, the security and quality of code must remain a high priority. Delivering secure and reliable software at a rapid pace is crucial for most organizations today, but it’s not an easy task. What security best practices do organizations put in place to successfully produce secure software? How should DevOps teams […]
Best of 2021 – The Next Evolutions of DevOps
As we close out 2021, we at DevOps.com wanted to highlight the most popular articles of the year. Following is the seventh in our series of the Best of 2021. As society continues to recover from the global COVID-19 pandemic and some semblance of normal starts to return, technology continues to move forward. The pandemic […]
Does Shift Left Matter to SREs?
If you’re a software engineer, you’ve likely heard all about shift left, a practice that can streamline certain aspects of software development. But shift left isn’t just for developers. It can be equally valuable for site reliability engineers (SREs). Although the main mission of SREs is ensuring the reliability of software after it has been […]
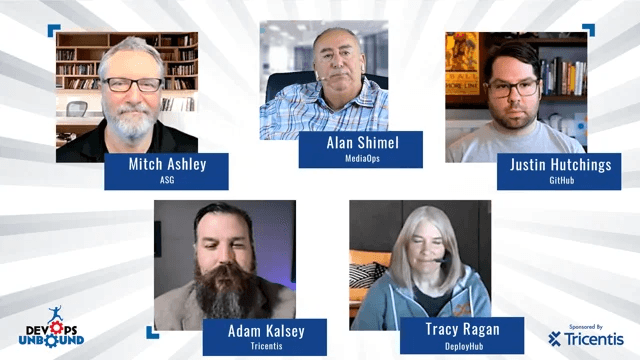
EP 11: Unburdening Developers
Every app development need seems to ultimately fall to developers to fulfill. Build in security. Shift testing left. Provide users cooler, more customized experiences at cloud speed and scale. And do it all faster, of course. How do we accommodate the rising expectations without burning out developers? What can other team members do to lighten the load and allow developers to focus on the creative work they require to thrive? In this episode of DevOps Unbound, hosts Alan Shimel and Mitchell Ashley are joined by panelists Adam Kalsey of Tricentis, Tracy Ragan of DeployHub and Justin Hutchings of GitHub to talk about unburdening developers.
No More Hot Potato: How Collaboration is Key in Application Security
Technology is accelerating at an unprecedented rate and companies with little digital footprint or experience in application security are struggling to keep up. With more and more breaches and vulnerabilities being detected in applications, people are shifting blame like it’s a game of hot potato. But it doesn’t have to be that way. With Shifting […]
How Real-Time Debugging Improves Reliability
When designing and building software, service reliability is always at the top of the list of critical focus areas for development teams. Every team that builds software typically has, either directly or indirectly, service level agreements with their customers. These are, essentially, agreed-upon metrics or performance criteria that teams use to measure and ensure the […]
How to Analyze Your Code for Security Vulnerabilities
Shifting Left 2.0 is a two-day virtual conference taking place from 9 a.m. to 2 p.m. PDT on June 22nd-23rd that dives deep into application security in the modern tech space. Security experts share insights on topics ranging from how to measure AppSec success to what role AppSec plays in digital transformation. Software developers, security […]
Prevent False Positives From Derailing Shift Left
Static application security testing (SAST) tools are designed to balance false positives (incorrect warnings) with false negatives (missed vulnerabilities) primarily because deeper analysis requires more time and computing resources. Both of these are in short supply among developers that are tasked with meeting shorter and shorter product delivery milestones. So, while SAST vendors consider a […]