

Code Security: SAST, Shift-Left, DevSecOps and Beyond
Automation is the key to pushing code security beyond DevSecOps In virtually every industry, developers are dealing with ensuring the safety of their code. Regardless of whether it’s enterprise or applications for automotive, aviation or industrial controls, small systems or large systems, every organization struggles with security. In response, the industry continues to evolve to […]
Why It’s Time for Site Reliability Engineering to Shift Left
By adopting a multilevel approach to site reliability engineering and arming your team with the right tools, you can unleash benefits that impact the entire service-delivery continuum In today’s application-driven economy, the infrastructure supporting business-critical applications has never been more important. In response, many companies are recruiting site reliability engineering (SRE) specialists to help them […]
GitLab Adds Fuzz Testing to DevSecOps Toolbox
GitLab today announced it has acquired Peach Tech, a provider of protocol fuzz testing and dynamic application security testing (DAST) API testing tools, and Fuzzit, a continuous fuzz testing tool, as part of its efforts to advance the adoption of best DevSecOps practices. David DeSanto, director of product for GitLab Secure & Defend, said the […]
Using this Time to Optimize Your Dev Team’s Workflow
As Andy Warhol once said, “They always say time changes things, but you actually have to change them yourself.” This more than ever resonates with the change that companies have found themselves experiencing of late. The more the world embraces digital methods of work, the more that change becomes paramount to a successful workflow. It […]
Who’s Responsible for Security? Apparently, It Depends
More than 10 years after organizations began implementing DevOps, responsibility for security still resembles the proverbial chicken and egg dilemma. GitLab’s 2020 Global DevSecOps Survey asked developers, security team members, operations pros and testers about sole responsibility for security in their organizations. About 28% of developers, 33% of security teams, 21% of ops pros and 23% […]
The DevOps Sweet Spot: Inserting Security at Pull Requests (Part 2)
In part one of this two-part series, I explored how organizations can more effectively automate security quality decisions and discard doing automation for automation’s sake. I shared why security scans need to be faster, more reliable and comprehensive. Only then can security be meaningfully automated into developer workflows without slowing them down. But, the other […]
Better Apps and Better Security When You Shift Left
Tens of thousands of people and hundreds of cybersecurity vendors descended on San Francisco at the end of April. While the RSA Conference was the primary draw, there are a number of peripheral events that go on throughout the week as well, such as the Cloud Security Alliance Summit, the CIO/CISO Interchange, BSides San Francisco […]
Survey Sees Little Progress in Drive to Shift Testing Left
It looks like the drive to shift testing left toward developers to accelerate the development and deployment of applications has stalled. A survey of 102 IT professionals involved in application testing published by Perforce, a provider of testing tools, finds only 18% of organizations test applications solely within their development feature teams. The rest continue […]
Shifting Left – But How Far Left Do Companies Need to Go?
For developers, there’s nothing more satisfying than looking at a web app or service and being able to say “I made that.” Or at least part of that. Being able to develop code that works and helps millions of people do what they need to get done is an excuse for bragging rights. But the […]
Practical Approaches to Long-Term Cloud-Native Security
There is no shortage of advice out there about how to secure modern, cloud-native workloads. By now, most developers and IT engineers who work with cloud-native deployments have heard all of the mantras about DevSecOps, shift-left security, multi-layer defenses and dynamic baselining (to name just some of the key concepts that are driving IT security […]
How Organizations Benefit from AWS App Patterns
As a startup, an organization thrives by breaking rules, challenging the status quo and standing for all that is against the norm. The same rules don’t apply once the same organization grows, matures, becomes popular, gains a long list of clients and expands to a global footprint. With scale and growth comes the need for […]
Rethinking Data Management in a DevOps Environment
You often hear data is the new oil. This valuable, ever-changing commodity has begun to play a starring role in many cloud-native applications. Yet, according to a number of DevOps teams, data issues continue to plague their efforts to continuously integrate, test and deploy frequent software releases. More specifically, issues with persistent data (and its […]
Quality Engineering Has DevOps and Agile in the Driving Seat
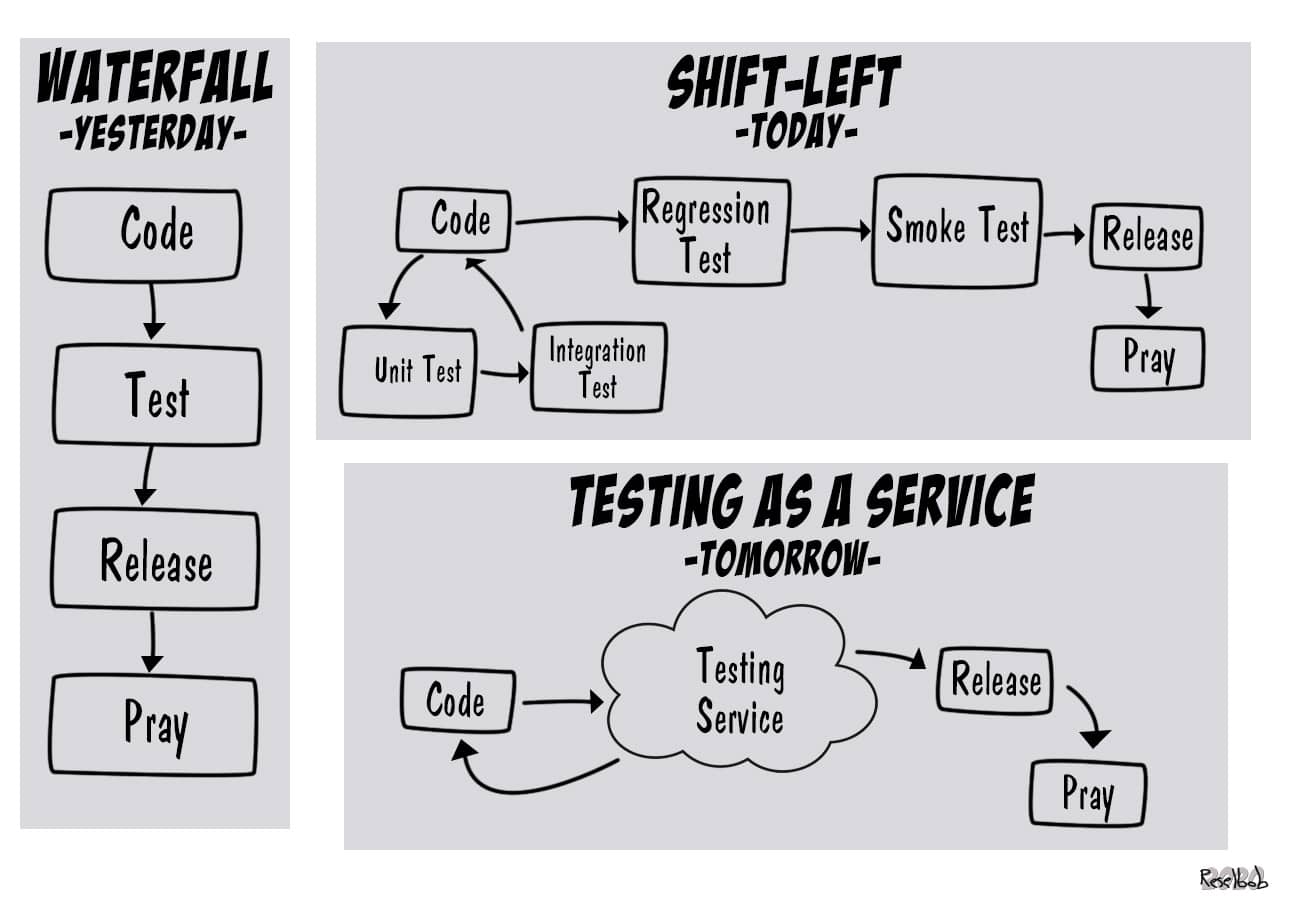
As opposed to the traditional software development lifecycle (aka waterfall), today’s Agile and DevOps-based software development process is more outcome-oriented. The unrelenting pace of the changing market landscape has made the hybrid, Agile plus DevOps way of software development absolutely critical in addressing customer demands and staying competitive. The focus on Agile and DevOps is […]
Trend Micro Partners With Snyk to Advance DevSecOps
Trend Micro today announced an alliance with Snyk through which alerts about vulnerabilities in open source code will be passed on to the tools Trend Micro makes available to apply virtual patches to both monolithic and microservices-based applications. Snyk provides a tool that identifies and fixes vulnerabilities and license violations in open source dependencies and […]
When Shift Right is Shift Left
In some areas of IT, we utilize the idea of shift right quite a bit. Testing and security are two areas where it comes up often. The idea is that tracking late in the process–usually while the application is in production–leads us to find more insidious issues that might have remained hidden, and gives us […]
Shift-Left Testing, Continuous Integration and the Mainframe
“Mainframe” is one of the oldest terms in tech. “Shift-left” is much newer. You may not think, then, that mainframes and shift-left testing have much in common. But you’d be wrong. Shifting testing to the left can deliver tremendous benefits, even in the context of mainframe applications. Let us explain. What Is Shift-Left Testing? Shift-left […]
Helping Developers Win in the Shift-Left Revolution
The shift-left revolution is upon us. Just because it’s a cliche, doesn’t mean it’s not true. As software development organizations continue to implement DevOps culture, processes, and tools, developers are adopting the practice of testing and ensuring the security of their applications as early as possible in the DevOps pipeline. This is quite a change […]
How Continuous Testing Advances Your Business Goals
The goals of any successful business fit into two broad categories: driving higher revenue and greater operational efficiency. Finding solutions to achieve both of these is an organization’s goldmine. Considering the ease of access to new, alternate products from developers across the globe, competition continues to grow. In the software industry, customer expectations magnify cut-throat […]
6 Traits That Define DevSecOps
How do we define DevSecOps? A combination of DevOps and security is readily apparent, but the philosophy goes much deeper. In a recent eBook, The State of DevSecOps, we asked industry experts to define what DevSecOps meant to them. Below, we’ve condensed their answers into five core attributes. Following these principles, CIOs or CTOs now […]
Self-Service Workload Protection for DevOps Teams
Everyone (or almost everyone) in the DevOps world likes to talk about the importance of security. But too often, these DevOps security conversations end with generic recommendations such as, “Follow the OWASP Top 10.” Don’t get me wrong—reference frameworks such as OWASP are great resources for helping to guide DevOps security. But it’s usually far […]
Building a Security Feedback Process for DevOps
The last few years have seen some major slip-ups in the security space among all major cloud providers, resulting in uncertainty and speculation. That’s understanding; cloud security is an extremely complicated subject as enterprises build and deploy applications faster than ever before to keep up with business requirements. Most of the security issues that occur […]
Shift Left Without Fear: The Role of Security in Enabling DevOps
It’s the age of DevOps, and we all want to shift left, which refers to the idea of performing processes earlier in the CI/CD cycle. That includes security checks and audits. By starting security operations earlier in the delivery pipeline, it becomes easier to find problems, and teams have more time to address them before […]