

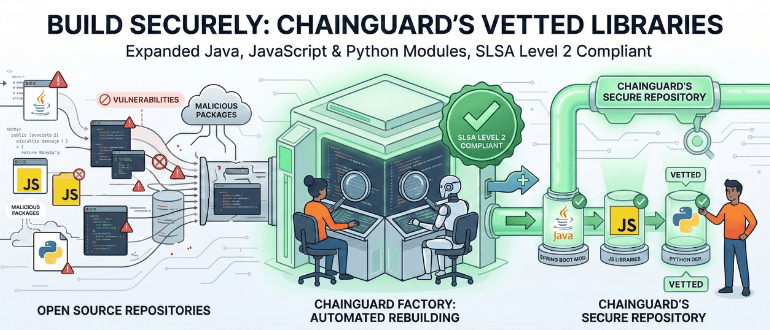
Chainguard Expands Repository to Add More Secure Open Source Libraries
Learn how Chainguard is strengthening software supply chains by expanding its secure repository of Java, JavaScript, and Python libraries, enabling DevOps teams to access components compliant with SLSA framework standards.
Software Supply Chain Threats Are on the OWASP Top Ten—Yet Nothing Will Change Unless We Do
Software supply chain security is steadily moving to the forefront of cybersecurity conversations. In the past, it has been overshadowed by a focus on malware outbreaks, ransomware, endpoint protection, and application vulnerabilities. That changed this month, when OWASP elevated software supply chain failures to third place on its 2025 Top 10 list. The OWASP Top […]
Checkmarx Acquisition of Tromzo Accelerates Plan to Apply AI to Application Security
Checkmarx accelerates its AI-driven DevSecOps strategy after acquiring Tromzo, integrating AI agents to automate application security across the software development lifecycle.
Endor Labs Adds AI SAST Tool to Discover Vulnerabilities in Code
Endor Labs launches an agentic AI-powered SAST tool that drastically reduces false positives, identifies deeper code flaws and helps DevSecOps teams secure AI-generated code across 40+ languages.
JFrog Adds Ability to Track Usage of AI Coding Tools
JFrog introduces AI-Generated Code Detection and Shadow AI Detection tools to identify AI-created code, track model usage, and enhance DevSecOps governance across software supply chains.
DevSecOps in Practice: Closing the Gap Between Development Speed and Security Assurance
In the world of modern software development, speed is king. Teams are under constant pressure to release features, fix bugs and stay ahead of competitors. Yet, as development velocity increases, so does the risk of introducing vulnerabilities — an inconvenient truth that security teams have been sounding alarms about for years. This tension between speed and […]
Establishing Visibility and Governance for Your Software Supply Chain
Asset visibility and cloud governance start with SBOMs, VEX, and provenance tracking. Learn how to secure your software supply chain.
Git Services Need Better Security. Here’s How End-to-End Encryption Could Help
A new study from the University of Sydney, UESTC, and Google introduces efficient end-to-end encryption for Git services like GitHub and GitLab. Learn how this breakthrough could secure your code repositories without slowing development.
Build vs. Buy: What it Really Takes to Harden Your Software Supply Chain
When it comes to securing the software supply chain, engineering teams often assume that the choice between building their own hardened images or buying a solution is straightforward…until they try to build the images themselves. As the programmer’s credo goes: “We do these things not because they are easy, but because we thought they’d be easy.” The decision […]
How GitHub Plans to Secure npm After Recent Supply Chain Attacks
GitHub strengthens npm security after Shai-Hulud worm attack with mandatory 2FA, granular tokens, and trusted publishing to protect the open source supply chain.
Nominations Are Open: DevOps Dozen 2025
The DevOps Dozen 2025 awards are open. Celebrate community leaders and tools shaping DevOps, from AI to platform engineering and supply chain security.
Survey Surfaces Significant Lack of Visibility Into Software Supply Chain Risks
A global survey of 1,500 C-suite and senior executives published today finds about half (49%) concede their organization lacks the visibility needed to fully understand – or even identify – software supply chain risks.
Teleport Unifies Infrastructure and Application Workload Security
Teleport today added an offering that makes it simpler to declaratively secure IT infrastructure and workloads using short-lived X.509 certificates.
Harness Merges with Traceable to Provide Integrated DevSecOps Platform
Harness today announced that Traceable will be merged into the company to create a combined company that will further advance the adoption of best DevSecOps practices across the software development lifecycle (SDLC).
GitLab Fixes Security Flaw That Lets Attackers Run Pipeline Jobs
If left unpatched, the vulnerability in the code repository could let threat actors run malicious code and access sensitive information.
Why DevOps is Key to Software Supply Chain Security
Organizations can maintain their DevOps momentum while protecting the software supply chain by shifting security left.
Techstrong Research: Combatting CI/CD Security Anti-Patterns
Techstrong Research finds the imperative to secure the software supply chain and CI/CD pipelines is undeniable and urgent.
Checkmarx Report Details Havoc Caused by ‘Everything’ Package on NPM Registry
A Checkmarx report details an ‘Everything’ package distributed via the NPM registry that cripples any machine used to download it.
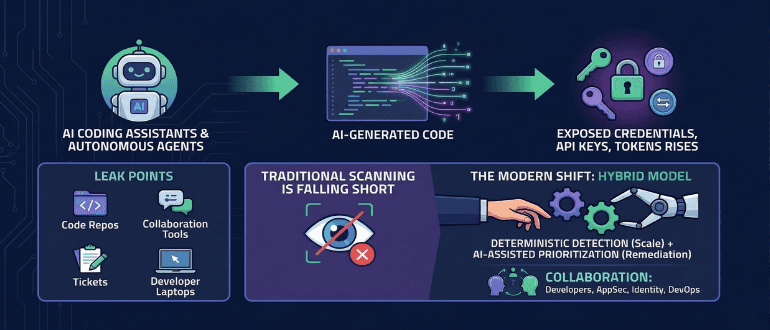
GitGuardian Adds Tool for Discovering Secrets in Public Repositories
GitGuardian added a tool that makes it possible for DevOps teams to search GitHub repos to determine if secrets have inadvertently found their way into other apps.
Summit Highlights Open Source Software Security Progress
The OpenSSF hosted a Secure Open Source Software (SOSS) Summit 2023 event during which it made available a Secure Open Source Software Vision Brief 2023.
Stop Leaking Secrets!
All too often, software teams trip over complexities and inadvertently leave secrets exposed in private and public software repositories.
I Guess This is Growing Up: Devs and CISA’s Secure-by-Design Guidelines
With the downward pressure of a global recession, inflation and general post-pandemic turbulence underpinning disruption to multiple facets of life, it seems only fair that we in the IT, software and security industry would eventually feel the winds of change, too. We have rolled with the punches of escalating cybercrime and data breaches; the collective, […]
The Role of SBOMs in Software Supply Chain Security
The software supply chain has become increasingly complex and dynamic with the rise of cloud computing, open source software and third-party software components and APIs. Widespread damage can occur if third-party APIs, cloud services, SDKs and open source software have security flaws. As a result, software supply chain security has emerged as a critical concern […]