

DeepSeek Wants Coding Agents to Stop Waiting for Instructions
DeepSeek’s open-source Super-Agent prototype replaces isolated coding sessions with an always-on system that coordinates multiple AI workers, responds to development events and can initiate bug fixes without direct prompting. For DevOps teams, the promise of autonomous development brings new challenges around permissions, pipeline security, observability and code verification.
Endor Labs Adds AI Tool to Generate Fixes for Open Source Vulnerabilities
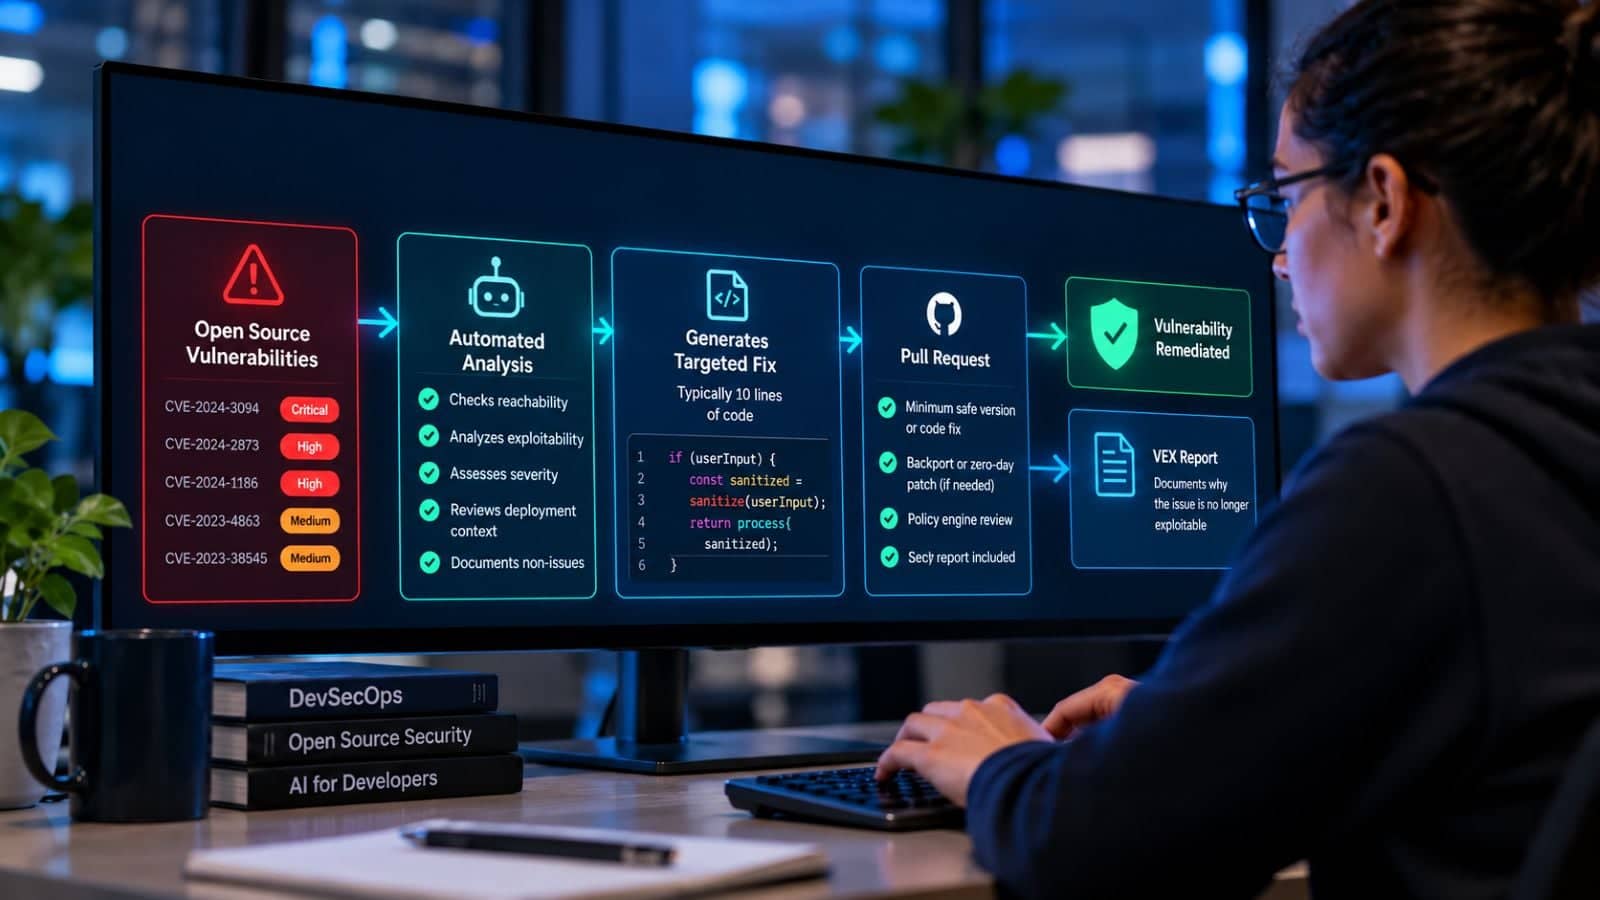
Endor Labs this week added an artificial intelligence (AI) tool to its portfolio that evaluates every reachable open source vulnerability against a code context graph to generate fixes that typically require only 10 lines of code to be generated and applied. Joe Harrington, a principal product manager for Endor Labs, said AURI Fix for Open […]
AI Made Building Apps Easy, but Who Really Runs Them?
A few months ago, a product manager at an agency reached out to us. They had built a client reporting app over a weekend using an AI coding tool and made it live so customers could try it. It worked great until we found that authentication was broken and the app’s admin interface was accessible […]
Claude Writes 180 Million Lines of Proofs to Verify 123 Open Source Libraries
Formal verification has long been the gold standard for software correctness. It has also been too expensive for almost everyone. New research from Anthropic suggests that’s changing. Anthropic’s Frontier Red Team, working with formal methods company Theorem, used Claude to prove security properties in the compiled code of 123 open-source libraries from Google’s OSS-Fuzz project. […]
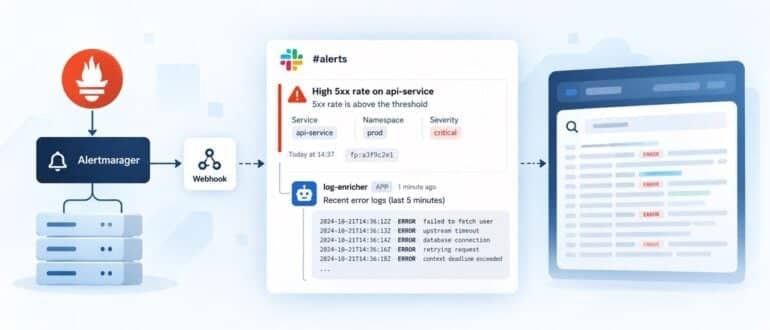
Attaching Evidence to Alerts: an Enrichment Sidecar for Alertmanager
Every on-call engineer knows the ritual. A page lands in Slack: the 5xx rate on a service is above the threshold. The message tells you that something is wrong and nothing about what. So you open Kibana or Loki in another tab, set the time window to the last few minutes, filter by the service, […]
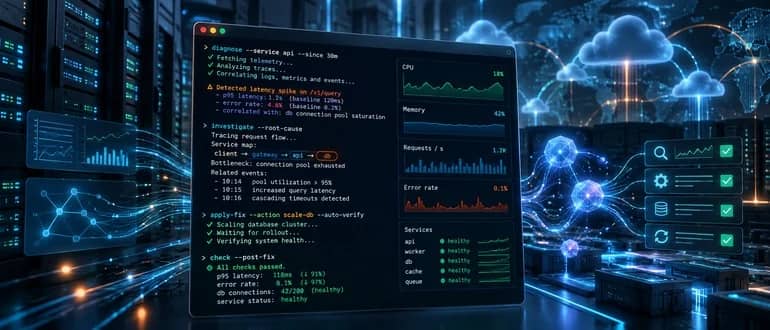
New Relic Debuts Command-Line Observability Tool for Developers and AI Agents
New Relic has unveiled Ground Truth CLI, a command-line tool that enables software developers and AI agents to analyze system performance and verify whether technical issues have been resolved without needing to use dashboards. The release reflects a big shift in enterprise IT as AI agents take on more advanced troubleshooting tasks. Traditional observability dashboards […]
From Software Supply Chains to AI Vulnerabilities: Why Neither Solves Enterprise Linux Security
For nearly a decade, cybersecurity has been dominated by one overarching concern: securing the software supply chain. Organizations invested heavily in Software Bills of Materials (SBOMs), artifact signing, provenance frameworks, reproducible builds, and vulnerability scanners capable of identifying compromised dependencies before software reached production. The software supply chain became the industry’s focal point, accelerated by […]
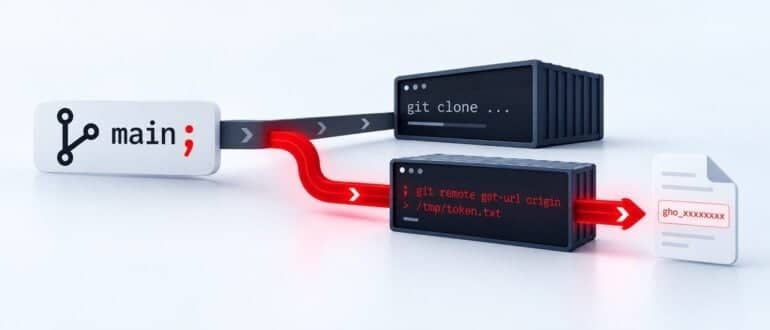
A Semicolon in a Branch Name Was All It Took to Steal an AI Agent’s GitHub Token
AI coding agents don’t just suggest code anymore. Tools like OpenAI’s Codex spin up a real container, clone a real repository, and authenticate with a real GitHub credential to get the job done — which means every agent your team wires up is also a new privileged identity, holding real access, running with comparatively little […]
Your DevOps Pipeline Is Already a Sustainability Program
During my doctoral research on modern engineering practices and operational efficiency, one pattern kept surfacing that I did not expect to find. The engineering teams making the most measurable progress on sustainability were not the ones that had appointed green committees. They were the ones running tight DevOps discipline: right-sized fleets, lean pipelines, tuned alerting, […]
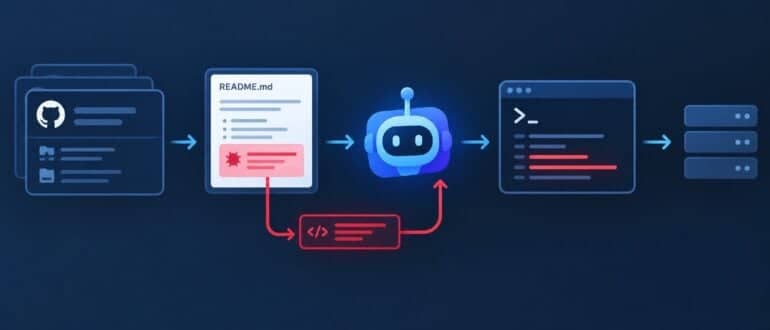
When AI Coding Agents Become Malware Delivery Systems
AI coding agents are becoming part of everyday development work. Developers use them to find libraries, configure projects, troubleshoot installation problems, and set up new tools. An agent can search GitHub, read project documentation, and run commands without the developer having to work through every step manually. That convenience is creating another security concern for […]
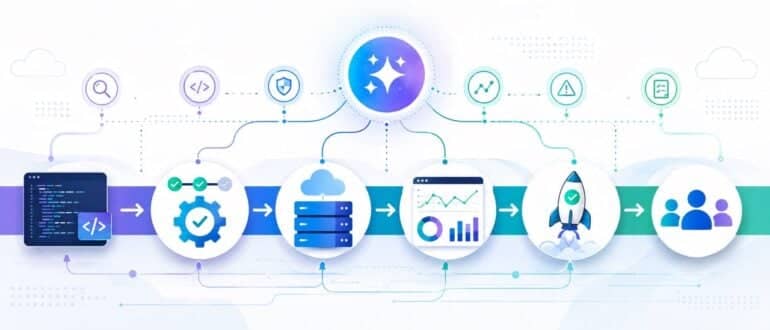
The Rise of AI-Native DevOps: How AI Is Reshaping Software Delivery in 2026
For years, DevOps had a pretty straightforward mission: help teams ship reliable software faster by getting development and operations folks working together. Tools like automation, continuous integration, continuous delivery, infrastructure as code, and better observability have all been key pieces of the puzzle. But now, things are shifting again. This time, artificial intelligence is changing […]
Open Source Code Just as Secure as Proprietary Software—If You Manage It Right, Says CISA
Open source can be just as safe as proprietary software, though government agencies (and private enterprises) should take additional measures to secure it properly, according to a new guide published by the U.S. Cybersecurity and Infrastructure Security Agency (CISA). The report, “Open Source Software: Security Principles and Practices,” provides with guidance to help agencies comply […]
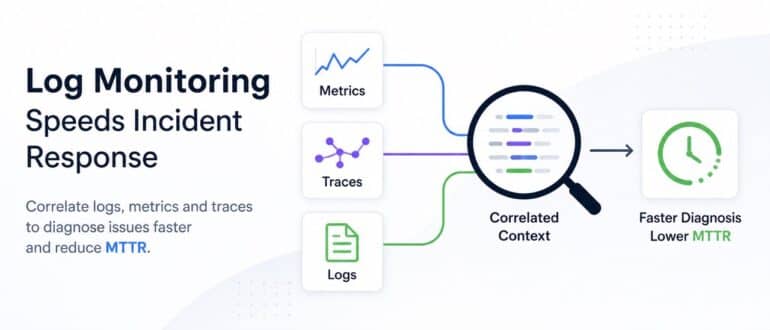
Why Log Monitoring Is the Missing Link in Most Incident Response Workflows
Modern engineering teams have invested heavily in observability. Dashboards are populated, alerts are configured, on-call rotations are set. Yet when production incidents occur, the average time to resolution hasn’t dropped nearly as fast as the tooling has improved. The reason, in many cases, comes down to one overlooked gap: logs aren’t being used the way […]
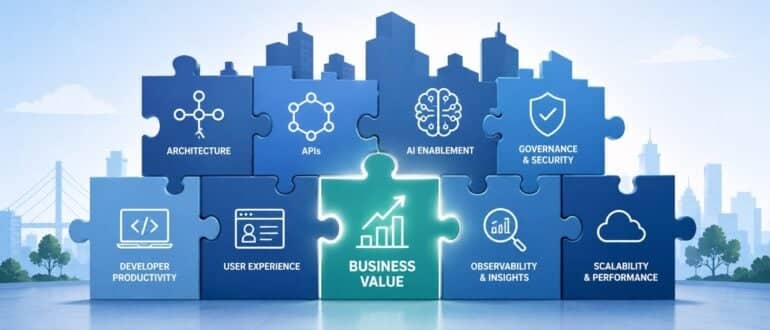
The Innovation Puzzle 2.0: Connecting Vision and Value
The tech landscape constantly evolves, making it tempting to chase every new trend. Ironically, in today’s business world, the word “innovation” has become almost synonymous with technology adoption. Yet after years of leading digital transformations, I’ve learned that sustainable innovation isn’t about having the latest technology—it’s about solving business problems and delivering measurable impact. In […]
Zero Trust Starts at the Code: Building Secure Systems with PKI and DevOps Automation
When a certificate expires, it can take down a production system, and teams usually only find out after something goes wrong. These issues are hard to catch because they rarely trigger alerts. Expired certificates often remain unnoticed in a config file or an old key until they cause trouble. Enterprise apps are no longer single, […]
Building CI/CD Pipelines for On-Prem Azure DevOps: What the Cloud Docs Don’t Tell You
The engineering that makes on-prem CI/CD reliable is invisible when it works. When it does not work, the failures are subtle and the documentation is thin.
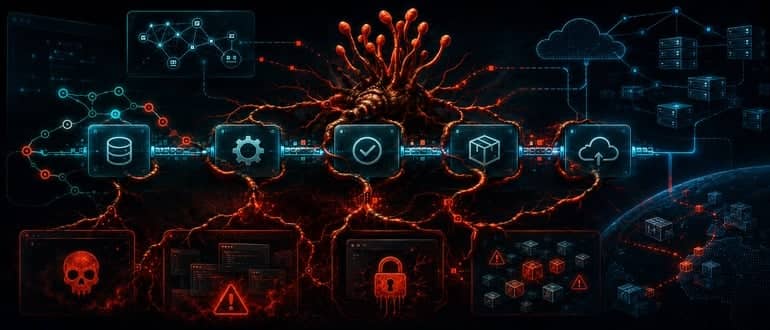
Novee Uncovers Cordyceps: The Latest Threat to CI/CD Pipelines
A newly discovered supply chain security flaw is once again putting a spotlight on inherent weaknesses in CI/CD pipelines and the growing interest among cyberthreat actors to exploit them. Security researchers with Novee, an AI penetration testing platform provider, wrote about Cordyceps, an exploitable pattern in the open source supply chain that can allow attackers […]
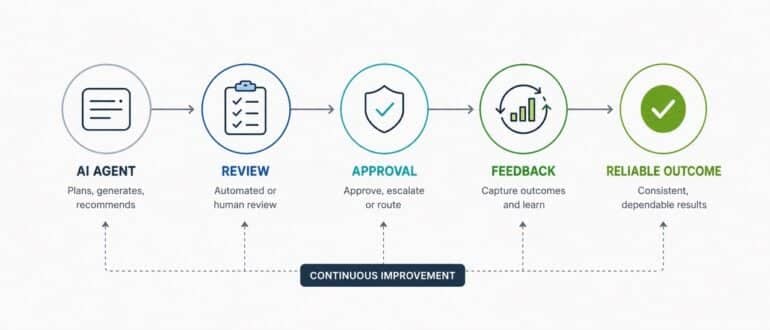
Reliability Comes From the System, Not the Agent
One of the most common questions executives ask right now sounds straightforward: is the agent reliable enough yet? It feels like the right place to start, but the framing quietly points people in the wrong direction because it assumes something about reliability that has rarely been true in complex systems. When people ask whether an […]

Modernization Is Not Migration
Modernization worked only if the platform became easier to change, easier to understand and safer to run under pressure. That is not a philosophical position — it is a measurable one.
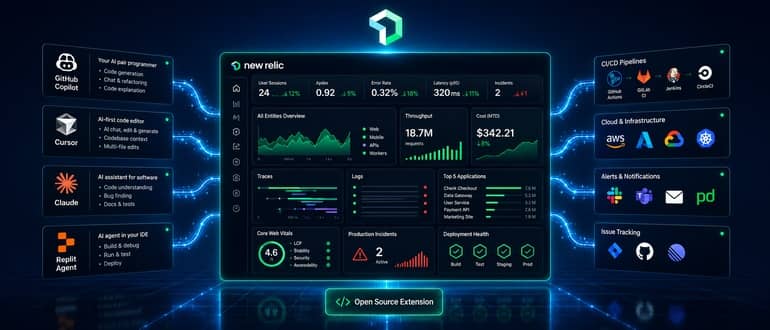
New Relic Adds Open Source Tool to Observe AI Coding
New Relic has made available an open source extension to its observability platform for coding tools at no additional cost. Nic Benders, chief technical strategist for New Relic, said the New Relic AI Coding Observability capability will make it simpler for DevOps teams to centrally monitor usage of a diverse range of artificial intelligence (AI) […]

Why Your Observability Stack Is Costing You More Than Your Cloud Bill
There’s a pattern playing out across engineering teams right now that nobody talks about openly: the tool meant to reduce operational complexity has quietly become one of the biggest line items on the infrastructure budget. Observability spending is out of control, and for most teams, it’s not because they’re monitoring too much. It’s because they’re […]
npm v12 Is Coming in July — Here’s What Developers Need to Do Now
For years, running npm install meant trusting that whatever code got pulled in would behave itself. That trust was often misplaced. Starting in July 2026, npm v12 changes the rules. Install scripts won’t run automatically anymore. Neither will dependencies be pulled from Git repos or remote URLs. All of it becomes opt-in. This is a […]
Security Flaw in Claude Code Illustrates the Risk of AI in Developer Workflows
AI coding agents are reshaping software development—but they’re also expanding the attack surface. Researchers uncovered a now-patched vulnerability in Anthropic’s Claude Code GitHub Action that could have enabled prompt injection attacks to expose CI/CD secrets, API keys, and credentials. As AI agents gain autonomy in development workflows, organizations must treat untrusted inputs as hostile and rethink CI/CD security models. Natural language is becoming executable code—and attackers know it.