


Talentica Software Unfurls Managed AI Service to Optimize Software Delivery
Talentica Software this week launched a managed software delivery service that leverages artificial intelligence (AI) to enable DevOps teams to deploy applications developed using AI coding tools at scale. Company CTO Manjusha Madabushi said the DevX AI Pods service makes use of a set of AI agents that Talentica has trained to provide the context […]

New npm Threat Bypasses Install Script Protections
A malicious npm package that has been downloaded millions of times comes with a new way of spreading the malware that makes it easier to bypass security protections, say researchers with security vendor Checkmarx. Rather than using more common preinstall or postinstall scripts, the bad actors instead created a malicious package – indexed-btree – that […]

Why Your CI/CD Pipeline Is Your Most Unprotected Attack Surface
CI/CD pipelines often hold privileged credentials, execute third-party code and connect directly to production, making pipeline security one of the most overlooked risks in modern DevOps.
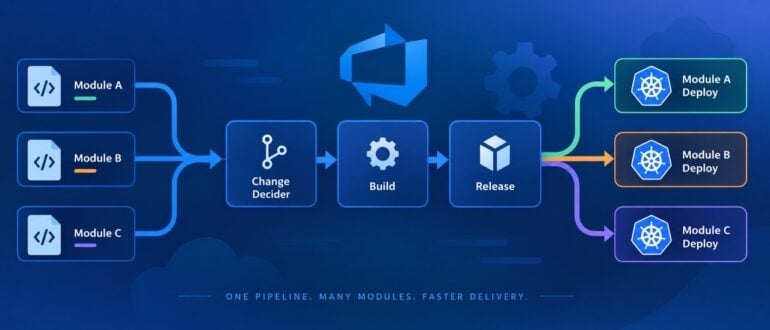
How I Consolidated Duplicate Delivery Pipelines With Parameters and Build Tags
Two modules in a repository had near-identical Azure DevOps build and release definitions. A third would have required another pair. The delivery chain used five definitions: one change decider, two builds, and two releases. I consolidated it into one decider, one generic build, and one release with a deployment stage for each onboarded module. The […]

Cloudsmith Extends Policies and Controls to Secure Application Binaries
Cloudsmith this week revealed it has expanded the policy management and continuous risk detection capabilities it makes available within its software artifact management platform to now include policy templates, cooldown policies, and expanded evaluation triggers. Alison Sickelka, vice president of product for Cloudsmith, said these additions to the platform will make it simpler to prevent […]

Fast-Moving Shai-Hulud Attack Infects npm Packages with 2 Billion Monthly Downloads
Researchers at Aikido Security and Endor Labs are tracking a fast-spreading supply-chain attack that is compromising a wide range of npm software packages that combined have more than 2 billion installs a month and is stealing a wide range of secrets and other information. According to Ilyas Makari, malware researcher with Aikido, the bad actor […]

Building SOC 2 Compliant CI/CD Pipelines on AWS with GitHub Actions
How to design a secure, traceable AWS CI/CD pipeline using separate accounts, centralized ECR, OIDC and immutable image promotion for SOC 2.

FakeGit Targets AI Coding Agents with Malicious GitHub Repos
Threat actors continue to find new ways to incorporate AI into schemes aimed at luring developers into downloading malware from fake repositories. The latest example involves almost 7,600 malicious GitHub repositories that are being used to distribute a loader and an information-stealer. The FakeGit campaign is nothing new, with Oleg Zaytsev, lead security researcher with […]

GitHub API Abuse, ‘Ghost’ Accounts Part of Malicious Efforts to Map Organizations
Datadog researchers uncover months-long overlapping campaigns to scrape data about companies and their developers.

‘HalluSquatting’ Compromises AI Coding Agents to Install Malware, Create Botnets
Hallucinations have been an ongoing problem since OpenAI first introduced its ChatGPT chatbot in November 2022, highlighting generative AI’s tendency to generate plausible but false or misleading information and its inability to just say “I don’t know.” They can lead to embarrassing or uncomfortable moments. However, security researchers in Israel have found that the large […]

How to Build a DevSecOps CI/CD Pipeline on Azure With GitHub Actions
Fix security problems when they’re cheap to fix, which is before the code is deployed. A pipeline that enforces this automatically is what makes that principle real.

North Korea Expands the Reach of PolinRider Supply Chain Attack Campaign
The North Korean-sponsored threat groups behind the long-running fake interview scams targeting developers are expanding the PolinRider supply chain campaign that has escalated over the past several months. Reports from cybersecurity vendors Socket and Rescana found that two groups linked to the Democratic People’s Republic of Korea (DPRK) have published at least 108 malicious packages […]

‘GitLost’ Flaw Lets Attackers Trick GitHub AI Agent Into Leaking Private Repos
Noma researchers again show how easy it is to manipulate AI agents with malicious commands via indirect prompt injection attacks.

A Beginner’s Guide to CI/CD and CI/CD Pipelines
Modern software development moves at a pace that would have been unthinkable a decade ago. Organizations push updates on demand, respond to vulnerabilities within minutes, and integrate new features at a relentless pace. This acceleration is driven by continuous integration and continuous delivery (CI/CD). To understand how CI/CD reshapes the security posture of modern organizations, […]

Novee Uncovers Cordyceps: The Latest Threat to CI/CD Pipelines
A newly discovered supply chain security flaw is once again putting a spotlight on inherent weaknesses in CI/CD pipelines and the growing interest among cyberthreat actors to exploit them. Security researchers with Novee, an AI penetration testing platform provider, wrote about Cordyceps, an exploitable pattern in the open source supply chain that can allow attackers […]
These are 10 CI/CD Pipeline Mistakes That Slow Down Engineering Teams
Continuous software delivery in the digital age depends on CI/CD pipelines, which enable engineering teams to rapidly develop, test, and deploy code while maintaining high usability and consistency across environments.

Mastering the Blast Radius, Deployment Without Fear- Progressive Delivery in Modern DevOps
‘Progressive delivery’ is the modern evolution of continuous delivery, designed to reduce the blast radius of new features and decouple ‘deployment’ (moving code to production) from ‘release’ (exposing features to users).
Shift-Left Performance Testing in CI/CD: A Practical LoadRunner Framework
CI/CD pipelines speed up software delivery, but performance testing is often delayed, resulting in late feedback and costly fixes. Many teams run tests earlier but fail to enforce performance as a deployment gate.

Security Flaw in Claude Code Illustrates the Risk of AI in Developer Workflows
AI coding agents are reshaping software development—but they’re also expanding the attack surface. Researchers uncovered a now-patched vulnerability in Anthropic’s Claude Code GitHub Action that could have enabled prompt injection attacks to expose CI/CD secrets, API keys, and credentials. As AI agents gain autonomy in development workflows, organizations must treat untrusted inputs as hostile and rethink CI/CD security models. Natural language is becoming executable code—and attackers know it.

Why DIY Test Automation Succeeds Its Way Into a Problem
Ask any engineering team if they can build their own test automation framework, and the answer is almost always “yes.” With modern AI tools involved, that answer arrives faster and with more confidence than ever before. In 30 days, a capable team can spin up scripts, automate flows, generate test cases, and show a demo […]

Designing an AI-Powered DevSecOps Guardrail Pipeline Using GitHub Actions
By embedding AI-powered guardrails directly into CI/CD pipelines, organizations can detect vulnerabilities earlier, enforce security policies automatically and accelerate secure software delivery.

Critical Microsoft GitHub Flaw Highlights Dangers to CI/CD Pipelines: Tenable
A critical vulnerability in a popular Microsoft GitHub repository could allow a threat actor to easily exploit its CI/CD infrastructure to run arbitrary code in the repository and gain access to secrets, according to researchers with cybersecurity firm Tenable. In an advisory issued April 21, Rémy Marot, staff research engineer at Tenable, wrote that “by […]
Can Claude Agents Replace DevOps Teams? A Practical Reality Check
Are AI agents replacing DevOps engineers? Explore how tools like Claude are shifting DevOps from rigid automation to autonomous, adaptive systems, and why human judgment remains the critical link in managing system complexity and risk.
Showing the 24 most recent articles. Additional archive pages are not yet available.