
Tag: devsecops
AWS Benchmark Aims to Reduce Number of False Positives Found by AI Vulnerability Scanners
Amazon Web Services (AWS) has developed a benchmark that can be used to test whether a model can distinguish real vulnerabilities from code that looks risky but is actually safe. The Deception ...
Survey: Lack of Confidence in Software Supply Chain Security Runs High
A survey of 400 platform and security engineers in the U.S and United Kingdom (UK), finds nearly three quarters (73%) are either only moderately confident (58%) or not confident (15%) in the ...
GitHub’s Security Autofix Agent Now Remembers What It Fixed
 Tom Smith | | agentic autofix, AI coding agents, AI security, application security, code scanning, CodeQL, Copilot Memory, devsecops, github, GitHub Advanced Security, GitHub Copilot, repository memory, secure coding, vulnerability remediation
GitHub’s agentic autofix now uses Copilot Memory to reuse repository-specific security fix patterns, helping Copilot apply lessons from past vulnerabilities across future alerts, reviews and coding workflows ...
Leaked GitLab Email Tokens Can Reach Code, Secrets and CI/CD Pipelines
 Jaime Hampton | | Aikido Security, application security, CI/CD, devsecops, gitlab, Software Supply Chain
Security researchers have uncovered a GitLab behavior that could let attackers use a leaked project email address to push code, trigger CI/CD jobs and reach other repositories accessible to the address owner ...
Blitzy Makes Sandbox for Reverse Engineering Code Available at No Cost
Blitzy has made available a sandbox where DevOps teams can reverse-engineer up to one million lines of code, generate up to 25,000 lines of tested end-to-end code, and identify security vulnerabilities across ...
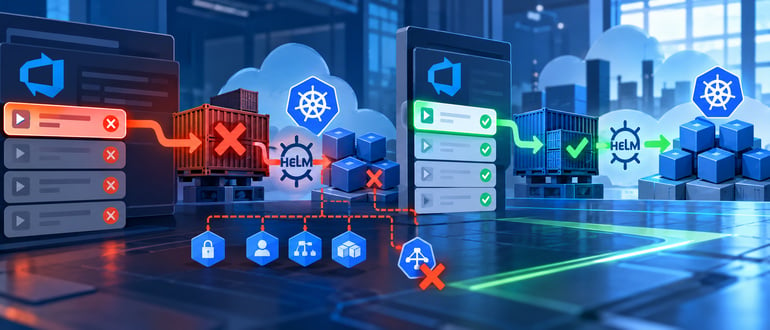
Why Old Azure DevOps Releases Survive a Pipeline Cutover
 Ahmed Tariq | | Azure DevOps, Azure DevOps Classic, Azure pipelines, CI/CD, container security, deployment automation, devops, devsecops, Helm, kubernetes, Kubernetes security, Pipeline Migration, release management, Release Pipelines, software delivery
Old Azure DevOps Classic releases can retain retired deployment tasks, Helm names, image paths and variables long after a pipeline cutover, leaving stale redeploy paths active ...
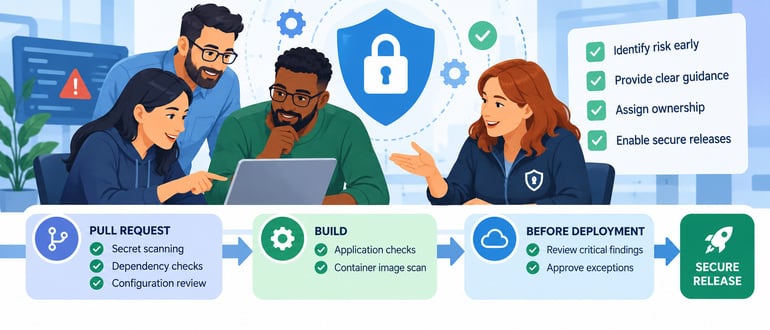
DevSecOps Teams as Partners in Secure Software Delivery
 Manish Shetty | | application security, CI/CD, CI/CD security, dependency security, devops security, devsecops, risk management, secure software development, security automation, Security Guardrails, shift left security, software security, Software Supply Chain, vulnerability management
DevSecOps teams can reduce last-minute release delays by shifting security decisions earlier, improving guardrails, clarifying ownership and making findings actionable ...
Why Software Supply Chain Security Is Moving to the Gate

March 2026: malicious versions of axios get published directly to npm. May 2026: attackers forge valid provenance for 42 TanStack packages on npm, with 84 malicious versions shipped before detection. August 2026: ...
GitHub Gives Enterprises a Full Count of Who Holds the Keys
Tom Smith | | access management, agentic AI, AI coding agents, credential inventory, credential security, Developer Security, devsecops, github, GitHub Apps, GitHub Enterprise Cloud, identity security, least-privilege, OAuth tokens, PATs, Personal Access Tokens, secrets management, security operations, Software Supply Chain Security, SSH keysGitHub Enterprise Cloud now lets organizations export a full inventory of credentials, helping security teams identify stale, overprivileged and forgotten access across users, apps and automation ...
Cycode Extends DevSecOps Reach to Software Packages Developers Download
 Mike Vizard | | ADLC, agentic development lifecycle, AI coding agents, cool down period, Cycode, dependency security, Developer Security, devsecops, malicious packages, package security, software repositories, Software Supply Chain Security, supply chain attacks, threat intelligence, workstation protection
Cycode is adding workstation-level protection to stop developers and AI coding agents from downloading malicious or insufficiently vetted software packages ...
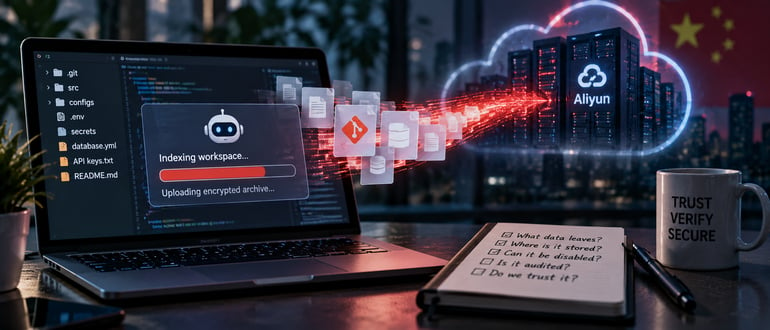
Your AI Coding Assistant Has the Keys to the Repo. Z.ai Just Showed Why That Matters
Tom Smith | | AI coding assistants, AI Governance, AI security, Cloud Security, code security, Data Exfiltration, data privacy, Developer Security, developer tools, devsecops, egress monitoring, secrets management, shadow ai, Software Supply Chain, source code security, Z.ai, ZCode, Zhipu AIZCode’s default-on indexing feature reportedly uploaded entire developer workspaces to cloud storage, highlighting why AI coding assistants should be treated as privileged software and closely monitored ...
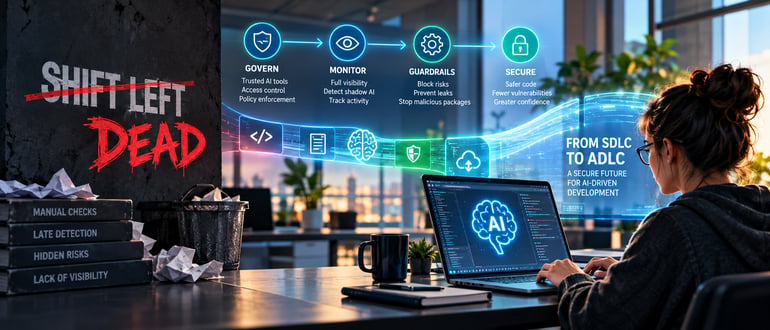
Why Shift Left is Dead
 Devin Maguire | | ADLC, agentic development lifecycle, AI Governance, AI guardrails, AI security, AI-Driven Development, AI-generated code, application security, Developer Security, devsecops, prompts, sdlc, secure software development, shadow ai, shift left security, Software Supply Chain Security
AI-driven development is exposing risks before code is written, forcing security teams to move beyond shift-left and govern agents, prompts, tools and data across the entire development lifecycle ...

