TL;DR — Key Takeaways
– StackHawk launched Wingman to automatically detect, fix and verify vulnerabilities during AI-assisted coding sessions.
– Wingman integrates with tools including Claude Code, Cursor, GitHub Copilot, Codex and Antigravity.
– The tool runs security tests against live applications, sends findings back to the coding agent and rescans code to confirm fixes.
StackHawk this week launched Wingman, an artificial intelligence (AI) tool that makes it possible for application developers to automatically fix vulnerability issues as code is being written.
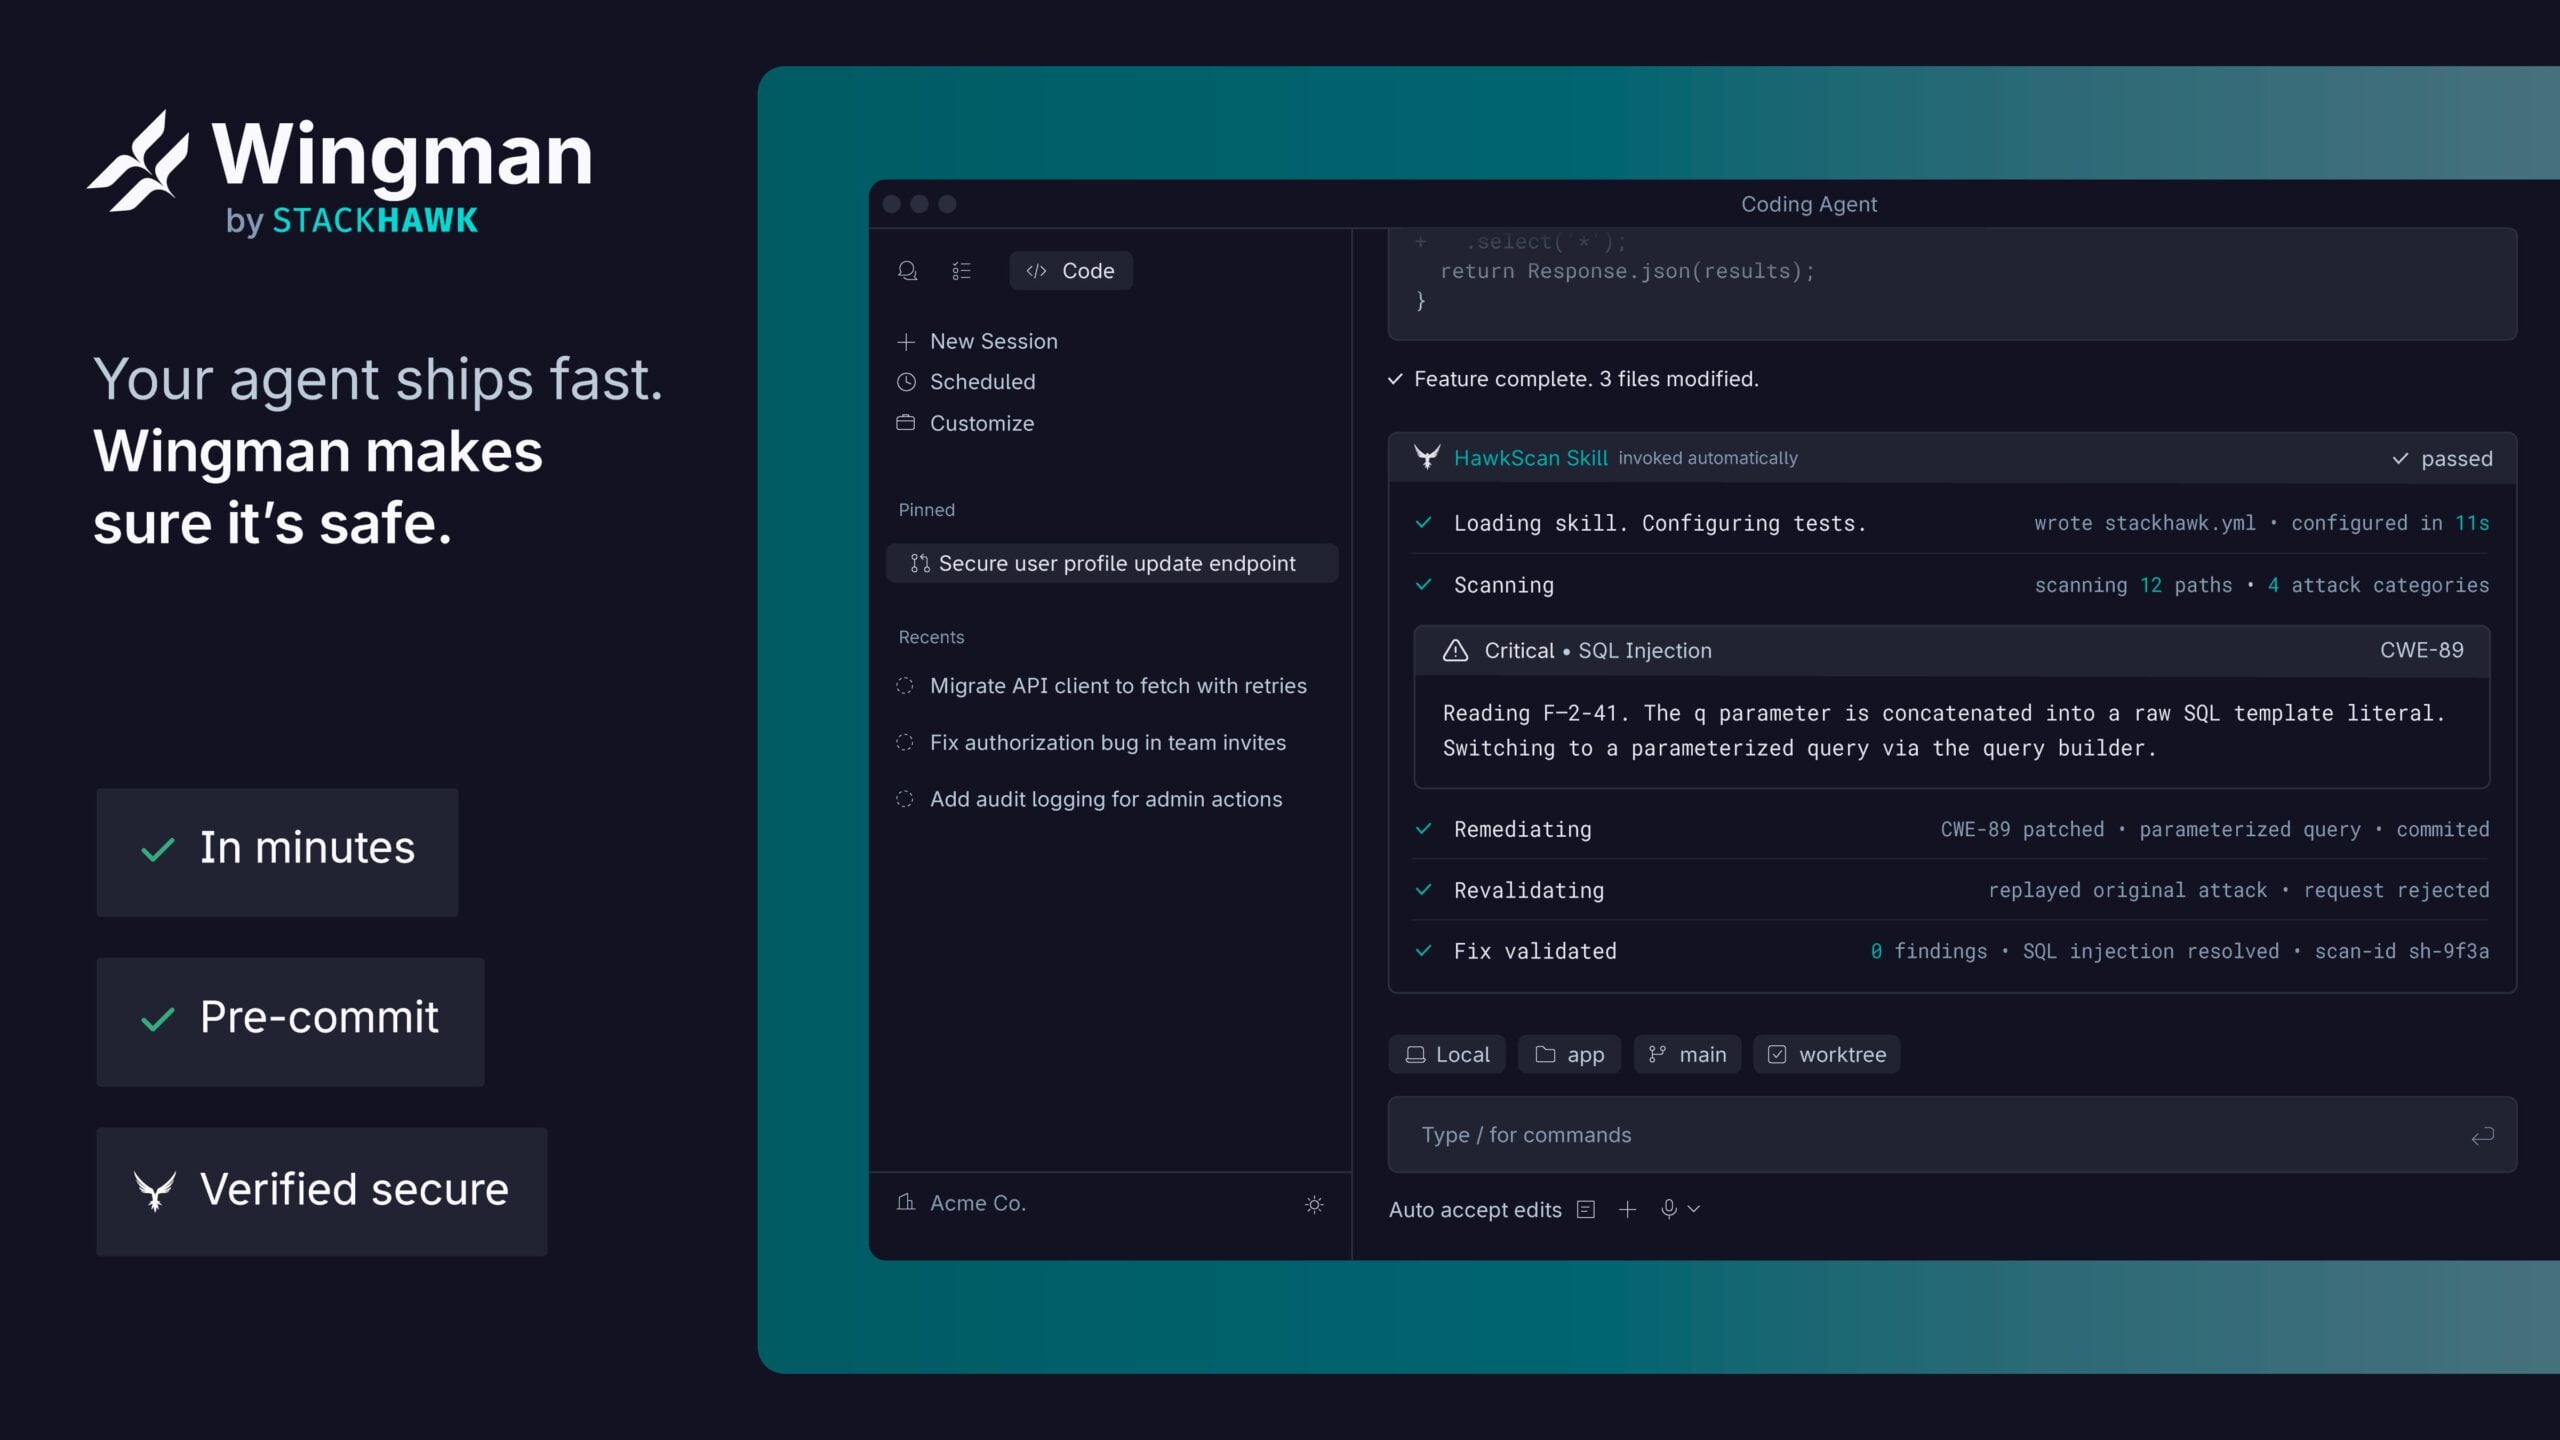
Wingman is designed to install into Claude Code, Cursor, GitHub Copilot, Codex, and Antigravity. It scans the live application, interprets findings, and fixes vulnerabilities in a way that makes it simpler for application developers to maintain context as they write code. At the core of those capabilities is StackHawk’s application testing platform, which Wingman accesses through a set of AI skills, hooks and rules.
Once an AI coding agent finishes a feature, Wingman auto-configures and boots the running application to run a series of security tests with no manual steps required. Findings are then shared with the AI coding agent that wrote the code to fix any issues discovered. Wingman then rescans that application to confirm the fix held before reporting back to the continuous integration (CI) pipeline that the issue has been resolved. Every test is tied to a specific commit, giving security teams an attestation record of what code was securely shipped.
Priced at $10 per user, per month, Wingman includes unlimited applications that can be scanned 50 times per user, per month. StackHawk claims Wingman has already automatically fixed more than 7,000 vulnerabilities for early access customers, with 98% of those fixes remaining resolved with no regressions.
StackHawk CEO Joni Klippert said Wingman is designed to prevent vulnerabilities from ever finding their way into a build in the first place. That capability dramatically reduces the backlog of issues that DevSecOps teams need to address by eliminating tickets they would otherwise have to address at a time when the overall pace at which code is being generated has dramatically accelerated in the AI era, she added.
Mitch Ashley, vice president and practice lead for the Futurum Group, said embedding the fix and verification inside the coding session moves the security control point out of the pipeline gate and into the loop that writes the code. That is the right response to AI-generated code because verification work is accumulating faster than teams can hire reviewers, he added.
Most application developers, to one degree or another, are now relying on AI to generate code. Historically, those application developers lacked the security expertise required to prevent vulnerabilities from being inadvertently included in their code. As the pace at which code is developed in the AI era continues to accelerate, the number of issues that DevSecOps teams are expected to resolve has already dramatically increased. The goal now needs to be to resolve those issues before any ticket is ever created.
Hopefully, the quality of the code being generated in the AI era will get better sooner than later. In the meantime, however, DevSecOps teams, in the absence of any ability to automatically remediate vulnerabilities, are increasing technical security debt at a time when cybercriminals are becoming more adept at using AI to reverse engineer the code needed to exploit those vulnerabilities.

Frequently Asked Questions
What is StackHawk Wingman?
Wingman is an AI-powered security tool that detects, fixes and verifies application vulnerabilities during AI-assisted coding sessions.
Which AI coding tools does Wingman support?
Wingman is designed to work with Claude Code, Cursor, GitHub Copilot, Codex and Antigravity.
How does Wingman verify vulnerability fixes?
After an AI coding agent applies a fix, Wingman rescans the running application to confirm that the vulnerability has been resolved before reporting the result to the CI pipeline.