
DevSecOps
AWS Benchmark Aims to Reduce Number of False Positives Found by AI Vulnerability Scanners

Amazon Web Services (AWS) has developed a benchmark that can be used to test whether a model can distinguish real vulnerabilities from code that looks risky but is actually safe. The Deception ...
TeamPCP Supply Chain Attack Leads to CrowdSec Source Code Being Stolen
 Jeff Burt | | CrowdSec, EDR, github, Mini Shai-Hulud, NPM security, OAuth tokens, supply chain attacks, TanStack compromise, TeamPCP
CrowdSec says attackers stole source code from about 170 private GitHub repositories after a TanStack npm supply chain attack exposed an OAuth token tied to a former employee ...
US District Court Decision in AI’s Favor Worries Open-Source Developers

A federal appeals court handed GitHub, Microsoft, and OpenAI an important win in the first major appellate ruling over how AI coding tools can use open-source code. As we all know, all ...
StackHawk Delivers Wingman to Fix Vulnerabilities as Developers Write Code
StackHawk this week launched Wingman, an artificial intelligence (AI) tool that makes it possible for application developers to automatically fix vulnerability issues as code is being written. Wingman is designed to install ...

Why AI Agents Shouldn’t Guess at Vulnerability Exploitability
 Harish Gaggar | | AI agents, application security, SBoM, Software Supply Chain, vulnerability management, vulnerability prioritization
Vulnerability prioritization is not a language problem. The safest agent architectures use models to interpret and explain, while deterministic systems traverse the evidence. Ask a security team a simple question: Of the ...
Atlassian Aims to Fill Context and Governance Gap for AI Coding Agents
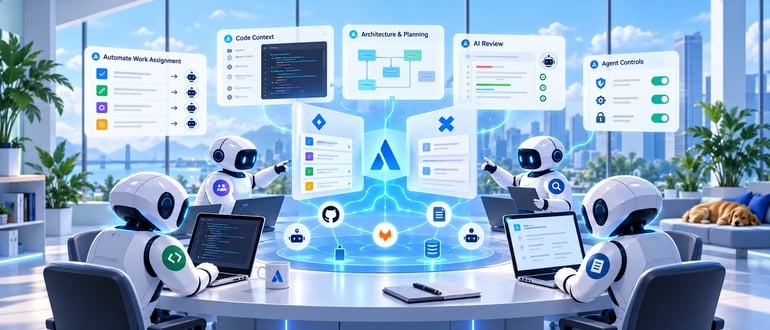
Atlassian today extended the capabilities of its portfolio to provide teams of artificial intelligence (AI) coding agents with the level of context needed to build and deploy applications in production environments at ...
JFrog CEO: No One Cares About Source Code Anymore
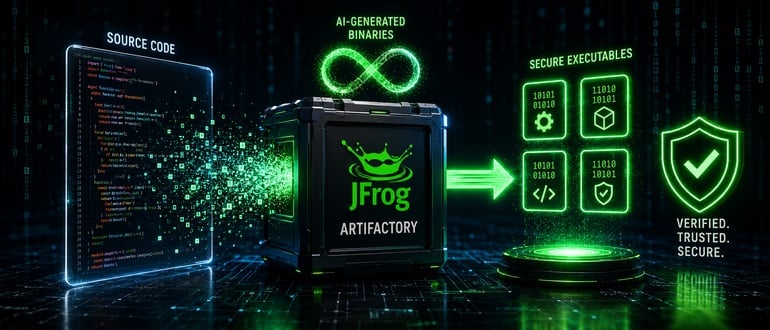
JFrog CEO Shlomi Ben Haim told approximately 500 software engineers today that in the age of artificial intelligence (AI) no one will soon care much about source code anymore. Speaking at the ...
CrowdStrike Moves to Secure Software Supply Chains at the Endpoint
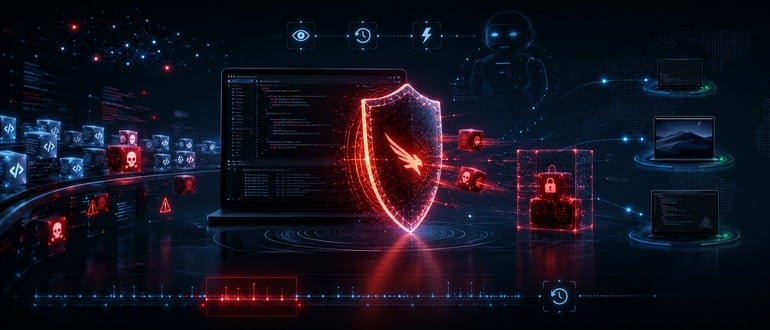
CrowdStrike today at its Fal.con 2026 conference extended its reach into the realm of software supply chain security with the addition of an offering that blocks malicious open-source packages at the endpoint ...
JFrog Moves to Secure Agentic Engineering Workflows
JFrog today at its swampUP 2026 conference added a zero touch remediation capability that ensures the most secure version of a binary is provided even when application developers request a version that ...
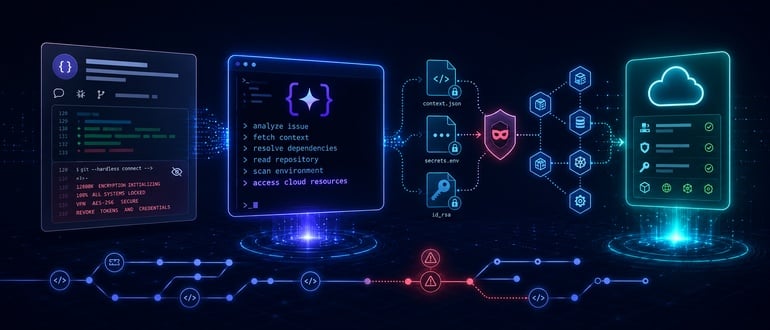
Cybersecurity Researchers Uncover Flaw in Google AI Coding Tool
Cybersecurity researchers from Pillar Security this week revealed how a prompt injection inserted into a GitHub repository was used to gain Editor-level access to an internal Google Cloud project using a flaw ...
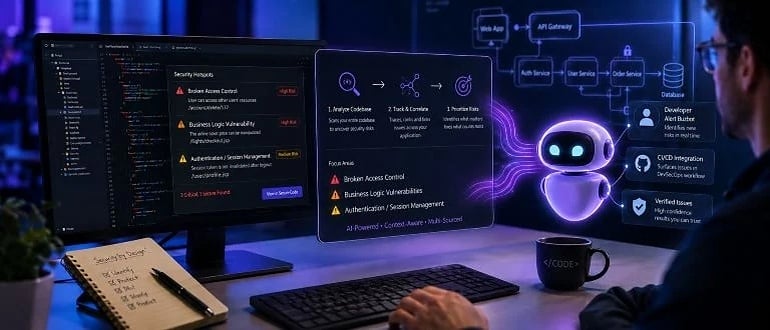
Sonar AI Agent Discovers Vulnerabilities Hidden in Business Logic Workflows
Sonar today made available an artificial intelligence (AI) agent designed to discover vulnerabilities and business logic flaws that pose the greatest risk to an organization should they be exploited. The SonarQube Hunter ...
Hackers Target Popular arrayref Rust Crate in Supply-Chain Attack
Jeff Burt | | arrayref, information stealing, North Korea, Rust programming language, software supply chain attacks, StepSecurity, typosquatting, Wiz ResearchSecurity researchers are sorting through a complex, stealthy, and fast-moving supply-chain attack aimed at pushing information-stealing malware by compromising the account of the maintainer of multiple Rust crates and introducing four more ...

