

EU-Funded CodeSupply Offers Grants for Open Source Software Supply Chain R&D
Software supply chain, security and compliance tools all depend on accurate information about the packages they analyze, but that data is often fragmented across multiple sources and can be difficult to access or use consistently. A new European Union-funded initiative called CodeSupply, coordinated by the NLnet Foundation, is making €400,000 in grants available for open […]
JFrog CEO: No One Cares About Source Code Anymore
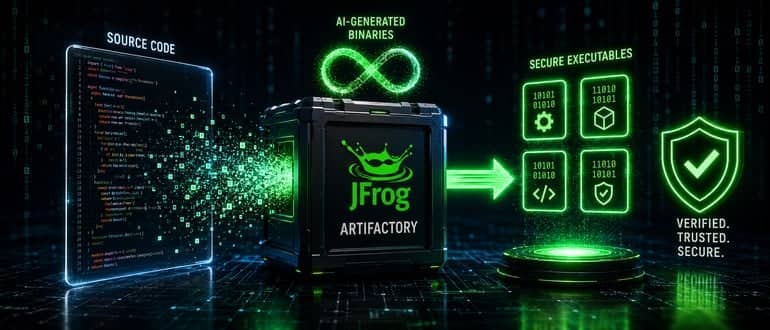
JFrog CEO Shlomi Ben Haim told approximately 500 software engineers today that in the age of artificial intelligence (AI) no one will soon care much about source code anymore. Speaking at the company’s swampUP 2026 conference, Ben Haim said AI tools are now creating executable binaries directly without relying on source code that historically existed […]
CrowdStrike Moves to Secure Software Supply Chains at the Endpoint
CrowdStrike today at its Fal.con 2026 conference extended its reach into the realm of software supply chain security with the addition of an offering that blocks malicious open-source packages at the endpoint before their embedded code can run. Bartley Richardson, chief AI and autonomous systems officer for CrowdStrike, said Real-Time Supply Chain Attack Protection is […]
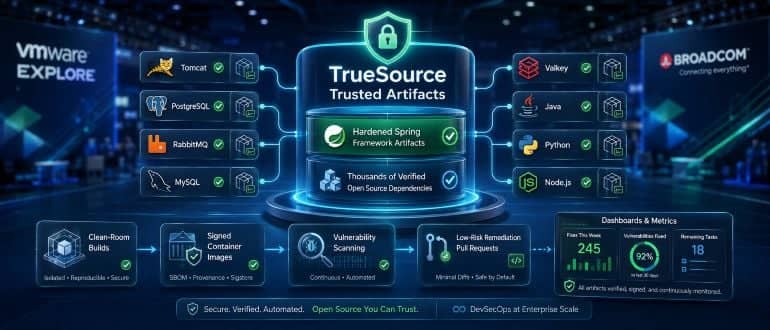
Broadcom Launches Trusted Artifact Service for Spring Framework
Broadcom launches TrueSource Trusted Artifacts to provide hardened Spring dependencies, secure open source packages and automated vulnerability remediation.
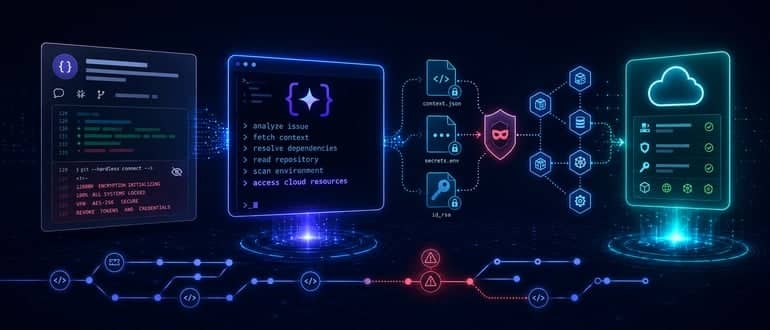
Cybersecurity Researchers Uncover Flaw in Google AI Coding Tool
Cybersecurity researchers from Pillar Security this week revealed how a prompt injection inserted into a GitHub repository was used to gain Editor-level access to an internal Google Cloud project using a flaw in the command line interface (CLI) of an artificial intelligence (AI) coding tool that Google provides. Dan Lisichkin, a cybersecurity researcher for Pillar […]
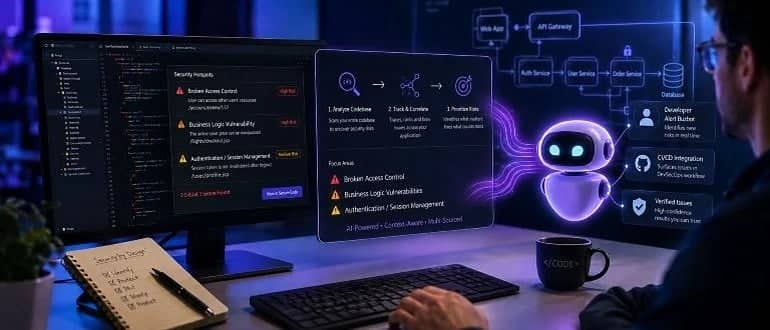
Sonar AI Agent Discovers Vulnerabilities Hidden in Business Logic Workflows
Sonar today made available an artificial intelligence (AI) agent designed to discover vulnerabilities and business logic flaws that pose the greatest risk to an organization should they be exploited. The SonarQube Hunter Agent first analyzes an entire codebase to find three categories of flaws: broken access control, business-logic vulnerabilities, and authentication or session-management issues. Satinder […]
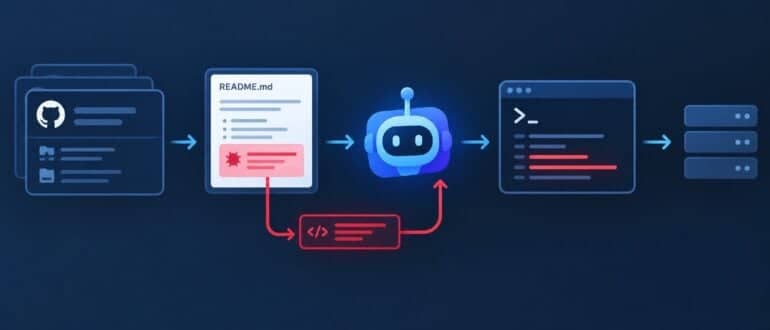
When AI Coding Agents Become Malware Delivery Systems
AI coding agents are becoming part of everyday development work. Developers use them to find libraries, configure projects, troubleshoot installation problems, and set up new tools. An agent can search GitHub, read project documentation, and run commands without the developer having to work through every step manually. That convenience is creating another security concern for […]
AI Can Generate Your Infrastructure. Can Your CI/CD Pipeline Trust It?
AI-generated infrastructure code is exposing a growing security gap, pushing platform teams to add stronger automated gates, provenance tracking and human review before Terraform, Kubernetes and CI/CD changes reach production.
Report Shines Spotlight on 91 Vulnerabilities Fixed in Latest Update to Spring Framework
Sonatype says 91 Spring vulnerabilities affecting more than 209,000 software components highlight how AI is accelerating vulnerability discovery and creating a new patching challenge for DevSecOps teams.
Why Cryptographic Inventory Is the First Step Toward Quantum Readiness
Post-quantum readiness starts with visibility. DevOps teams need a continuous cryptographic inventory to map algorithms, keys, certificates, libraries, infrastructure and third-party dependencies before PQC migration begins.
npm v12 Shuts Down a Popular Malware Trick — But the Threat Isn’t Going Away
For years, one of the easiest ways to sneak malware onto a developer’s machine has been to hide in plain sight. Install a package from npm, and any lifecycle script bundled with it runs automatically — no review, no approval, no second look. Attackers have known this for a long time, and they’ve used it […]
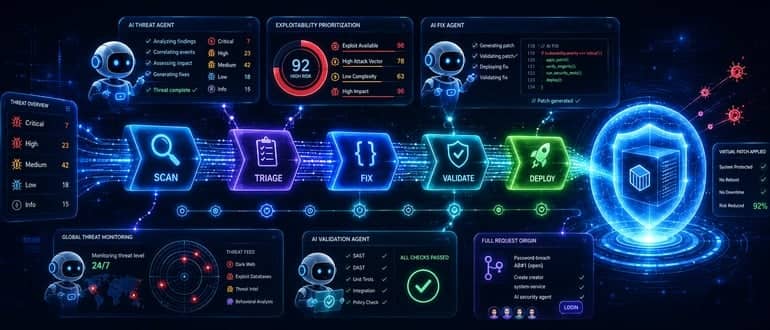
Harness Adds AI Agents to Automate DevSecOps Workflows at Machine Speed
Harness today added multiple artificial intelligence (AI) agents and a virtual patching capability to its portfolio to automate DevSecOps workflows at a time when the number of vulnerabilities being discovered in code continues to exponentially increase. The AI agents include one that has been added to the static application security testing (SAST) tool that Harness […]
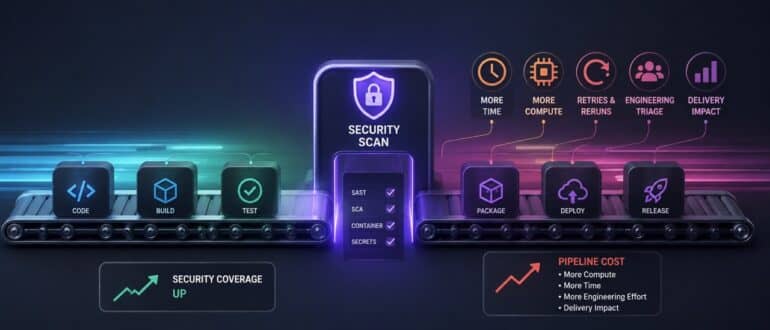
Is Your New DevSecOps Tooling Reducing Work Or Just Adding to It?
Security belongs in the software delivery pipeline. The harder question is where, how often and at what cost. Many pipeline teams eventually add security scanning to CI/CD, and relatively few go back afterward to measure what it actually cost the delivery process. Security coverage went up. Something else changed too, and it is rarely measured […]
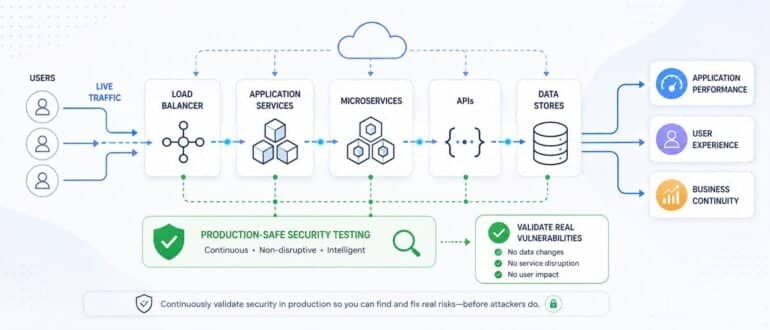
Production-Safe Testing: The Missing Piece in Most DevSecOps Strategies
Most DevSecOps teams invest heavily in security before deployment, yet attackers target the production environment where applications, APIs, and user behavior are constantly changing. If security validation stops before release, critical risks can remain hidden until they are exploited. The gap is more common than many organizations realize. A survey found that over 70% of […]
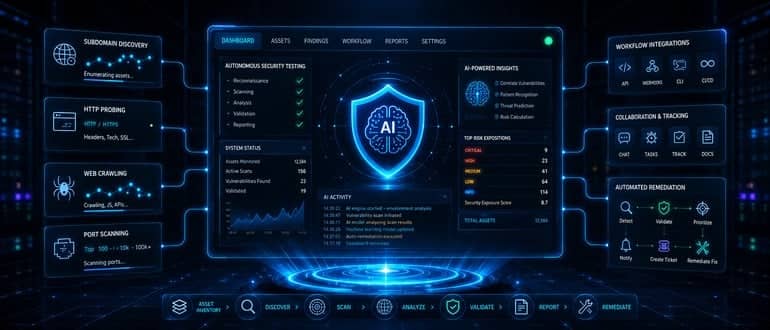
ProjectDiscovery Brings Open Source AI Testing to Vulnerability Discovery
ProjectDiscovery has made available an autonomous security testing platform that leverages an open source artificial intelligence (AI) testing framework to detect and validate vulnerabilities at a lower total cost. Company CEO Rishi Sharma said version 1.0 of the Neo platform is also available via a cloud service that makes it possible for DevSecOps teams to […]
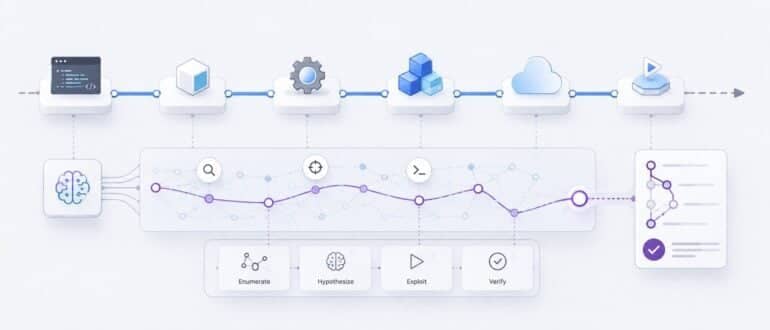
Why CI/CD Security Testing Is Going Autonomous (and Why It Should Stay Local)
Continuous integration and delivery changed the tempo of software. Teams merge dozens of times a day, infrastructure is redefined on every commit, and a new build can reach production in minutes. Security testing never caught up with that tempo. It still lives in two modes that both fight the pipeline instead of moving with it. […]
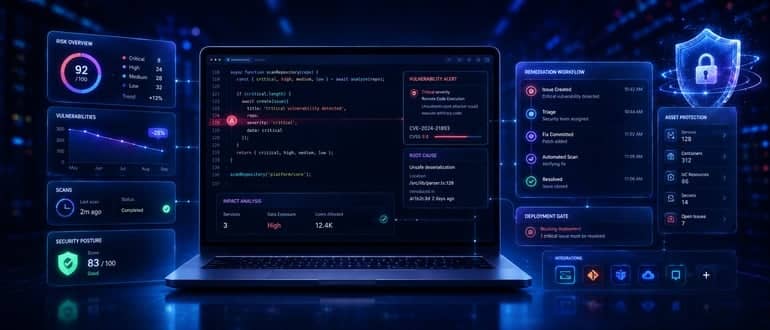
HackerOne Extends Platform Reach to Remediate Source Code Vulnerabilities
HackerOne has added a remediation capability to its H1 Platform that reduces the amount of time required to remediate validated vulnerabilities and other weaknesses affecting specific lines of source code. Nidhi Aggarwal, chief product officer for HackerOne, said H1 Remediation combines artificial intelligence (AI) and crowdsourced research to identify the root cause of issues that […]
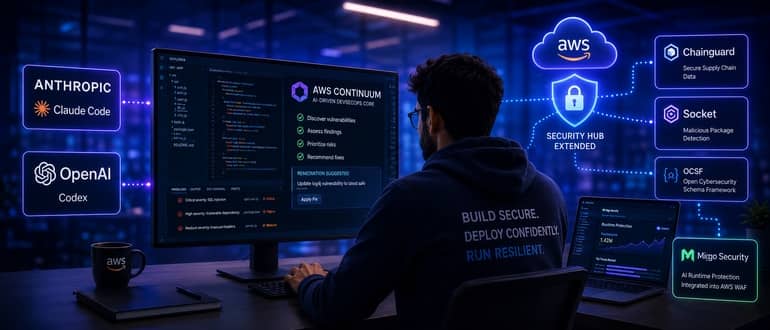
AWS Extends DevSecOps Reach to AI Coding Tools from Anthropic and OpenAI
Amazon Web Services (AWS) this week at the Black Hat USA conference revealed it is working with both Anthropic and OpenAI to integrate their respective coding tools with a service it has developed that makes available artificial intelligence (AI) agents to help application developers write more secure code. Launched earlier this year, the AWS Continuum […]
RapidFort Extends Open Source Software Security Reach to Runtime Environments
RapidFort today at the Black Hat USA conference announced it has extended its ability to secure open source software to the runtimes that DevOps teams deploy in production environments. Michael Wood, chief marketing officer for RapidFort, said the RapidFort Runtime platform makes it possible to now monitor open source software deployed within a container image […]
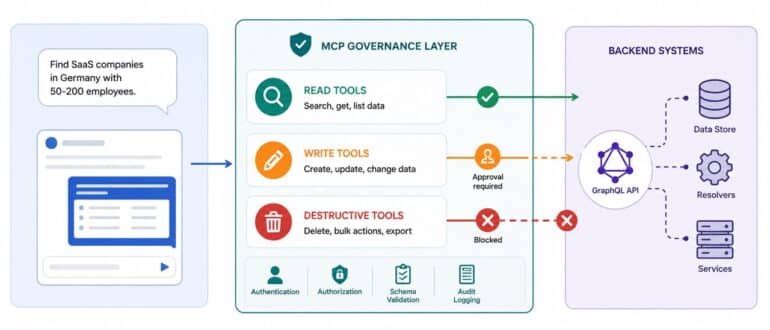
From API Integration to Agent Governance: What Backend Teams Need to Know About MCP
Many MCP projects begin with an existing API and a simple request: expose one backend capability to an LLM client. The quickest route is to wrap an endpoint as a tool and connect it to Claude or another MCP host. Users can then ask for data in natural language instead of navigating a fixed interface. […]
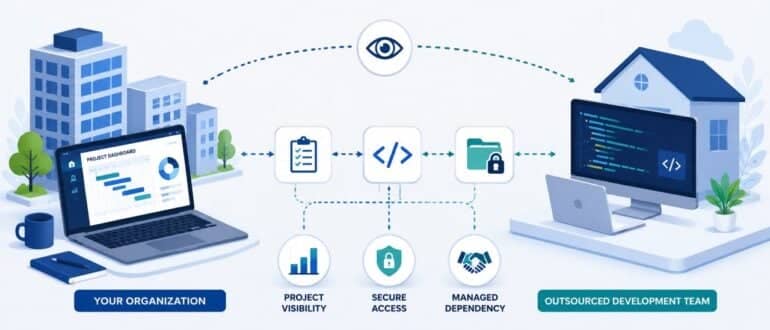
Common Risks of Outsourcing Software Development, and How to Tackle Them
Both SMBs and large enterprises often choose software development outsourcing over developing software in-house. It is no surprise, as partnering with external developers enables companies to bridge IT talent gaps that cannot be filled internally, avoid time-consuming recruiting and training processes, and eliminate expenses associated with salaries and benefits, eventually accelerating software delivery and reducing […]
DevOps Is Drowning in Updates—and Engineering Is Paying the Price
DevOps used to be a manageable rhythm: several core tools, a handful of respected blogs, and a few incident write-ups that made everyone slightly uncomfortable in a useful way. Now it feels like a firehose aimed directly at the on-call rotation. DevOps teams now have more information than they can reasonably track. Critical updates are […]
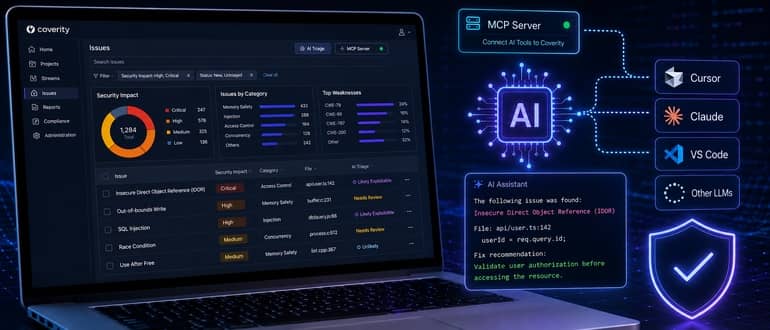
Black Duck Extends Scope and Reach of Code Scanning Tool
Black Duck has updated its Coverity static analysis code scanning tool to provide deeper integrations with artificial intelligence (AI) tools along with updates to its user interface that make it simpler to prioritize issues in a way that makes it easier to adhere to multiple compliance mandates. A Model Context Protocol (MCP) server added to […]