

AI Moved the Bottleneck From Writing Code to Understanding and Trusting It
AI coding boosts velocity, but without stronger review, governance and codebase visibility, teams risk higher costs, security gaps and production failures. TL;DR
Why Developer Workstations Have Become a Critical Part of the Software Supply Chain
For years, software supply-chain security discussions focused on centralized infrastructure such as build servers, package registries, and CI/CD systems. Recent attacks suggest that this view is incomplete. The Megalodon campaign injected malicious GitHub Actions workflows into thousands of repositories, while a separate incident involving a malicious Visual Studio Code extension demonstrated how a single compromised […]
How to Build a DevSecOps CI/CD Pipeline on Azure With GitHub Actions
Fix security problems when they’re cheap to fix, which is before the code is deployed. A pipeline that enforces this automatically is what makes that principle real.
North Korea Expands the Reach of PolinRider Supply Chain Attack Campaign
The North Korean-sponsored threat groups behind the long-running fake interview scams targeting developers are expanding the PolinRider supply chain campaign that has escalated over the past several months. Reports from cybersecurity vendors Socket and Rescana found that two groups linked to the Democratic People’s Republic of Korea (DPRK) have published at least 108 malicious packages […]
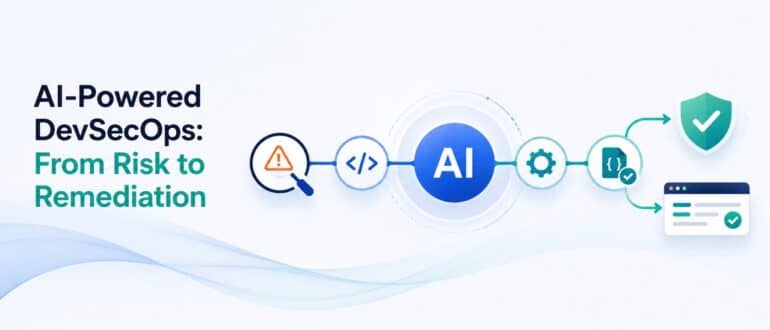
How AI is Revamping DevSecOps Processes
Artificial Intelligence is pushing DevSecOps into a new phase where security is no longer just about detecting vulnerabilities, but increasingly about resolving them automatically within the flow of software delivery. As many organizations are discovering, DevSecOps historically gave teams visibility into risk. AI is now turning that visibility into automated remediation. This evolution has taken […]
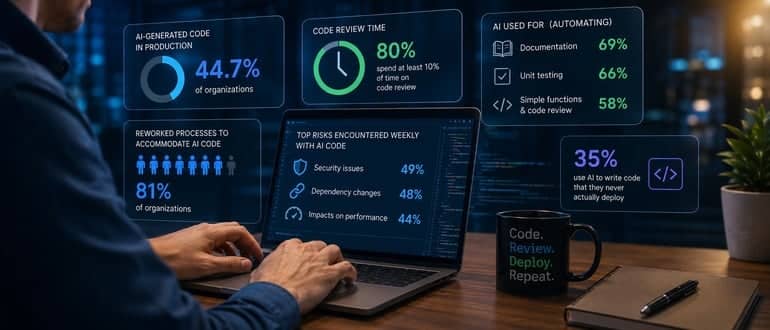
Survey: More AI Code Running in Production Environments with Caveats
A global survey of 309 software engineering leaders, published today, finds 81% of organizations have to some degree reworked development and release processes to accommodate code generated using artificial intelligence (AI) coding tools. However, only 45% said their organization is running any of that code in production environments. Conducted by Dimensional Research on behalf of […]
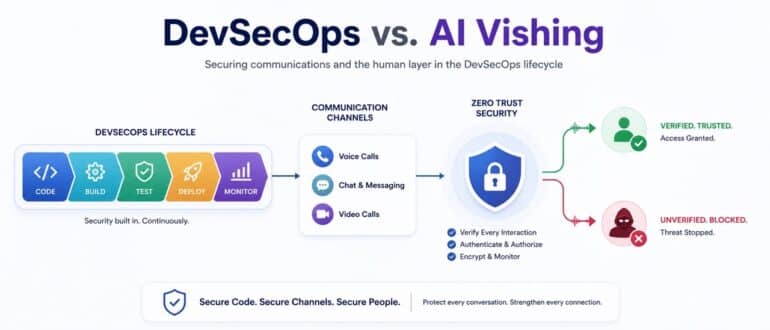
From Phishing to Vishing: Why DevSecOps Must Rethink Communication Security
Key Takeaways: Vishing is the new frontline threat: Attackers are shifting from emails to phone-based scams, using AI and social engineering to bypass traditional security controls. DevSecOps must expand its scope: Securing code is no longer enough; communication channels like voice, chat, and messaging must be integrated into threat models and security pipelines. Human and […]
Why CI-Based Security is Too Late for Modern Node.js Projects
Most Node.js teams rely on CI pipelines to tell them whether their dependencies are secure. By the time that feedback arrives, however, the most important decisions have already been made.
Homebrew to Packages: No ID, No Service
Homebrew, the unofficial but default package manager for many Apple Mac users, now has safeguards to prevent supply-chain attacks. The approach mimics how GitHub just fortified npm against attacks by establishing a set of trusted repositories to download from. “The Homebrew team is aware of the supply-side security issues with other package managers. We’ve taken […]
AWS Continuum Service Employs AI to Secure Software Supply Chains
Amazon Web Services (AWS) today launched a service that expands the scope of the artificial intelligence (AI) tools it provides to secure code to include an agent that discovers, validates and prioritizes vulnerabilities that are then used to surface a remediation recommendation. Announced at the AWS New York Summit, the AWS Continuum service also adds […]
Tenet’s ‘Agentjacking’ Attack Turns Sentry Errors Into Code Execution
AI coding agents can create a new code execution risk when they treat externally influenced error data as trusted guidance and have access to command line tools, according to new research from Tenet Security. The security company demonstrated an indirect prompt injection technique it calls “Agentjacking” in a recent report. In its proof of concept, […]
Why Endpoint Protection Matters More than Ever in CI/CD Environments
CI/CD environments depend on far more than repositories and deployment infrastructure. Developer endpoints hold sensitive data: cloud credentials, SSH keys, deployment permissions, direct access to internal systems. Endpoint security and control are part of daily operational risk management. Engineering teams are shifting more and more toward distributed workflows, so discussions around CI/CD security include the […]
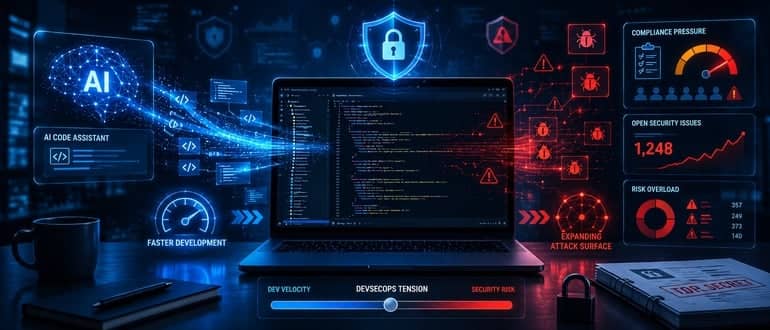
Survey Surfaces Depth of DevSecOps Crisis in the Age of AI
A global survey of 2,350 developers, CISOs and application security managers published this week finds that while nearly all respondents (96%) work for organizations that have embedded or connected artificial intelligence (AI) code and tools into some aspect of their application development workflows, nearly half of all code (49%) running in production environments was AI-generated […]
Shift Left to the Developer’s Machine: Building Local Git Security Gates
Shift left to the developer’s machine. The principle is what matters: Stop secrets before they ship. The tooling is a means to that end.
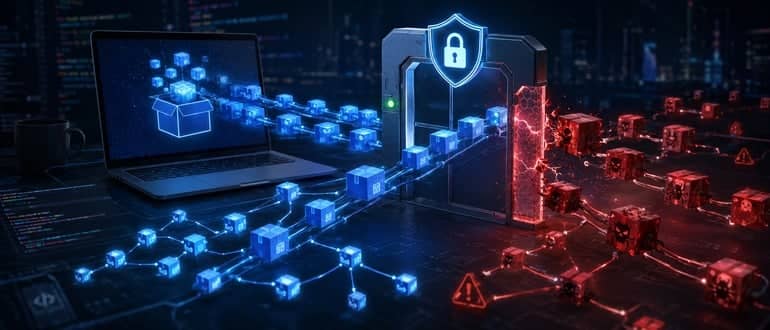
npm v12 Is Coming in July — Here’s What Developers Need to Do Now
For years, running npm install meant trusting that whatever code got pulled in would behave itself. That trust was often misplaced. Starting in July 2026, npm v12 changes the rules. Install scripts won’t run automatically anymore. Neither will dependencies be pulled from Git repos or remote URLs. All of it becomes opt-in. This is a […]
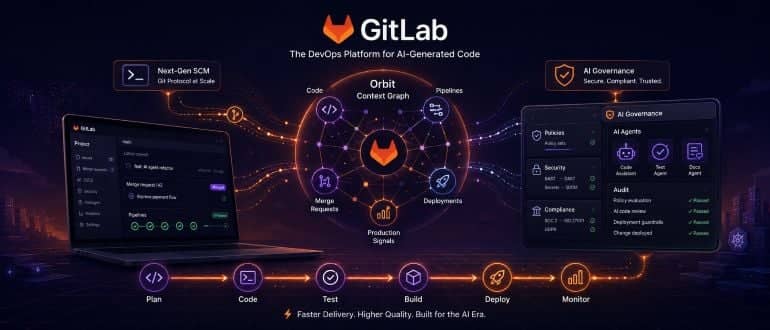
GitLab Previews Revamped DevOps Platform for the Agentic AI Era
At Transcend 2026, GitLab launched updates to optimize its DevOps platform for AI-generated code, featuring Next Gen Source Code Management, GitLab Orbit, and an AI Governance framework.
Broadcom Aims to Better Secure Spring Applications in the AI Era
Broadcom today released a raft of updates to the open source Spring framework for building Java applications to primarily address a wave of vulnerabilities discovered by researchers using artificial intelligence (AI) tools. At the same time, Broadcom is also adding a managed service through which organizations can secure thousands of Spring dependencies for organizations building […]
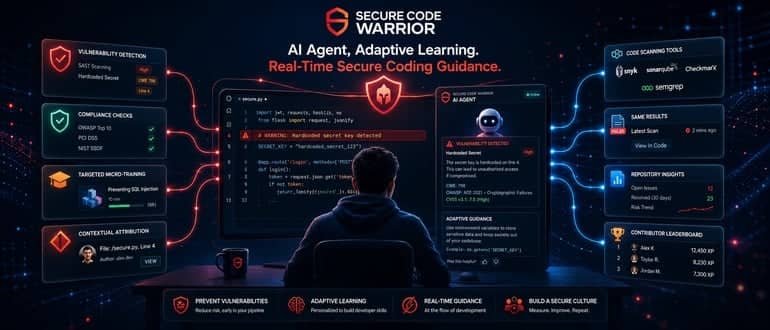
Secure Code Warrior Leverages AI to Extend DevSecOps Training Reach
Secure Code Warrior this week extended the capability of its artificial intelligence (AI) agent to make it possible to surface relevant training insights in real time as application developers are writing code. Announced at the Gartner Security & Risk Management Summit, the Adaptive Learning capability added to the company’s learning platform detects which AI tools […]
Agentic DevSecOps: AI Security Co-Pilots for Your CI/CD Pipeline
The emergence of AI has brought endless possibilities and innovative opportunities in today’s ever-changing, fast-paced technology landscape. AI is helping development teams produce software significantly faster than ever before. AI-enabled DevSecOps tools can automatically scan code, infrastructure and other configurations for security issues throughout development, accelerating the overall process. The introduction of agentic AI into the software […]

Risk-Based Review for Infrastructure as Code Pull Requests
Not every infrastructure pull request deserves the same review path. A tag change in a development account and a network-policy change in production should not create identical reviewer load. When every change is treated as high risk, reviewers stop trusting the signal. In IaC review, I have seen reviewers spend too much attention on low-risk changes […]
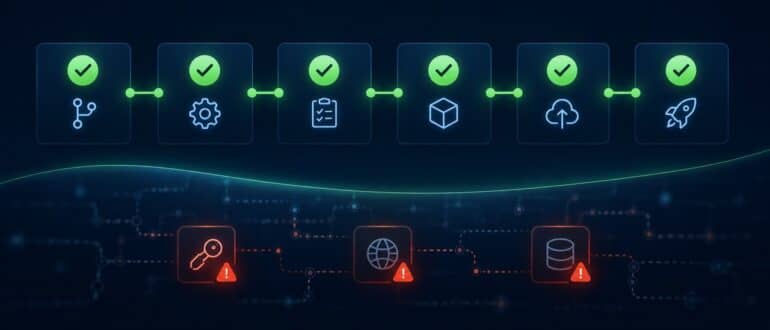
The Silent Risk of AI-Written DevOps Pipelines
These days, when a developer needs a CI/CD pipeline, they don’t always dive into GitHub Actions docs or spin up Jenkins from scratch. Instead, they pull up an AI assistant and type out something like: “Create a deployment pipeline for a containerized application.” Seconds later, the AI spits out a complete workflow. It looks polished. […]

Regression Testing Tools in the Age of AI-Assisted Development: What Has Changed
For most of the past decade, the conversation around regression testing tools was fairly stable. The tools got faster, the integrations got smoother, and the underlying approach stayed largely the same: write tests, run them in CI, fix failures. The fundamental model did not change much because the problem did not change much. AI-assisted development […]
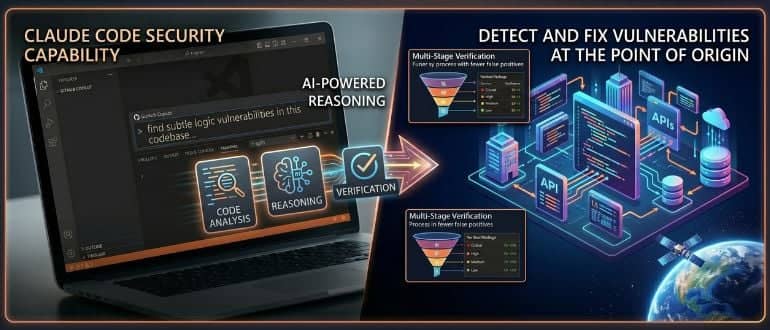
Claude Code Security Catches Vulnerabilities While You Write Code
Claude Code Security uses AI reasoning to catch complex vulnerabilities in code — including logic flaws that traditional static analysis tools consistently miss.