

OWASP Adopts CVE Lite CLI to Boost Dependency Scanning
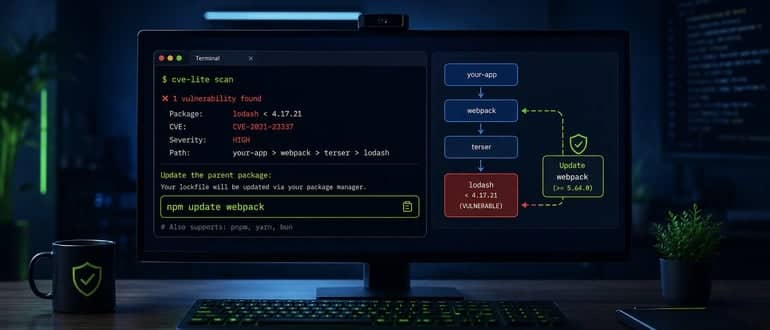
Checking for dependency vulnerabilities in freshly developed software is usually done near the end of the build process. Remediation at that point can be tricky. Now, JavaScript and TypeScript developers can check for vulnerabilities themselves as they – or their agents – write their source code, using an open source project called CVE Lite CLI. […]

Designing an AI-Powered DevSecOps Guardrail Pipeline Using GitHub Actions
By embedding AI-powered guardrails directly into CI/CD pipelines, organizations can detect vulnerabilities earlier, enforce security policies automatically and accelerate secure software delivery.
Modernizing DevOps Security With Intelligent KYC Enforcement Layers
This is where smart KYC enforcement layers fit in — not a compliance box, but an engineering control that is directly part of DevOps processes.
CI/CD Supply Chain Security: Hardening Artifacts, Dependencies, and Delivery Pipelines
Modern CI/CD pipelines have become one of the most attractive attack surfaces in enterprise environments. As organizations push for faster releases, broader automation, and greater reuse of third-party components, the software supply chain has quietly expanded beyond the direct control of any single team. Source code is only one small piece of what ultimately runs in […]
Software Weaponization Raises DevSecOps Stakes
The threat model that DevSecOps teams have been working from for the last decade was built around accidental vulnerabilities — mistakes that needed to be found and fixed before someone exploited them. That assumption is breaking. Vulnerabilities are increasingly being treated as strategic assets, stockpiled by nation-states and threat actors and held back from disclosure […]
OpenSSF’s CRob: ‘The Runway Is Rapidly Running Out’ on EU CRA Readiness
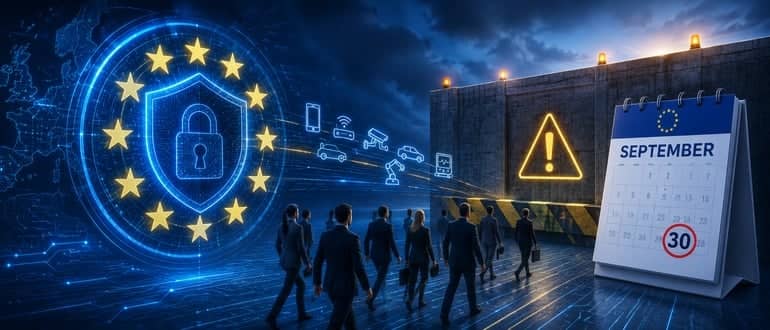
The EU’s Cyber Resilience Act kicks into high gear this September, and companies are still clueless about how they must obey its strictures. MINNEAPOLIS — At Open Source Summit North America, Christopher “CRob” Robinson, Chief Security Architect for the Open Source Software Foundation (OpenSSF), spoke about the European Union’s (EU) Cyber Resilience Act (CRA). CRob […]
1Password Allies With OpenAI to Secure Codex AI Coding Tool
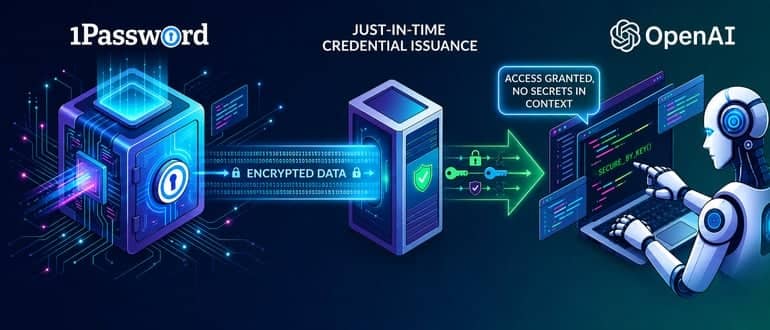
DevSecOps teams can now manage coding agents as a tenant rather than another vault where secrets might be stored, ensuring credentials are never exposed to an AI agent or LLM as plain text. The MCP server does not read or return secret values through the MCP channel, allowing Codex to create environments and invoke applications while the values themselves never leave the 1Password vault.
Why DevOps Is Critical for Modern Business Resilience
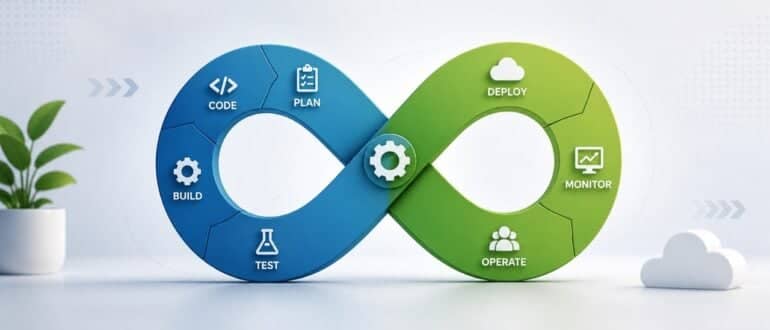
Today’s business world operates in a state of constant change. What the customer wants to buy changes quickly, new competitors appear overnight, and cyber threats are changing faster than ever. In this world, the concept of “resilience,” the ability to adapt, to overcome, and to continue to create value for the enterprise despite the changes, […]
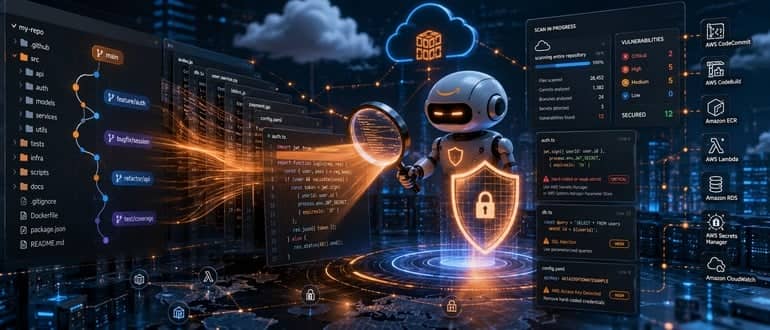
AWS Security Agent Brings Full Repository Code Scanning to Preview
Security teams have long relied on static analysis tools to catch vulnerabilities before code ships. Those tools are useful, but they have a fundamental limitation: they match code against known patterns. They don’t understand your application. AWS is taking a different approach with its latest addition to AWS Security Agent. The company recently released full […]
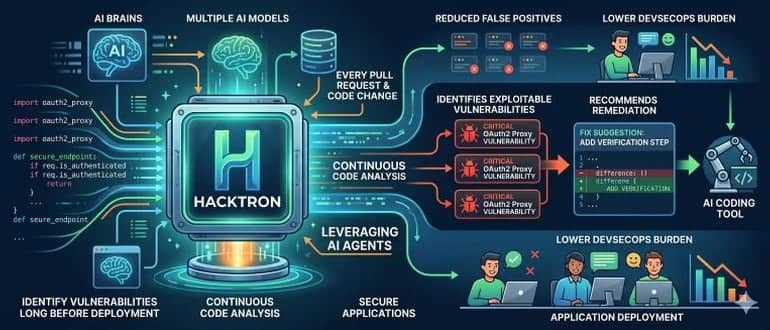
Hacktron Plans to Build AI Platform to Test Code for Vulnerabilities
Hacktron revealed today it is developing a platform that leverages artificial intelligence (AI) to continuously test code for vulnerabilities. Fresh off raising $2.9 million in seed capital, Hacktron founder Zayne Zhang said the company’s platform will employ multiple AI models to test every pull request and code change to identify vulnerabilities that are actually exploitable. […]

Continuous Security in DevSecOps: Moving Beyond One-Time Testing
Waiting for a single annual pentest to secure your application is like locking your front door only once a year and hoping for the best. In an era where 133 new vulnerabilities are reported every single day, relying on periodic snapshots leaves your organization exposed to evolving threats for months at a time. This approach is no longer just […]
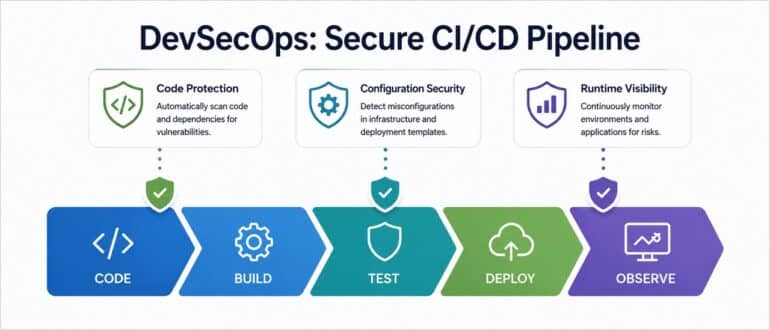
Beyond the Build: Integrating Security into CI/CD Pipelines
In today’s fast-paced software development landscape, Continuous Integration and Continuous Deployment (CI/CD) pipelines are essential for delivering applications efficiently. However, the speed and automation they offer can inadvertently introduce security vulnerabilities if not properly managed. Integrating security into CI/CD pipelines, often referred to as DevSecOps, is no longer optional; it’s a necessity. The Importance of […]
The Messy Reality of Vibe Coding
The default reaction to vibe coding has been alarm — a default assumption that letting AI write large chunks of an application is going to flood production with vulnerabilities and undocumented behavior. That fear is doing as much damage as the bad code people are afraid of. Teams that freeze, ban the tools or push […]
The Great Decoupling: Scaling the Outer Loop for the Agentic Era
The “Inner Loop” of software development—the iterative cycle of writing, building, and debugging code—has just broken the sound barrier. With the emergence of agentic coding tools like Claude Code and GitHub Copilot Workspace, the developer experience has undergone a fundamental shift. Developers are no longer merely tab-completing snippets; they are orchestrating agents that generate entire […]
The Trust Problem With AI Agents in Production Pipelines
AI agents boost DevOps pipelines, but confident failures create risk. Here’s how to design for calibrated trust and human oversight.
Agentic AI for Defense: How Checkmarx Turns Security into a Coding Partner
“AI-powered” has become the default label for every security tool on the market. But there’s a meaningful difference between a tool that uses AI to generate alerts after the fact and one that actively participates in development, preventing vulnerabilities as code is written. That difference is what separates reactive AI from agentic AI. And it […]
The Open Source Trap: Why Trust Isn’t a Security Strategy
The XZ Utils backdoor was a wake-up call, but the underlying problem it exposed has not gone away. Sophisticated adversaries are playing the long game, spending months or years earning trust within open source projects before introducing malicious code into libraries that sit at the foundation of modern software infrastructure. Mike Vizard and Josh Bressers, […]
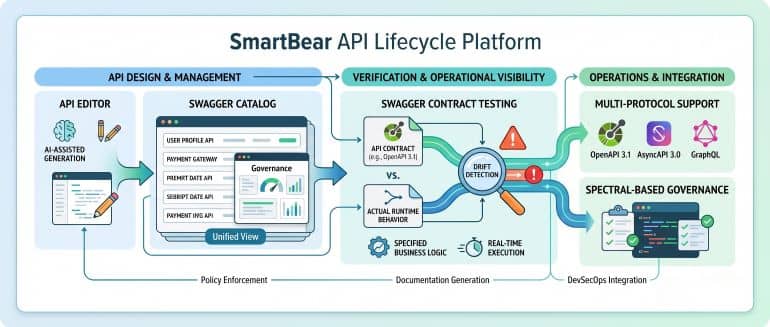
SmartBear Extends Scope of API Lifecycle Management Ambitions
SmartBear upgrades its API platform with a revamped Swagger Catalog and AI-driven drift detection to secure the modern API lifecycle against rogue, zombie, and misconfigured endpoints.
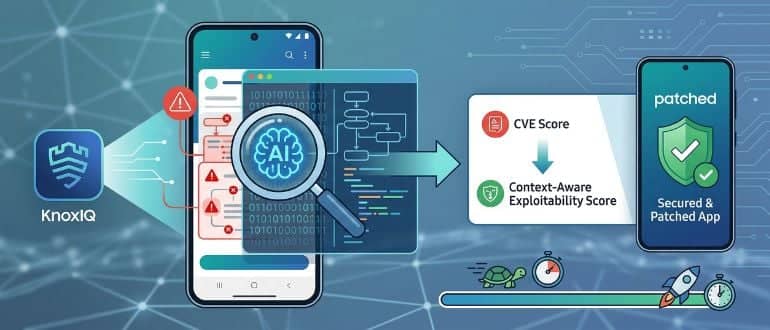
Appknox Adds AI Tool to Detect and Fix Vulnerabilities in Mobile Applications
Appknox today added an ability to apply artificial intelligence (AI) to assess vulnerabilities in the binaries used to construct a mobile application and recommend a fix that can be passed on to an AI coding tool to implement. Company CEO Harshit Agarwal said KnoxIQ provides an AI copilot to more accurately assess how exploitable a […]
Is Your AI Agent Secure? The DevOps Case for Adversarial QA Testing
Adversarial QA testing helps validate AI agents under real-world conditions, exposing risks like prompt injection and logic failures.
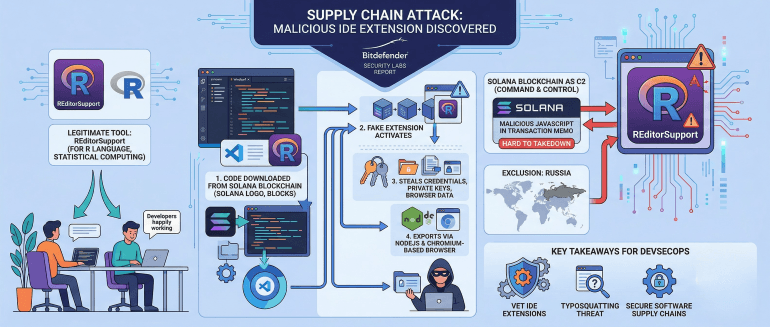
Latest Typosquatting Attack Targeting VS Code Tools Hits Windsurf IDE
Cybersecurity researchers from Bitdefender, a provider of an endpoint detection and response (EDR) platform, have discovered an extension to the Windsurf integrated development environment (IDE) that steals credentials and data after code is downloaded from the Solana blockchain platform. Silviu Stahie, a security analyst for Bitdefender, said the extension makes use of typosquatting tactics to […]
How AI is Shaping Modern DevOps and DevSecOps
AI is reshaping DevOps and DevSecOps by improving CI/CD workflows, DORA metrics and security without adding unnecessary complexity.
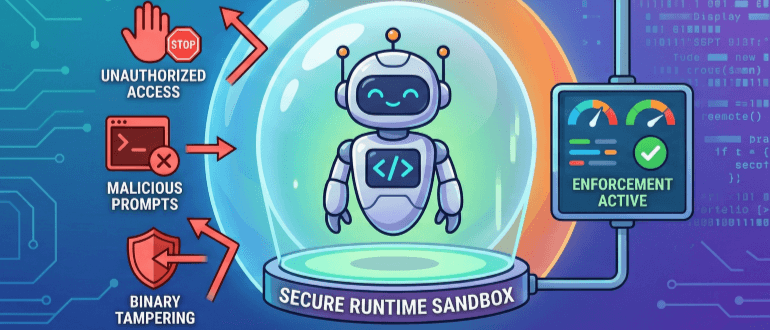
Sysdig Adds Runtime to Secure AI Coding Agents
Sysdig this week at the RSA Conference (RSAC) revealed it has created a runtime that makes it possible to securely deploy artificial intelligence (AI) coding tools. Jonas Rosland, director of the open source program for Sysdig, said the runtime makes it possible to monitor the activity of AI coding agents in real time, including potential […]