
Tag: Software Supply Chain
Survey: Lack of Confidence in Software Supply Chain Security Runs High

A survey of 400 platform and security engineers in the U.S and United Kingdom (UK), finds nearly three quarters (73%) are either only moderately confident (58%) or not confident (15%) in the ...
Leaked GitLab Email Tokens Can Reach Code, Secrets and CI/CD Pipelines
 Jaime Hampton | | Aikido Security, application security, CI/CD, devsecops, gitlab, Software Supply Chain
Security researchers have uncovered a GitLab behavior that could let attackers use a leaked project email address to push code, trigger CI/CD jobs and reach other repositories accessible to the address owner ...
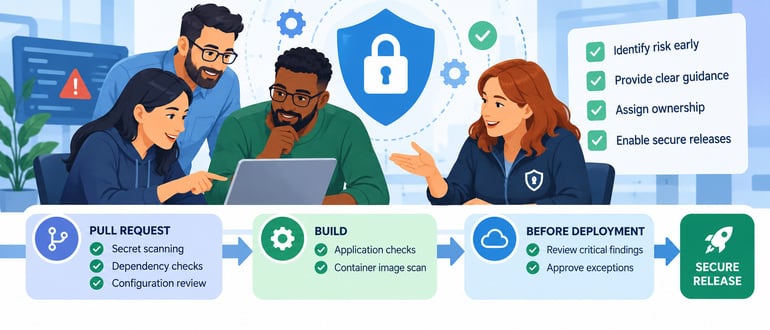
DevSecOps Teams as Partners in Secure Software Delivery
 Manish Shetty | | application security, CI/CD, CI/CD security, dependency security, devops security, devsecops, risk management, secure software development, security automation, Security Guardrails, shift left security, software security, Software Supply Chain, vulnerability management
DevSecOps teams can reduce last-minute release delays by shifting security decisions earlier, improving guardrails, clarifying ownership and making findings actionable ...
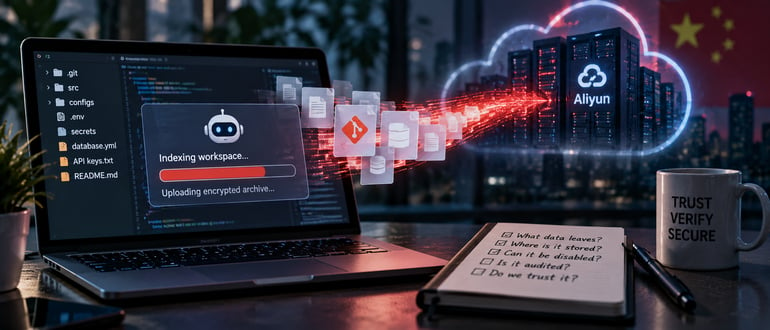
Your AI Coding Assistant Has the Keys to the Repo. Z.ai Just Showed Why That Matters
 Tom Smith | | AI coding assistants, AI Governance, AI security, Cloud Security, code security, Data Exfiltration, data privacy, Developer Security, developer tools, devsecops, egress monitoring, secrets management, shadow ai, Software Supply Chain, source code security, Z.ai, ZCode, Zhipu AI
ZCode’s default-on indexing feature reportedly uploaded entire developer workspaces to cloud storage, highlighting why AI coding assistants should be treated as privileged software and closely monitored ...
Codex Sandbox Escapes Show Why Agent Guardrails Can’t Live Inside the Agent
Tom Smith | | agentic AI, AI coding agents, AI security, application security, Codex CLI, Codex Desktop, Codex Security, coding agent security, Developer Security, devsecops, Heapjack, OpenAI Codex, Overpatch, sandbox escape, sandbox security, Software Supply ChainTwo patched OpenAI Codex vulnerabilities, Heapjack and Overpatch, exposed how coding agents can escape sandboxes and reach developer systems without approval prompts ...
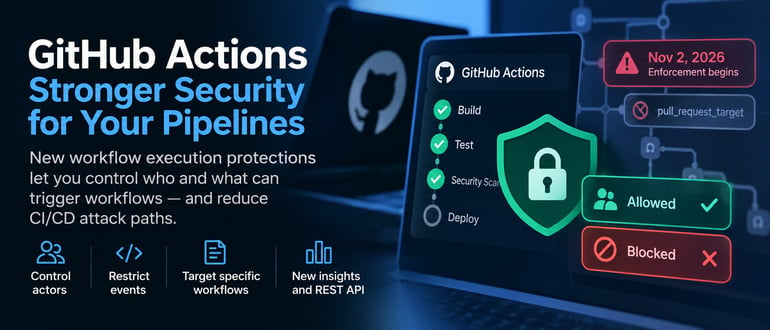
GitHub Separates Who Writes Code From Who Runs Your CI
Tom Smith | | Actions security, CI/CD security, devops, devsecops, github, GitHub Actions, GitHub Enterprise, GitHub security, pipeline security, pull_request_target, Repository Security, Software Supply Chain, supply chain security, workflow execution protections, workflow securityGitHub’s new workflow execution protections let teams control who and what can trigger Actions workflows, reducing CI/CD attack paths and tightening pipeline security ...
Why Your CI/CD Pipeline Is Your Most Unprotected Attack Surface
 Muhammad Yawar Malik | | application security, build agents, build pipelines, CI/CD security, Cloud Security, credential security, dependency security, deployment security, devops security, devsecops, ephemeral runners, GitHub Actions, infrastructure security, Jenkins security, least-privilege, pipeline security, provenance attestation, secrets management, secure pipelines, secure software development, software provenance, Software Supply Chain, supply chain attacks, third-party actions, XZ Utils
CI/CD pipelines often hold privileged credentials, execute third-party code and connect directly to production, making pipeline security one of the most overlooked risks in modern DevOps ...
More JFrog Artifactory Bugs Are Under Attack, and All Three Have Patches
Tom Smith | | administrative tokens, artifact repositories, authentication bypass, build pipeline security, CI/CD security, CVE-2026-42016, CVE-2026-42018, CVE-2026-82329, Cybersecurity, devsecops, Groovy plugins, JFrog Artifactory, patch management, privilege escalation, Repository Security, Rust backdoors, Software Supply Chain, vulnerability management, web shellsAttackers are actively exploiting three JFrog Artifactory flaws, exposing how slow patching can turn artifact repositories into software supply chain attack paths ...
GitLab’s Critical Patch Closes a Path Traversal Flaw Attackers Are Already Probing
Tom Smith | | access control, API security, CI/CD security, credential theft, CVE-2026-85706, CVE-2026-87719, CVSS 10.0, Cybersecurity, devops security, devsecops, gitlab, GitLab Duo, GitLab security, GraphQL security, patch management, Repository Security, self-managed GitLab, Software Supply Chain, vulnerability managementGitLab patches two critical flaws, including a CVSS 10.0 unauthenticated file-read vulnerability, putting self-managed instances under urgent pressure to upgrade ...

GitHub’s August Outages Show Growth Is Outpacing Infrastructure
Tom Smith | | AI coding agents, capacity planning, CI/CD, cloud infrastructure, developer infrastructure, developer productivity, devops, distributed systems, github, GitHub Actions, GitHub Copilot, GitHub outages, incident response, platform engineering, platform reliability, production resilience, retry storms, service availability, software delivery, Software Supply ChainGitHub's August 2026 report details five outages tied to Actions and Copilot growth outpacing infrastructure. Here's what platform teams should know ...

Why AI Agents Shouldn’t Guess at Vulnerability Exploitability
 Harish Gaggar | | AI agents, application security, SBoM, Software Supply Chain, vulnerability management, vulnerability prioritization
Vulnerability prioritization is not a language problem. The safest agent architectures use models to interpret and explain, while deterministic systems traverse the evidence. Ask a security team a simple question: Of the ...
EU-Funded CodeSupply Offers Grants for Open Source Software Supply Chain R&D
Jaime Hampton | | CodeSupply, devsecops, grants and funding, NLnet Foundation, open source, software security, Software Supply ChainSoftware supply chain, security and compliance tools all depend on accurate information about the packages they analyze, but that data is often fragmented across multiple sources and can be difficult to access ...

