

Running Experiments on a Busy Backend Without Taxing a Single Request
Once a product reaches a certain scale, A/B testing and cohort targeting stop being a nice-to-have. There are plenty of good commercial platforms for this, but at scale they push you into a trade-off: Pay a big vendor bill, or send your customers’ data to a third-party API just to figure out which button someone […]
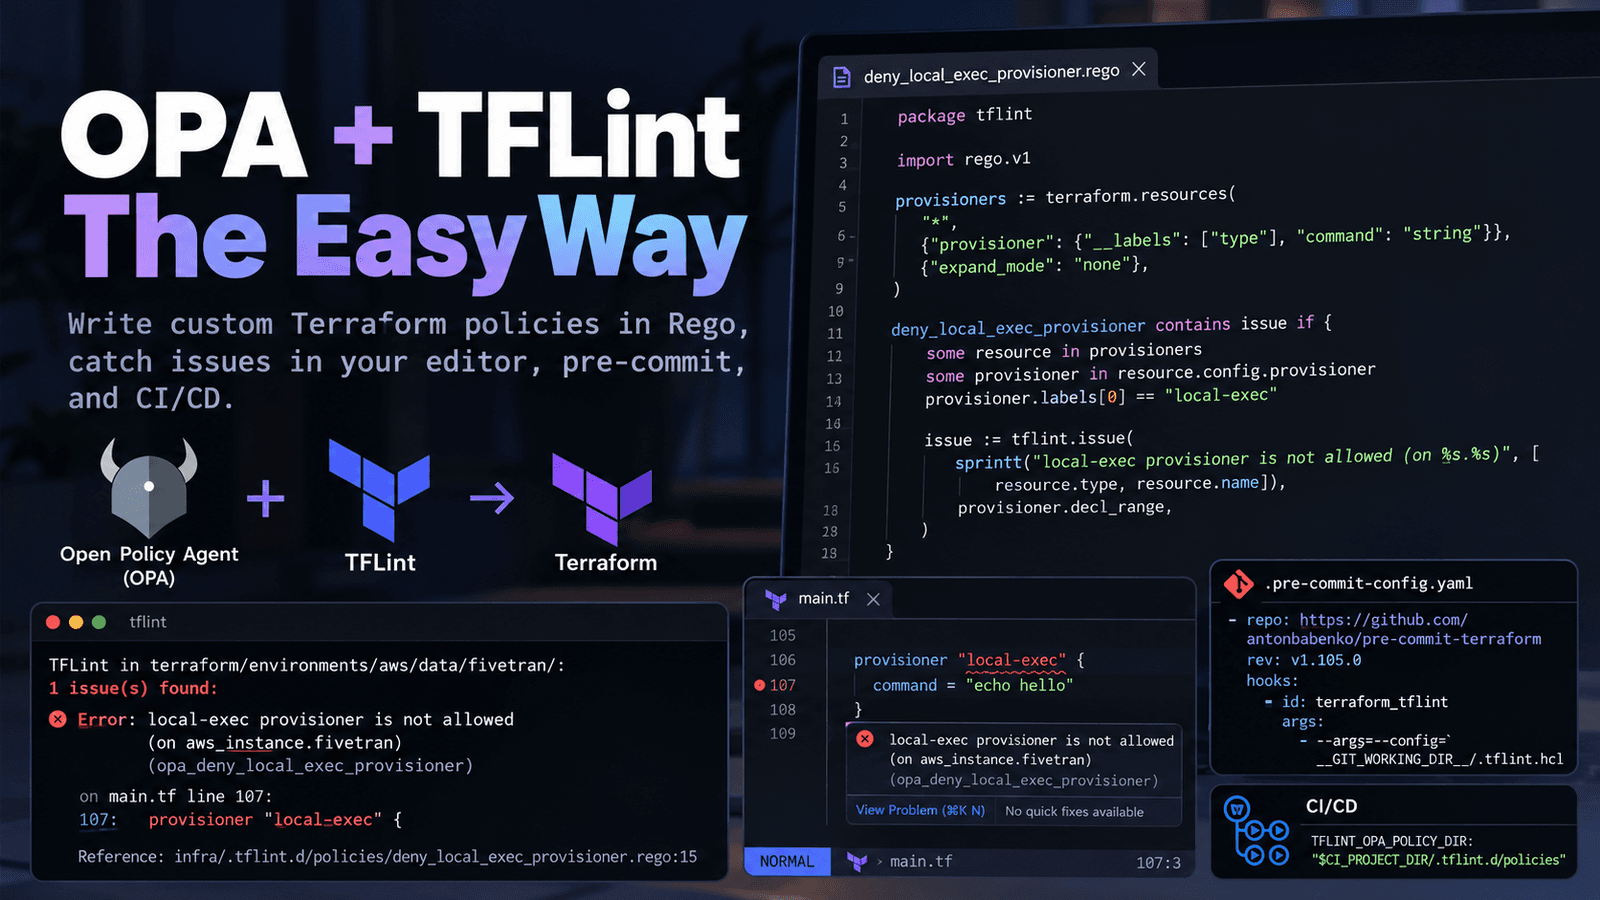
Implementing OPA with Terraform the Easy Way
Terraform compliance doesn’t have to mean complicated policy pipelines. By combining TFLint with OPA and Rego, developers can enforce infrastructure guardrails directly in their editors, pre-commit hooks and CI/CD workflows, catching violations before deployment.
Recursive Flint Puts a Fast Agentic Coding Model on Developers’ Laptops
Recursive has unveiled Flint, a 40-billion-parameter, open-weight coding model designed to run locally on developer hardware. Built with help from the company’s Eureka Machine research system, Flint promises faster inference, greater source-code privacy and freedom from per-token API fees. For DevOps teams, the launch raises fresh questions about AI agent governance, code quality and continuous model evaluation.
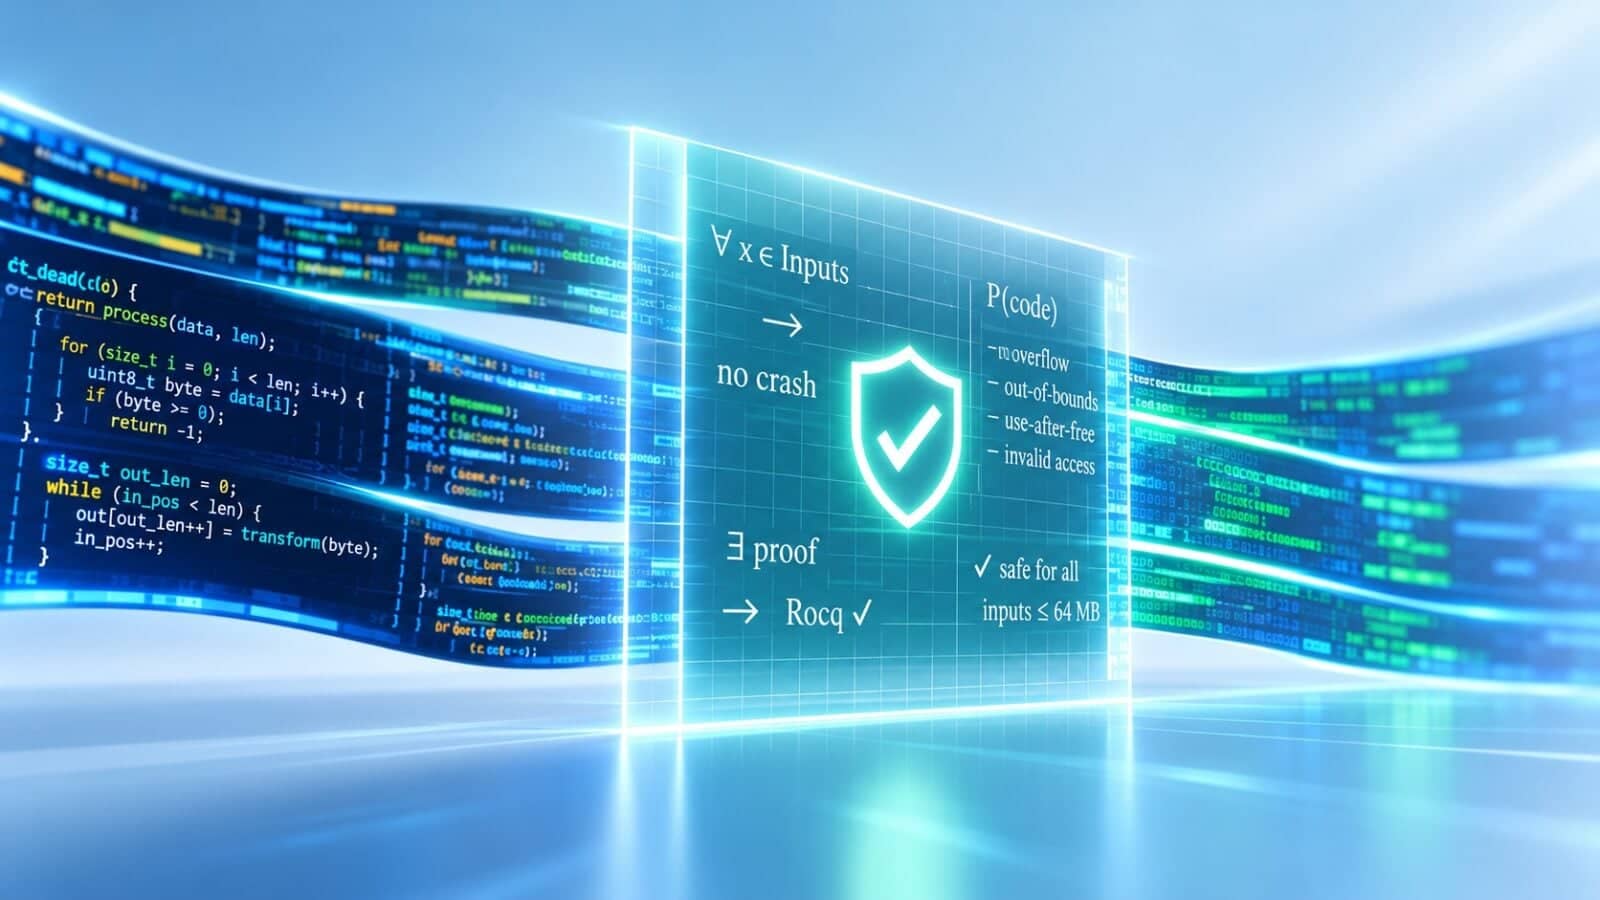
Claude Writes 180 Million Lines of Proofs to Verify 123 Open Source Libraries
Formal verification has long been the gold standard for software correctness. It has also been too expensive for almost everyone. New research from Anthropic suggests that’s changing. Anthropic’s Frontier Red Team, working with formal methods company Theorem, used Claude to prove security properties in the compiled code of 123 open-source libraries from Google’s OSS-Fuzz project. […]
Report: AI Agents Increase Observability Costs
Cisco has released its Splunk State of Observability 2026 report, revealing that companies face growing costs and operational challenges as they deploy AI agents without sufficient monitoring capabilities. The report found that 57% of organizations spend more on telemetry, the data used to monitor IT systems, than on the infrastructure being monitored. Additionally, 55% of […]
When 200 OK Isn’t OK: Observability for LLM Systems
Traditional monitoring can show an LLM-powered application as healthy even when it delivers incorrect answers. Drawing on experience at Varo Bank, this article explains why AI observability must go beyond the four golden signals and how automated evaluation, groundedness checks and CI pipelines can catch silent failures before they reach customers.
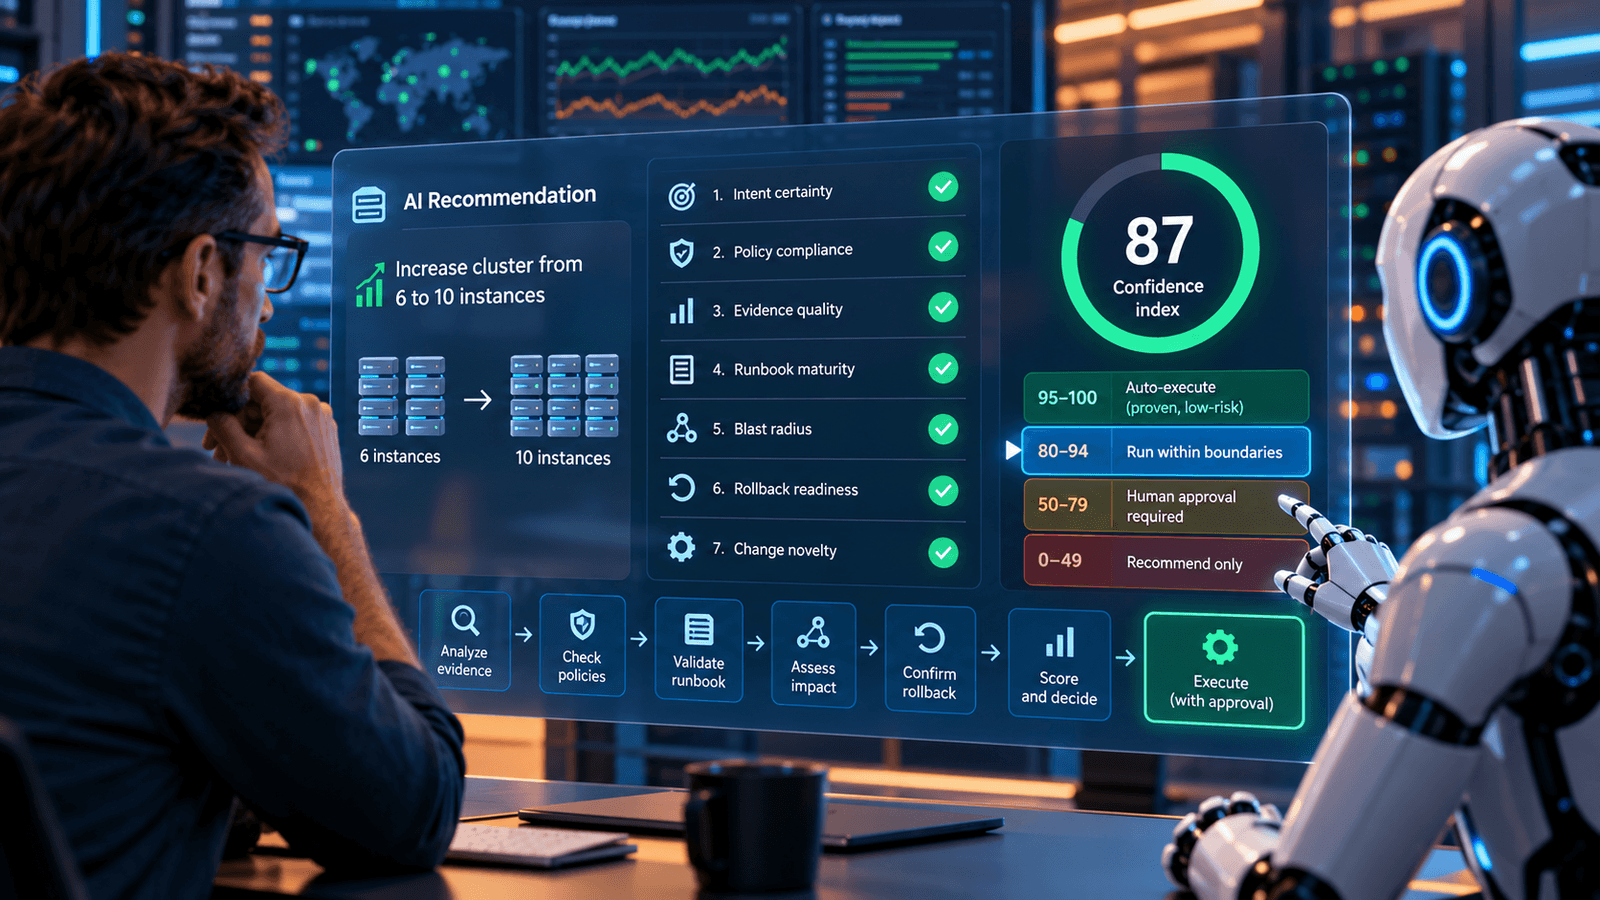
The Automation Confidence Gap: When Should AI Be Allowed to Change Production?
AI-generated infrastructure recommendations can look convincing, but production execution requires more than a plausible runbook. A seven-factor confidence index helps platform teams determine when AI should recommend, seek approval or execute changes within strictly enforced boundaries.
Hackers Inject Credential-Stealer, RAT Into LiteLLM
Attackers compromised a version of LiteLLM this week by injecting malicious code into all seven of its published Python wheels on PyPI, delivering a package that included an infostealer to exfiltrate credentials and secrets and a remote access trojan (RAT) that could let bad actors run arbitrary code on infected machines. The compromised version – […]
Linux Foundation: AI Speeds Development, but Low-Quality Code Strains Maintainers
A new Linux Foundation study finds that generative AI is delivering big productivity gains for open source software developers, but AI is also creating an influx of low-quality code submissions that need time-consuming human review. The research found that an estimated 25% of incoming pull requests, which are proposed changes to software projects, are considered […]
What Comes After the Pull Request?
We’ve spent plenty of time figuring out how to fit agents into the existing software development lifecycle. But the pull request was designed for humans to coordinate with other humans. If agents can generate, review, and validate changes continuously as they work, why do we need a separate interaction point at all? I’m not convinced […]
How Dependency Mocking Affects CI/CD Pipeline Reliability
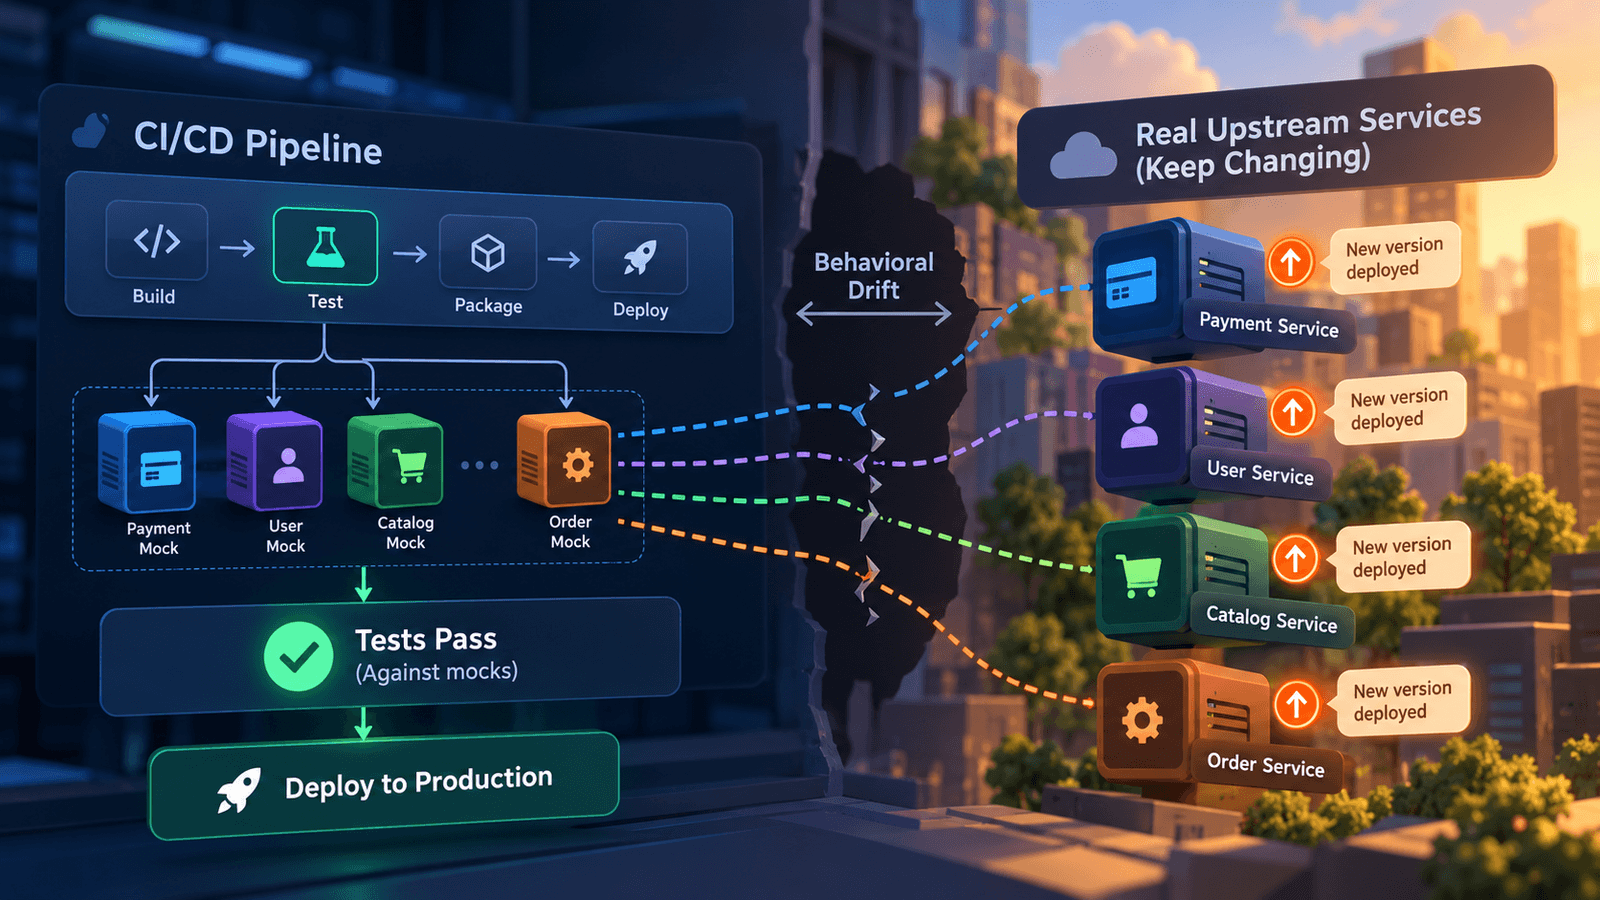
Stale dependency mocks can make CI/CD pipelines pass while production integrations fail. Learn how mock drift undermines reliability and how to prevent it.
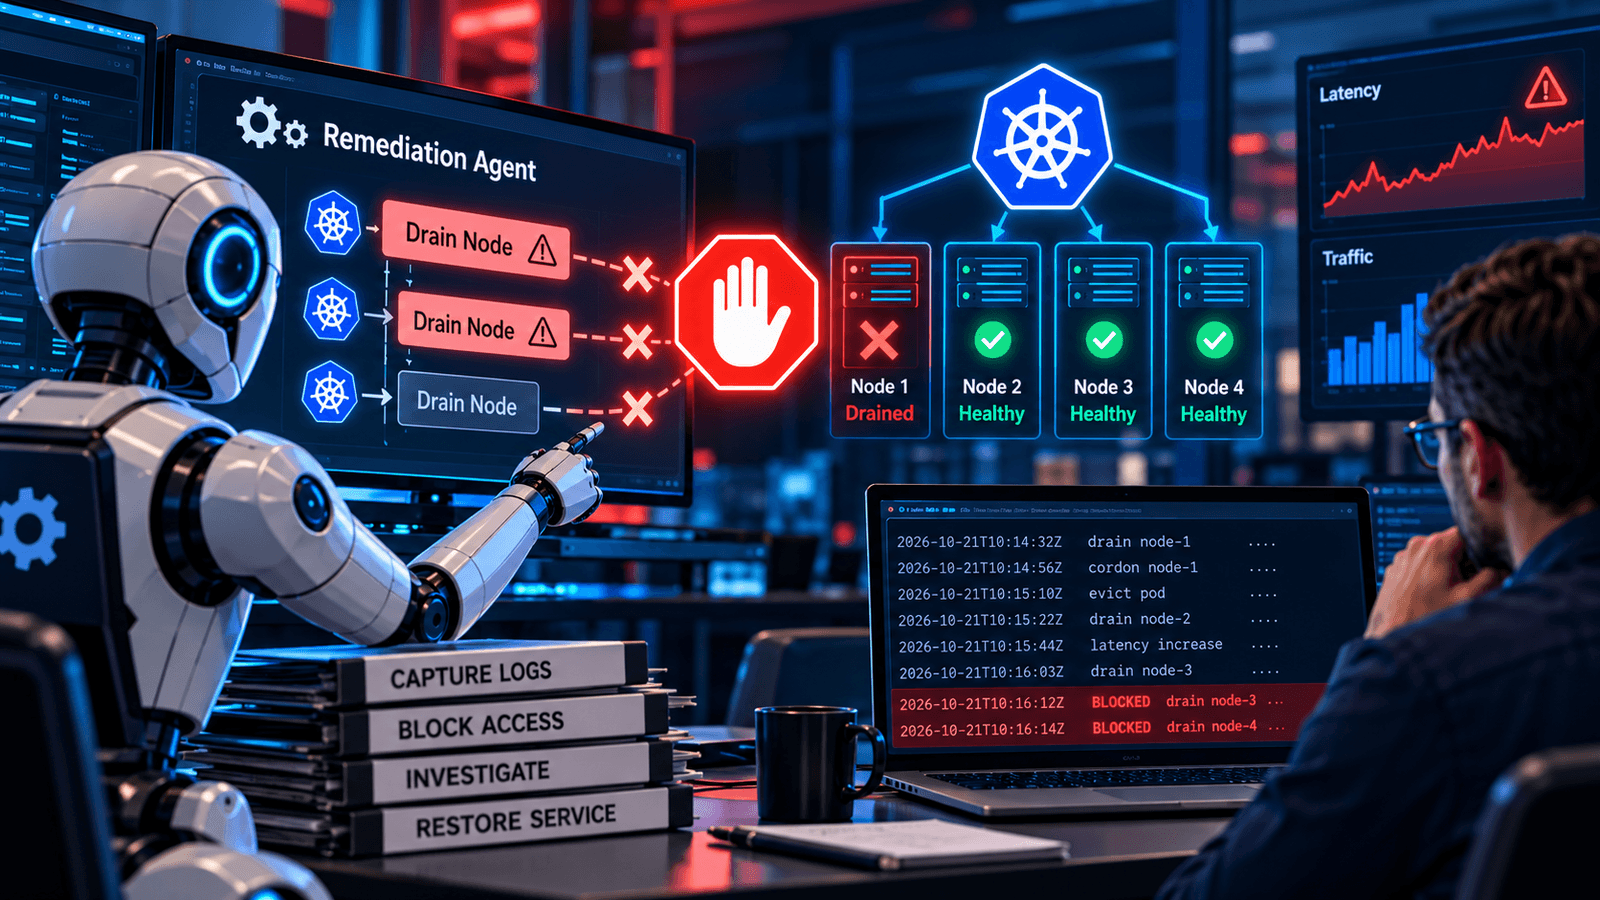
When the Agent is the Incident
When AI remediation agents make the wrong infrastructure decisions, automated fixes can quickly escalate into major incidents. This seven-step incident response playbook explains how to stop unsafe agent actions, block tool access, preserve forensic evidence and restore services without triggering further damage. A Kubernetes simulation demonstrates why stopping an agent worker alone is not enough.
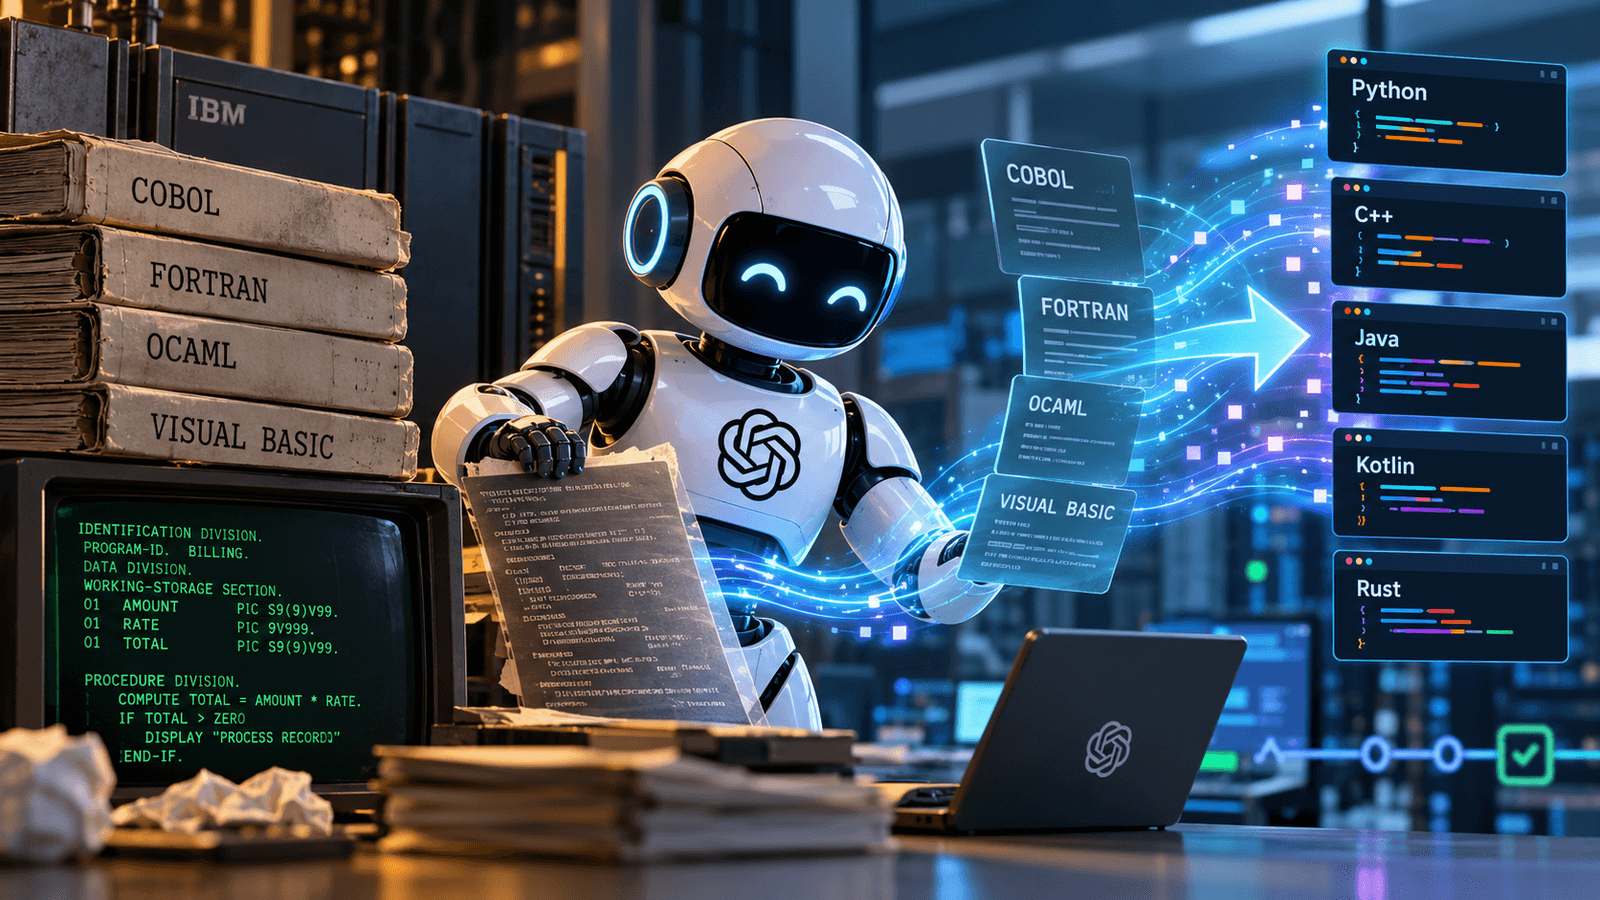
OpenAI Puts COBOL Migration to the Test, and Its Newest Models Mostly Pass
OpenAI’s latest coding benchmarks show substantial improvements in handling COBOL, Fortran and other low-resource languages. But for DevOps teams modernizing legacy applications, translating code is only half the challenge. The real test is preserving business logic, arithmetic precision and production behavior.
Survey: AI Coding Tools Increase Open Source Software Dependencies
A survey of 307 enterprise technology leaders finds that as organizations rely more on artificial intelligence (AI) coding tools to build applications, they are simultaneously increasing the amount of open source software they are dependent on. Conducted by the market research firm Moving Horizon on behalf of ActiveState, a provider of a platform for accessing […]
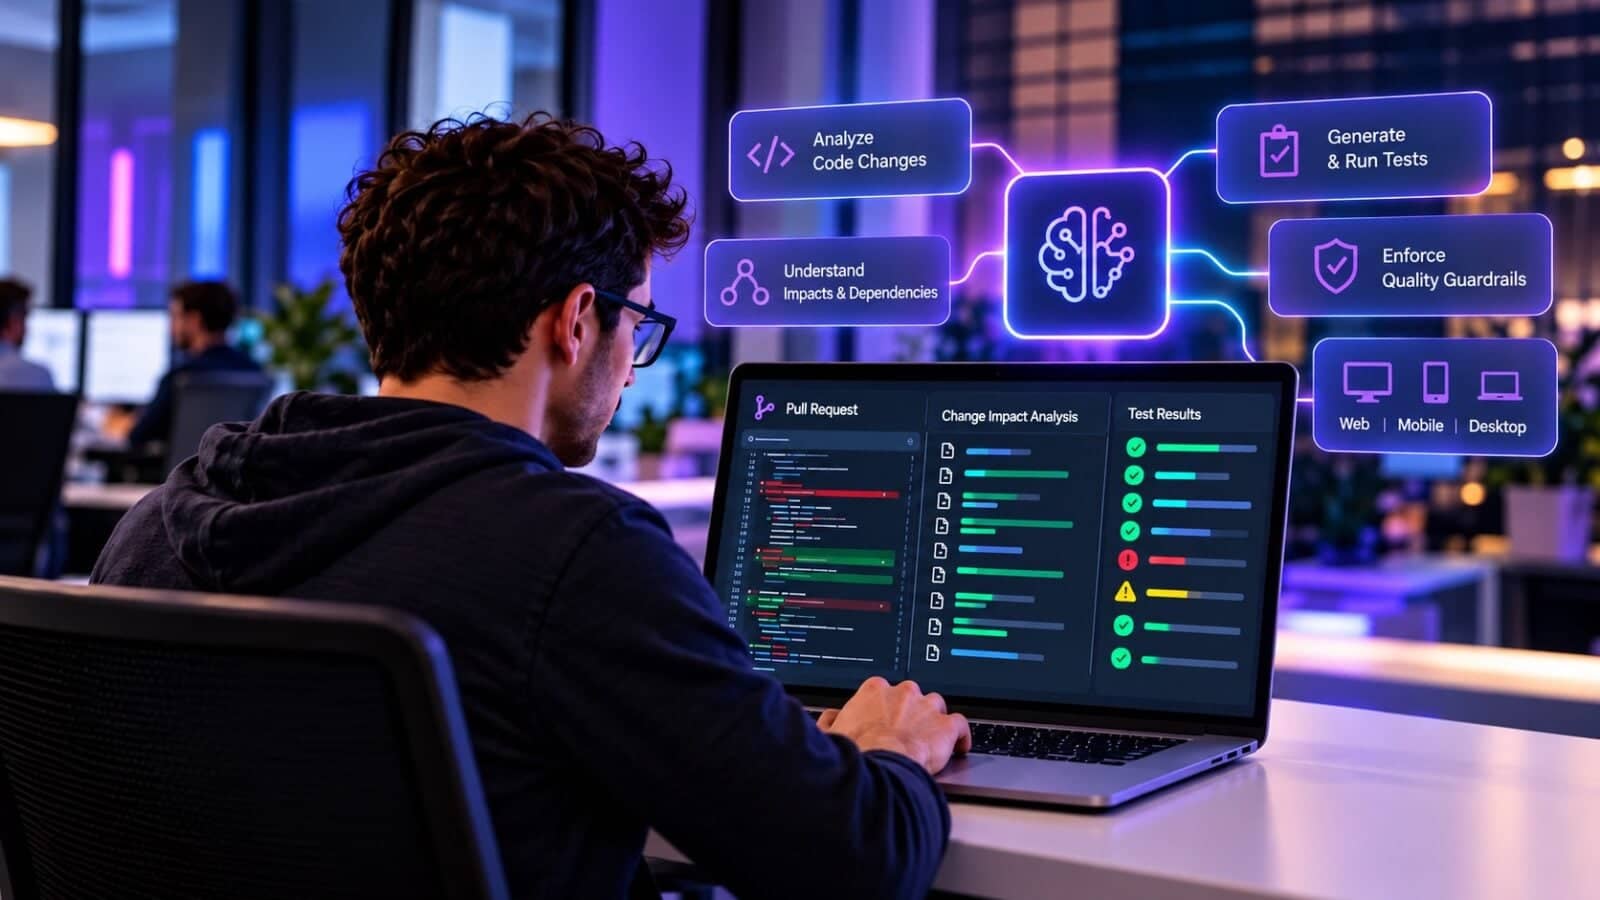
mabl Adds Harness to AI Testing Automation Platform
Mabl today extended its test automation platform with a harness that, in addition to enforcing guardrails and testing standards for artificial intelligence (AI) agents, enables application development teams to better understand the impact of code changes before a pull request (PR) is made. Announced at a mabl Experience event, the extensions to the test automation […]
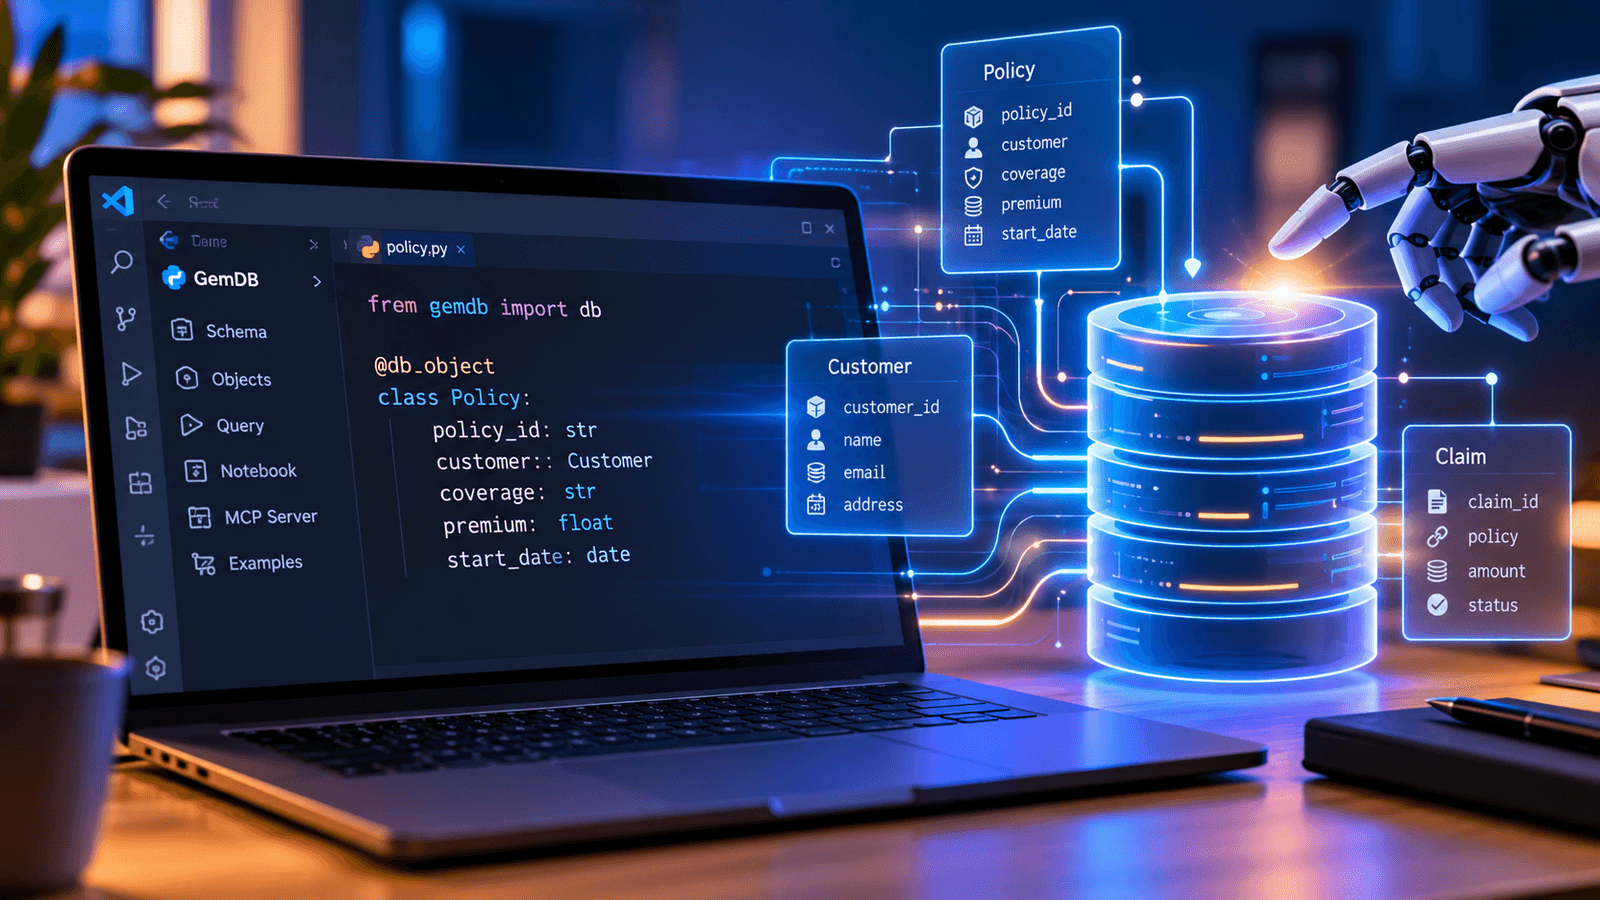
GemDB Extension Uses Code to Update Database
GemDB has introduced a Visual Studio Code extension that enables developers and AI coding agents to create, modify and persist database objects directly through Python code. With integrated Jupyter Notebook and MCP support, GemDB Code aims to eliminate traditional schema migrations, simplify database management and accelerate DevOps workflows.
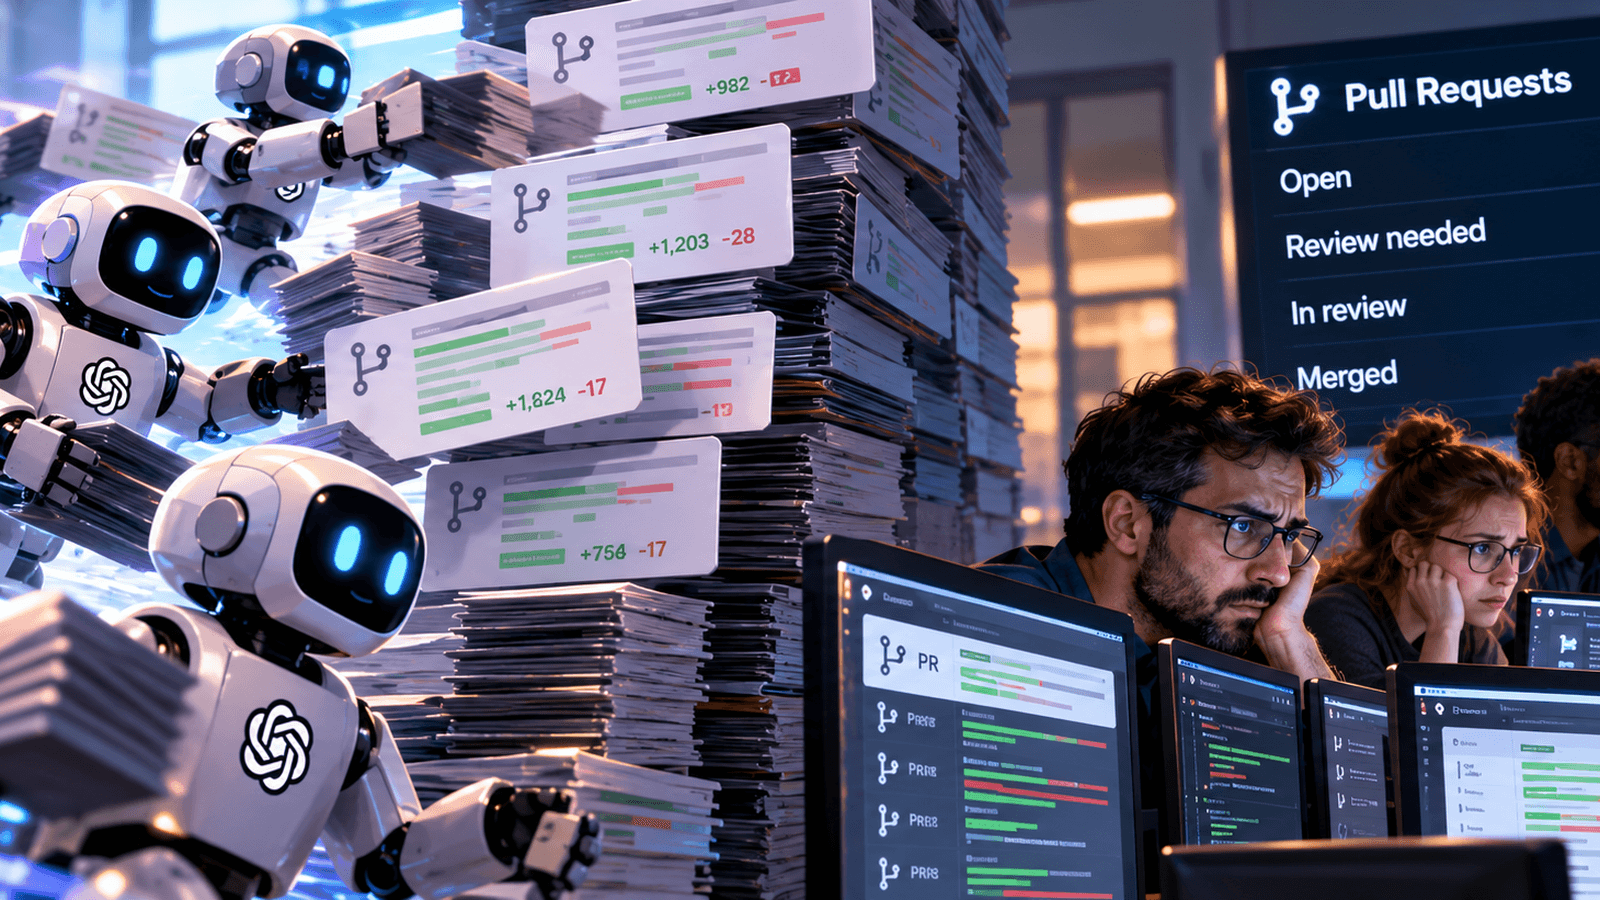
Coding Agents Moved the Bottleneck From Writing to Reviewing PRs
AI coding agents are generating more pull requests than developers can review. Learn why review bottlenecks create quality debt and how DevOps teams can respond.
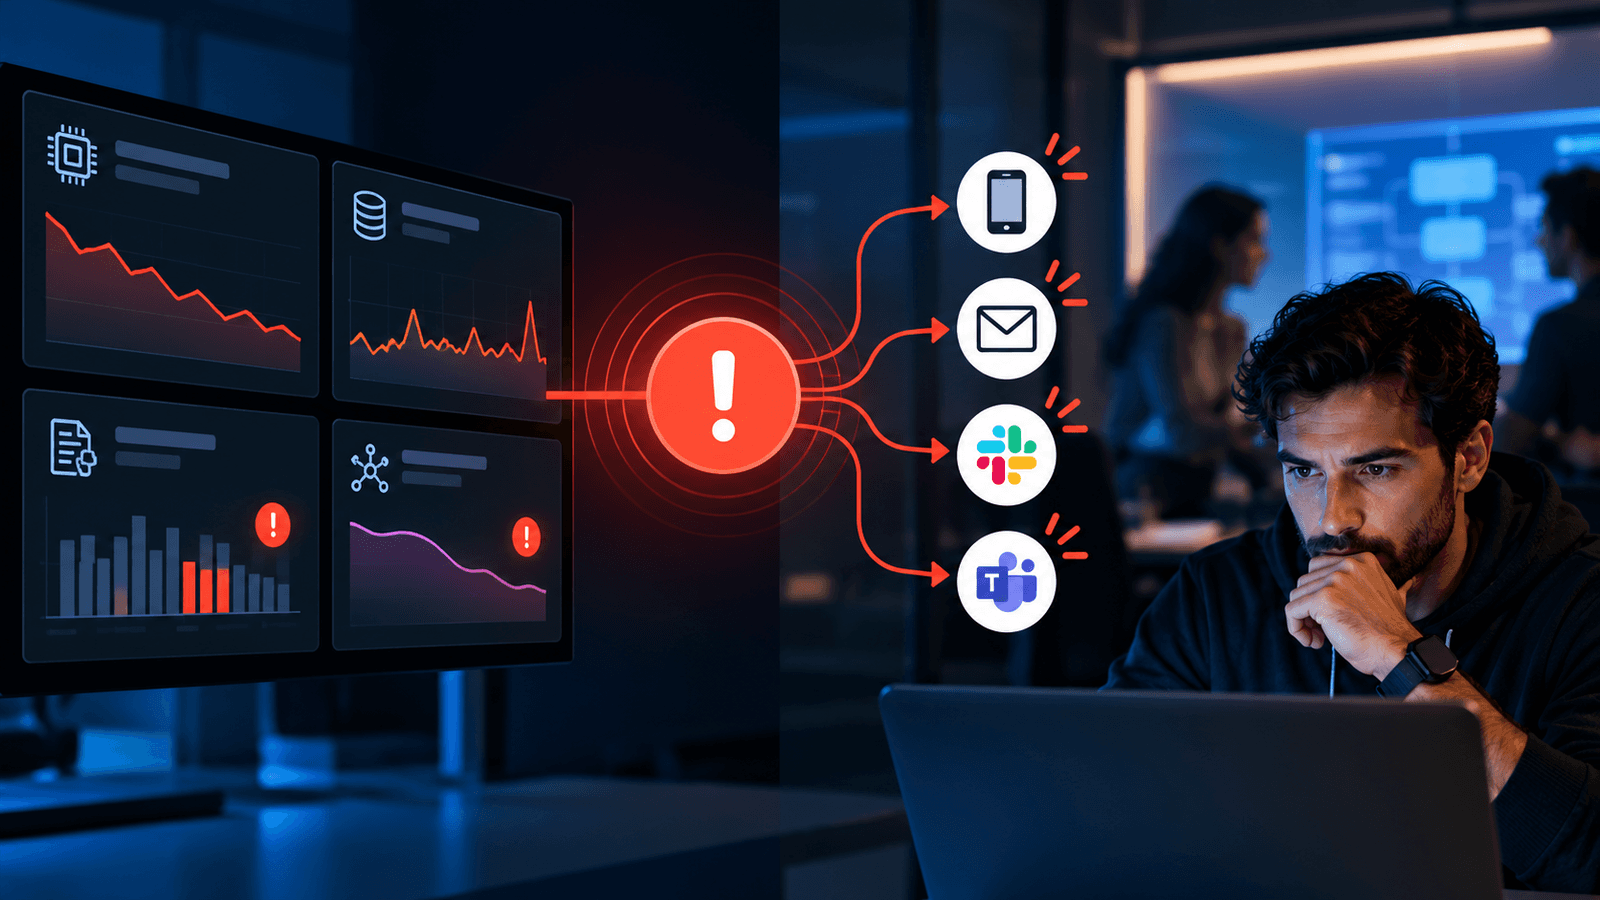
Navigating AI Infrastructure Incidents: Bridging the Critical Gap Between Detection and Response
AI systems can appear healthy while response quality, latency and data freshness deteriorate. Advanced observability tools can detect these issues, but identifying a problem is only half the battle. Engineering teams must close the gap between detection and response with persistent alerts, intelligent routing and automated escalation to reduce downtime and restore output integrity.
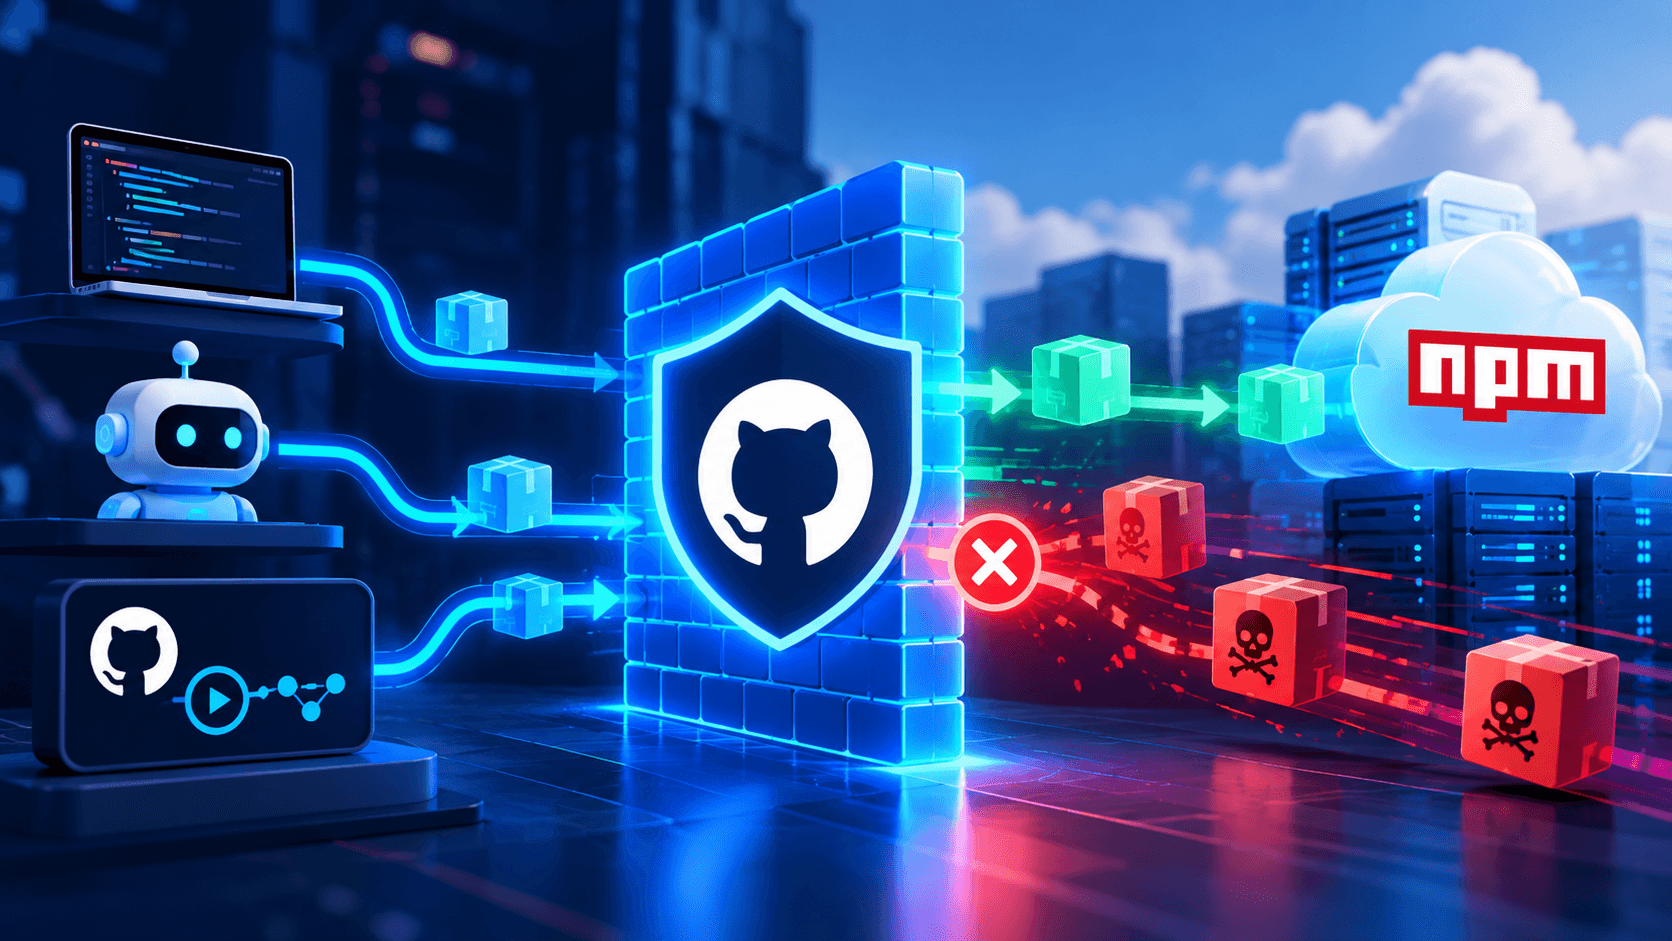
GitHub Puts a Firewall Between npm and Your CI Runners
GitHub’s new package firewall puts enterprise security policies between npm registries and the developers, CI runners and AI coding agents consuming packages. With malware detection, attestation checks and package-age restrictions, it aims to stop malicious dependencies before installation.
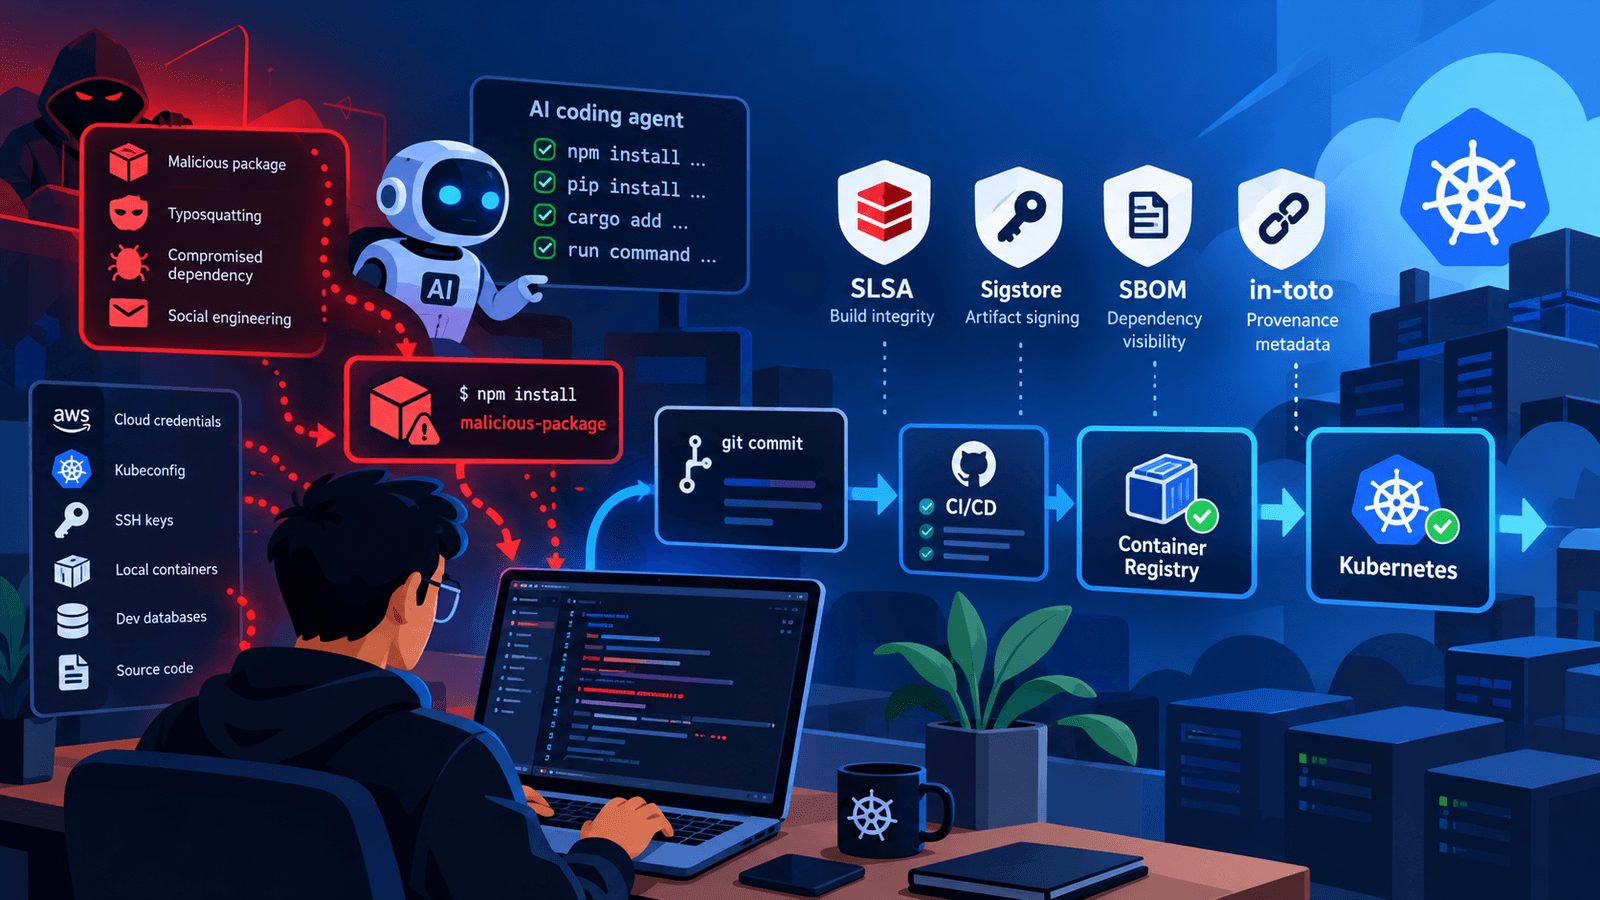
Beyond SLSA and Sigstore: Securing the Developer Origin in the Age of Agentic Coding
SLSA, Sigstore and SBOMs have strengthened software supply chain security, but attackers are increasingly targeting developer workstations before code reaches the CI/CD pipeline. With autonomous AI coding agents installing dependencies, executing commands and accessing sensitive credentials, endpoint security is becoming a critical cloud-native concern. Securing the software supply chain now requires protection from the developer’s IDE all the way to Kubernetes production workloads.
AI Agents Can Now Take Software Apart. DevOps Teams Need a Plan
AI-powered reverse engineering is making it easier to understand and rebuild software without source code. Tools such as REA and increasingly capable AI models create opportunities for legacy modernization while raising fresh concerns about intellectual property, application security and functional correctness.
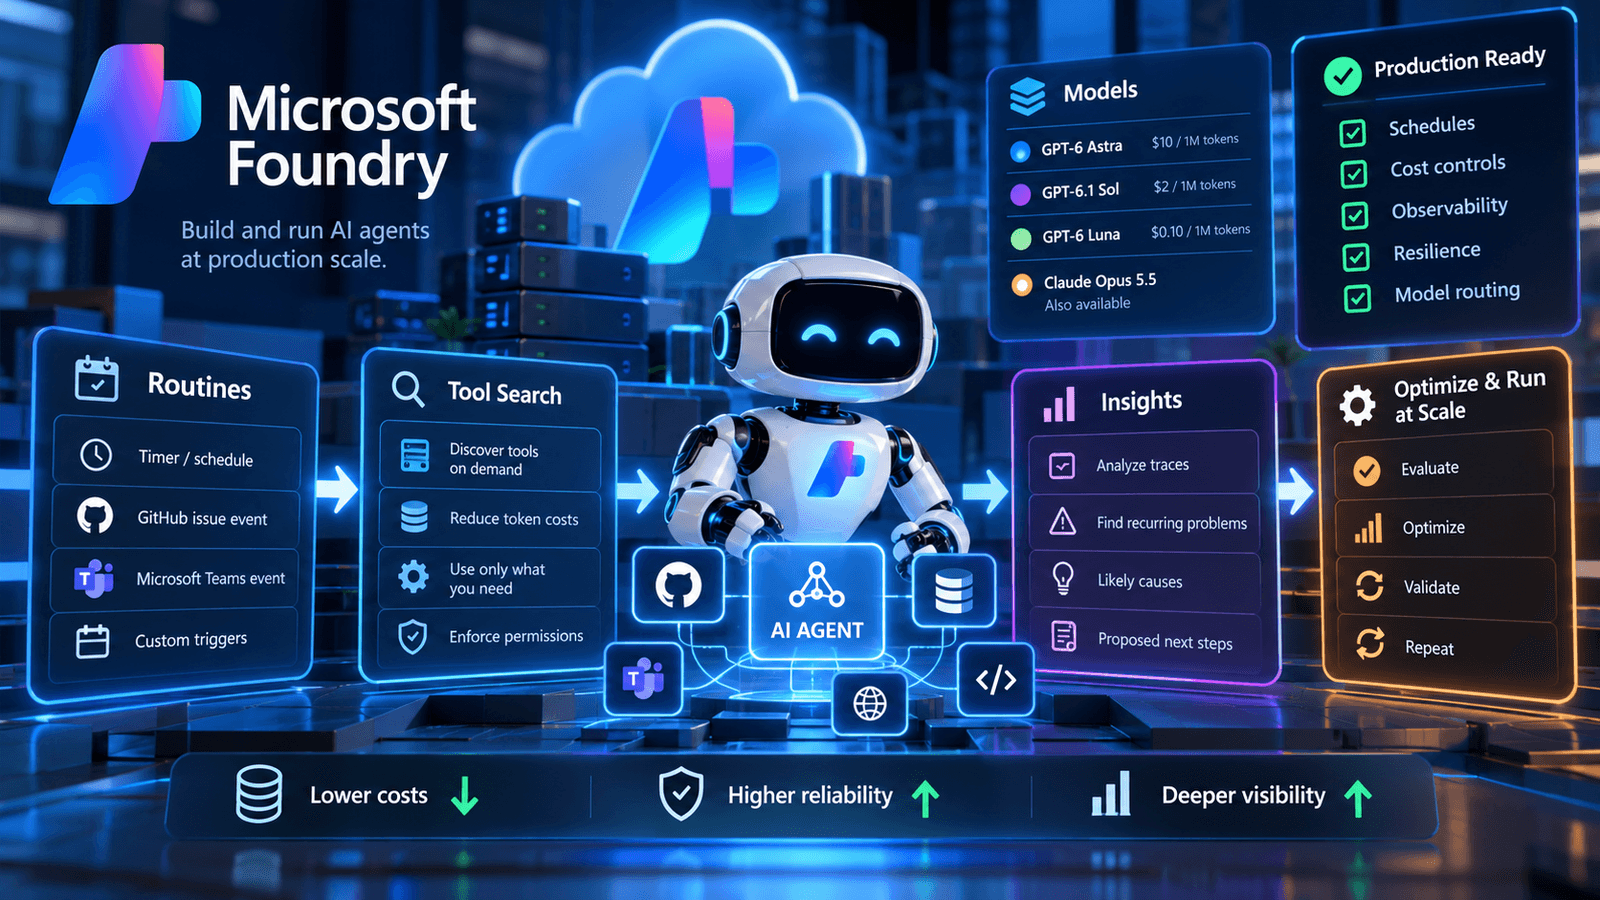
Microsoft Foundry Puts AI Agents on a Schedule and Under Watch
Microsoft’s September Foundry updates focus on making AI agents production-ready with automated routines, lower token costs, trace-based insights and improved resilience. For DevOps teams, the changes bring agent operations closer to familiar CI/CD and observability practices.
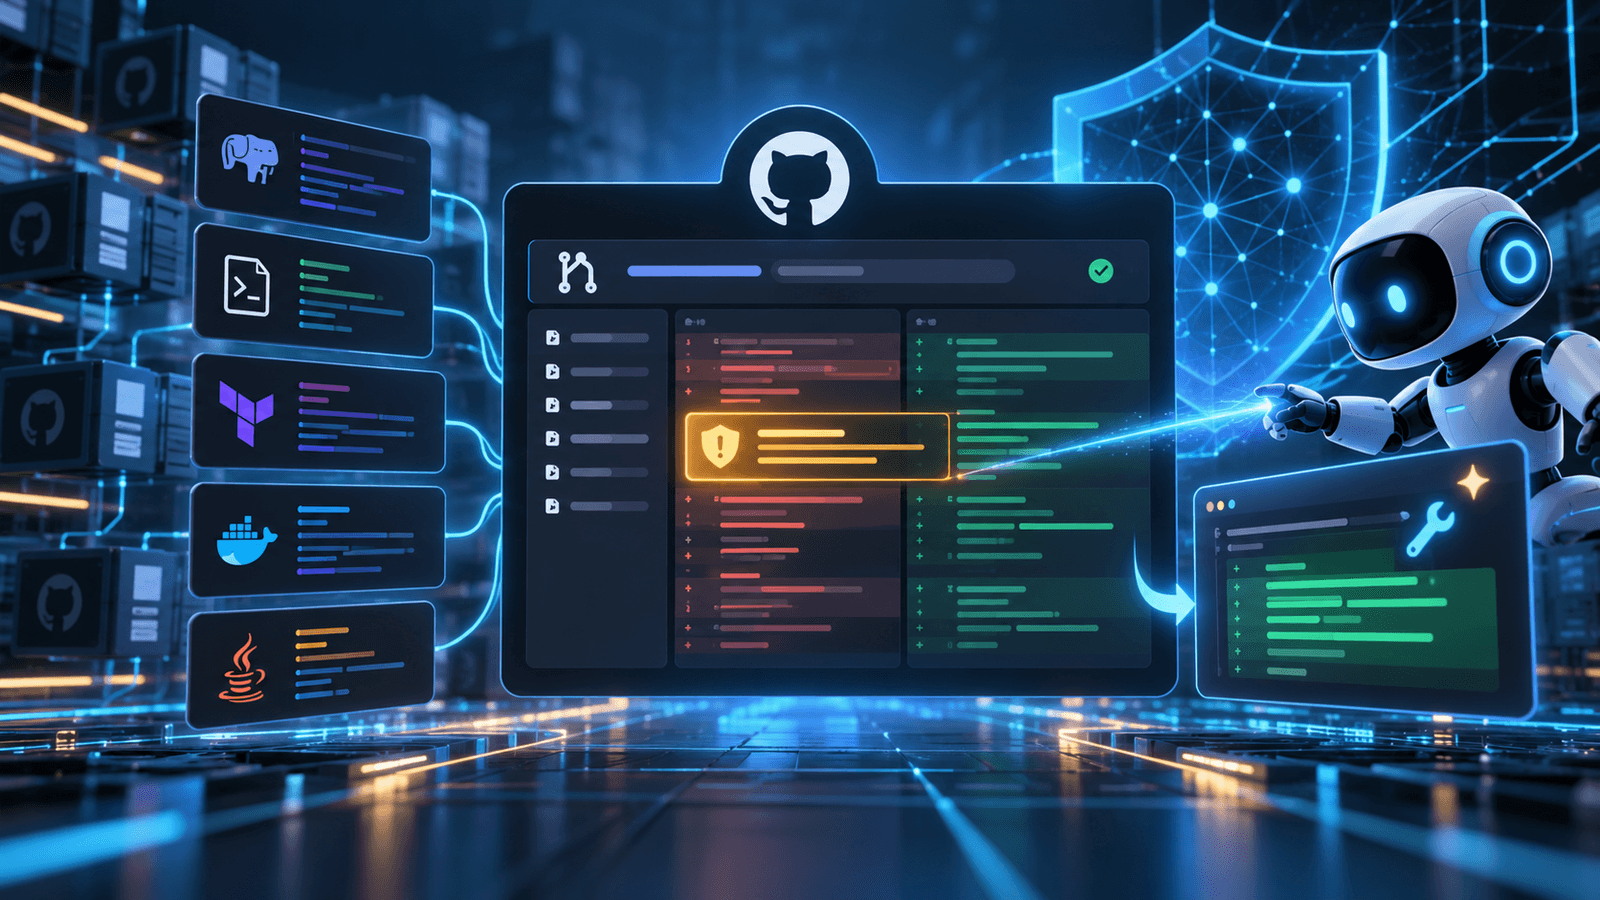
GitHub Brings AI Security Scanning to Pull Requests CodeQL Can’t Cover
GitHub’s AI Scan brings AI-powered vulnerability detection to pull requests involving languages, scripts and infrastructure files beyond CodeQL’s existing coverage. Paired with the general availability of agentic autofix, the release expands security automation across the development lifecycle. But advisory-only findings, coverage gaps and AI credit consumption mean DevOps teams still need clear review policies.