Tag: Software Supply Chain Security
Why Software Supply Chain Security Is Moving to the Gate

March 2026: malicious versions of axios get published directly to npm. May 2026: attackers forge valid provenance for 42 TanStack packages on npm, with 84 malicious versions shipped before detection. August 2026: ...
GitHub Gives Enterprises a Full Count of Who Holds the Keys
 Tom Smith | | access management, agentic AI, AI coding agents, credential inventory, credential security, Developer Security, devsecops, github, GitHub Apps, GitHub Enterprise Cloud, identity security, least-privilege, OAuth tokens, PATs, Personal Access Tokens, secrets management, security operations, Software Supply Chain Security, SSH keys
GitHub Enterprise Cloud now lets organizations export a full inventory of credentials, helping security teams identify stale, overprivileged and forgotten access across users, apps and automation ...
Cycode Extends DevSecOps Reach to Software Packages Developers Download
 Mike Vizard | | ADLC, agentic development lifecycle, AI coding agents, cool down period, Cycode, dependency security, Developer Security, devsecops, malicious packages, package security, software repositories, Software Supply Chain Security, supply chain attacks, threat intelligence, workstation protection
Cycode is adding workstation-level protection to stop developers and AI coding agents from downloading malicious or insufficiently vetted software packages ...
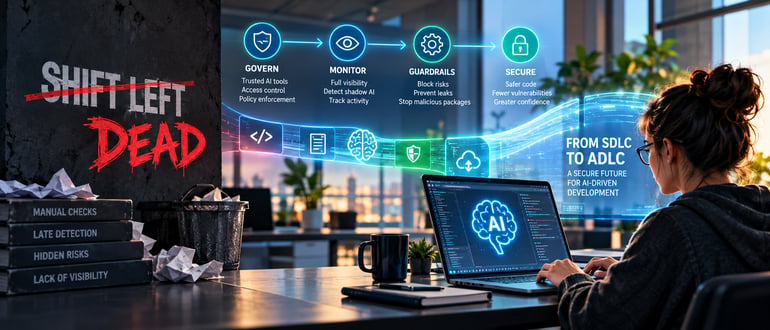
Why Shift Left is Dead
 Devin Maguire | | ADLC, agentic development lifecycle, AI Governance, AI guardrails, AI security, AI-Driven Development, AI-generated code, application security, Developer Security, devsecops, prompts, sdlc, secure software development, shadow ai, shift left security, Software Supply Chain Security
AI-driven development is exposing risks before code is written, forcing security teams to move beyond shift-left and govern agents, prompts, tools and data across the entire development lifecycle ...

GitHub Widens the Door on Advanced Security Trials
Tom Smith | | AI coding, application security, CodeQL, Developer Security, devsecops, exposed credentials, GHAS, GitHub Advanced Security, GitHub Code Security, GitHub Enterprise Cloud, GitHub Secret Protection, GitHub security, mid-market security, Repository Security, secret scanning, secure software development, Software Supply Chain Security, vulnerability scanningGitHub raised its self-serve Advanced Security trial cap from 100 to 300 licenses, letting more mid-size Enterprise Cloud orgs test for free ...
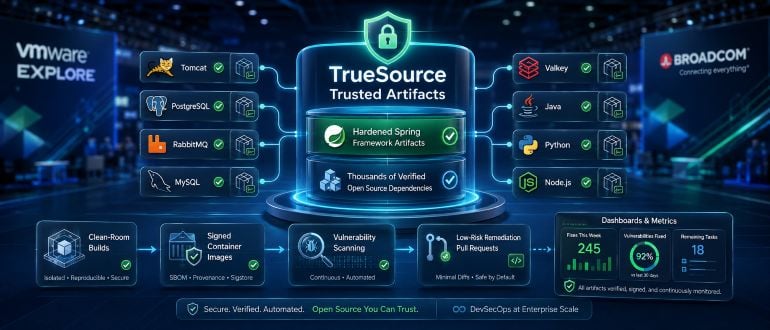
Broadcom Launches TrueSource Service to Secure Spring Framework
Mike Vizard | | AI coding, Apache Tomcat, application security, Bitnami Secure Images, Broadcom, container security, dependency security, devsecops, java, kubernetes, node.js, open source security, open source vulnerabilities, patch management, Python, SBoM, secure software development, software artifacts, Software Supply Chain Security, Spring framework, Spring Security, Tanzu, TrueSource Trusted Artifacts, VMware explore, vulnerability managementBroadcom launches TrueSource Trusted Artifacts to provide hardened Spring dependencies, secure open source packages and automated vulnerability remediation ...
Why Cryptographic Inventory Is the First Step Toward Quantum Readiness
 Michael Carter | | CBOM, CI/CD security, crypto-agility, cryptographic dependencies, cryptographic discovery, cryptographic inventory, cryptography bill of materials, devops security, devsecops, Kubernetes security, ML-KEM, NIST PQC migration, post-quantum cryptography, PQC, quantum readiness, Software Supply Chain Security
Post-quantum readiness starts with visibility. DevOps teams need a continuous cryptographic inventory to map algorithms, keys, certificates, libraries, infrastructure and third-party dependencies before PQC migration begins ...
The Agent Proposes, the Pipeline Disposes: Controls for AI-Authored Change
 Veera Ravindra Divi | | agent permissions, agentic coding, AI change control, AI code review, AI coding agents, AI Governance, AI pull requests, AI software development, AI-authored code, AI-generated code security, autonomous coding agents, bounded-write agents, change-budget gates, CI/CD security, human-in-the-loop, in-toto, independent evals, least-privilege, policy as code, protected paths, provenance attestation, provenance verification, Secure DevOps, signed attestations, Sigstore, SLSA, Software Supply Chain Security, staged autonomy
When agents write code and open pull requests faster than humans can read them, ‘the diff looked fine’ stops being a control. The durable controls live outside the agent’s reasoning loop ...

Shift Left Security: 4 Automated Security Gates in GitHub Actions
 Zia Ullah | | automated security testing, CI/CD security gates, CodeQL, container image scanning, CVE detection, DAST, dependency scanning, DevSecOps pipeline, Dynamic Application Security Testing, GitHub Actions security, Node.js security, npm audit, OWASP ZAP, SAST, shift left security, Snyk, Software Supply Chain Security, Static Application Security Testing, Trivy, vulnerability scanning
Learn how to add four automated security gates to GitHub Actions using npm audit, Snyk, Trivy, CodeQL and OWASP ZAP—without an enterprise licence ...
CISA’s 2026 SBOM Guidance Adds Hash Requirements and AI Coverage
Tom Smith | | AI supply chain security, CISA, CISA SBOM 2026, CMMC, component hashes, component licensing, continuous SBOM validation, CycloneDX, FBI, FedRAMP, NSA, open source security, SaaS security, SBOM automation, SBOM minimum elements, software bill of materials, software procurement, Software Supply Chain Security, software transparency, SPDX, vendor risk managementCISA’s updated 2026 SBOM minimum elements expand software transparency requirements to AI, SaaS and open source while adding hashes, licenses and stronger validation ...
GitHub and PyPI Bet On Time to Slow Down Software Supply Chain Attacks
Tom Smith | | automated updates, CI/CD security, dependency cooldown, dependency pinning, dependency updates, devops security, GitHub Dependabot, lockfiles, malicious packages, open source security, package poisoning, package registry security, platform engineering, PyPi, Python Package Index, scoped access tokens, Software Supply Chain Security, supply chain attacksGitHub and PyPI are using time as a security control, delaying dependency updates and locking older releases against new file uploads ...

Signed, Attested, and Malicious: The Software Supply Chain Has a Deepfake Problem
 Nigel Douglas | | AI coding agents, AntV packages, behavioural analysis, continuous scanning, dependency security, Developer Security, GitHub Actions compromise, malicious packages, Miasma worm, Mini Shai-Hulud, npm malware, OIDC tokens, open source security, package provenance, package quarantine, policy as code, Red Hat npm attack, registry scanning, Shai-Hulud worm, SLSA provenance, software attestation, Software Supply Chain Security, TanStack compromise, trusted pipeline attacks
A developer pulls a package from a reliable repo. It is signed, has provenance, and has been scanned. And then…it contains malware. That is no longer hypothetical. When the Miasma worm tore ...

