

Diagrid Updates Dapr Runtime for the Agentic AI Era
Diagrid at the KubeCon + CloudNativeCon North America 2026 conference has made available an update to the open source Distributed Application Runtime (Dapr) that makes it possible to deploy artificial intelligence (AI) agents in a way that consumes infrastructure resources more efficiently. The Dapr framework is based on Actors that are used to build stateful, […]
How AI SRE Agents Are Changing Observability and Incident Response
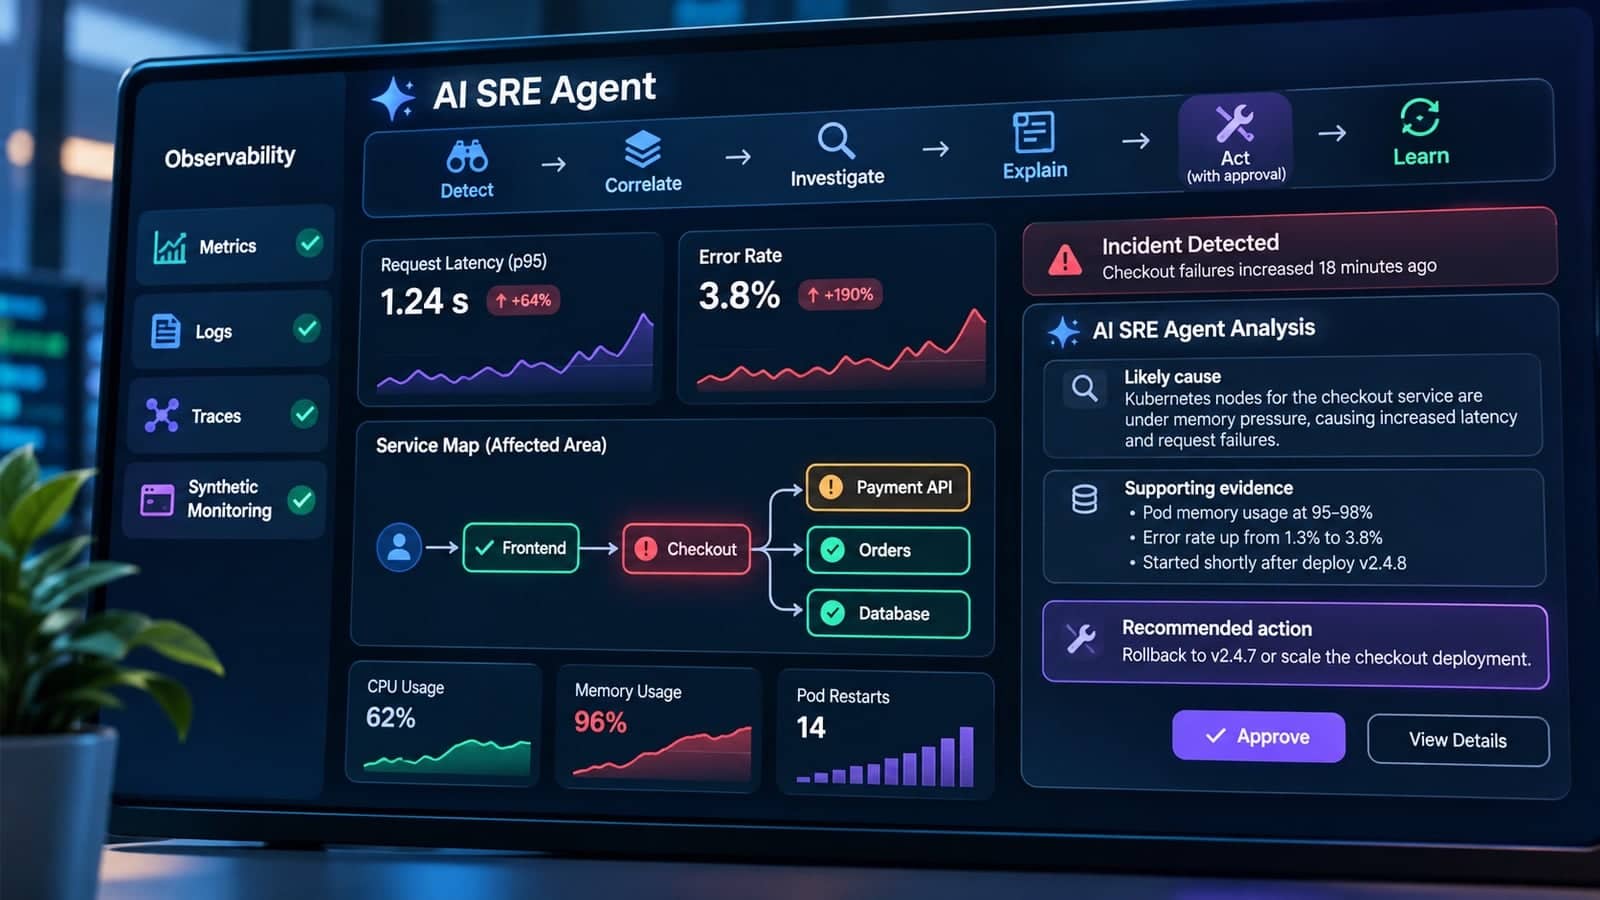
Modern systems fail in ways that dashboards were never designed to explain. A single checkout failure can trace back to a Kubernetes node under memory pressure, a slow third-party API, or a log line nobody was watching. Teams now run hundreds of services, thousands of containers and millions of telemetry events per minute. Humans can […]
Why We Do What We Do
“Simplicity means that the smallest solution that solves the entire problem is the best solution. It keeps the systems easy to understand and reduces complex component interactions that can cause debugging nightmares.” — The Practice of System and Network Administration In every infrastructure codebase I maintain, there’s a directory called docs/adr. It’s where I keep […]
Blitzy Partners with Microsoft Frontier Company to Bring AI to Azure Workload Migrations
Blitzy, a provider of an artificial intelligence model that establishes the relationship between all the software artifacts in an IT environment, today announced it has allied with the Microsoft Frontier Company to help DevOps teams refactor existing applications in a way that makes it simpler to move them to the Microsoft Azure cloud service. As […]
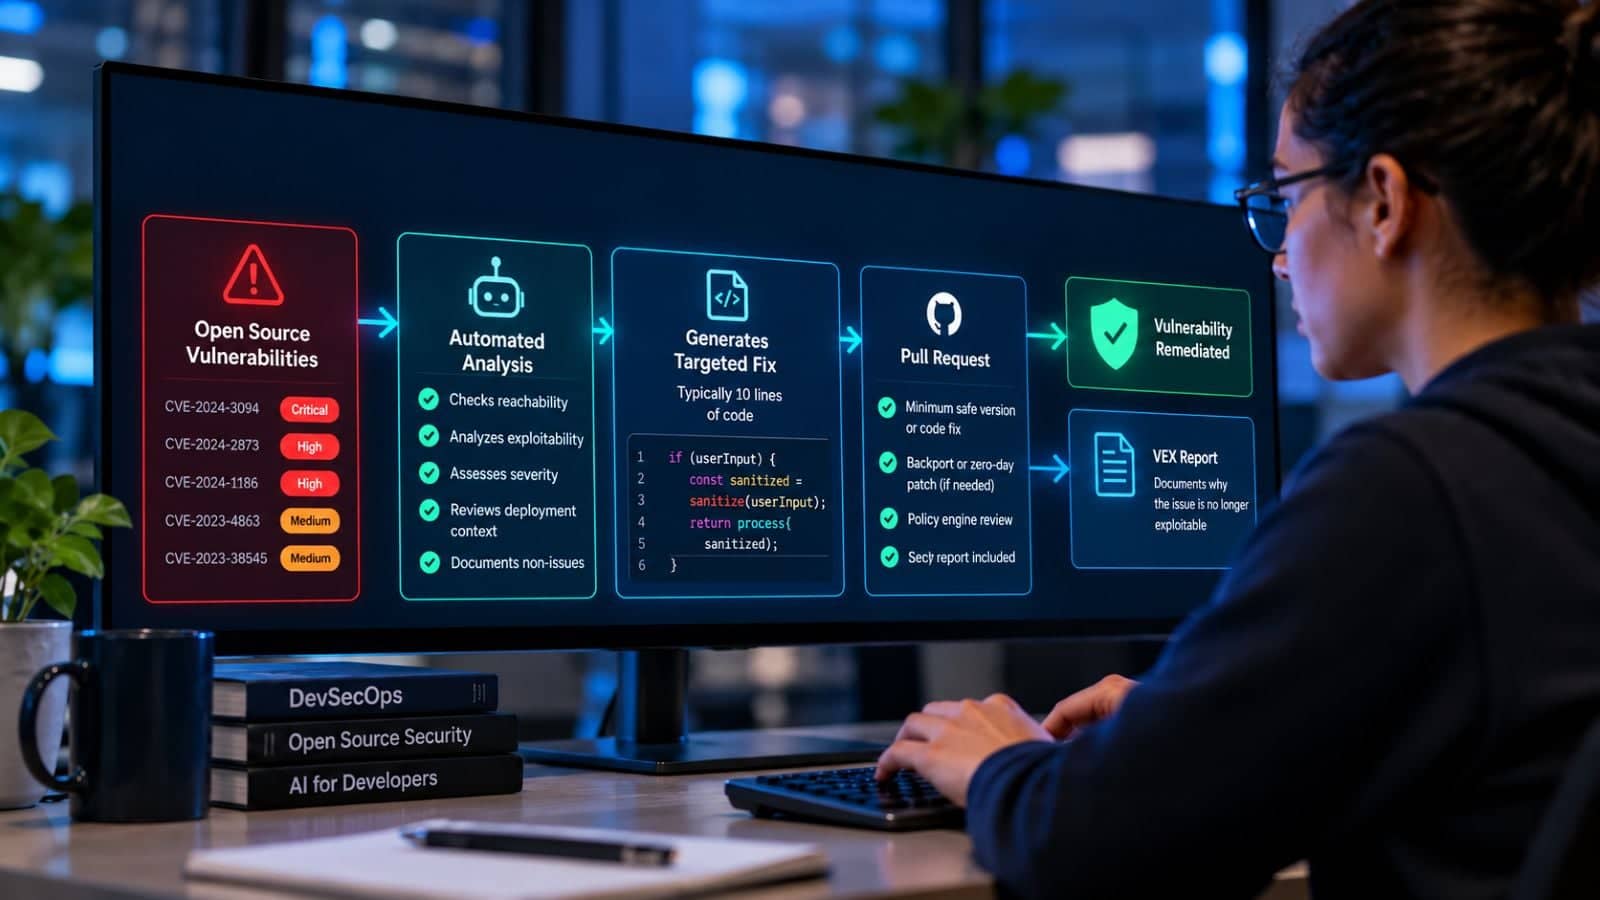
Endor Labs Adds AI Tool to Generate Fixes for Open Source Vulnerabilities
Endor Labs this week added an artificial intelligence (AI) tool to its portfolio that evaluates every reachable open source vulnerability against a code context graph to generate fixes that typically require only 10 lines of code to be generated and applied. Joe Harrington, a principal product manager for Endor Labs, said AURI Fix for Open […]
Why Continuous Vulnerability Management Belongs in Every DevSecOps Strategy
DevSecOps is part of the larger shift-left IT paradigm, which aims to identify and address vulnerabilities before they lead to security incidents. NIST’s guidance on secure software development emphasizes integrating security throughout the development lifecycle, rather than treating it as a separate concern addressed late in development or after deployment. By prioritizing a proactive approach […]
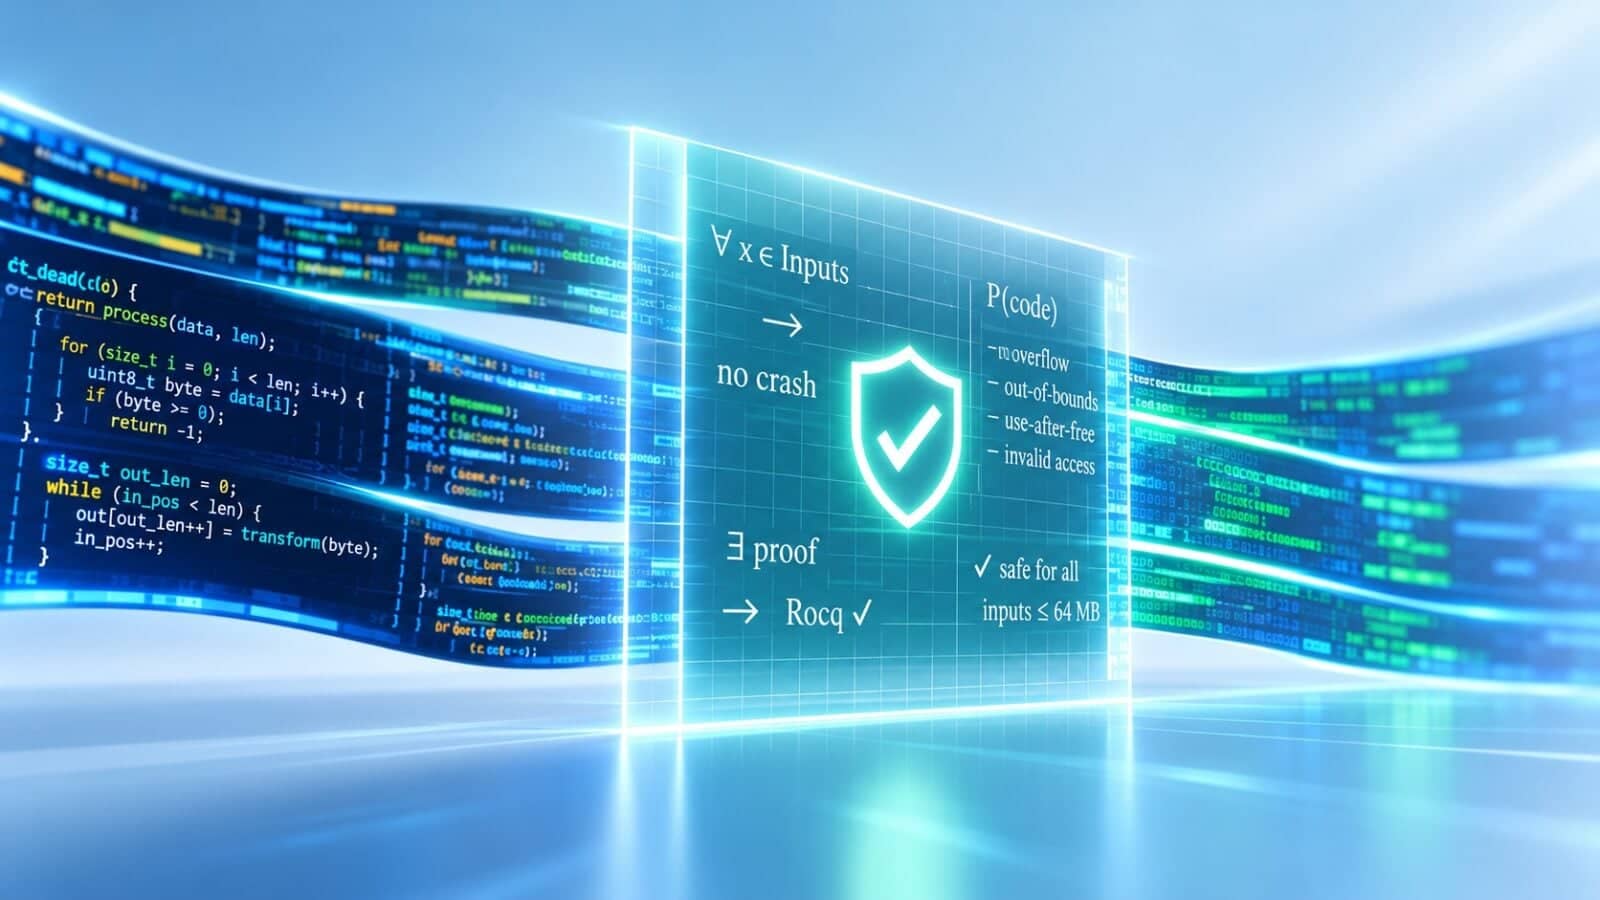
Claude Writes 180 Million Lines of Proofs to Verify 123 Open Source Libraries
Formal verification has long been the gold standard for software correctness. It has also been too expensive for almost everyone. New research from Anthropic suggests that’s changing. Anthropic’s Frontier Red Team, working with formal methods company Theorem, used Claude to prove security properties in the compiled code of 123 open-source libraries from Google’s OSS-Fuzz project. […]
When 200 OK Isn’t OK: Observability for LLM Systems
Traditional monitoring can show an LLM-powered application as healthy even when it delivers incorrect answers. Drawing on experience at Varo Bank, this article explains why AI observability must go beyond the four golden signals and how automated evaluation, groundedness checks and CI pipelines can catch silent failures before they reach customers.
Survey: AI Coding Tools Increase Open Source Software Dependencies
A survey of 307 enterprise technology leaders finds that as organizations rely more on artificial intelligence (AI) coding tools to build applications, they are simultaneously increasing the amount of open source software they are dependent on. Conducted by the market research firm Moving Horizon on behalf of ActiveState, a provider of a platform for accessing […]
Ten Great DevOps Job Opportunities
DevOps.com is now providing a weekly DevOps jobs report through which opportunities for DevOps professionals will be highlighted as part of an effort to better serve our audience. Our goal in these challenging economic times is to make it just that much easier for DevOps professionals to advance their careers. Of course, the pool of […]
Apple Brings Whole-Program C++ Hardening to Clang
Apple has added a new tool to the upstream LLVM project that could change how teams harden large C++ codebases. The clang-ssaf-driver, merged into LLVM Git this week, analyzes an entire project as it builds and then rewrites source code based on what it finds. The driver is part of Clang’s Scalable Static Analysis Framework […]
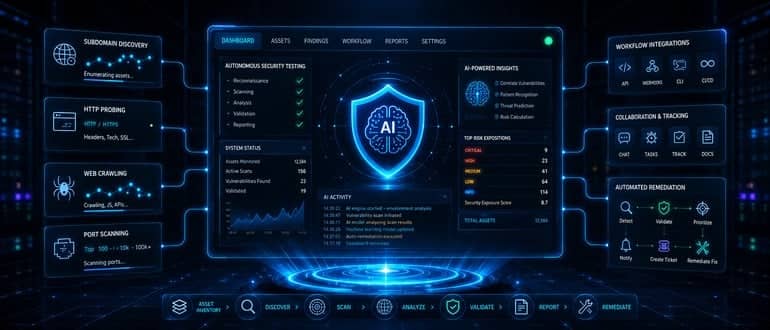
ProjectDiscovery Brings Open Source AI Testing to Vulnerability Discovery
ProjectDiscovery has made available an autonomous security testing platform that leverages an open source artificial intelligence (AI) testing framework to detect and validate vulnerabilities at a lower total cost. Company CEO Rishi Sharma said version 1.0 of the Neo platform is also available via a cloud service that makes it possible for DevSecOps teams to […]
LiteLLM Attack Affected 2,500 Companies, 434,000 CI/CD Pipelines: CloudSEK
The massive supply-chain attack that compromised LiteLLM in the spring affected more than 2,500 companies and exposed about 434,000 CI/CD pipelines, with victims ranging from top-tier IT and AI companies to cybersecurity firms, SaaS, and enterprises. It rolled up a lot of victims, but also was a high-profile example of the growing trend of threat […]
Open Source Code Just as Secure as Proprietary Software—If You Manage It Right, Says CISA
Open source can be just as safe as proprietary software, though government agencies (and private enterprises) should take additional measures to secure it properly, according to a new guide published by the U.S. Cybersecurity and Infrastructure Security Agency (CISA). The report, “Open Source Software: Security Principles and Practices,” provides with guidance to help agencies comply […]
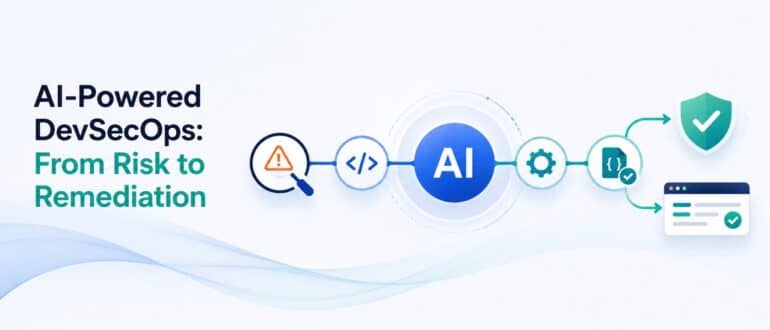
How AI is Revamping DevSecOps Processes
Artificial Intelligence is pushing DevSecOps into a new phase where security is no longer just about detecting vulnerabilities, but increasingly about resolving them automatically within the flow of software delivery. As many organizations are discovering, DevSecOps historically gave teams visibility into risk. AI is now turning that visibility into automated remediation. This evolution has taken […]
Platform Engineering vs. DevOps: Why This Is the Wrong Question
DevOps has done what it was supposed to do. It broke down the wall between development and operations, it made continuous delivery a normal expectation, it made shared ownership of production a cultural default, and it moved software delivery from a scheduled event to a continuous flow. The results reshaped how modern software gets built. […]
AI Is Exposing a Growing Blind Spot in Open Source Security
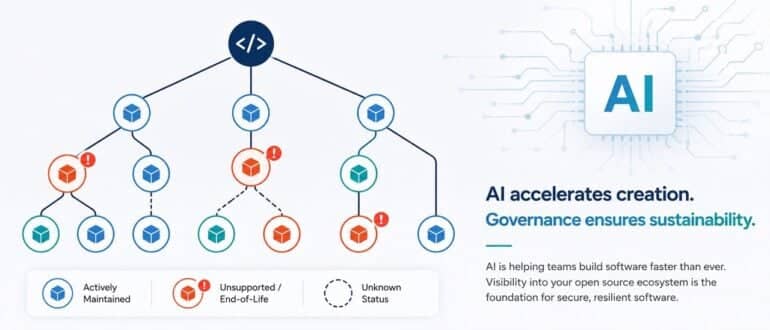
With AI, teams across organizations are now building internal applications faster than ever, often pulling in open source libraries and frameworks without much thought about long-term support, lifecycle management, or security ownership. An unintended consequence of this is that unsupported open source software (OSS) is quietly spreading across environments faster than security and engineering teams […]

Why Your Observability Stack Is Costing You More Than Your Cloud Bill
There’s a pattern playing out across engineering teams right now that nobody talks about openly: the tool meant to reduce operational complexity has quietly become one of the biggest line items on the infrastructure budget. Observability spending is out of control, and for most teams, it’s not because they’re monitoring too much. It’s because they’re […]
Why Your AI Agent is a Black Box and How to fix it With OpenTelemetry
You built the agent. It works in testing. Then it hits production and starts giving wrong answers, timing out or burning through your token budget, and you have no idea why. This is when developers discover that print statements and log files weren’t designed for this. LLM applications fail in ways that traditional tooling can’t see. A hallucination doesn’t throw […]
GitHub Breach Tied to Malicious VS Code Extension Exposes Thousands of Internal Repositories
GitHub says attackers accessed thousands of internal repositories after a company employee’s device was compromised through a malicious Visual Studio Code extension, though the company said it has removed the malicious extension, isolated the compromised endpoint, and launched an investigation. The company confirmed that approximately 3,800 internal repositories were affected. GitHub stated that investigators have […]
OpenSSF’s CRob: ‘The Runway Is Rapidly Running Out’ on EU CRA Readiness
The EU’s Cyber Resilience Act kicks into high gear this September, and companies are still clueless about how they must obey its strictures. MINNEAPOLIS — At Open Source Summit North America, Christopher “CRob” Robinson, Chief Security Architect for the Open Source Software Foundation (OpenSSF), spoke about the European Union’s (EU) Cyber Resilience Act (CRA). CRob […]
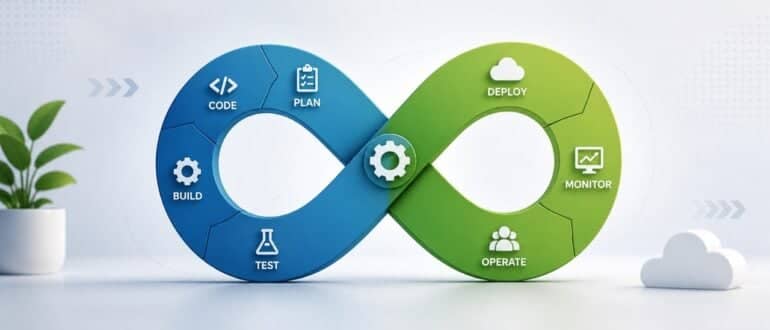
Why DevOps Is Critical for Modern Business Resilience
Today’s business world operates in a state of constant change. What the customer wants to buy changes quickly, new competitors appear overnight, and cyber threats are changing faster than ever. In this world, the concept of “resilience,” the ability to adapt, to overcome, and to continue to create value for the enterprise despite the changes, […]
Migration Observability: Measure Meaning, Not Movement
Traditional operational observability focuses on latency, errors, throughput and saturation. Migration observability needs a different category: Semantic drift.