

Harmonizing AI-Driven DevOps: Building Secure, Self-Healing Pipelines With AWS Bedrock and SageMaker
The combination of SageMaker and Bedrock enables DevOps teams to develop secure self-healing pipelines through AI harmonization, which transforms software delivery processes.
ArmorCode Makes Anya AI Agent Generally Available
ArmorCode at the 2025 RSA Conference this week made generally available Anya, an artificial intelligence (AI) agent added to its application security posture management (ASPM) platform that has specifically been trained to augment DevSecOps teams.
Lineaje Leverages AI Agents to Secure Open Source Packages and Images
Lineaje has added artificial intelligence (AI) agents that leverage multiple types of code scanners to ensure the open-source software packages and artifacts being used by application developers are truly secure.
Cycode Adds AI Agent Teammates to Secure Software Supply Chains
Cycode, this week, added multiple artificial intelligence (AI) agents to its application security posture management (ASPM) capable of monitoring code and offering remediation suggestions. In addition, the company is adding an ability to, in real-time, monitor continuous integration processes running in memory. That capability makes it possible to thwart, for example, recent attacks that exploited […]
Endor Labs Adds AI Agents to Automate Application Security Reviews
Endor Labs today added a set of artificial intelligence (AI) agents to its platform, specifically trained to identify security defects in applications and suggest remediations. Fresh off raising an additional $93 million in funding, Endor Labs founder and CEO Varun Badhwar said going beyond simply identifying vulnerabilities in code, these AI agents are trained to […]
Veracode Extends Scope and Reach of DevSecOps Portfolio
Veracode today updated its risk management tool to provide integration with Kubernetes runtime environments, increased integration with code repositories to make it simpler to identify the origin of vulnerabilities and, available shortly, an ability to add tags and classifications to help streamline remediation efforts.
AI-Generated Code Packages Can Lead to ‘Slopsquatting’ Threat
AI hallucinations – the occasional tendency of large language models to respond to prompts with incorrect, inaccurate or made-up answers – have been an ongoing concern as the enterprise adoption of generative AI has accelerated over the past two years. They’re also an issue for developers using AI-based tools when building code, including generating names of packages […]
Report: Commercial Software Just as Vulnerable as Open Source
An analysis published by ReversingLabs, a provider of tools for securing application development environments, suggests that commercial software used in software supply chains is just as vulnerable as open-source code.
Report: Bulk of Application Vulnerabilities Don’t Require Immediate Attention
An analysis of more than 101 million application security alerts conducted by OX Security, a provider of an application security posture management (ASPM) platform, finds only 2% to 5% require immediate action, with more than 95% considered informational.
Demystifying Code-to-Cloud Security
Code-to-cloud security is considered the future of application security, as it helps lower expenses, prevents data breaches and ensures compliance infringement, thereby protecting an organization’s reputation.
Securing the Future: DevSecOps in the Age of Artificial Intelligence
Why DevSecOps is a critical discipline in the AI era, the benefits and challenges of integrating AI into DevSecOps pipelines and why it provides a framework for successfully adopting these emerging technologies.
The DevOps Bottleneck: Why IaC Orchestration is the Missing Piece
If you work in DevOps, you’ve heard it a thousand times: “Do more with less.” More automation, more security, more reliability—but with the same (or fewer) people. Meanwhile, your development teams keep growing, pushing out new features at breakneck speed. Yet somehow, the infrastructure team is supposed to scale magically to keep up. Let’s be […]
JFrog Survey Surfaces Limited DevSecOps Gains
A global survey of 1,402 application developers, cybersecurity and IT operations professionals finds 71% work for organizations that, despite any potential vulnerabilities, still allow developers to download packages directly from the internet.
Pulumi Extends Security Reach to Include Managing Secrets and Policy-as-Code
Pulumi today extended the reach of its Environments, Secrets and Configurations (ESC) platform for managing infrastructure-as-code (IaC) into the realm of DevSecOps by adding the ability to manage secrets and implement policies.
GitHub Action Compromise Risks Data Leaks for 23,000 Repositories
The attacker introduced malicious Python code that would expose secrets like authentication credentials in public repositories.
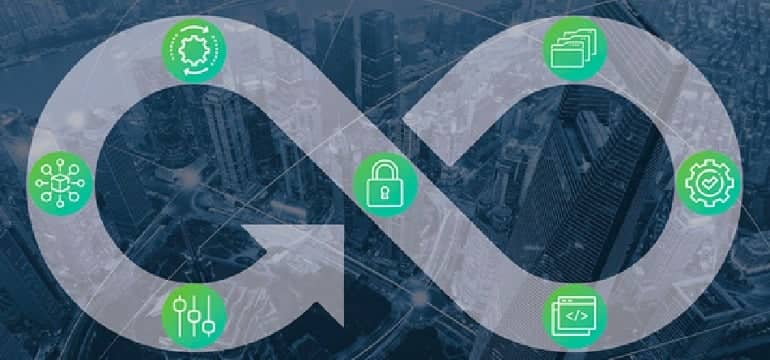
Bridging the Dev and SecOps Gap: How Intelligent Continuous Security Enables True End-to-End Security
Intelligent Continuous Security (TM) (ICS) is the next evolution — harnessing AI-driven automation, real-time threat detection and continuous compliance enforcement to eliminate these inefficiencies. ICS extends beyond DevSecOps to also close security gaps with SecOps, ensuring end-to-end continuous security across the entire software lifecycle.
Sonar Combines SAST and SCA Tools in Single Offer
Sonar today revealed it will at the end of May add an offering that combines its Static Application Security Testing (SAST) tool with the software composition analysis (SCA) tools it gained with the acquisition of Tidelift late last year.
DeepSource Open Sources Globstar Alternative to Semgrep to Analyze Code
DeepSource has made available an open source static code analysis tool, dubbed Globstar, that DevSecOps teams can employ to embed code checkers in their pipelines.
Legit Security Extends ASPM Platform to Provide More Vulnerability Context
Legit Security this week added an ability to determine the level of risk a vulnerability actually represents to its application security posture management (ASPM) platform.
Teleport Unifies Infrastructure and Application Workload Security
Teleport today added an offering that makes it simpler to declaratively secure IT infrastructure and workloads using short-lived X.509 certificates.
Why Has DevSecOps Failed?
DevSecOps is failing because we underestimated the complexity of cultural transformation and the importance of human-centered tools.
North Korea’s Lazarus Group Targets Developers, Supply Chain
North Korea’s notorious Lazarus Group is using an advanced malicious implant to target cryptocurrency wallets and spreading it via legitimate GitHub profile and possibly through npm packages. The ongoing campaign, dubbed Operation Marstech Mayhem, is the example of a threat group using open-source code repositories like GitHub, npm, and Python Package Index (PyPI) in software supply […]
Open Source Software Security Concerns with Spike Curtis
Spike Curtis, principal engineer for Coder Technologies, dives into why open source software security concerns are valid, and why the only viable option is to invest more in securing software supply chains to mitigate potential threats. While open source benefits from community oversight, organizations must vet the projects they rely on to avoid security gaps. […]