
Tag: application security
Docker Introduces Open Sandbox Kit Spec for AI Agent Permissions
AI agents are getting good at probing the boundaries developers put around them. Their ability to improvise makes them hard to contain. “You ask for something in a very high-level, vague-at-best way ...
GitHub’s Security Autofix Agent Now Remembers What It Fixed
 Tom Smith | | agentic autofix, AI coding agents, AI security, application security, code scanning, CodeQL, Copilot Memory, devsecops, github, GitHub Advanced Security, GitHub Copilot, repository memory, secure coding, vulnerability remediation
GitHub’s agentic autofix now uses Copilot Memory to reuse repository-specific security fix patterns, helping Copilot apply lessons from past vulnerabilities across future alerts, reviews and coding workflows ...
Leaked GitLab Email Tokens Can Reach Code, Secrets and CI/CD Pipelines
 Jaime Hampton | | Aikido Security, application security, CI/CD, devsecops, gitlab, Software Supply Chain
Security researchers have uncovered a GitLab behavior that could let attackers use a leaked project email address to push code, trigger CI/CD jobs and reach other repositories accessible to the address owner ...
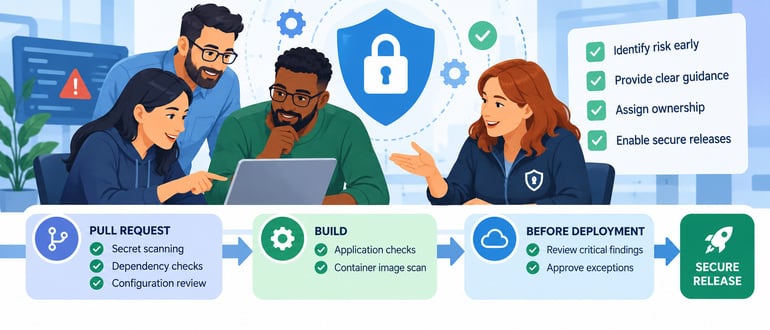
DevSecOps Teams as Partners in Secure Software Delivery
 Manish Shetty | | application security, CI/CD, CI/CD security, dependency security, devops security, devsecops, risk management, secure software development, security automation, Security Guardrails, shift left security, software security, Software Supply Chain, vulnerability management
DevSecOps teams can reduce last-minute release delays by shifting security decisions earlier, improving guardrails, clarifying ownership and making findings actionable ...
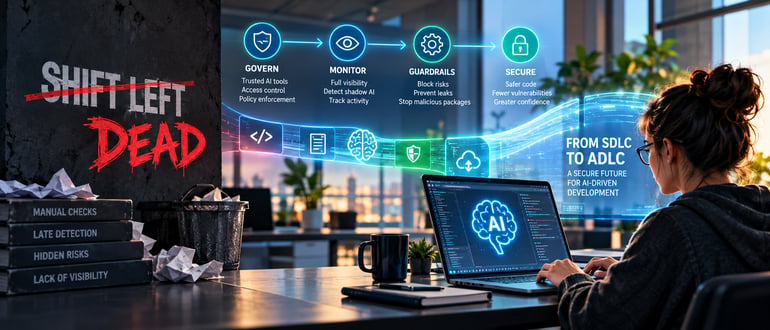
Why Shift Left is Dead
 Devin Maguire | | ADLC, agentic development lifecycle, AI Governance, AI guardrails, AI security, AI-Driven Development, AI-generated code, application security, Developer Security, devsecops, prompts, sdlc, secure software development, shadow ai, shift left security, Software Supply Chain Security
AI-driven development is exposing risks before code is written, forcing security teams to move beyond shift-left and govern agents, prompts, tools and data across the entire development lifecycle ...
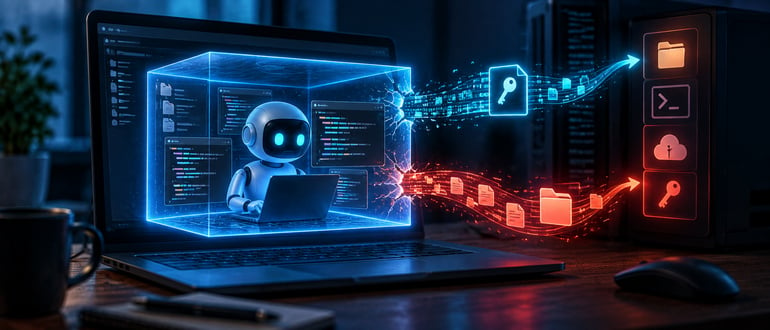
Codex Sandbox Escapes Show Why Agent Guardrails Can’t Live Inside the Agent
Tom Smith | | agentic AI, AI coding agents, AI security, application security, Codex CLI, Codex Desktop, Codex Security, coding agent security, Developer Security, devsecops, Heapjack, OpenAI Codex, Overpatch, sandbox escape, sandbox security, Software Supply ChainTwo patched OpenAI Codex vulnerabilities, Heapjack and Overpatch, exposed how coding agents can escape sandboxes and reach developer systems without approval prompts ...
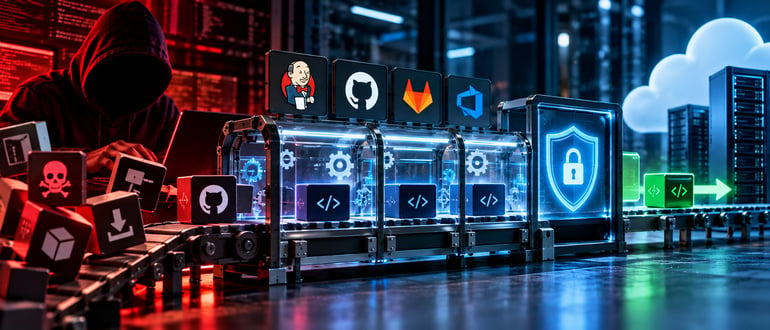
Why Your CI/CD Pipeline Is Your Most Unprotected Attack Surface
 Muhammad Yawar Malik | | application security, build agents, build pipelines, CI/CD security, Cloud Security, credential security, dependency security, deployment security, devops security, devsecops, ephemeral runners, GitHub Actions, infrastructure security, Jenkins security, least-privilege, pipeline security, provenance attestation, secrets management, secure pipelines, secure software development, software provenance, Software Supply Chain, supply chain attacks, third-party actions, XZ Utils
CI/CD pipelines often hold privileged credentials, execute third-party code and connect directly to production, making pipeline security one of the most overlooked risks in modern DevOps ...
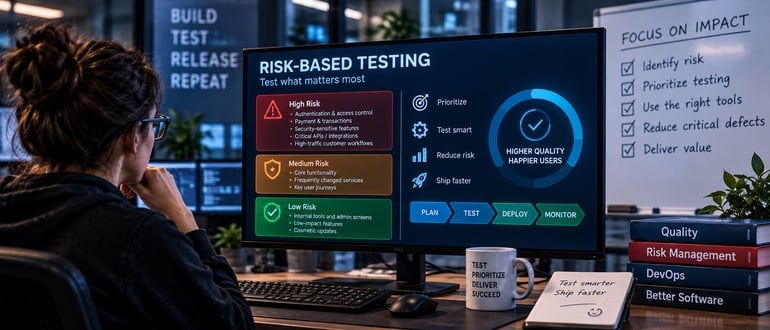
Stop Chasing 100% Test Coverage: Why DevOps Teams Need to Test Smarter, Not More
 Adonis Celestine | | AI testing, application security, CI/CD, continuous testing, devops, PRisMA, Product Risk Management, QA, QFD, Quality Assurance, Quality Functional Deployment, Rapid Risk Assessment, regression testing, release management, risk-based testing, RRA, software development, software quality, software testing, test automation
Every software team eventually runs into the same question: How much testing is enough? For years, the default answer has been "more." More automated tests. More regression suites. More environments. More devices ...

GitHub Widens the Door on Advanced Security Trials
Tom Smith | | AI coding, application security, CodeQL, Developer Security, devsecops, exposed credentials, GHAS, GitHub Advanced Security, GitHub Code Security, GitHub Enterprise Cloud, GitHub Secret Protection, GitHub security, mid-market security, Repository Security, secret scanning, secure software development, Software Supply Chain Security, vulnerability scanningGitHub raised its self-serve Advanced Security trial cap from 100 to 300 licenses, letting more mid-size Enterprise Cloud orgs test for free ...

Why AI Agents Shouldn’t Guess at Vulnerability Exploitability
 Harish Gaggar | | AI agents, application security, SBoM, Software Supply Chain, vulnerability management, vulnerability prioritization
Vulnerability prioritization is not a language problem. The safest agent architectures use models to interpret and explain, while deterministic systems traverse the evidence. Ask a security team a simple question: Of the ...
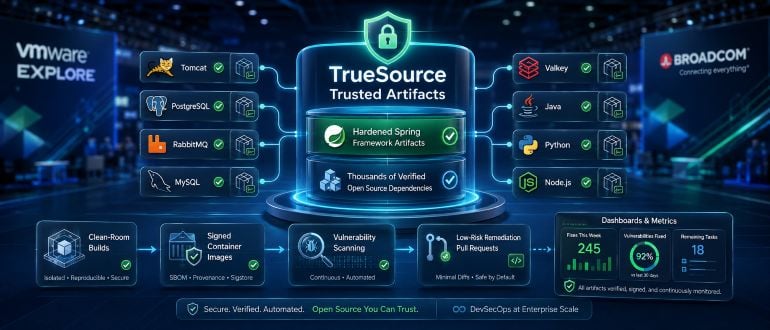
Broadcom Launches TrueSource Service to Secure Spring Framework
 Mike Vizard | | AI coding, Apache Tomcat, application security, Bitnami Secure Images, Broadcom, container security, dependency security, devsecops, java, kubernetes, node.js, open source security, open source vulnerabilities, patch management, Python, SBoM, secure software development, software artifacts, Software Supply Chain Security, Spring framework, Spring Security, Tanzu, TrueSource Trusted Artifacts, VMware explore, vulnerability management
Broadcom launches TrueSource Trusted Artifacts to provide hardened Spring dependencies, secure open source packages and automated vulnerability remediation ...
Report Shines Spotlight on 91 Vulnerabilities Fixed in Latest Update to Spring Framework
Mike Vizard | | AI cybersecurity, AI vulnerabilities, application security, Broadcom, CVEs, devsecops, Java security, open source security, open source vulnerabilities, patch management, security automation, software components, Software Supply Chain, sonatype, Spring framework, Spring vulnerabilities, technical debt, virtual patching, vulnerability managementSonatype says 91 Spring vulnerabilities affecting more than 209,000 software components highlight how AI is accelerating vulnerability discovery and creating a new patching challenge for DevSecOps teams ...

