Tag: Developer Security
GitHub Gives Enterprises a Full Count of Who Holds the Keys
 Tom Smith | | access management, agentic AI, AI coding agents, credential inventory, credential security, Developer Security, devsecops, github, GitHub Apps, GitHub Enterprise Cloud, identity security, least-privilege, OAuth tokens, PATs, Personal Access Tokens, secrets management, security operations, Software Supply Chain Security, SSH keys
GitHub Enterprise Cloud now lets organizations export a full inventory of credentials, helping security teams identify stale, overprivileged and forgotten access across users, apps and automation ...
Cycode Extends DevSecOps Reach to Software Packages Developers Download
 Mike Vizard | | ADLC, agentic development lifecycle, AI coding agents, cool down period, Cycode, dependency security, Developer Security, devsecops, malicious packages, package security, software repositories, Software Supply Chain Security, supply chain attacks, threat intelligence, workstation protection
Cycode is adding workstation-level protection to stop developers and AI coding agents from downloading malicious or insufficiently vetted software packages ...
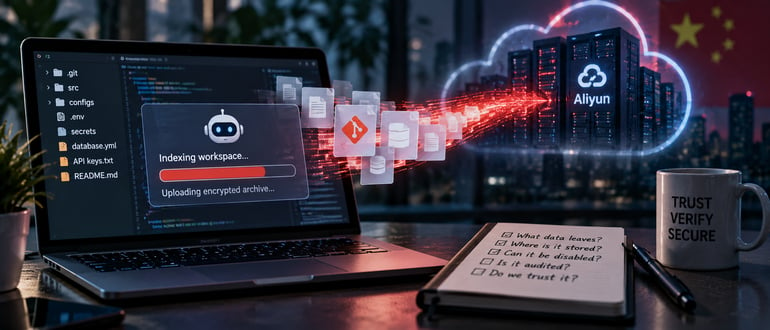
Your AI Coding Assistant Has the Keys to the Repo. Z.ai Just Showed Why That Matters
Tom Smith | | AI coding assistants, AI Governance, AI security, Cloud Security, code security, Data Exfiltration, data privacy, Developer Security, developer tools, devsecops, egress monitoring, secrets management, shadow ai, Software Supply Chain, source code security, Z.ai, ZCode, Zhipu AIZCode’s default-on indexing feature reportedly uploaded entire developer workspaces to cloud storage, highlighting why AI coding assistants should be treated as privileged software and closely monitored ...
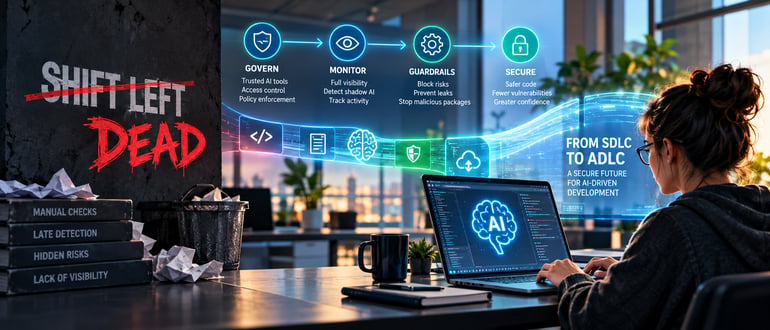
Why Shift Left is Dead
 Devin Maguire | | ADLC, agentic development lifecycle, AI Governance, AI guardrails, AI security, AI-Driven Development, AI-generated code, application security, Developer Security, devsecops, prompts, sdlc, secure software development, shadow ai, shift left security, Software Supply Chain Security
AI-driven development is exposing risks before code is written, forcing security teams to move beyond shift-left and govern agents, prompts, tools and data across the entire development lifecycle ...
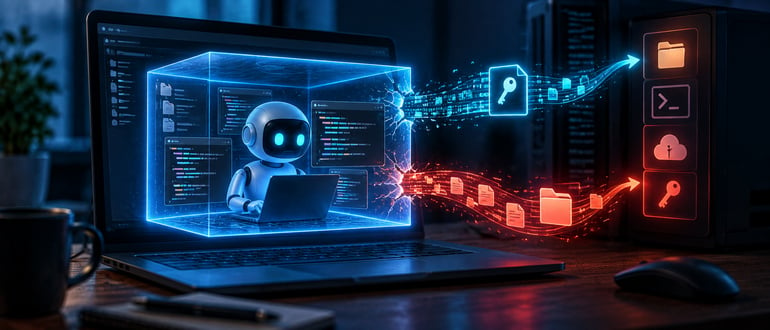
Codex Sandbox Escapes Show Why Agent Guardrails Can’t Live Inside the Agent
Tom Smith | | agentic AI, AI coding agents, AI security, application security, Codex CLI, Codex Desktop, Codex Security, coding agent security, Developer Security, devsecops, Heapjack, OpenAI Codex, Overpatch, sandbox escape, sandbox security, Software Supply ChainTwo patched OpenAI Codex vulnerabilities, Heapjack and Overpatch, exposed how coding agents can escape sandboxes and reach developer systems without approval prompts ...

GitHub Widens the Door on Advanced Security Trials
Tom Smith | | AI coding, application security, CodeQL, Developer Security, devsecops, exposed credentials, GHAS, GitHub Advanced Security, GitHub Code Security, GitHub Enterprise Cloud, GitHub Secret Protection, GitHub security, mid-market security, Repository Security, secret scanning, secure software development, Software Supply Chain Security, vulnerability scanningGitHub raised its self-serve Advanced Security trial cap from 100 to 300 licenses, letting more mid-size Enterprise Cloud orgs test for free ...
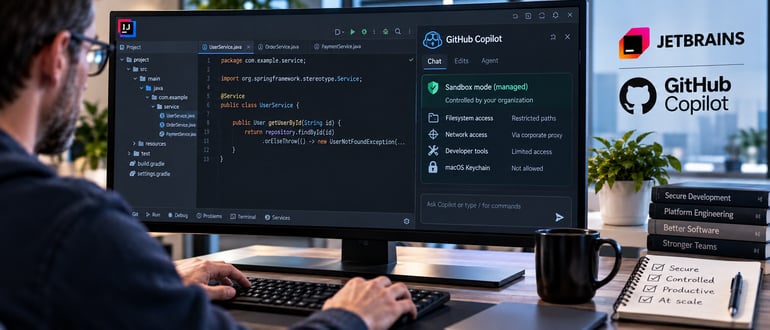
GitHub Puts Guardrails on Copilot’s Sandbox Inside JetBrains IDEs
Tom Smith | | AI agents, AI coding agents, AI Governance, Copilot sandbox, Developer Security, developer tools, Enterprise AI, filesystem controls, GitHub Copilot, GitHub Copilot JetBrains, IDE security, JetBrains, managed policies, MCP governance, network controls, OpenTelemetry, platform engineering, sandbox security, software developmentJetBrains IDEs are where a lot of enterprise backend work happens — Java, Kotlin, Spring, big monorepos with a lot to break. So when an AI coding agent starts running shell commands ...

Are LLMs Equally Good (or Bad) at Building Secure Software?
 Pieter Danhieux | | agentic AI, AI agents, AI code security, AI coding assistants, AI coding costs, AI coding models, AI Development, AI model benchmarking, AI-generated code, application security, Developer Security, framework security, LLM security, OWASP Top 10, SAST, secure code generation, secure coding, software development, software security, token costs
An SCW study finds a large variance in how frontier and budget LLMs perform across different frameworks, and explains the striking cost variance ...

Signed, Attested, and Malicious: The Software Supply Chain Has a Deepfake Problem
 Nigel Douglas | | AI coding agents, AntV packages, behavioural analysis, continuous scanning, dependency security, Developer Security, GitHub Actions compromise, malicious packages, Miasma worm, Mini Shai-Hulud, npm malware, OIDC tokens, open source security, package provenance, package quarantine, policy as code, Red Hat npm attack, registry scanning, Shai-Hulud worm, SLSA provenance, software attestation, Software Supply Chain Security, TanStack compromise, trusted pipeline attacks
A developer pulls a package from a reliable repo. It is signed, has provenance, and has been scanned. And then…it contains malware. That is no longer hypothetical. When the Miasma worm tore ...
Why Developer Workstations Have Become a Critical Part of the Software Supply Chain
 Samuel Ogbonna | | CI/CD security, Developer Security, Developer Workstations, devsecops, open source security, Software Supply Chain
For years, software supply-chain security discussions focused on centralized infrastructure such as build servers, package registries, and CI/CD systems. Recent attacks suggest that this view is incomplete. The Megalodon campaign injected malicious ...

Mozilla Shows the Danger of Indirect Prompt Injections in AI Coding Agents
 Jeff Burt | | AI coding agents, AI security risks, Anthropic Claude Code, Developer Security, exposed credentials, exposed secrets, Futurum Group, indirect prompt injection, leaked API keys, Mozilla 0DIN, shell scripts
A clean GitHub repository that contains no malicious code can launch an attack and fully compromise a developer’s systems by using indirect prompt injections to trick AI-powered coding agents like Anthropic’s Claude ...

Shift Left to the Developer’s Machine: Building Local Git Security Gates
 Arun Sanna | | CI/CD security, code security, Credential Leakage, Defense in Depth, developer experience, Developer Security, devsecops, Git Hooks, Git Security, GitLeaks, Open Source Security Tools, Pre-Commit Hooks, secret detection, secrets management, shift left security, Software Supply Chain, static analysis, supply chain security, vulnerability scanning
Shift left to the developer's machine. The principle is what matters: Stop secrets before they ship. The tooling is a means to that end. ...
