
Tag: Kubernetes security
Why Old Azure DevOps Releases Survive a Pipeline Cutover
 Ahmed Tariq | | Azure DevOps, Azure DevOps Classic, Azure pipelines, CI/CD, container security, deployment automation, devops, devsecops, Helm, kubernetes, Kubernetes security, Pipeline Migration, release management, Release Pipelines, software delivery
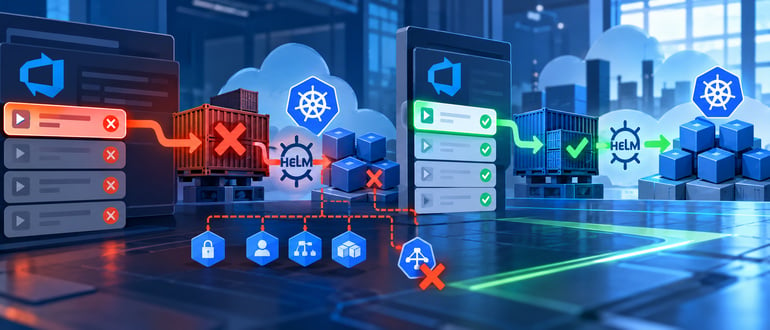
Old Azure DevOps Classic releases can retain retired deployment tasks, Helm names, image paths and variables long after a pipeline cutover, leaving stale redeploy paths active ...
AI Can Generate Your Infrastructure. Can Your CI/CD Pipeline Trust It?
 Oreoluwa Omoike | | AI code vulnerabilities, AI coding assistants, AI-generated code, AI-generated infrastructure, Checkov, CI/CD security, Conftest, devsecops, IaC security, infrastructure as code, infrastructure security, Kubernetes security, OPA, platform engineering, policy as code, provenance tracking, secret scanning, secure CI/CD, Terraform security, tfsec, Trivy, TruffleHog
AI-generated infrastructure code is exposing a growing security gap, pushing platform teams to add stronger automated gates, provenance tracking and human review before Terraform, Kubernetes and CI/CD changes reach production ...
Why Cryptographic Inventory Is the First Step Toward Quantum Readiness
 Michael Carter | | CBOM, CI/CD security, crypto-agility, cryptographic dependencies, cryptographic discovery, cryptographic inventory, cryptography bill of materials, devops security, devsecops, Kubernetes security, ML-KEM, NIST PQC migration, post-quantum cryptography, PQC, quantum readiness, Software Supply Chain Security
Post-quantum readiness starts with visibility. DevOps teams need a continuous cryptographic inventory to map algorithms, keys, certificates, libraries, infrastructure and third-party dependencies before PQC migration begins ...
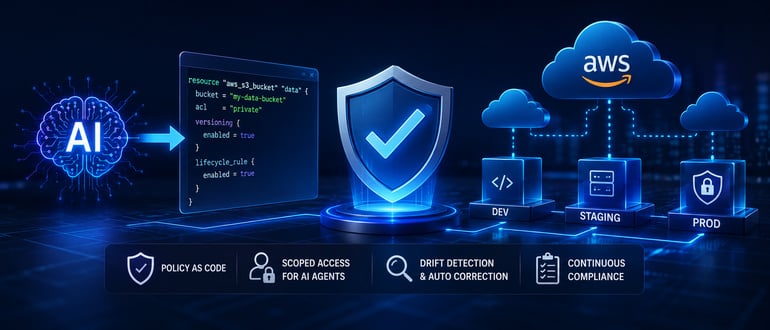
AI Agents Are Writing Your Infrastructure Code. Is Anyone Governing It?
 Neel Shah | | agentic infrastructure, AI agent governance, AI coding assistants, AI-generated infrastructure, cloud misconfiguration, cloud security automation, continuous drift detection, devops security, IAM misconfiguration, infrastructure as code security, infrastructure compliance, infrastructure guardrails, Kubernetes security, platform engineering security, policy as code, RBAC for AI agents, secure-by-default platforms, SRE governance, StackGen Aiden, Terraform security
AI agents now generate infrastructure code at scale, but security pass rates are stuck at 55%. Here’s how teams can close the governance gap ...
Build vs. Buy: What it Really Takes to Harden Your Software Supply Chain
 Matt Moore | | CI/CD security, container registry security, container vulnerabilities, devsecops, hardened images, Kubernetes security, secure build pipelines, Software Supply Chain Security
When it comes to securing the software supply chain, engineering teams often assume that the choice between building their own hardened images or buying a solution is straightforward…until they try to build the ...
Minimus Adds VEX Support to Managed Hardened Images Service

Minimus has extended its managed service for providing application developers with hardened images to include support for the Vulnerability Exploittability eXchange (VEX) format used to share data across multiple application security tools ...
