

Tessl Adds Reusable Loops to AI Software Factory Platform
Tessl this week revealed it has added ready-to-use loops that DevOps teams can now invoke and customize to drive agentic engineering workflows. Speaking at the company’s AI DevCon event, Tessl CEO Guy Podjarny told conference attendees that the company is moving to make it simpler to combine AI skills and self-optimizing loops to create a […]
PagerDuty Launches Autonomous SRE Agent Paige to Combat AI-Driven Outages
Facing an unprecedented wave of software failures driven by artificial intelligence (AI), cloud computing provider PagerDuty Inc. on Tuesday unveiled Paige, an autonomous Site Reliability Engineering (SRE) agent designed to diagnose and repair technical disruptions alongside human engineers. The announcement comes as enterprises confront a structural shift in enterprise IT. Software is increasingly written, tested, […]
Your Coding Agent Needs Production Discipline
I see engineers handing work to coding agents every day. Consider a straightforward assignment: Add an endpoint to an internal service, run the tests, and open a pull request. The agent may work for an hour before the engineer looks at it again, freeing that engineer to focus on another problem. Let’s follow that assignment […]
Malicious Claude Code Extension Affects Up to 5,000 Cursor Users
Cursor has disclosed a security incident involving malicious versions of Anthropic’s Claude Code extension that attempted to install a persistent backdoor on developers’ computers. The company initially estimated that up to 5,000 users could have been affected, highlighting the security risks associated with compromised software development tools. The compromised extension packages, identified as Anthropic.claude-code versions […]
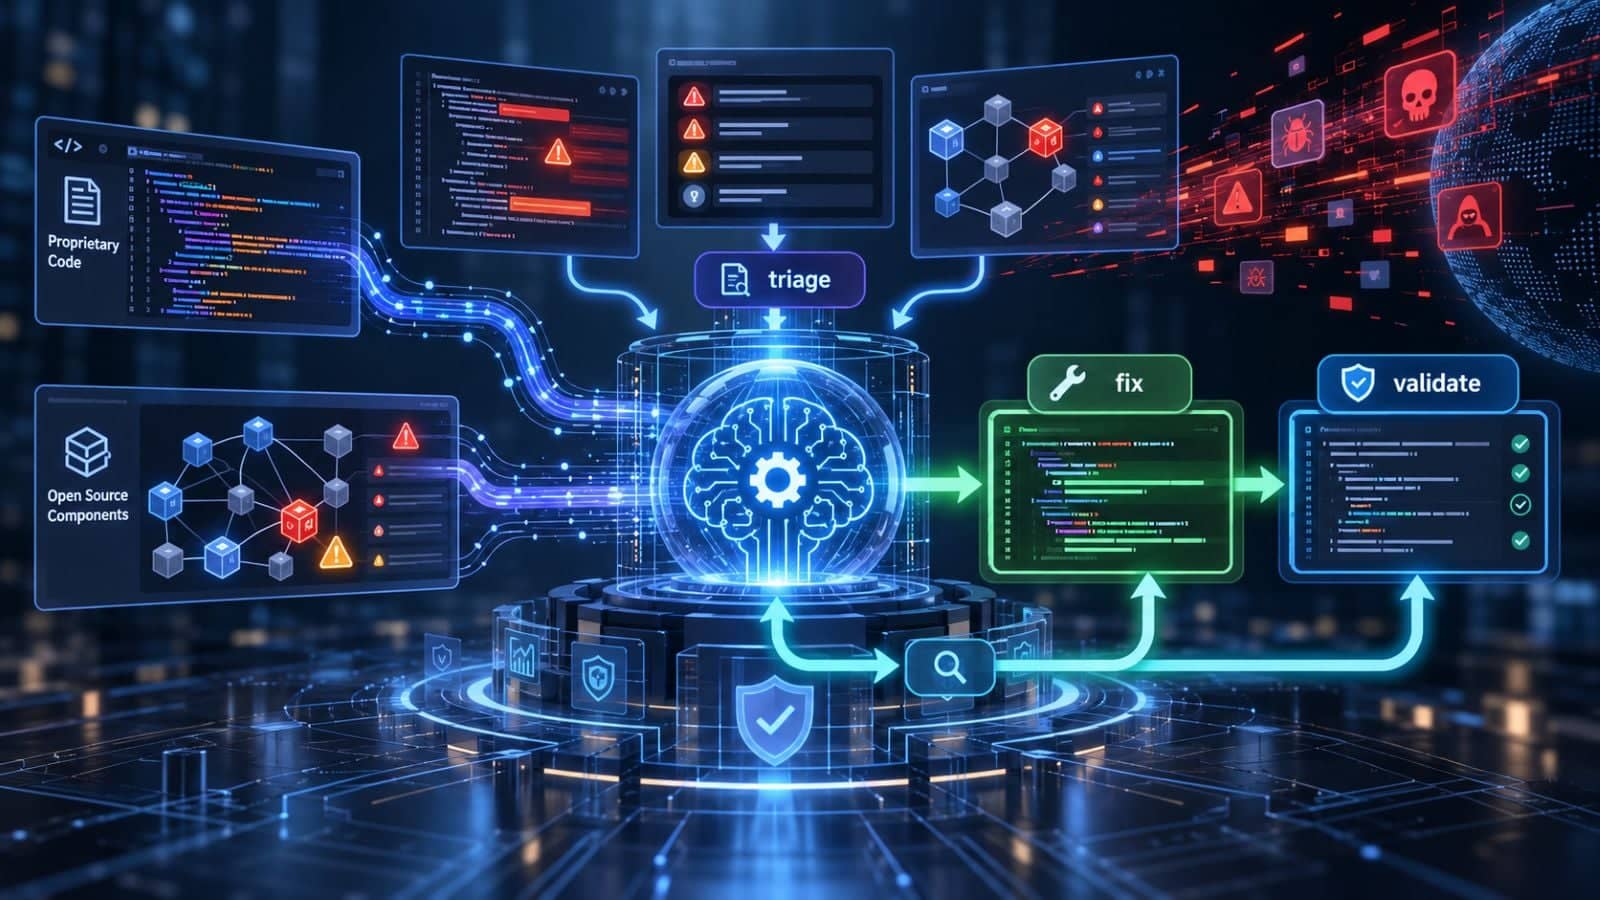
Black Duck Adds AI Agent to Triage and Fix Vulnerabilities
Black Duck this week added an artificial intelligence (AI) agent to its portfolio that triages vulnerabilities and then generates and validates fixes for DevSecOps teams to review before applying them. Patrick Carey, vice president of product marketing for Black Duck, said the Signal Agentic Fix agent leverages the company’s static application security testing (SAST) and […]
AI Made Building Apps Easy, but Who Really Runs Them?
A few months ago, a product manager at an agency reached out to us. They had built a client reporting app over a weekend using an AI coding tool and made it live so customers could try it. It worked great until we found that authentication was broken and the app’s admin interface was accessible […]
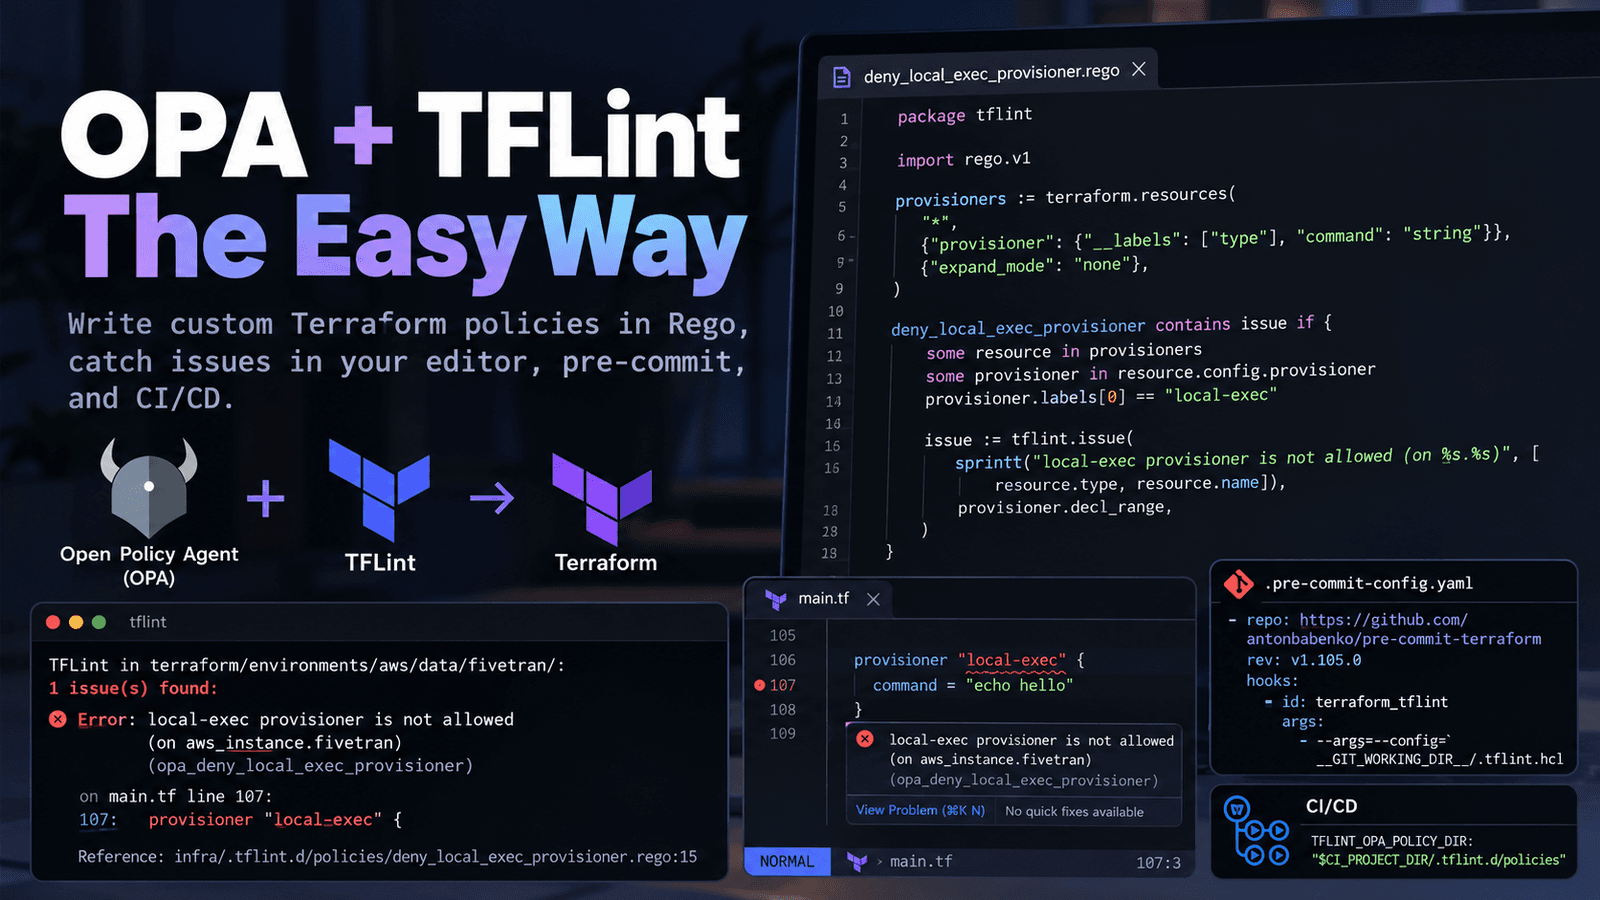
Implementing OPA with Terraform the Easy Way
Terraform compliance doesn’t have to mean complicated policy pipelines. By combining TFLint with OPA and Rego, developers can enforce infrastructure guardrails directly in their editors, pre-commit hooks and CI/CD workflows, catching violations before deployment.
Report: AI Agents Increase Observability Costs
Cisco has released its Splunk State of Observability 2026 report, revealing that companies face growing costs and operational challenges as they deploy AI agents without sufficient monitoring capabilities. The report found that 57% of organizations spend more on telemetry, the data used to monitor IT systems, than on the infrastructure being monitored. Additionally, 55% of […]
How Dependency Mocking Affects CI/CD Pipeline Reliability
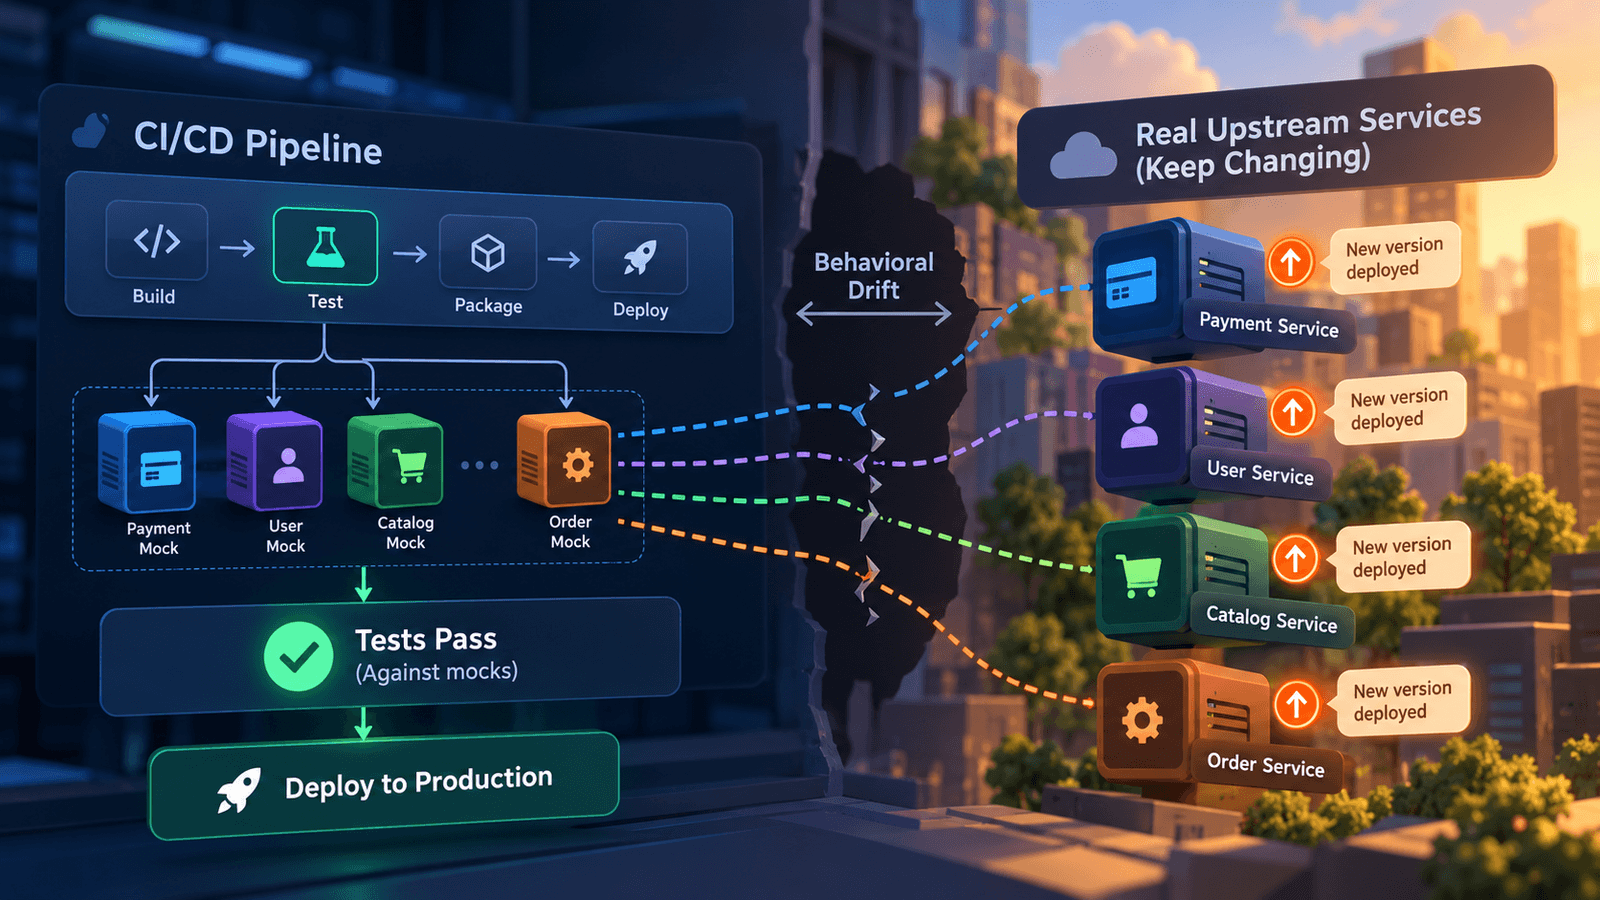
Stale dependency mocks can make CI/CD pipelines pass while production integrations fail. Learn how mock drift undermines reliability and how to prevent it.
Survey: AI Coding Tools Increase Open Source Software Dependencies
A survey of 307 enterprise technology leaders finds that as organizations rely more on artificial intelligence (AI) coding tools to build applications, they are simultaneously increasing the amount of open source software they are dependent on. Conducted by the market research firm Moving Horizon on behalf of ActiveState, a provider of a platform for accessing […]
Blitzy Adds Chat-to-Prompt Interface to Agentic AI Engineering Platform
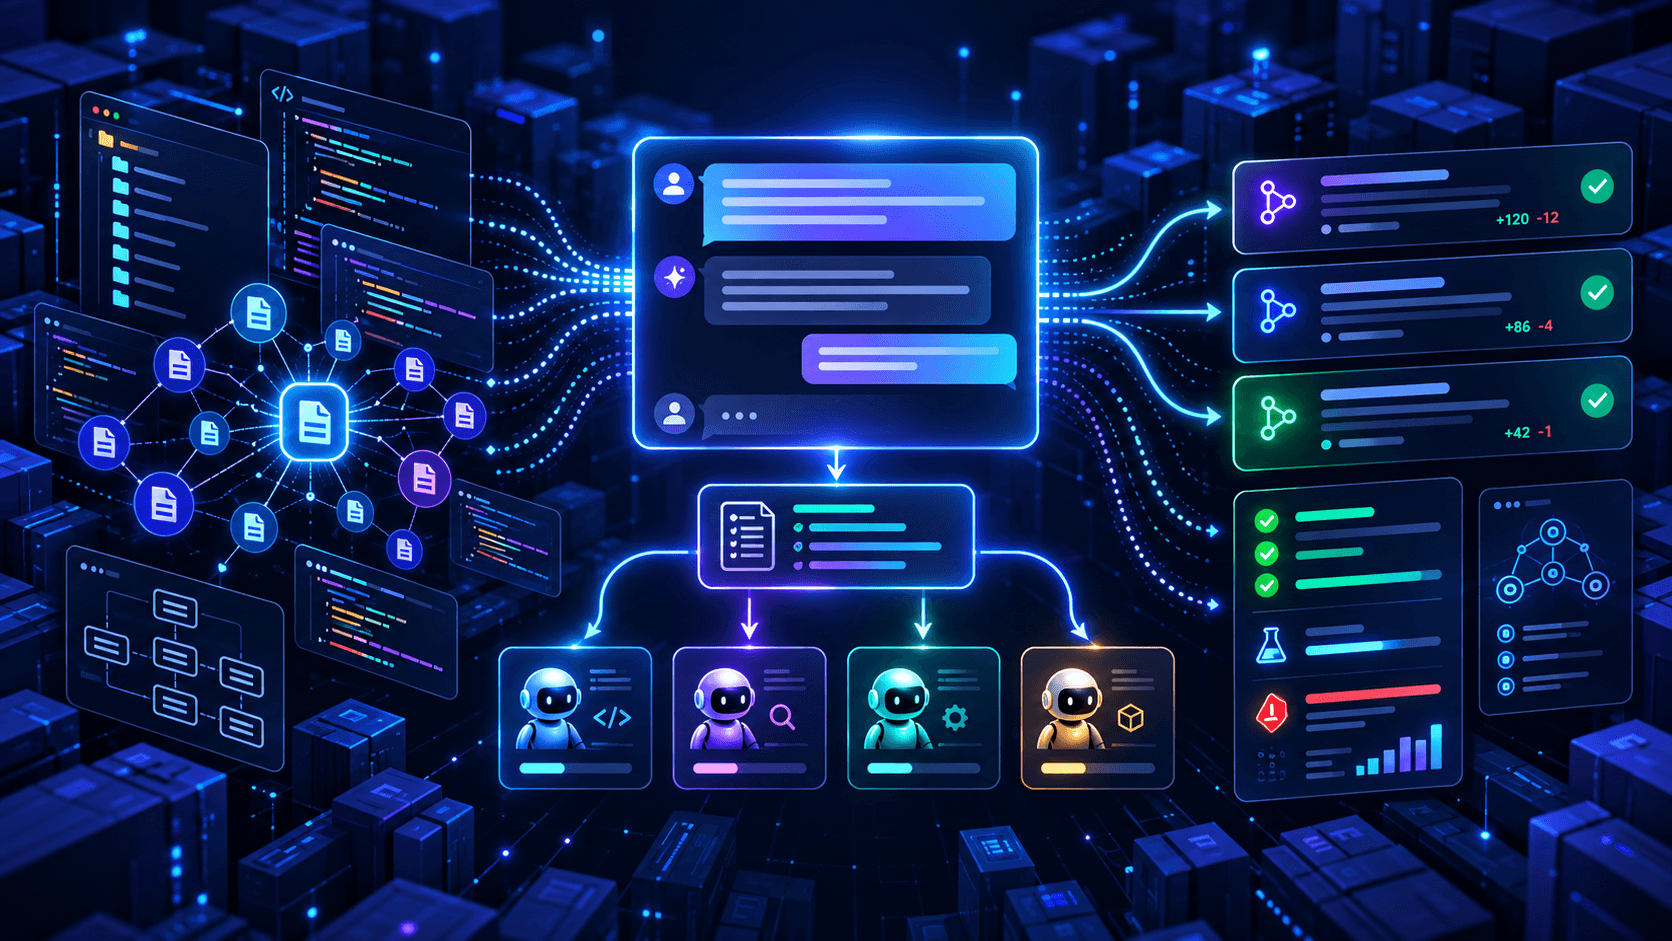
Blitzy this week added a chat interface to a platform that enables DevOps teams to employ artificial intelligence (AI) agents by expressing their intent in natural language. Dr. Neeraj Deshmukh, Field CTO for Blitzy, said the Chat to Prompt interface makes it possible for a software engineer to describe a desired outcome that is then […]
ScienceLogic Extends Observability Reach and Control Deeper into AI Agents
ScienceLogic has added additional tools and capabilities to its observability platform that provide deeper visibility and control over artificial intelligence (AI) agents that are being used to automate IT operations. The latest 2.7 update to the Skylar AI platform provides visibility into agent routing and tool selection via a catalog that uses traces to surface […]
Claude Platform Now Sends Agent Traces Straight to Your Observability Stack
Anthropic is making it easier to see what Claude-based agents do in production. The company has added OpenTelemetry trace export to the Claude Platform. Developers can now send traces from the Messages API, Claude Managed Agents, and the Claude SDKs to the observability tools they already use. The feature launched in public beta on October […]
Apple Brings Whole-Program C++ Hardening to Clang
Apple has added a new tool to the upstream LLVM project that could change how teams harden large C++ codebases. The clang-ssaf-driver, merged into LLVM Git this week, analyzes an entire project as it builds and then rewrites source code based on what it finds. The driver is part of Clang’s Scalable Static Analysis Framework […]
GitLab Fixes CVSS 10 Flaw in CI/CD Regex Engine, Plus 23 Other Vulnerabilities
GitLab is telling every self-managed customer to upgrade now. On October 12, the company shipped versions 19.4.2, 19.3.5, and 19.2.8 of GitLab Community Edition (CE) and Enterprise Edition (EE). The releases fix 24 security vulnerabilities. One has a CVSS score of 10.0, the highest rating possible. GitLab.com already runs the patched code. GitLab Dedicated customers […]
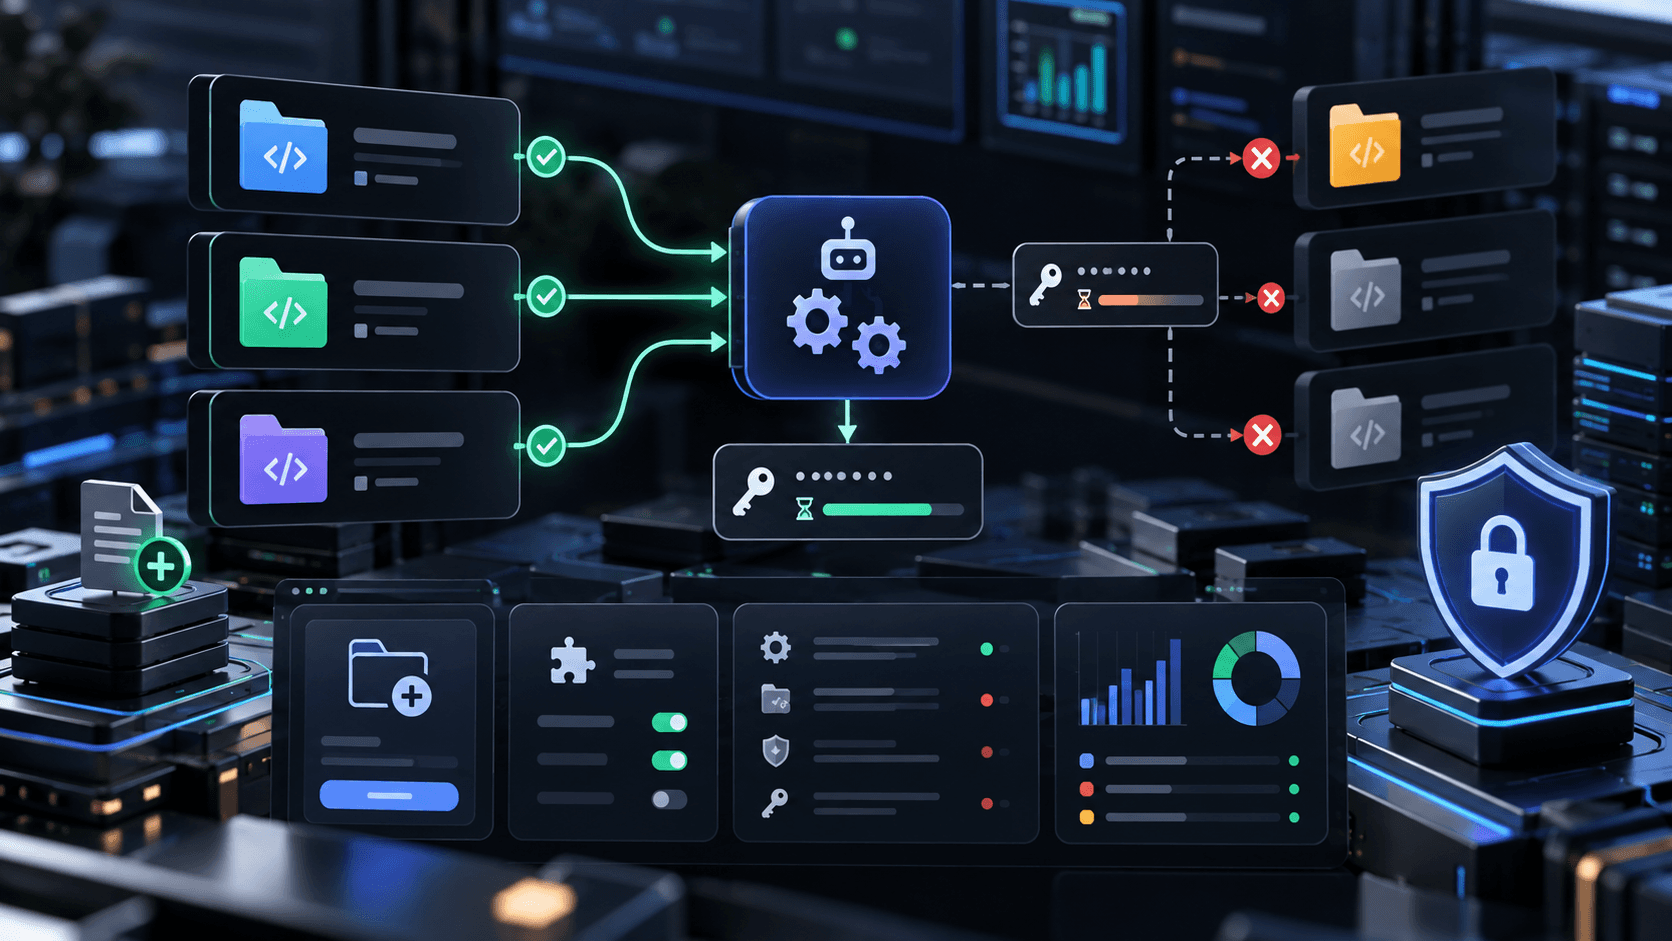
GitHub Narrows App Permissions to Pull Teams Off Classic PATs
GitHub is giving DevOps teams more ways to limit an automation job to only the access it needs. A batch of GitHub Apps updates released Oct. 13 adds narrower permissions, relaxes a long-standing install restriction for repository administrators, and makes it easier to move users to expiring tokens. GitHub says the goal is to help […]
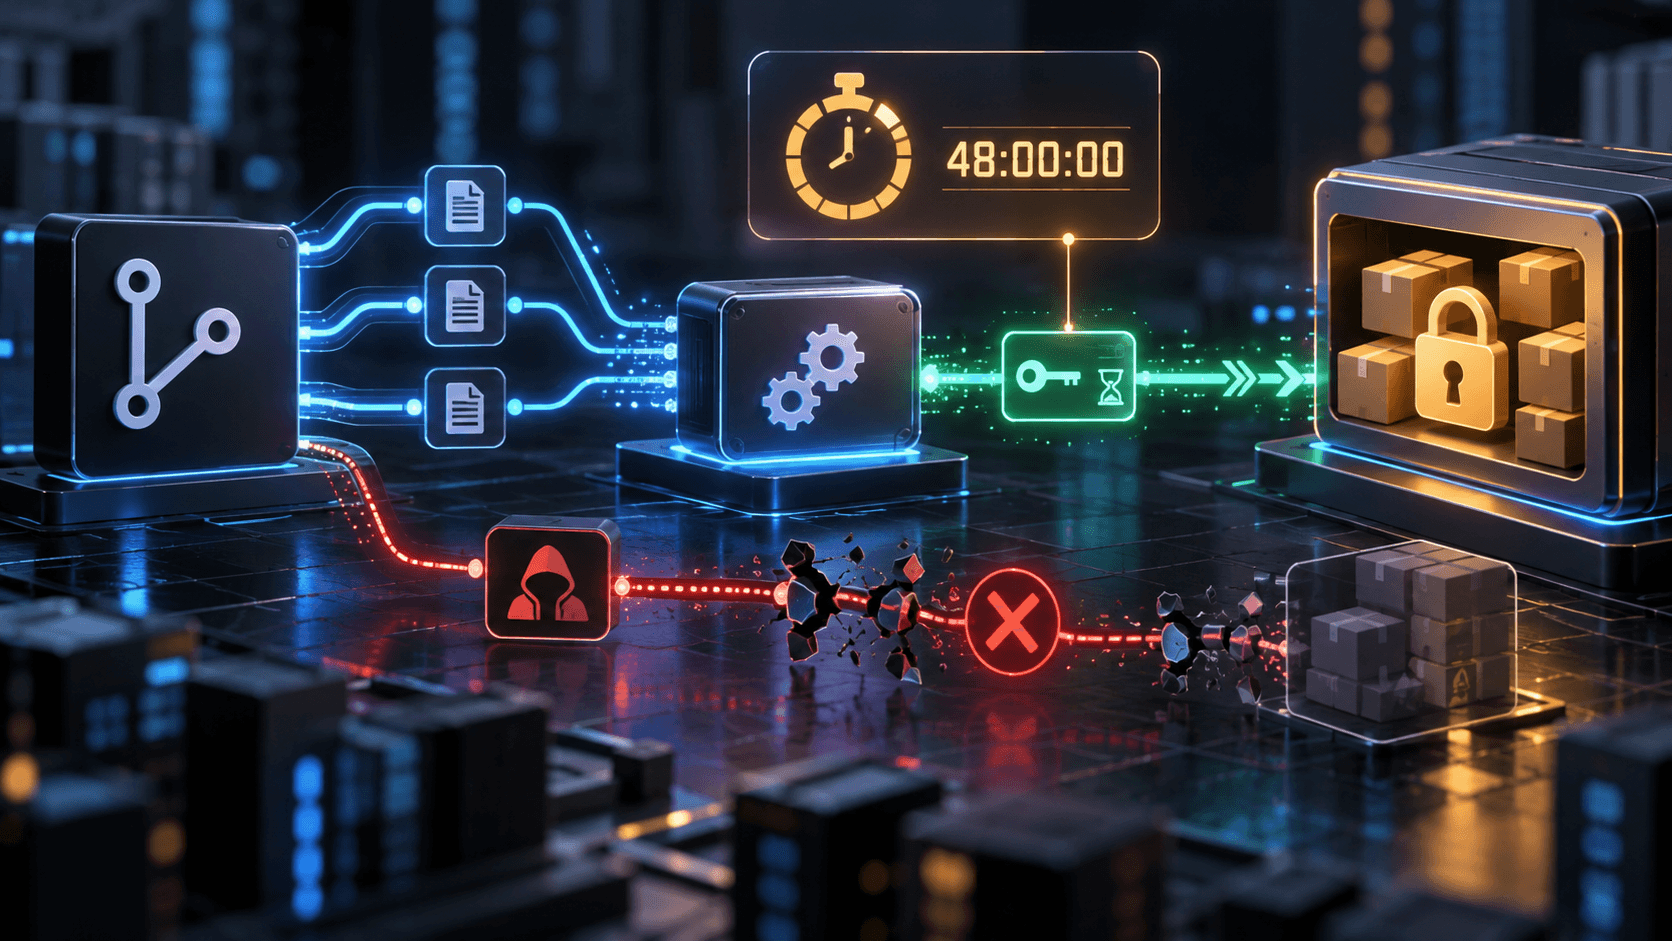
npm Puts a 48-Hour Clock on Unused Trusted Publishing Configurations
GitHub has added an expiration date to unused npm trusted publishing configurations. Any configuration that doesn’t complete a successful publish within 48 hours of creation now expires and can no longer authorize a release. It’s a small change. But it closes a gap that matters to anyone who publishes packages from a CI/CD pipeline. How […]
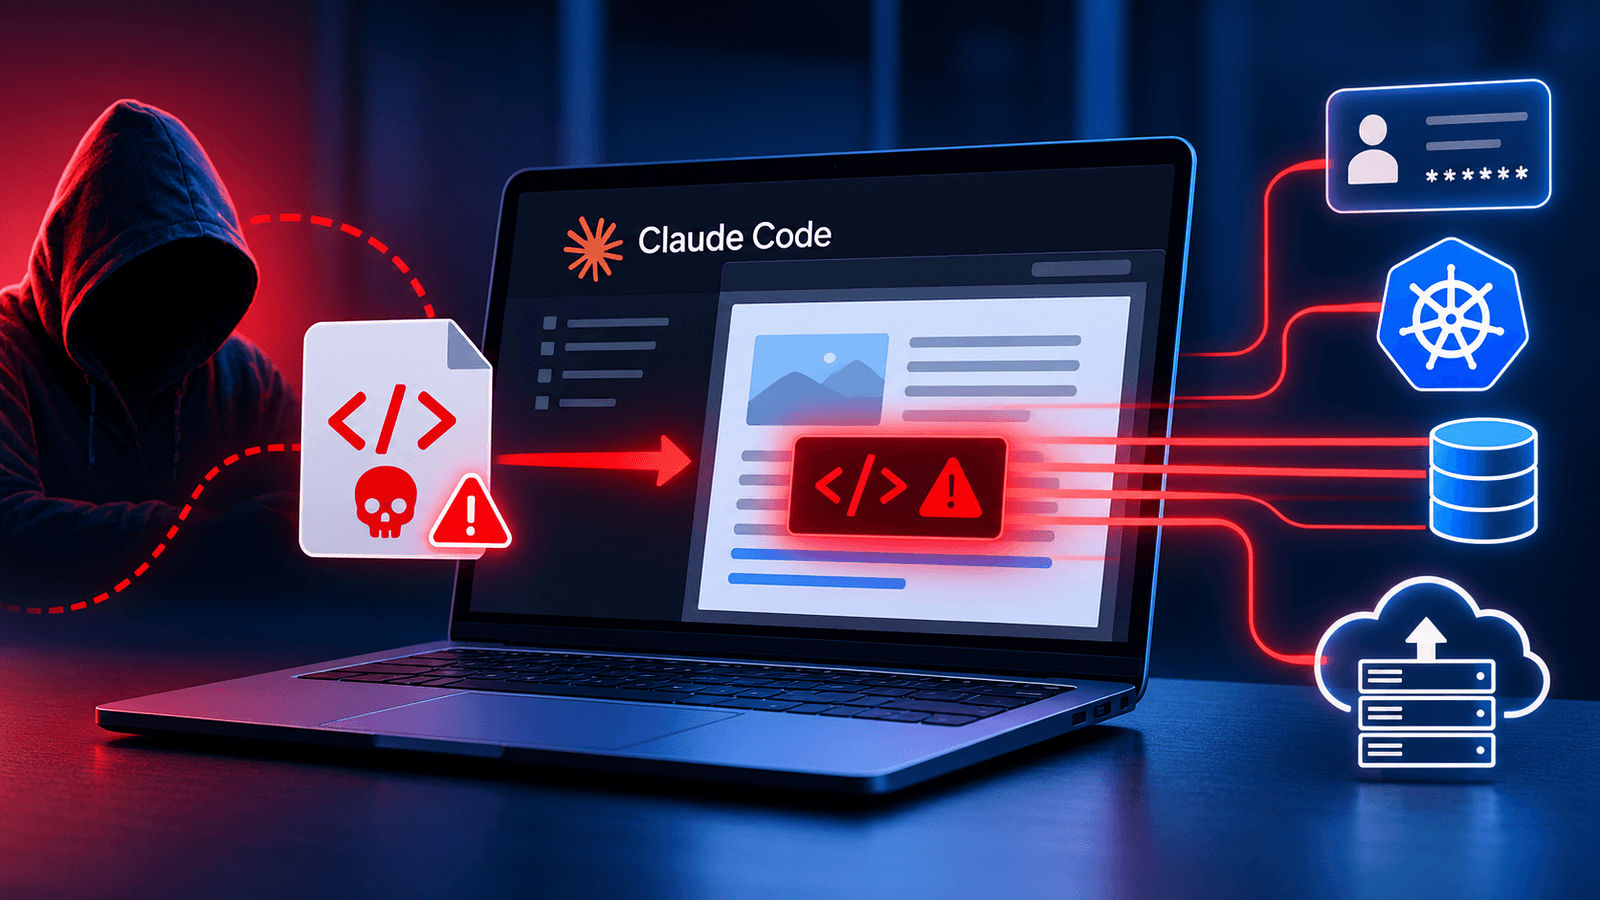
Noma Security Discloses Claude Code Desktop Exploit
Security researchers at Noma Security uncovered SneakPeek, a vulnerability in Anthropic’s Claude Code Desktop that allowed malicious JavaScript embedded in large HTML files to bypass sandbox protections and silently steal sensitive local data. The flaw exposed credentials, API tokens and Kubernetes configurations through the application’s preview pane. Although Anthropic has released a security update addressing the exploit, the discovery highlights growing software supply chain risks as AI coding tools become embedded in developer workflows without sufficient security oversight.
LocalStack Extends Emulation Reach to Microsoft Azure Services
LocalStack has made available a public beta of its platform that enables application developers to emulate Microsoft Azure cloud services on their local machines. Colin Neagle, head of marketing for LocalStack, said LocalStack now enables application developers to build software locally that can run across more than 40 Azure services. Following initial support for cloud […]
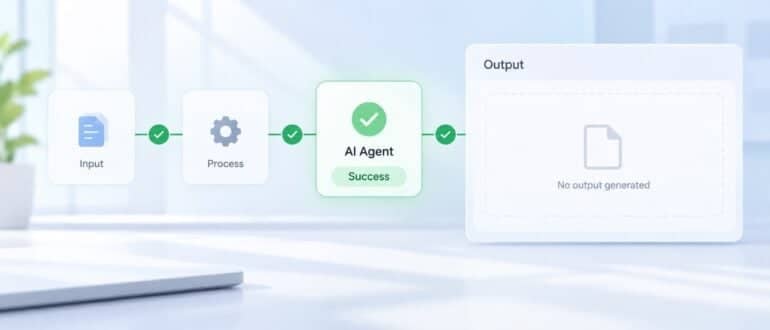
The Agent Failure Your Approval Gate Can’t Catch
An agent that does the wrong thing leaves evidence — a bad diff, a malformed record, a customer complaint. An agent that does nothing and reports success leaves a green checkmark, and green is the one signal your incident process is built to trust. Worry more about the second failure, because everything a DevOps team […]
IBM and Red Hat Disclose Discovery of More Than 400 Java Vulnerabilities
IBM and Red Hat this week reported they have identified and remediated more than 400 previously unknown vulnerabilities in Java libraries since launching a Lightwell initiative earlier this year. Additionally, Lightwell Clearinghouse, a program that enables IT organizations to submit specific open source software dependencies for priority review and remediation, is now generally available. Ben […]
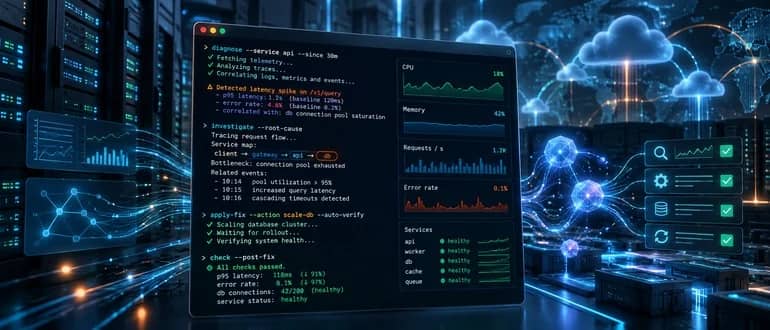
New Relic Debuts Command-Line Observability Tool for Developers and AI Agents
New Relic has unveiled Ground Truth CLI, a command-line tool that enables software developers and AI agents to analyze system performance and verify whether technical issues have been resolved without needing to use dashboards. The release reflects a big shift in enterprise IT as AI agents take on more advanced troubleshooting tasks. Traditional observability dashboards […]
GitHub Slams the Brakes on Private Vulnerability Reports
Drowning in AI-generated bug reports? GitHub has a radical answer: Stop accounts from reporting them. GitHub’s new limits on bug reports aren’t a solution to the AI bug-report flood. Anything but! They’re an admission that the traditional security-disclosure workflow, with human maintainers in the loop, simply doesn’t scale. The scarce resource is no longer discovering […]