
Tag: auditability
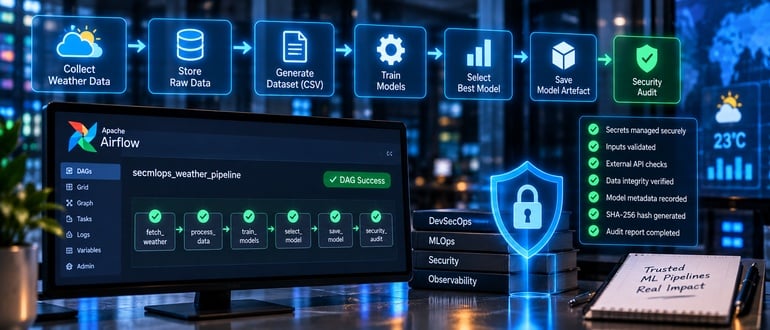
Why MLOps Pipelines Need Security Audits
 Natacha Bakir | | AI security, Airflow Variables, Apache Airflow, artifact integrity, auditability, data validation, devsecops, machine learning security, ML pipelines, MLOps, model metadata, model security, pipeline security, SecMLOps, secrets management, SHA-256
A practical SecMLOps experiment shows how Apache Airflow ML pipelines can adopt DevSecOps controls for secrets, validation, artifact integrity and auditable security evidence ...
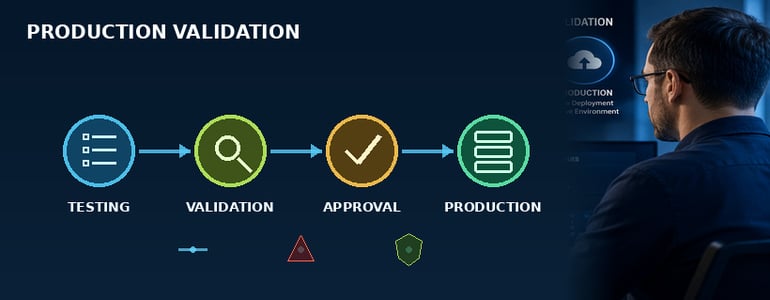
Production Validation: The Missing Layer in Enterprise Releases
 Kawaljeet Singh Chadha | | auditability, business validation, business-critical systems, change management, data quality, deployment controls, DevOps governance, enterprise devops, Enterprise software, exception-handling, operational approval, production assurance, production readiness, production validation, reconciliation, regulated environments, release governance, release management, release readiness, software testing
Production validation adds a critical business-control layer between testing and deployment, combining data checks, exception review, approvals, reconciliation and operational readiness before a release reaches production ...

Why Governance Determines Whether Agentic AI Accelerates or Stalls Engineering
 Eric Paulsen | | agentic AI, Agentic Workflows, AI code review, auditability, Automated Refactoring, Code Completion, Developer Velocity, Engineering Governance, Governance Debt, Parallel Engineering, Risk-based Governance, software development lifecycle SDLC
AI coding tools offer rapid productivity gains, but "governance debt" often slows delivery. Learn how to embed risk-based controls and auditability into agentic AI workflows to scale engineering capacity ...

Gemini CLI Plan Mode Separates Thinking From Doing — and Makes Read-Only the Default
 Tom Smith | | agent governance, ask_user, auditability, codebase investigation, Conductor, developer approval, Gemini 3.1 Pro, Gemini CLI, MCP read-only, model routing, orchestration, plan mode, read-only, research-first, risk management
Google’s Gemini CLI Plan Mode enforces read-only research-first workflows—using higher-reasoning models for strategy, ask_user prompts for clarification, and read-only MCP integration—so agents propose vetted implementation plans before code changes ...

Cybersecurity Laws Will Shape the Future of DevOps
 Alexander Williams | | auditability, CI/CD compliance, CISA, compliance-as-code, compliance-driven DevOps, cybersecurity compliance frameworks, cybersecurity regulation, DevOps accountability, devsecops, Executive Order 14028, global cybersecurity laws, governance in DevOps, incident disclosure, NIS2 Directive, RegOps, regulatory DevOps, SBoM, SEC breach disclosure, secure software development, secure-by-design, security automation, software liability, traceability, zero-trust
From the EU’s NIS2 Directive to U.S. SEC breach disclosure rules, cybersecurity regulation is accelerating faster than code releases. DevOps teams must evolve into RegOps—embedding compliance, traceability, and trust directly into their ...
