
Tag: AI security
GitHub’s Security Autofix Agent Now Remembers What It Fixed
 Tom Smith | | agentic autofix, AI coding agents, AI security, application security, code scanning, CodeQL, Copilot Memory, devsecops, github, GitHub Advanced Security, GitHub Copilot, repository memory, secure coding, vulnerability remediation
GitHub’s agentic autofix now uses Copilot Memory to reuse repository-specific security fix patterns, helping Copilot apply lessons from past vulnerabilities across future alerts, reviews and coding workflows ...
Your AI Coding Assistant Has the Keys to the Repo. Z.ai Just Showed Why That Matters
Tom Smith | | AI coding assistants, AI Governance, AI security, Cloud Security, code security, Data Exfiltration, data privacy, Developer Security, developer tools, devsecops, egress monitoring, secrets management, shadow ai, Software Supply Chain, source code security, Z.ai, ZCode, Zhipu AIZCode’s default-on indexing feature reportedly uploaded entire developer workspaces to cloud storage, highlighting why AI coding assistants should be treated as privileged software and closely monitored ...
Why Shift Left is Dead
 Devin Maguire | | ADLC, agentic development lifecycle, AI Governance, AI guardrails, AI security, AI-Driven Development, AI-generated code, application security, Developer Security, devsecops, prompts, sdlc, secure software development, shadow ai, shift left security, Software Supply Chain Security
AI-driven development is exposing risks before code is written, forcing security teams to move beyond shift-left and govern agents, prompts, tools and data across the entire development lifecycle ...
Codex Sandbox Escapes Show Why Agent Guardrails Can’t Live Inside the Agent
Tom Smith | | agentic AI, AI coding agents, AI security, application security, Codex CLI, Codex Desktop, Codex Security, coding agent security, Developer Security, devsecops, Heapjack, OpenAI Codex, Overpatch, sandbox escape, sandbox security, Software Supply ChainTwo patched OpenAI Codex vulnerabilities, Heapjack and Overpatch, exposed how coding agents can escape sandboxes and reach developer systems without approval prompts ...
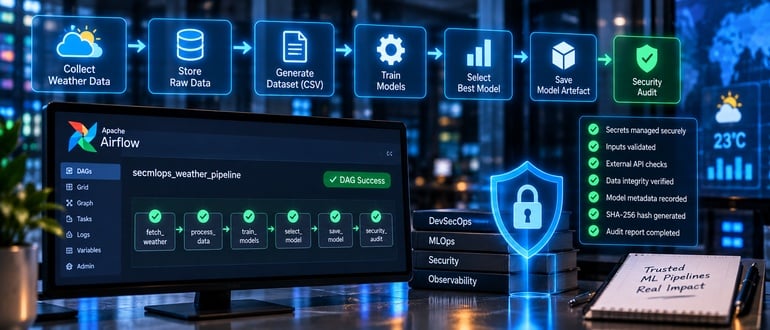
Why MLOps Pipelines Need Security Audits
 Natacha Bakir | | AI security, Airflow Variables, Apache Airflow, artifact integrity, auditability, data validation, devsecops, machine learning security, ML pipelines, MLOps, model metadata, model security, pipeline security, SecMLOps, secrets management, SHA-256
A practical SecMLOps experiment shows how Apache Airflow ML pipelines can adopt DevSecOps controls for secrets, validation, artifact integrity and auditable security evidence ...
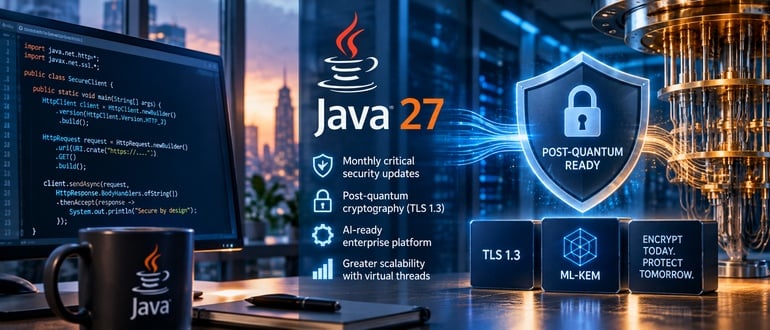
Java 27 Tackles Post-Quantum Security and a Faster Patch Cadence
Tom Smith | | AI security, critical patch updates, enterprise applications, enterprise Java, FIPS 140-3, harvest now decrypt later, Helidon 27, Java 27, Java security, JavaFX 27, JDK 11, JDK 17, JDK 21, JDK 25, JDK 27, JDK 8, ML-KEM, OpenJDK, Oracle Java, Oracle Jipher, post-quantum cryptography, quantum security, TLS 1.3, virtual threadsJava 27 strengthens enterprise security with monthly critical patch updates and post-quantum TLS 1.3 support, helping organizations prepare for AI-driven threats and future quantum risks ...
A Simple Website Summary Just Exposed the Limits of AI Coding Guardrails
Tom Smith | | agentic AI security, AI agent security, AI coding assistants, AI guardrails, AI security, Anthropic, Auto Mode, Claude Code, Claude Opus 5, devops security, indirect prompt injection, Johann Rehberger, network egress, platform engineering, prompt injection, Python module shadowing, RCE, remote code execution, sandboxing, struct.pyClaude Code’s Auto Mode was bypassed in an attack chain that turned a routine webpage summary into remote code execution, highlighting the limits of AI agent guardrails ...
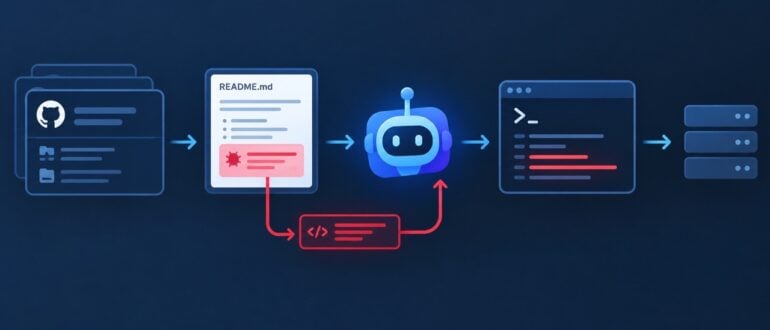
When AI Coding Agents Become Malware Delivery Systems
 Samuel Ogbonna | | AI coding agents, AI security, devsecops, github, prompt injection, Software Supply Chain
AI coding agents are becoming part of everyday development work. Developers use them to find libraries, configure projects, troubleshoot installation problems, and set up new tools. An agent can search GitHub, read ...
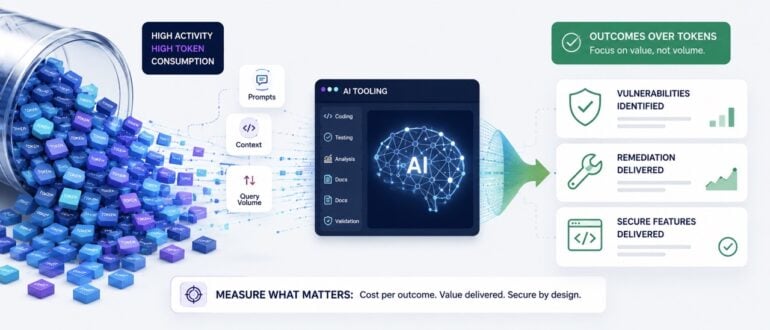
Why “Tokenmaxxing” Was Always the Wrong Way for Developers to Measure AI Productivity
 Drew Thompson | | ai, AI Development, AI security, application security, developer productivity, software development
The term "tokenmaxxing" left the developer lexicon just as quickly as it arrived, and like most viral technology concepts, it means different things depending on who's using it. In practice, the term ...
Critical Flaw in isolated-vm Can Lead to Sandbox Escape, RCE Threat
 Jeff Burt | | Activepieces, AI security, C/C++, Endor Labs, isolated-vm, JavaScript security, Mastra, n8n, Node.js security, remote code execution, Sandbox, software vulnerability, TOCTOU, V8 Isolate, vm2
Developers for years have been using vm2, an open-source Node.js library, to run untrusted JavaScript inside a secure and isolated sandbox environment. It uses Node.js’s built-in modules and JavaScript Proxies and lets ...
What the Microservices Era Can Teach Us About AI
 Mark Fussell | | agent identity, agent observability, agent runtime, agentic AI, agentic durable execution, AI agents, AI architecture, AI Governance, AI infrastructure, AI security, autonomous agents, cloud-native AI, distributed systems, durable execution, LLM observability, microservices, Open Standards, platform engineering, vendor lock-in, workflow orchestration
AI agents are not just microservices with LLMs attached. Their long-running, non-deterministic workflows demand durable execution, per-step identity, governance and observability ...
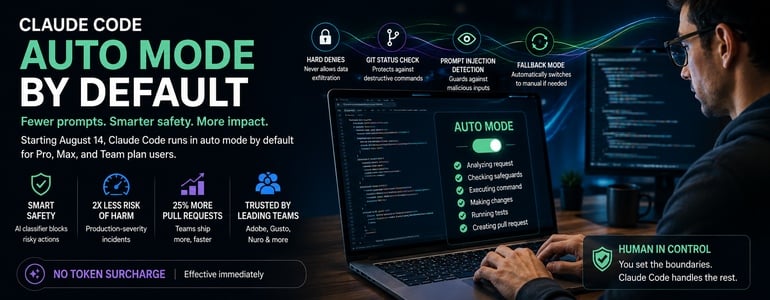
Anthropic Makes Claude Code’s Auto Mode the Default, Betting Automation Beats Manual Review
Tom Smith | | agent permissions, agentic coding, AI code generation, AI coding agents, AI Governance, AI guardrails, AI permissions, AI safety, AI security, Anthropic, autonomous coding agents, Claude Code, Claude Code auto mode, Claude Code security, coding automation, developer productivity, developer tools, human engineering the loop, human-in-the-loop, permission fatigue, prompt injection, Pull Request Automation, secure AI agents, software development, software engineeringAnthropic is making Claude Code’s auto mode the default for Pro, Max and Team users, replacing constant permission prompts with classifier-based guardrails designed to catch risky actions without slowing developers down ...

