
Tag: secure software development
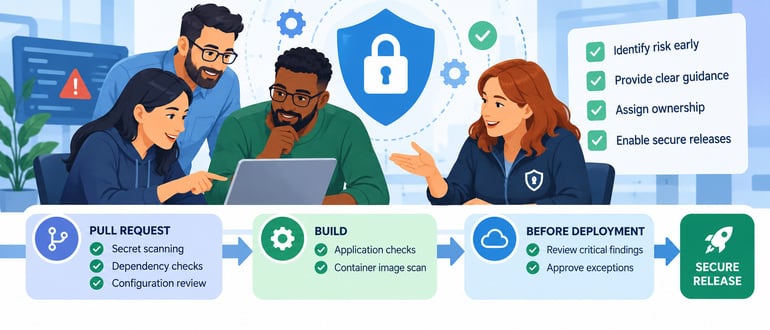
DevSecOps Teams as Partners in Secure Software Delivery
 Manish Shetty | | application security, CI/CD, CI/CD security, dependency security, devops security, devsecops, risk management, secure software development, security automation, Security Guardrails, shift left security, software security, Software Supply Chain, vulnerability management
DevSecOps teams can reduce last-minute release delays by shifting security decisions earlier, improving guardrails, clarifying ownership and making findings actionable ...
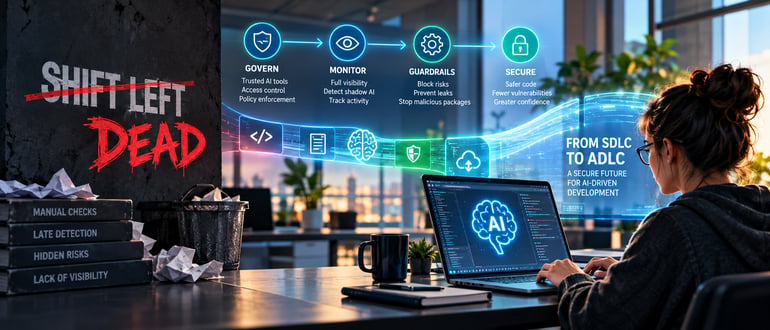
Why Shift Left is Dead
 Devin Maguire | | ADLC, agentic development lifecycle, AI Governance, AI guardrails, AI security, AI-Driven Development, AI-generated code, application security, Developer Security, devsecops, prompts, sdlc, secure software development, shadow ai, shift left security, Software Supply Chain Security
AI-driven development is exposing risks before code is written, forcing security teams to move beyond shift-left and govern agents, prompts, tools and data across the entire development lifecycle ...
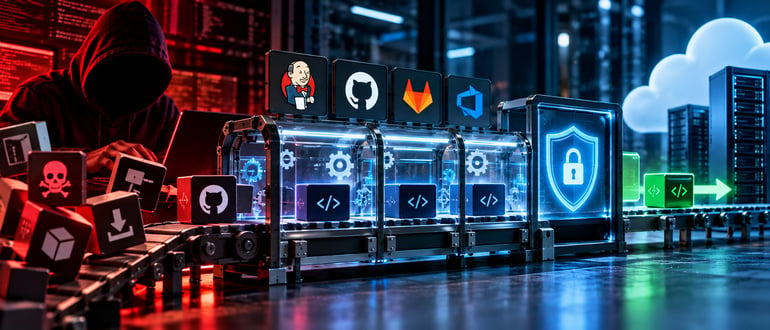
Why Your CI/CD Pipeline Is Your Most Unprotected Attack Surface
 Muhammad Yawar Malik | | application security, build agents, build pipelines, CI/CD security, Cloud Security, credential security, dependency security, deployment security, devops security, devsecops, ephemeral runners, GitHub Actions, infrastructure security, Jenkins security, least-privilege, pipeline security, provenance attestation, secrets management, secure pipelines, secure software development, software provenance, Software Supply Chain, supply chain attacks, third-party actions, XZ Utils
CI/CD pipelines often hold privileged credentials, execute third-party code and connect directly to production, making pipeline security one of the most overlooked risks in modern DevOps ...

GitHub Widens the Door on Advanced Security Trials
 Tom Smith | | AI coding, application security, CodeQL, Developer Security, devsecops, exposed credentials, GHAS, GitHub Advanced Security, GitHub Code Security, GitHub Enterprise Cloud, GitHub Secret Protection, GitHub security, mid-market security, Repository Security, secret scanning, secure software development, Software Supply Chain Security, vulnerability scanning
GitHub raised its self-serve Advanced Security trial cap from 100 to 300 licenses, letting more mid-size Enterprise Cloud orgs test for free ...
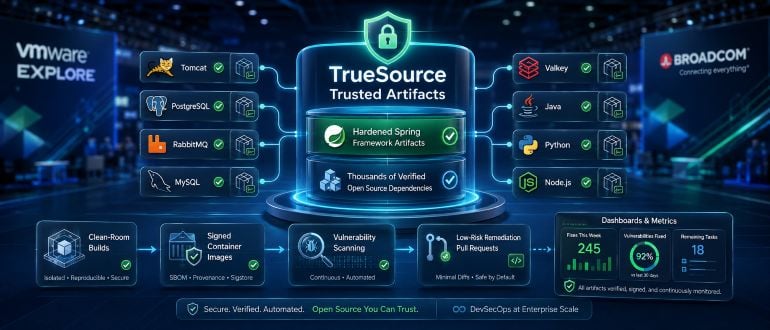
Broadcom Launches TrueSource Service to Secure Spring Framework
 Mike Vizard | | AI coding, Apache Tomcat, application security, Bitnami Secure Images, Broadcom, container security, dependency security, devsecops, java, kubernetes, node.js, open source security, open source vulnerabilities, patch management, Python, SBoM, secure software development, software artifacts, Software Supply Chain Security, Spring framework, Spring Security, Tanzu, TrueSource Trusted Artifacts, VMware explore, vulnerability management
Broadcom launches TrueSource Trusted Artifacts to provide hardened Spring dependencies, secure open source packages and automated vulnerability remediation ...

Anthropic Code Review Dispatches Agent Teams to Catch the Bugs That Skim Reads Miss
Tom Smith | | AI code review, AI coding agents, Anthropic Code Review, Claude Code, Code Review Automation, developer productivity, devops, Engineering Velocity, GitHub integration, Logical Bug Detection, multi-agent systems, Pull Request Automation, secure software development, software quality, software reliabilityAnthropic Code Review dispatches agent teams to find bugs in PRs. Multi-agent analysis, severity ranking, and inline fixes for Teams and Enterprise ...
Feeding the Beast: Why Giving Your Code to AI Agents Might Be Your Biggest Mistake Yet
 Alexander Williams | | AI agent security risks, AI assisted development pitfalls, AI code automation risks, AI coding agents, AI data leakage, AI model drift, codebase governance, DevSecOps AI risk, generative AI code review, human in the loop coding, secure software development, software engineering AI, technical debt from AI
Your codebase isn’t food, but AI agents are more than happy to devour it. Teams keep handing over entire repositories because automation feels like a cheat code for productivity. The problem shows up later, ...

DevSecOps in Practice: Closing the Gap Between Development Speed and Security Assurance
 Usman Peter | | application security automation, automated vulnerability scanning, CI/CD pipeline security, cloud and container security, continuous feedback loops, continuous security integration, developer security mindset, development speed and security balance, devsecops, DevSecOps best practices, risk-based security, SaferNet VPN, Secure DevOps, secure software development, security as code, security automation tools, security champions, security culture, shift left security, Software Supply Chain Security
In the world of modern software development, speed is king. Teams are under constant pressure to release features, fix bugs and stay ahead of competitors. Yet, as development velocity increases, so does ...

Cybersecurity Laws Will Shape the Future of DevOps
Alexander Williams | | auditability, CI/CD compliance, CISA, compliance-as-code, compliance-driven DevOps, cybersecurity compliance frameworks, cybersecurity regulation, DevOps accountability, devsecops, Executive Order 14028, global cybersecurity laws, governance in DevOps, incident disclosure, NIS2 Directive, RegOps, regulatory DevOps, SBoM, SEC breach disclosure, secure software development, secure-by-design, security automation, software liability, traceability, zero-trustFrom the EU’s NIS2 Directive to U.S. SEC breach disclosure rules, cybersecurity regulation is accelerating faster than code releases. DevOps teams must evolve into RegOps—embedding compliance, traceability, and trust directly into their ...
Establishing Visibility and Governance for Your Software Supply Chain
 Parth Patel | | application security, asset visibility, attack surface management, build-time security, Cloud Governance, context-aware security, cybersecurity governance, dependency tracking, eBPF runtime analysis, Kubernetes Gatekeeper, Log4Shell, open source security, provenance attestation, risk reduction, SBoM, SBOM automation, secure software development, SLSA, software bill of materials, software provenance, Software Supply Chain Security, supply chain risk, Third-party Dependencies, VEX, vulnerability management, vulnerability prioritization
Asset visibility and cloud governance start with SBOMs, VEX, and provenance tracking. Learn how to secure your software supply chain ...
CISA Pushes Steps to Better Secure Software and Product Designs

The country’s top cybersecurity agency is urging developers to take steps to ensure the software they’re building and the products they roll out are secure and protect end users. The Cybersecurity and ...

Can Regulatory Mandates Secure Software Development?

Software companies have a long history of delivering incomplete and insecure products. This happens for a couple of reasons. Fast time-to-market has always been a business priority, taking precedence over security, especially ...

