
Tag: vulnerability management
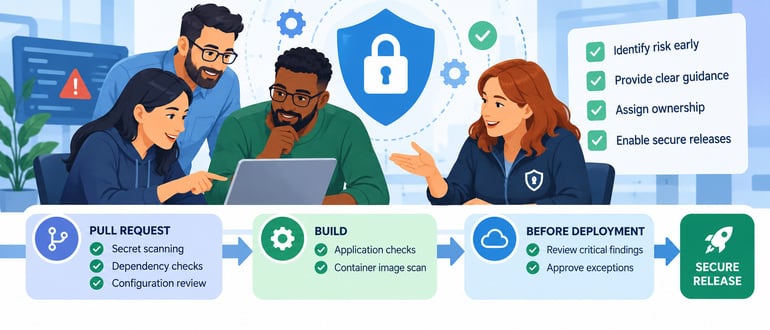
DevSecOps Teams as Partners in Secure Software Delivery
 Manish Shetty | | application security, CI/CD, CI/CD security, dependency security, devops security, devsecops, risk management, secure software development, security automation, Security Guardrails, shift left security, software security, Software Supply Chain, vulnerability management
DevSecOps teams can reduce last-minute release delays by shifting security decisions earlier, improving guardrails, clarifying ownership and making findings actionable ...
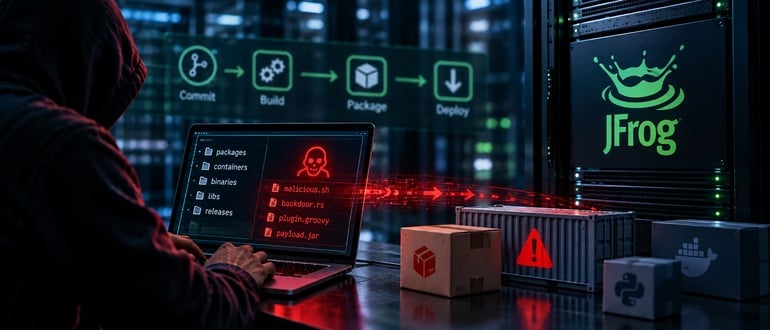
More JFrog Artifactory Bugs Are Under Attack, and All Three Have Patches
 Tom Smith | | administrative tokens, artifact repositories, authentication bypass, build pipeline security, CI/CD security, CVE-2026-42016, CVE-2026-42018, CVE-2026-82329, Cybersecurity, devsecops, Groovy plugins, JFrog Artifactory, patch management, privilege escalation, Repository Security, Rust backdoors, Software Supply Chain, vulnerability management, web shells
Attackers are actively exploiting three JFrog Artifactory flaws, exposing how slow patching can turn artifact repositories into software supply chain attack paths ...
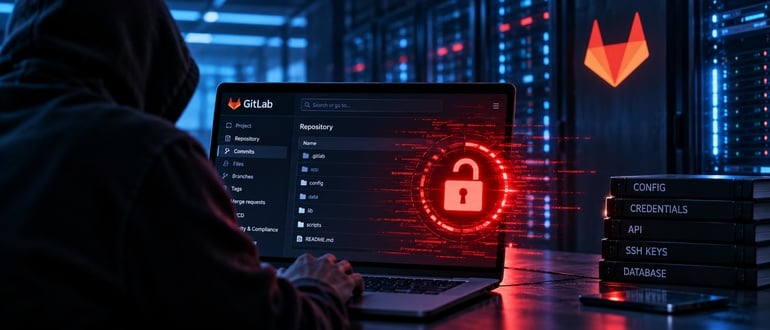
GitLab’s Critical Patch Closes a Path Traversal Flaw Attackers Are Already Probing
Tom Smith | | access control, API security, CI/CD security, credential theft, CVE-2026-85706, CVE-2026-87719, CVSS 10.0, Cybersecurity, devops security, devsecops, gitlab, GitLab Duo, GitLab security, GraphQL security, patch management, Repository Security, self-managed GitLab, Software Supply Chain, vulnerability managementGitLab patches two critical flaws, including a CVSS 10.0 unauthenticated file-read vulnerability, putting self-managed instances under urgent pressure to upgrade ...

Why AI Agents Shouldn’t Guess at Vulnerability Exploitability
 Harish Gaggar | | AI agents, application security, SBoM, Software Supply Chain, vulnerability management, vulnerability prioritization
Vulnerability prioritization is not a language problem. The safest agent architectures use models to interpret and explain, while deterministic systems traverse the evidence. Ask a security team a simple question: Of the ...
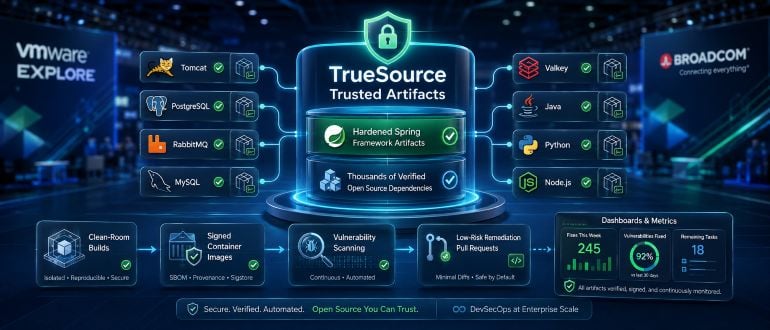
Broadcom Launches TrueSource Service to Secure Spring Framework
 Mike Vizard | | AI coding, Apache Tomcat, application security, Bitnami Secure Images, Broadcom, container security, dependency security, devsecops, java, kubernetes, node.js, open source security, open source vulnerabilities, patch management, Python, SBoM, secure software development, software artifacts, Software Supply Chain Security, Spring framework, Spring Security, Tanzu, TrueSource Trusted Artifacts, VMware explore, vulnerability management
Broadcom launches TrueSource Trusted Artifacts to provide hardened Spring dependencies, secure open source packages and automated vulnerability remediation ...
Report Shines Spotlight on 91 Vulnerabilities Fixed in Latest Update to Spring Framework
Mike Vizard | | AI cybersecurity, AI vulnerabilities, application security, Broadcom, CVEs, devsecops, Java security, open source security, open source vulnerabilities, patch management, security automation, software components, Software Supply Chain, sonatype, Spring framework, Spring vulnerabilities, technical debt, virtual patching, vulnerability managementSonatype says 91 Spring vulnerabilities affecting more than 209,000 software components highlight how AI is accelerating vulnerability discovery and creating a new patching challenge for DevSecOps teams ...
Open Source Code Just as Secure as Proprietary Software—If You Manage It Right, Says CISA
 Joab Jackson | | AI security, CISA, federal government, open source software, Software Supply Chain, vulnerability management
Open source can be just as safe as proprietary software, though government agencies (and private enterprises) should take additional measures to secure it properly, according to a new guide published by the ...
Continuous Security in DevSecOps: Moving Beyond One-Time Testing
 James Miller | | automated security, CI/CD pipeline, continuous security, devsecops, penetration testing, SAST/DAST, sdlc, shift left security, software composition analysis (SCA), vulnerability management
Waiting for a single annual pentest to secure your application is like locking your front door only once a year and hoping for the best. In an era where 133 new vulnerabilities are reported every single ...
Rein Security Emerges to Analyze Reachability of Application Vulnerabilities
Mike Vizard | | AI-generated vulnerabilities, API security, application security, continuous vigilance, devsecops, funding, Matan Bar Efrat, performance overhead, security automation, software development, software security testing, vulnerability managementRein Security has emerged from stealth to launch an application security platform capable of determining the reach of a vulnerability based on which libraries and application programming interfaces are actually running in ...

Is Claude Opus 4.6 the Best Security Researcher Ever?
Mike Vizard | | 600 vulnerabilities, AI augmentation, AI-driven vulnerability discovery, Anthropic, attackers/opportunists, Axios, Claude Opus 4.6, continuous discovery, coordinated disclosure, defensive adaptation, Gadi Evron, Heather Adkins, maintainers burnout, open source projects, Red Team report, remediation, scale vs capacity, security triage, The Futurum Group, vulnerability management, zero daysAnthropic’s Claude Opus 4.6 uncovered more than 600 previously unknown vulnerabilities in widely used open source software, raising new questions about AI-driven security research, vulnerability management, and defensive readiness ...

Your AI Agents Have a Blind Spot: What DevOps Teams Need to Know About Cross-LLM Security
 Arun Sanna | | AI agents, AI infrastructure, Behavioral Monitoring, Cross-LLM Detection, Cybersecurity, devops, DevOps pipelines, incident management, Model-Aware Detection, Multi-LLM Environments, security best practices, Security Gaps, supply chain security, threat detection, vulnerability management
Explore the challenges of AI agents in DevOps pipelines, highlighting the importance of model-aware detection to improve security and reduce vulnerabilities ...
Patch or Perish: The Brutal Truth About Vulnerability Management in 2025
 Samuel Ogbonna | | Active Risk AI, AI-powered VM, attack surface management, breach costs, Cisco VM, continuous monitoring, CVEs 2025, cybersecurity best practices, delayed patching, exploit prediction, IBM data breach report, Kenna Security, machine learning risk scoring, patch management, predictive prioritization, Rapid7, remediation automation, risk-based prioritization, Tenable, threat-aware prioritization, unpatched vulnerabilities, Vulcan Cyber, vulnerability management, vulnerability scanning
Vulnerability management in 2025 is overwhelmed by escalating CVEs and costly breaches; organizations must shift from slow, manual patching to continuous, risk-based, AI-powered remediation to stay secure ...

