
IT Security
From Software Supply Chains to AI Vulnerabilities: Why Neither Solves Enterprise Linux Security
 Moshe Bar | | enterprise security, Linux security, patch management, runtime protection, runtime security, vulnerability management
For nearly a decade, cybersecurity has been dominated by one overarching concern: securing the software supply chain. Organizations invested heavily in Software Bills of Materials (SBOMs), artifact signing, provenance frameworks, reproducible builds, ...
Leaked GitLab Email Tokens Can Reach Code, Secrets and CI/CD Pipelines
 Jaime Hampton | | Aikido Security, application security, CI/CD, devsecops, gitlab, Software Supply Chain
Security researchers have uncovered a GitLab behavior that could let attackers use a leaked project email address to push code, trigger CI/CD jobs and reach other repositories accessible to the address owner ...
TeamPCP Supply Chain Attack Leads to CrowdSec Source Code Being Stolen
 Jeff Burt | | CrowdSec, EDR, github, Mini Shai-Hulud, NPM security, OAuth tokens, supply chain attacks, TanStack compromise, TeamPCP
CrowdSec says attackers stole source code from about 170 private GitHub repositories after a TanStack npm supply chain attack exposed an OAuth token tied to a former employee ...
Flaw in DeepSeek Harness AI Coding Tool Let Agents Disable Their Sandbox
Jeff Burt | | agentic AI security, AI coding agents, AI sandbox, API Keys, DeepSeek Harness, OX Security, VulnCheckNews of the now-fixed vulnerability comes amid growing concerns that AI vendors do not in have complete control of their autonomous agents ...
JFrog Moves to Secure Agentic Engineering Workflows

JFrog today at its swampUP 2026 conference added a zero touch remediation capability that ensures the most secure version of a binary is provided even when application developers request a version that ...
Hackers Target Popular arrayref Rust Crate in Supply-Chain Attack
Jeff Burt | | arrayref, information stealing, North Korea, Rust programming language, software supply chain attacks, StepSecurity, typosquatting, Wiz ResearchSecurity researchers are sorting through a complex, stealthy, and fast-moving supply-chain attack aimed at pushing information-stealing malware by compromising the account of the maintainer of multiple Rust crates and introducing four more ...
npm v12 Shuts Down a Popular Malware Trick — But the Threat Isn’t Going Away

For years, one of the easiest ways to sneak malware onto a developer's machine has been to hide in plain sight. Install a package from npm, and any lifecycle script bundled with ...
Critical Flaw in isolated-vm Can Lead to Sandbox Escape, RCE Threat
Jeff Burt | | Activepieces, AI security, C/C++, Endor Labs, isolated-vm, JavaScript security, Mastra, n8n, Node.js security, remote code execution, Sandbox, software vulnerability, TOCTOU, V8 Isolate, vm2Developers for years have been using vm2, an open-source Node.js library, to run untrusted JavaScript inside a secure and isolated sandbox environment. It uses Node.js’s built-in modules and JavaScript Proxies and lets ...

GitHub Sharpens CodeQL’s Eye on Actions Workflows and Modern JavaScript
GitHub Actions pipelines have become one of the quieter attack surfaces in software development. They pull in third-party actions, cache dependencies, and pass secrets between jobs, often without anyone reviewing the workflow ...
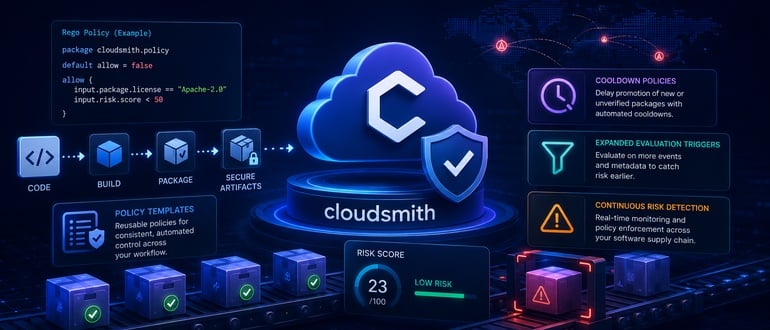
Cloudsmith Extends Policies and Controls to Secure Application Binaries
Cloudsmith this week revealed it has expanded the policy management and continuous risk detection capabilities it makes available within its software artifact management platform to now include policy templates, cooldown policies, and ...

GitHub Breach Tied to Malicious VS Code Extension Exposes Thousands of Internal Repositories

GitHub says attackers accessed thousands of internal repositories after a company employee’s device was compromised through a malicious Visual Studio Code extension, though the company said it has removed the malicious extension, ...

Cyber Threats to DevOps Platforms Rising Fast, GitProtect Report Finds
Jeff Burt | | Azure DevOps, CI/CD, code repositories, Cybersecurity, DevOps platform downtime, devops security, extortion, GitHub security, GitProtect.io DevOps Threats report, GPUGate, JIRA, Kaspersky Lab, NPM security, Ransomware, Shai-HuludThe number of incidents targeting DevOps platforms grew 21% in 2025, but the amount of downtime jumped almost 95%, the security firm said ...

