
Features
Leaked GitLab Email Tokens Can Reach Code, Secrets and CI/CD Pipelines
 Jaime Hampton | | Aikido Security, application security, CI/CD, devsecops, gitlab, Software Supply Chain
Security researchers have uncovered a GitLab behavior that could let attackers use a leaked project email address to push code, trigger CI/CD jobs and reach other repositories accessible to the address owner ...
Blitzy Makes Sandbox for Reverse Engineering Code Available at No Cost
Blitzy has made available a sandbox where DevOps teams can reverse-engineer up to one million lines of code, generate up to 25,000 lines of tested end-to-end code, and identify security vulnerabilities across ...
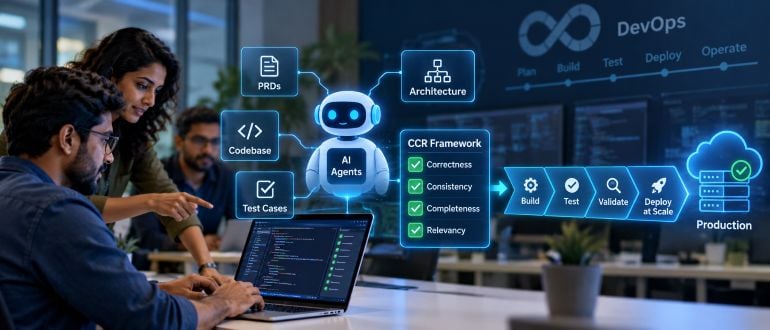
Talentica Software Unfurls Managed AI Service to Optimize Software Delivery
Talentica Software this week launched a managed software delivery service that leverages artificial intelligence (AI) to enable DevOps teams to deploy applications developed using AI coding tools at scale. Company CTO Manjusha ...
GitHub Gives Enterprises a Full Count of Who Holds the Keys
 Tom Smith | | access management, agentic AI, AI coding agents, credential inventory, credential security, Developer Security, devsecops, github, GitHub Apps, GitHub Enterprise Cloud, identity security, least-privilege, OAuth tokens, PATs, Personal Access Tokens, secrets management, security operations, Software Supply Chain Security, SSH keys
GitHub Enterprise Cloud now lets organizations export a full inventory of credentials, helping security teams identify stale, overprivileged and forgotten access across users, apps and automation ...
TeamPCP Supply Chain Attack Leads to CrowdSec Source Code Being Stolen
 Jeff Burt | | CrowdSec, EDR, github, Mini Shai-Hulud, NPM security, OAuth tokens, supply chain attacks, TanStack compromise, TeamPCP
CrowdSec says attackers stole source code from about 170 private GitHub repositories after a TanStack npm supply chain attack exposed an OAuth token tied to a former employee ...
AWS Adds Harness to Open Source SDK for Building AI Agents
Amazon Web Services (AWS) this week revealed it has added a harness to the open source software development kit (SDK) it makes available for building artificial intelligence (AI) agents. First introduced last ...
Cycode Extends DevSecOps Reach to Software Packages Developers Download
 Mike Vizard | | ADLC, agentic development lifecycle, AI coding agents, cool down period, Cycode, dependency security, Developer Security, devsecops, malicious packages, package security, software repositories, Software Supply Chain Security, supply chain attacks, threat intelligence, workstation protection
Cycode is adding workstation-level protection to stop developers and AI coding agents from downloading malicious or insufficiently vetted software packages ...
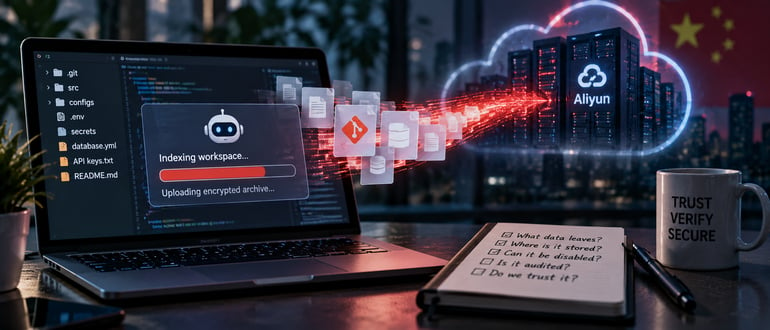
Your AI Coding Assistant Has the Keys to the Repo. Z.ai Just Showed Why That Matters
Tom Smith | | AI coding assistants, AI Governance, AI security, Cloud Security, code security, Data Exfiltration, data privacy, Developer Security, developer tools, devsecops, egress monitoring, secrets management, shadow ai, Software Supply Chain, source code security, Z.ai, ZCode, Zhipu AIZCode’s default-on indexing feature reportedly uploaded entire developer workspaces to cloud storage, highlighting why AI coding assistants should be treated as privileged software and closely monitored ...
New npm Threat Bypasses Install Script Protections
A malicious npm package that has been downloaded millions of times comes with a new way of spreading the malware that makes it easier to bypass security protections, say researchers with security ...
Ten Great DevOps Job Opportunities
DevOps.com is now providing a weekly DevOps jobs report through which opportunities for DevOps professionals will be highlighted as part of an effort to better serve our audience. Our goal in these ...
GitLab Tightens Rate Limits as Coding Agents Drive Demand

GitLab is introducing new rate limits for its cloud-based DevOps platform as growing demand from AI agents and automated development tools increases pressure on its infrastructure. The changes, which begin October 19, ...
Codex Sandbox Escapes Show Why Agent Guardrails Can’t Live Inside the Agent
Tom Smith | | agentic AI, AI coding agents, AI security, application security, Codex CLI, Codex Desktop, Codex Security, coding agent security, Developer Security, devsecops, Heapjack, OpenAI Codex, Overpatch, sandbox escape, sandbox security, Software Supply ChainTwo patched OpenAI Codex vulnerabilities, Heapjack and Overpatch, exposed how coding agents can escape sandboxes and reach developer systems without approval prompts ...

