Social – X
Git 2.56 Takes Aim at Messy Merges, Slow Diffs and Branch Sprawl
 Tom Smith | | AI coding agents, CI/CD, coding agents, developer tools, devops, GIT, Git 2.56, Git performance, Git repositories, merge conflicts, monorepos, platform engineering, software development, source control, version control
Git 2.56 improves merge safety, speeds up large-repository operations and adds cleanup tools that could prove especially useful for AI coding agents and busy DevOps teams ...
env zero Previews Control Plane for Agentic DevOps Workflows
 Mike Vizard | | agentic AI, AI agents, AI Governance, autonomous remediation, cloud infrastructure, CloudQuery, CMDB, devops, devops automation, env zero, EZ Control, IaC, infrastructure as code, infrastructure drift, kubernetes, MCP, platform engineering
env zero’s EZ Control introduces an agentic DevOps control plane that detects infrastructure drift, applies policy-driven remediation and keeps automated changes attributable, reversible and auditable ...
Docker Introduces Open Sandbox Kit Spec for AI Agent Permissions
AI agents are getting good at probing the boundaries developers put around them. Their ability to improvise makes them hard to contain. “You ask for something in a very high-level, vague-at-best way ...
Survey: Lack of Confidence in Software Supply Chain Security Runs High
A survey of 400 platform and security engineers in the U.S and United Kingdom (UK), finds nearly three quarters (73%) are either only moderately confident (58%) or not confident (15%) in the ...
DHH Declares End of Hand-Writing Code at Rails World 2026
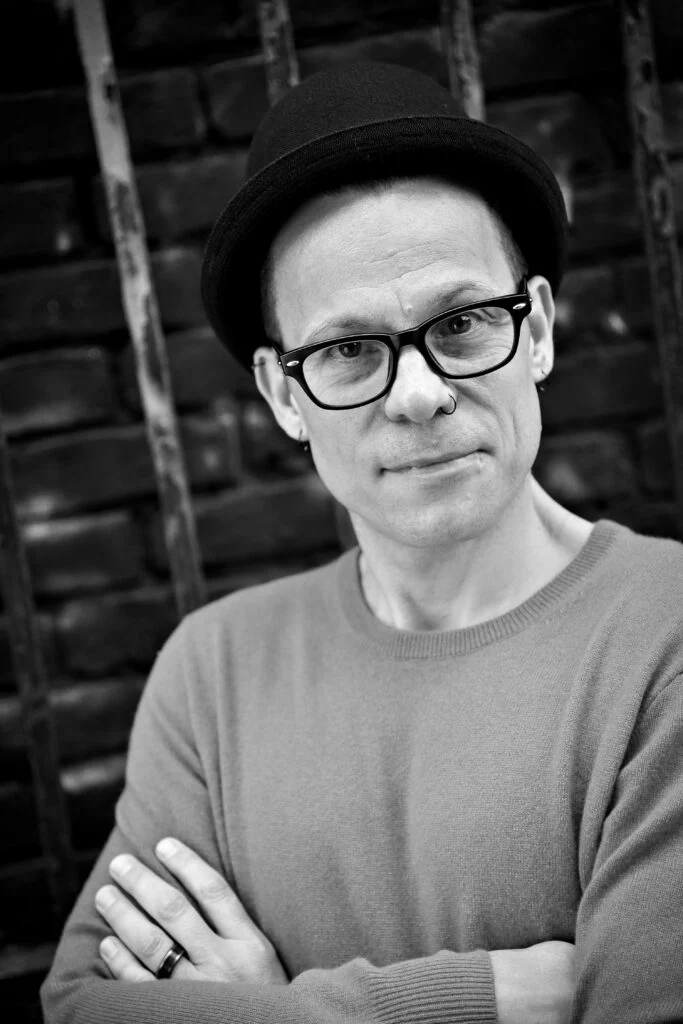
Controversial developer David Heinemeier Hansson (aka DHH) announced last week at Rails World 2026 that the end of handwritten code is upon us, calling it the modern era's "Brownie" moment. The moment ...
Ten Great DevOps Job Opportunities
DevOps.com is now providing a weekly DevOps jobs report through which opportunities for DevOps professionals will be highlighted as part of an effort to better serve our audience. Our goal in these ...
GitHub’s Security Autofix Agent Now Remembers What It Fixed
Tom Smith | | agentic autofix, AI coding agents, AI security, application security, code scanning, CodeQL, Copilot Memory, devsecops, github, GitHub Advanced Security, GitHub Copilot, repository memory, secure coding, vulnerability remediationGitHub’s agentic autofix now uses Copilot Memory to reuse repository-specific security fix patterns, helping Copilot apply lessons from past vulnerabilities across future alerts, reviews and coding workflows ...
Leaked GitLab Email Tokens Can Reach Code, Secrets and CI/CD Pipelines
 Jaime Hampton | | Aikido Security, application security, CI/CD, devsecops, gitlab, Software Supply Chain
Security researchers have uncovered a GitLab behavior that could let attackers use a leaked project email address to push code, trigger CI/CD jobs and reach other repositories accessible to the address owner ...
Blitzy Makes Sandbox for Reverse Engineering Code Available at No Cost
Blitzy has made available a sandbox where DevOps teams can reverse-engineer up to one million lines of code, generate up to 25,000 lines of tested end-to-end code, and identify security vulnerabilities across ...
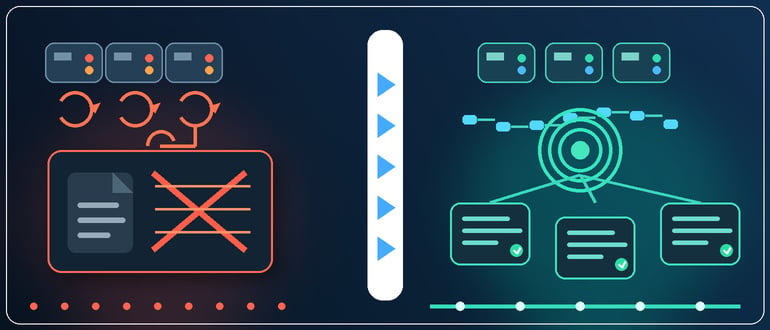
Dependency Mocking Approach That Gets More Accurate as Your Services Deploy More Often
 Sancharini Panda | | API testing, CI/CD, Contract Testing, Dependency Mocking, devops, ebpf, integration testing, Keploy, microservices, Mock Drift, service virtualization, software testing, test automation, Testcontainers, Traffic-Based Mocking
Traffic-based dependency mocking turns frequent upstream deployments into opportunities to refresh mocks from real behavior and reduce integration test drift ...
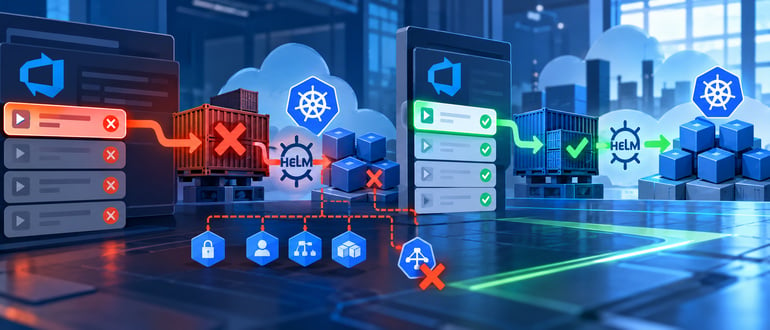
Why Old Azure DevOps Releases Survive a Pipeline Cutover
 Ahmed Tariq | | Azure DevOps, Azure DevOps Classic, Azure pipelines, CI/CD, container security, deployment automation, devops, devsecops, Helm, kubernetes, Kubernetes security, Pipeline Migration, release management, Release Pipelines, software delivery
Old Azure DevOps Classic releases can retain retired deployment tasks, Helm names, image paths and variables long after a pipeline cutover, leaving stale redeploy paths active ...
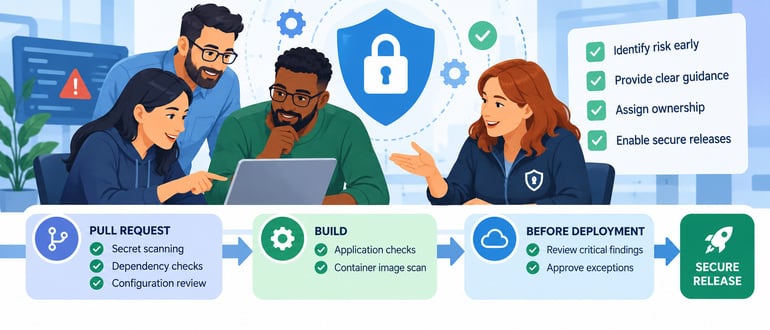
DevSecOps Teams as Partners in Secure Software Delivery
 Manish Shetty | | application security, CI/CD, CI/CD security, dependency security, devops security, devsecops, risk management, secure software development, security automation, Security Guardrails, shift left security, software security, Software Supply Chain, vulnerability management
DevSecOps teams can reduce last-minute release delays by shifting security decisions earlier, improving guardrails, clarifying ownership and making findings actionable ...

