Social – Facebook
Transforming Mainframe Recovery

Moving beyond disaster recovery, organizations can ensure business-critical mainframe environments. Over decades, the mainframe has earned a reputation for being synonymous with reliability. Many enterprise organizations continue to rely on the mainframe ...
Dash0 Acquires Polar Signals for Continuous Profiling and GPU Visibility

Observability startup Dash0 announced this week that it acquired Berlin-based continuous profiling specialist Polar Signals. The deal adds continuous profiling to SignalStore, Dash0’s OpenTelemetry-native data platform. Continuous profiling has been part of ...
Hackers Target Popular arrayref Rust Crate in Supply-Chain Attack
 Jeff Burt | | arrayref, information stealing, North Korea, Rust programming language, software supply chain attacks, StepSecurity, typosquatting, Wiz Research
Security researchers are sorting through a complex, stealthy, and fast-moving supply-chain attack aimed at pushing information-stealing malware by compromising the account of the maintainer of multiple Rust crates and introducing four more ...
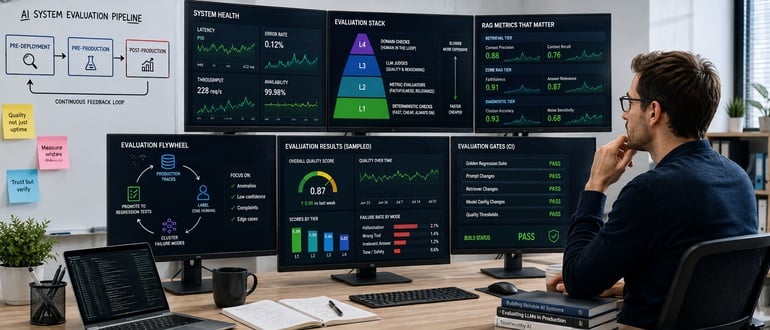
Production-Grade AI Eval Systems. What I Learned Putting LLMs on Call
 Anjaiah Methuku | | AI evals, AI guardrails, AI observability, AI quality monitoring, AI reliability engineering, AI SRE, AI testing, answer relevance, CI evals, context precision, context recall, faithfulness, hallucination detection, human-in-the-loop, LLM evaluation, LLM judges, LLM reliability, model monitoring, production AI, production-grade AI, RAG evaluation, RAG metrics, regression testing, retrieval-augmented generation
Production-grade AI reliability requires more than uptime and latency. A layered eval system helps teams detect hallucinations, RAG failures and quality regressions before customers do ...
Waterfall 2.0: Controlling LLM-Driven Software Development with Stage-Gated Discipline
 Georgy Starikov | | ADRs, Agile vs Waterfall, AI coding, AI development lifecycle, AI Software Engineering, AI-assisted engineering, architecture decision records, combi-shaper, engineering workflows, generative AI development, knowledge corpus, LLM engineering, LLM software development, MCP, Model Context Protocol, software architecture, software testing, system design, Waterfall 2.0
Waterfall 2.0 reimagines classic stage-gated software development for the LLM era, combining fast AI generation with structured validation, cheap backtracking and a shared knowledge corpus ...
Why API Test Generation Is a Judgment Problem, Not a Code Generation Problem
 Abhishek Saikia | | adaptive test coverage, AI API testing, AI quality engineering, AI test generation, API test generation, API testing, Automated testing, cross-field testing, DevOps Testing, fine-tuning, LLM testing, QA automation, RAG, software testing, test assertions, test coverage
When we started using large language models for API test generation at KushoAI, the results were impressive on the surface. Tests appeared in seconds. Coverage breadth went up. The team was excited ...
Why Cryptographic Inventory Is the First Step Toward Quantum Readiness
 Michael Carter | | CBOM, CI/CD security, crypto-agility, cryptographic dependencies, cryptographic discovery, cryptographic inventory, cryptography bill of materials, devops security, devsecops, Kubernetes security, ML-KEM, NIST PQC migration, post-quantum cryptography, PQC, quantum readiness, Software Supply Chain Security
Post-quantum readiness starts with visibility. DevOps teams need a continuous cryptographic inventory to map algorithms, keys, certificates, libraries, infrastructure and third-party dependencies before PQC migration begins ...
npm v12 Shuts Down a Popular Malware Trick — But the Threat Isn’t Going Away

For years, one of the easiest ways to sneak malware onto a developer's machine has been to hide in plain sight. Install a package from npm, and any lifecycle script bundled with ...
AI Agents Are Writing Code Faster Than Anyone Can Review It. Tessl Is Betting On Standards To Close That Gap
Every team that has turned coding agents loose on real work has run into the same wall. The agents write fast. They write a lot. And somewhere between the tenth and twentieth ...
Critical Flaw in isolated-vm Can Lead to Sandbox Escape, RCE Threat
Jeff Burt | | Activepieces, AI security, C/C++, Endor Labs, isolated-vm, JavaScript security, Mastra, n8n, Node.js security, remote code execution, Sandbox, software vulnerability, TOCTOU, V8 Isolate, vm2Developers for years have been using vm2, an open-source Node.js library, to run untrusted JavaScript inside a secure and isolated sandbox environment. It uses Node.js’s built-in modules and JavaScript Proxies and lets ...

UiPath Test Cloud: Robots Handle Repetition, Agents Adapt and Humans Lead

Most companies don't actually struggle to ship software anymore. AI made that part fast. What they struggle with is releasing what they built with any real confidence in it. That gap between ...

GitHub Sharpens CodeQL’s Eye on Actions Workflows and Modern JavaScript
GitHub Actions pipelines have become one of the quieter attack surfaces in software development. They pull in third-party actions, cache dependencies, and pass secrets between jobs, often without anyone reviewing the workflow ...