
Tag: Repository Security
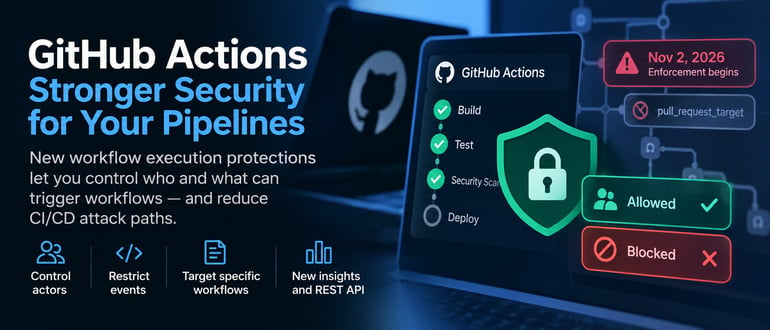
GitHub Separates Who Writes Code From Who Runs Your CI
 Tom Smith | | Actions security, CI/CD security, devops, devsecops, github, GitHub Actions, GitHub Enterprise, GitHub security, pipeline security, pull_request_target, Repository Security, Software Supply Chain, supply chain security, workflow execution protections, workflow security
GitHub’s new workflow execution protections let teams control who and what can trigger Actions workflows, reducing CI/CD attack paths and tightening pipeline security ...
More JFrog Artifactory Bugs Are Under Attack, and All Three Have Patches
Tom Smith | | administrative tokens, artifact repositories, authentication bypass, build pipeline security, CI/CD security, CVE-2026-42016, CVE-2026-42018, CVE-2026-82329, Cybersecurity, devsecops, Groovy plugins, JFrog Artifactory, patch management, privilege escalation, Repository Security, Rust backdoors, Software Supply Chain, vulnerability management, web shellsAttackers are actively exploiting three JFrog Artifactory flaws, exposing how slow patching can turn artifact repositories into software supply chain attack paths ...
GitLab’s Critical Patch Closes a Path Traversal Flaw Attackers Are Already Probing
Tom Smith | | access control, API security, CI/CD security, credential theft, CVE-2026-85706, CVE-2026-87719, CVSS 10.0, Cybersecurity, devops security, devsecops, gitlab, GitLab Duo, GitLab security, GraphQL security, patch management, Repository Security, self-managed GitLab, Software Supply Chain, vulnerability managementGitLab patches two critical flaws, including a CVSS 10.0 unauthenticated file-read vulnerability, putting self-managed instances under urgent pressure to upgrade ...

GitHub Widens the Door on Advanced Security Trials
Tom Smith | | AI coding, application security, CodeQL, Developer Security, devsecops, exposed credentials, GHAS, GitHub Advanced Security, GitHub Code Security, GitHub Enterprise Cloud, GitHub Secret Protection, GitHub security, mid-market security, Repository Security, secret scanning, secure software development, Software Supply Chain Security, vulnerability scanningGitHub raised its self-serve Advanced Security trial cap from 100 to 300 licenses, letting more mid-size Enterprise Cloud orgs test for free ...
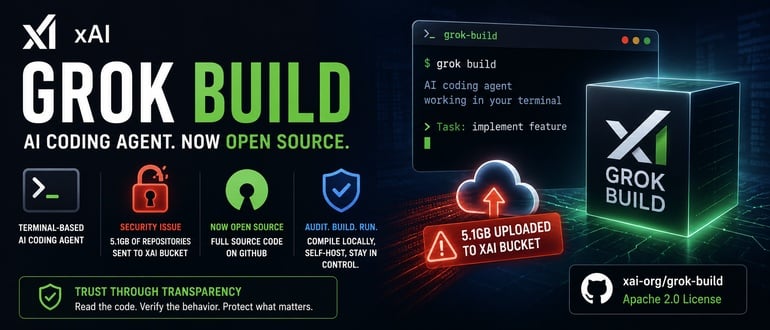
xAI Open-Sources Grok Build Coding Agent After Cloud Upload Exposes SSH Keys, Repos
Tom Smith | | AI agent governance, AI coding agent, Apache 2.0, credential exposure, developer privacy, devops security, github, Grok Build, open-source coding agent, Repository Security, source code security, xAIxAI has published the full source code for Grok Build, its terminal-based AI coding agent, on GitHub under an Apache 2.0 license. The release lands three days after a security researcher showed ...
Fake Stars in GitHub a Growing Security Threat, Analysis Finds

There was a surge of inauthentic stars on code repositories in 2024, ramping up the threat of software supply chain attacks ...

npm is Scam-Spam Cesspool ¦ Google in Microsoft Antitrust Thrust
 Richi Jennings | | Amit Zavery, azure, code repo, code repositories, code repository, GOOG, GOOGL, google, Google Cloud, IaaS, microsoft, Microsoft Azure, MSFT, NPM, npm registry, open source, public repository, Repos, repositories, repository, Repository Security, SEO, Software Supply Chain, software supply chain attacks, Software Supply Chain Security, Software Supply Chains, softwaresupplychain, source code repository, spam, supply chain, supply chain attacks, supply chain security, The Long View
In this week’s #TheLongView: The npm registry suffers spam infestation, and Microsoft makes Google sad ...
