Social – Facebook
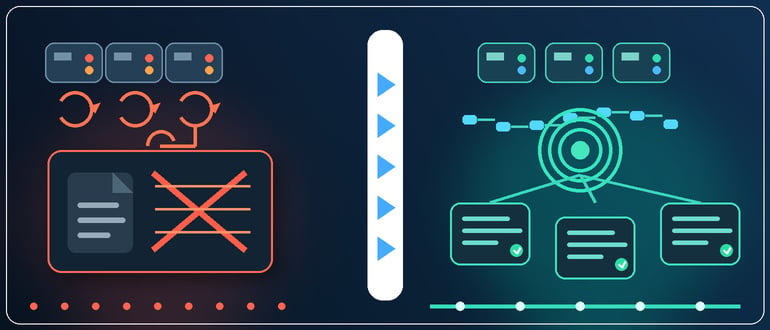
Dependency Mocking Approach That Gets More Accurate as Your Services Deploy More Often
 Sancharini Panda | | API testing, CI/CD, Contract Testing, Dependency Mocking, devops, ebpf, integration testing, Keploy, microservices, Mock Drift, service virtualization, software testing, test automation, Testcontainers, Traffic-Based Mocking
Traffic-based dependency mocking turns frequent upstream deployments into opportunities to refresh mocks from real behavior and reduce integration test drift ...
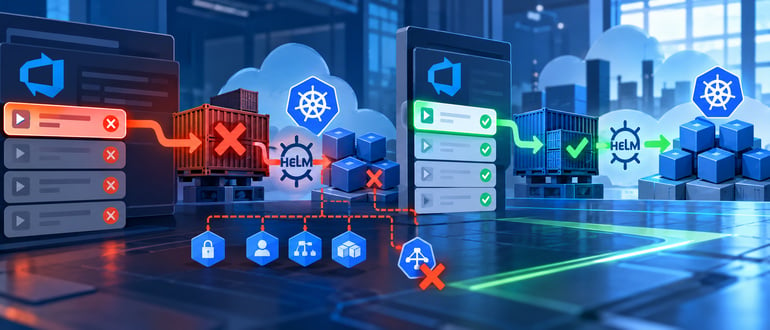
Why Old Azure DevOps Releases Survive a Pipeline Cutover
 Ahmed Tariq | | Azure DevOps, Azure DevOps Classic, Azure pipelines, CI/CD, container security, deployment automation, devops, devsecops, Helm, kubernetes, Kubernetes security, Pipeline Migration, release management, Release Pipelines, software delivery
Old Azure DevOps Classic releases can retain retired deployment tasks, Helm names, image paths and variables long after a pipeline cutover, leaving stale redeploy paths active ...
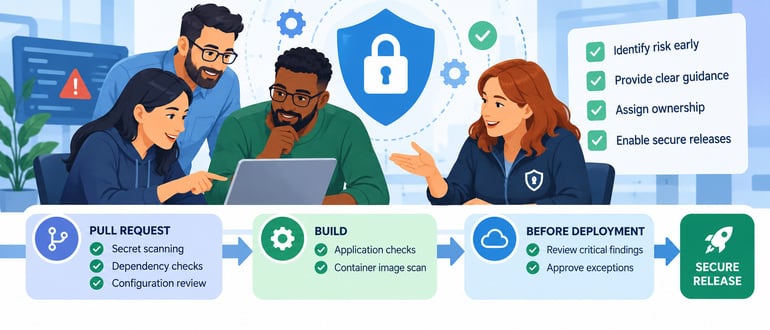
DevSecOps Teams as Partners in Secure Software Delivery
 Manish Shetty | | application security, CI/CD, CI/CD security, dependency security, devops security, devsecops, risk management, secure software development, security automation, Security Guardrails, shift left security, software security, Software Supply Chain, vulnerability management
DevSecOps teams can reduce last-minute release delays by shifting security decisions earlier, improving guardrails, clarifying ownership and making findings actionable ...
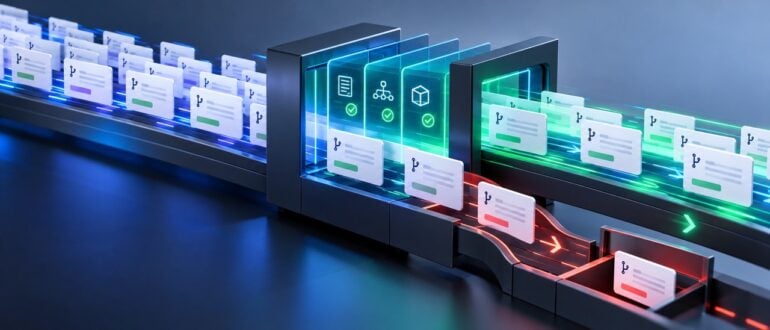
Why Plan Review Stopped Working
 Mariusz Michalowski | | AI agents, gitops, IaC, infrastructure as code, infrastructure automation, policy as code
The control that held your infrastructure together was plan review, meaning a person reading a diff and deciding whether to approve it. Not the policy document and not the pipeline configuration. It ...
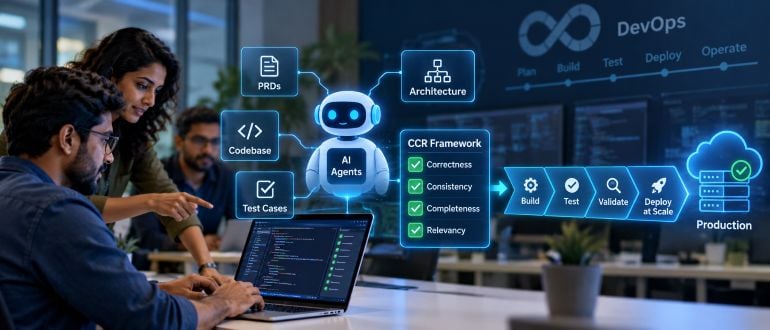
Talentica Software Unfurls Managed AI Service to Optimize Software Delivery
Talentica Software this week launched a managed software delivery service that leverages artificial intelligence (AI) to enable DevOps teams to deploy applications developed using AI coding tools at scale. Company CTO Manjusha ...
What I Learned Building Cloud-Portable Services Across Multiple Providers
 Sandeep Pal | | Alibaba Cloud, AWS, cloud abstraction, Cloud APIs, cloud architecture, cloud infrastructure, cloud portability, cloud SDKs, cloud-native development, conformance testing, developer experience, devops, Google Cloud, IDP, internal developer platforms, kubernetes, Multi-cloud, platform engineering, vendor lock-in, WireMock
Multi-cloud strategies often stumble over provider-specific behavior. A layered abstraction built on official SDKs can normalize differences while preserving access to valuable native capabilities ...
The Observability Tax: When Monitoring Costs Exceed Downtime Costs
 Muhammad Yawar Malik | | cloud costs, data retention, devops, Distributed Tracing, FinOps, incident response, infrastructure monitoring, logs, metrics, observability, observability costs, observability strategy, OpenTelemetry, platform engineering, SRE, telemetry, telemetry costs, traces
Observability costs can spiral when teams collect more telemetry than they actually use. A more mature approach prioritizes the data that directly improves incident detection, diagnosis and recovery ...
GitHub Gives Enterprises a Full Count of Who Holds the Keys
 Tom Smith | | access management, agentic AI, AI coding agents, credential inventory, credential security, Developer Security, devsecops, github, GitHub Apps, GitHub Enterprise Cloud, identity security, least-privilege, OAuth tokens, PATs, Personal Access Tokens, secrets management, security operations, Software Supply Chain Security, SSH keys
GitHub Enterprise Cloud now lets organizations export a full inventory of credentials, helping security teams identify stale, overprivileged and forgotten access across users, apps and automation ...
TeamPCP Supply Chain Attack Leads to CrowdSec Source Code Being Stolen
 Jeff Burt | | CrowdSec, EDR, github, Mini Shai-Hulud, NPM security, OAuth tokens, supply chain attacks, TanStack compromise, TeamPCP
CrowdSec says attackers stole source code from about 170 private GitHub repositories after a TanStack npm supply chain attack exposed an OAuth token tied to a former employee ...
AWS Adds Harness to Open Source SDK for Building AI Agents
Amazon Web Services (AWS) this week revealed it has added a harness to the open source software development kit (SDK) it makes available for building artificial intelligence (AI) agents. First introduced last ...
Cycode Extends DevSecOps Reach to Software Packages Developers Download
 Mike Vizard | | ADLC, agentic development lifecycle, AI coding agents, cool down period, Cycode, dependency security, Developer Security, devsecops, malicious packages, package security, software repositories, Software Supply Chain Security, supply chain attacks, threat intelligence, workstation protection
Cycode is adding workstation-level protection to stop developers and AI coding agents from downloading malicious or insufficiently vetted software packages ...
Your AI Coding Assistant Has the Keys to the Repo. Z.ai Just Showed Why That Matters
Tom Smith | | AI coding assistants, AI Governance, AI security, Cloud Security, code security, Data Exfiltration, data privacy, Developer Security, developer tools, devsecops, egress monitoring, secrets management, shadow ai, Software Supply Chain, source code security, Z.ai, ZCode, Zhipu AIZCode’s default-on indexing feature reportedly uploaded entire developer workspaces to cloud storage, highlighting why AI coding assistants should be treated as privileged software and closely monitored ...

